cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · securityweek.com

How LLM-Generated Access Policies Can Quietly Expand Permissions

Researcher Vatsal Gupta says LLM-written access policies can compile yet omit constraints, deny rules, or context, expanding permissions. He recommends validation, behavioral testing, and explicit deny-by-default controls.

Mar 30, 2026
Security Insights · thecyberexpress.com

Dr. Priyanka Sunder on Building Resilient Cybersecurity Programs

In an interview, Dr. Priyanka Sunder discusses GRC as a continuous resilience effort, Security by Design, cloud security priorities, and practical ways to strengthen organizational security culture.

Mar 30, 2026
Security Insights · hackingarticles.in

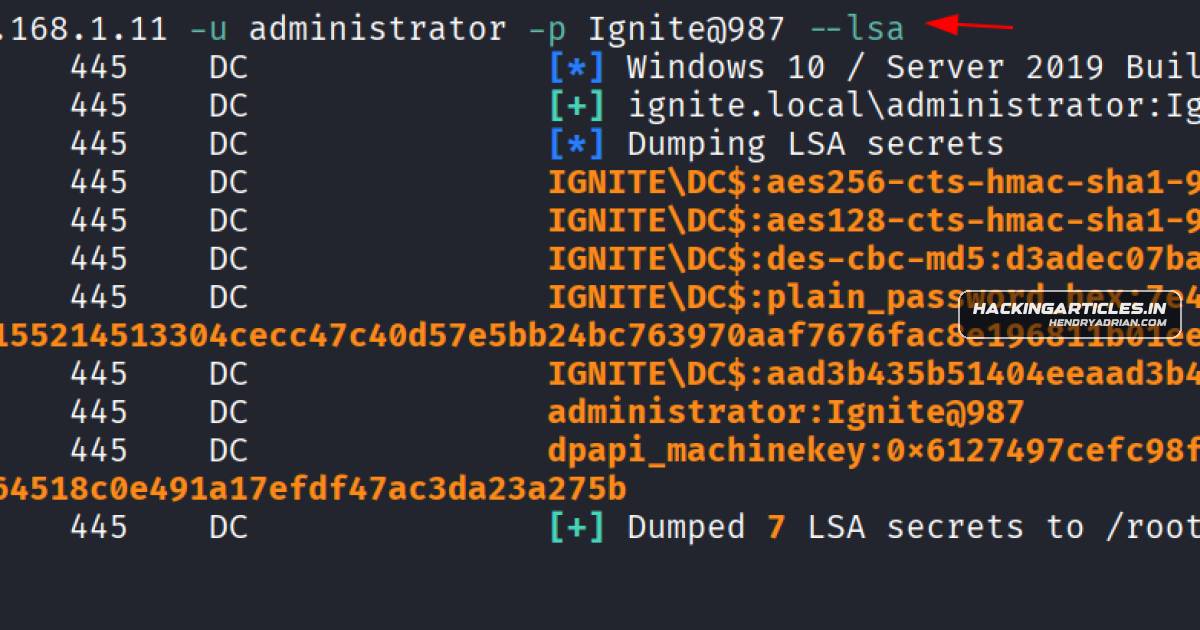
LSASS Credential-Dumping Methods, Tools, and Defenses

A walkthrough of local and remote LSASS credential dumping covers tools, dump parsing, and detection. It also outlines defenses including Credential Guard, LSASS Protected Process Light, ASR rules, and network monitoring.

Mar 30, 2026
Security Insights · bleepingcomputer.com

Gartner’s Seven Questions for Evaluating AI SOC Agents

A sponsored guide summarizes Gartner’s seven questions for evaluating AI SOC agents, emphasizing measurable outcomes, vendor viability and costs, analyst augmentation, autonomy guardrails, integration, transparency, and data protection.

Mar 30, 2026
Security Insights · hackingarticles.in

Using Impacket DACLEdit to Demonstrate Active Directory Privilege Escalation

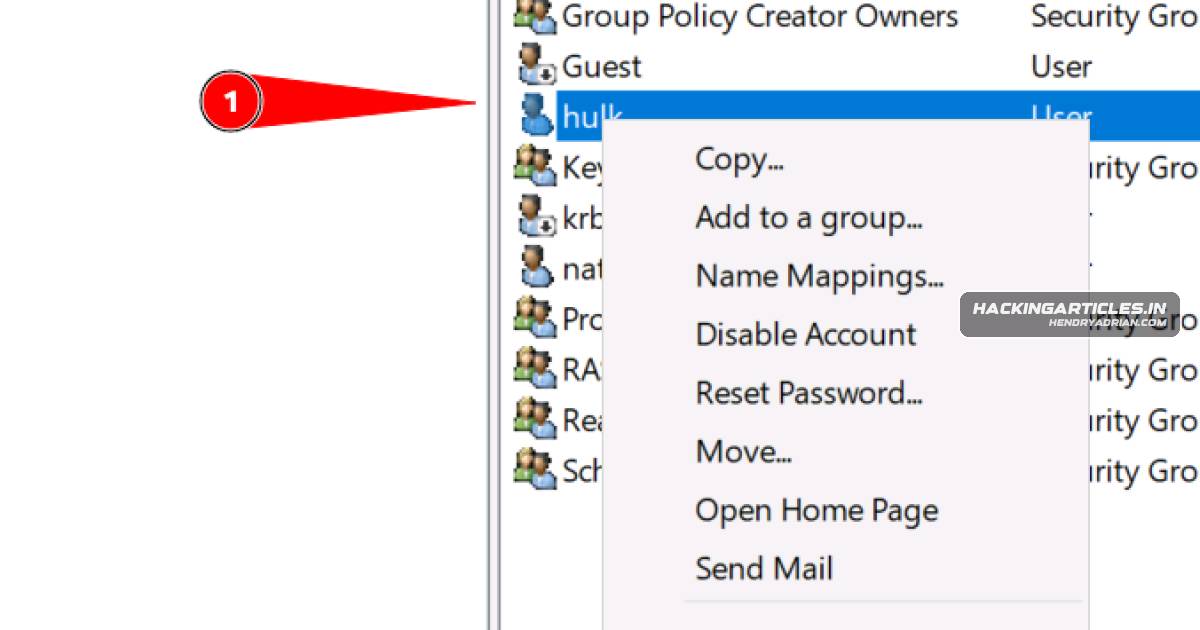
A lab walkthrough shows how misconfigured Active Directory DACLs can enable password resets, Domain Admin group changes, and DCSync, then recommends ACL restoration, auditing, least privilege, and monitoring.

Mar 29, 2026
Security Insights · hackingarticles.in

Active Directory Attack Chain and Defenses Using BloodyAD

A lab walkthrough uses BloodyAD and Impacket to demonstrate Active Directory enumeration, privilege escalation, credential attacks and persistence, then outlines monitoring and hardening measures for the misconfigurations exploited.

Mar 28, 2026
Security Insights · cofense.com

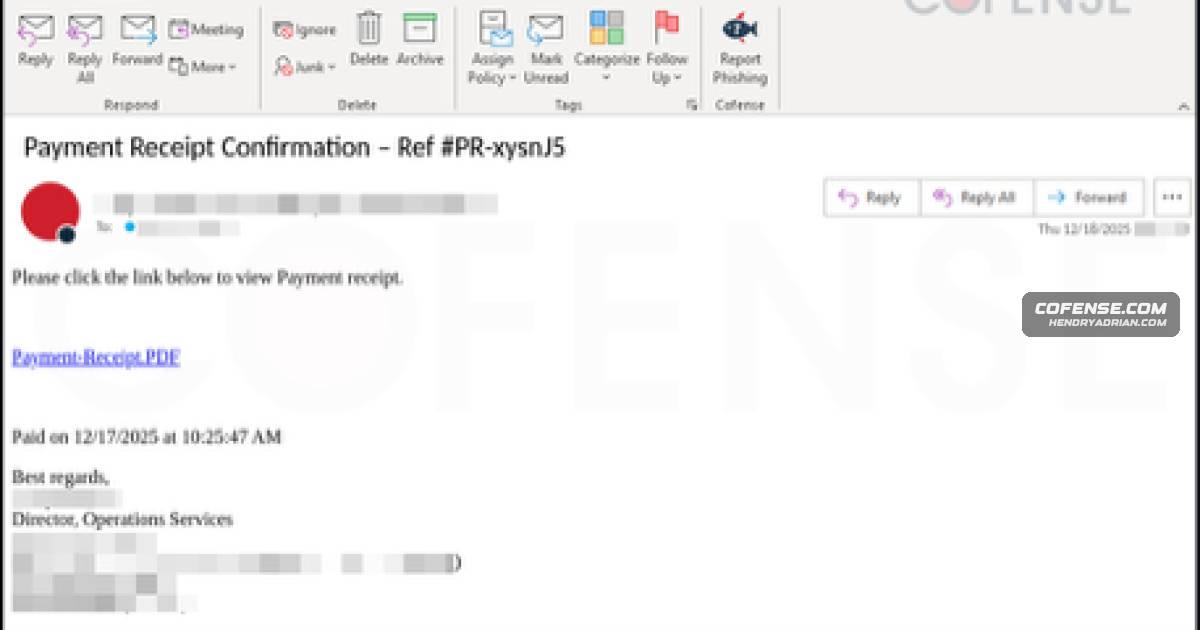
How Threat Actors Abuse Cloudflare Services for Phishing and Malware Delivery

Cofense describes Cloudflare Workers used for AiTM credential phishing and TryCloudflare Tunnels for malware delivery. A reported chain uses URL shortcuts, WebDAV, WSF and batch scripts to install Xeno RAT or XWorm RAT; Cloudflare uses behavioral detection, CAPTCHA and,

Mar 27, 2026
Security Insights · hackingarticles.in

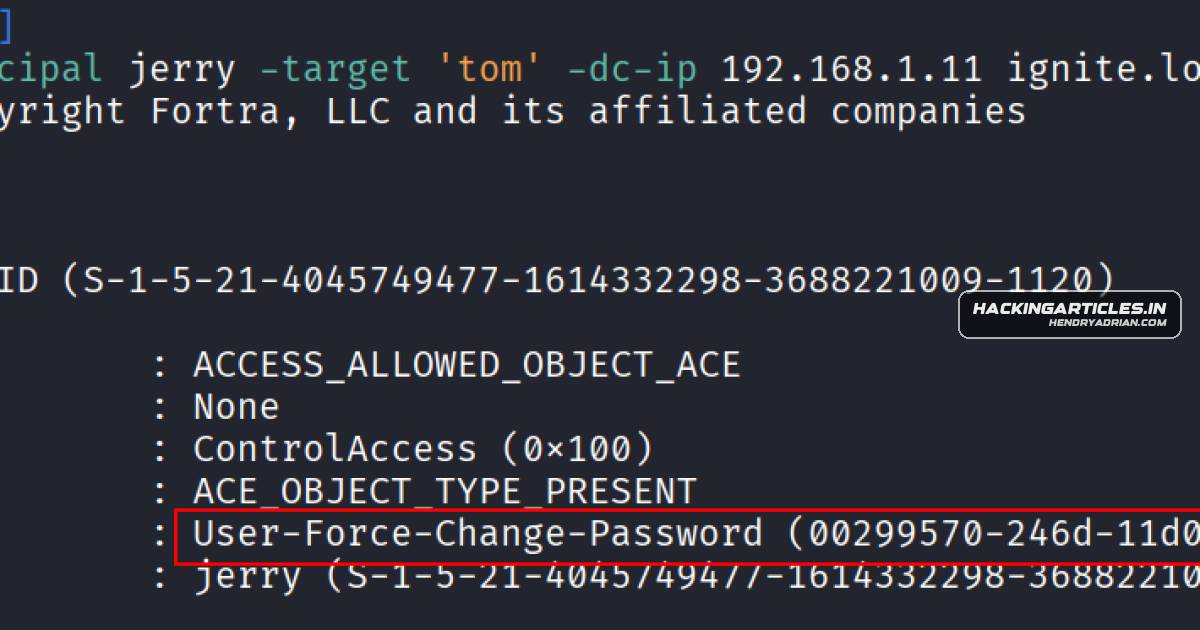
Impacket Tutorial Demonstrates Active Directory Password Reset Techniques

An Impacket tutorial demonstrates resetting or changing Active Directory passwords through ForceChangePassword, hash/AES/TGT authentication, and SMB-SAMR, RPC-SAMR, LDAP, and kpasswd. It also covers Windows event detection and AD defenses.

Mar 27, 2026
Security Insights · blog.sucuri.net

Web Shells: How Attackers Use Them and How to Detect and Remove Them

An overview of web shells as persistent backdoors on compromised servers, covering common entry methods, capabilities and risks, plus ways to detect, remove and prevent them.

Mar 26, 2026
Security Insights · toxsec.com

Multimodal Prompt Injections Hide Instructions in Images and Audio

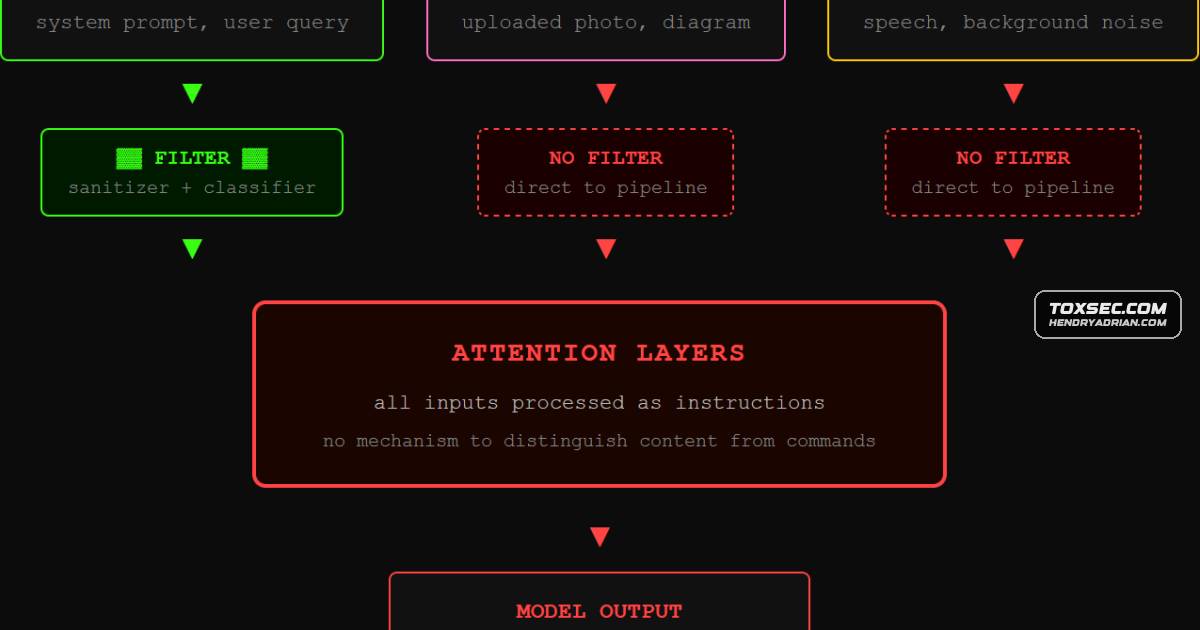
The article explains how image and audio prompt-injection techniques can bypass text-focused safeguards, citing research on cross-model transfer and high success rates in tests, including over-the-air audio attacks.

Mar 26, 2026
Security Insights · cloudsek.com

CloudSEK Warns Exposed MLOps Platforms Could Enable AI Pipeline Sabotage

CloudSEK says a 48-hour scan found over 100 exposed credential sets and more than 80 publicly accessible MLOps deployments, warning that attackers could access AI assets or tamper with training pipelines.

Mar 26, 2026
Security Insights · securityweek.com

PwC: AI Speeds Cyberattacks, but Identity Remains a Key Weakness

PwC threat intelligence leader Allison Wikoff says AI is accelerating reconnaissance, phishing and malware development, while fully autonomous attacks remain early-stage. She urges organizations to prioritize identity protection and defenses around critical assets.

Mar 25, 2026
Security Insights · hackingarticles.in

Pass-the-Hash Techniques Enable Windows Active Directory Lateral Movement

A technical walkthrough demonstrates NTLM hash-based lateral movement across Windows Active Directory services using tools including NetExec, Impacket, Mimikatz and Rubeus, and outlines mitigations such as Credential Guard and restricting NTLM.

Mar 25, 2026
Security Insights · thehackernews.com

Telegram Crackdown Contained Threat Actors but Did Not Displace Them

A Check Point executive says Telegram removed over 43 million channels and groups in 2025, but criminal actors quickly returned using gated access, backup channels and hybrid communications; he urges continuous, contextual monitoring.

Mar 25, 2026
Security Insights · thehackernews.com

Why Higher Education Faces Identity Security Risks in Hybrid Environments

The article describes how hybrid AD and Entra ID environments, high user turnover and decentralized IT can leave higher-education institutions with orphaned accounts and excess privileges. It recommends centralized, automated identity governance and auditing.

Mar 25, 2026
Security Insights · huntress.com

ClickFix Scams Trick Users Into Running Malicious Commands

ClickFix lures users with fake verification or tech-support prompts and tricks them into running commands themselves. Huntress says the technique accounted for over half of malware loader activity in its 2026 Cyber Threat Report.

Mar 25, 2026
Security Insights · securityweek.com

OpenClaw Highlights Governance Risks of Agentic AI Systems

The article explains how OpenClaw agents’ inherited permissions, gateway exposure and extensions can expand security risks, and recommends visibility into agent use, deployment controls and monitoring for malicious activity.

Mar 24, 2026
Security Insights · blogs.jpcert.or.jp

JPCERT/CC Profiles Azerbaijan’s CSIRTs and Cybersecurity Workforce

A JPCERT/CC visit to Azerbaijan profiled three CSIRTs, a national cybersecurity training center, and an industry association, highlighting incident response, information sharing, workforce development, and international cooperation.

Mar 24, 2026
Security Insights · thecyberexpress.com

Human Behavior Is a Major Cybersecurity Vulnerability, Says Dr. Sheeba Armoogum

In an interview, Dr. Sheeba Armoogum discusses social engineering, transparent AI-based defense, digital-legacy planning and ways organizations can support women in advanced cybersecurity research.

Mar 24, 2026
Security Insights · thecyberexpress.com

Hackmanac CEO Says Cybersecurity Must Be Managed as a Business Risk

Hackmanac CEO Sofia Scozzari argues that organizations should treat cybersecurity as a business risk, embed security by design, share threat information, and account for human factors and operational constraints.

Mar 23, 2026
Security Insights · huntress.com

Inside Cybercrime’s Organized Scam Operations and Use of AI

Huntress’s _declassified episode describes organized scam centers, their roles and revenue, examples of phone and tech-support scams, and the use of AI-generated identities and deepfakes. It also highlights tools that waste scammers’ time.

Mar 23, 2026
Security Insights · hackingarticles.in

How to Use Impacket secretsdump for Windows Credential Extraction

A hands-on guide to Impacket secretsdump covers remote credential extraction with DCSync and VSS, offline registry-hive parsing, authentication options, and flags for filtering and saving output.

Mar 21, 2026
Security Insights · hackingarticles.in

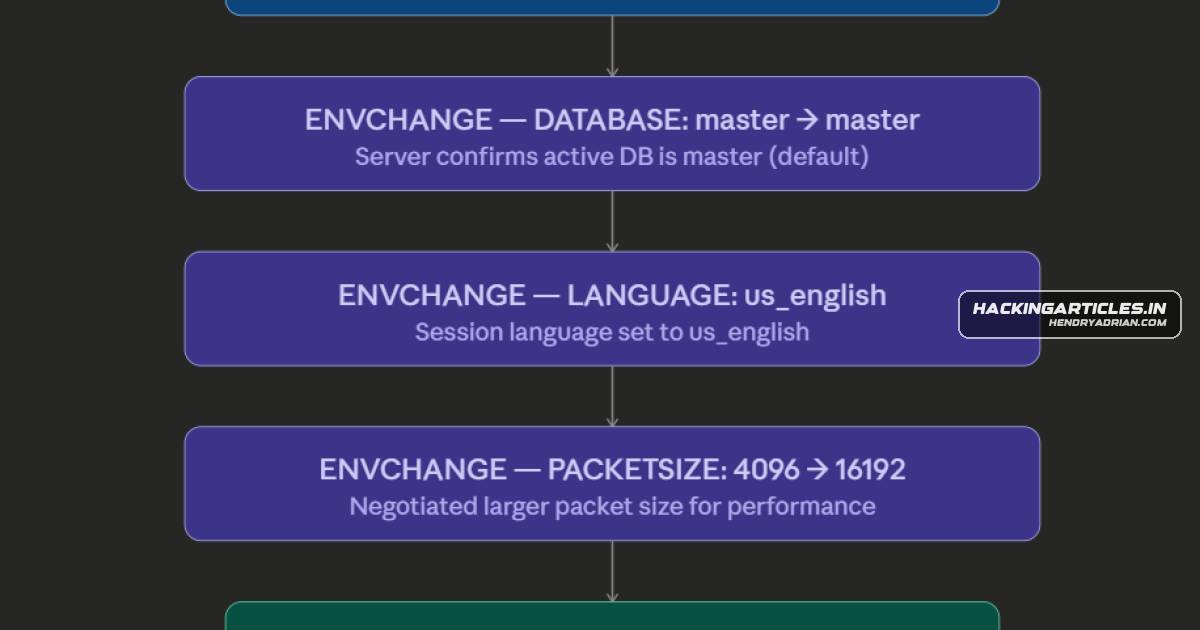
Using Impacket to Exploit Misconfigured Microsoft SQL Server

A penetration-testing walkthrough shows how weak SQL credentials, IMPERSONATE permissions, or linked servers can lead to SQL Server sysadmin access, OS command execution, and file uploads, and outlines defenses.

Mar 21, 2026
Security Insights · hackingarticles.in

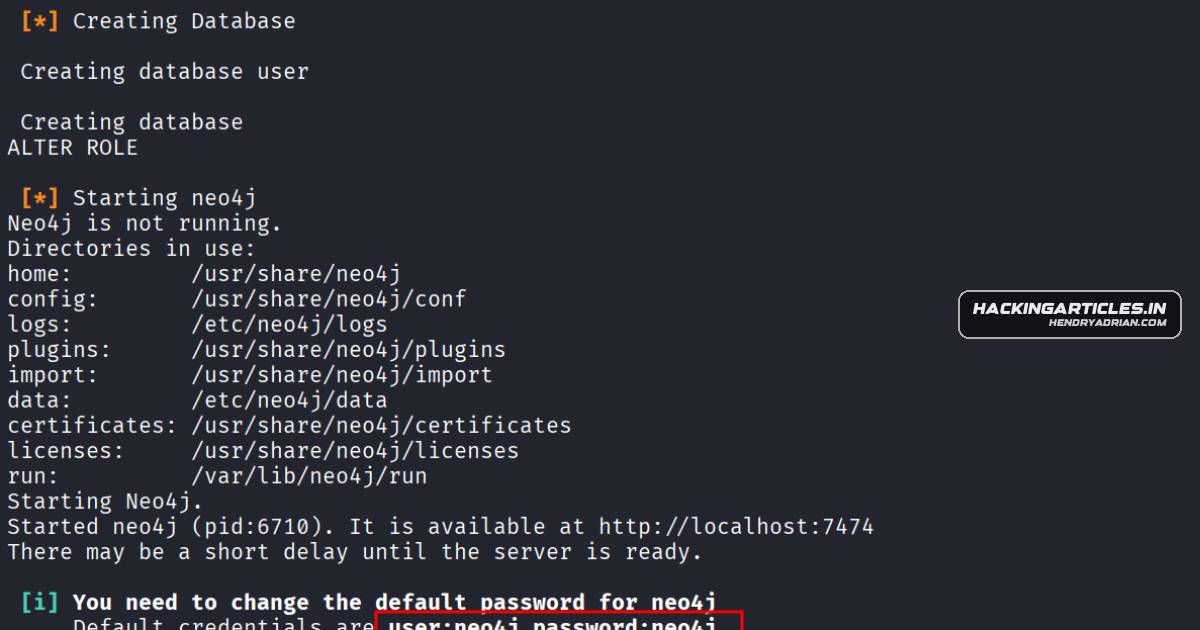
How to Use BloodHound CE to Map Active Directory Attack Paths

A practical guide to installing BloodHound CE, collecting Active Directory data with several tools, and analyzing relationships and permissions to identify privilege-escalation paths in the IGNITE.LOCAL example environment.

Mar 20, 2026
PreviousPage 36 of 54 Next
© 2026 cyber.hendryadrian.com