cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · darktrace.com

Darktrace Says Behavioral AI Can Help Defend Against AI-Driven Cyber Threats

Darktrace argues that AI-driven vulnerability discovery may outpace patching and recommends behavioral AI to identify and contain threats by spotting deviations from an organization’s normal activity.
Apr 16, 2026
Security Insights · securityweek.com

Sophos CISO Ross McKerchar on AI Threats, Burnout and Industry Trust

Sophos CISO Ross McKerchar discusses AI’s current and potential cyber risks, cybersecurity team burnout, the Pacific Rim project, and a growing trust problem in the security industry.

Apr 15, 2026
Security Insights · bleepingcomputer.com

How Cybercriminals Exploit Freight Systems and GPS Tracking

NMFTA's sponsored article describes how cybercriminals exploit freight identities, booking-site credentials, and GPS spoofing for cargo theft, and recommends MFA, network segmentation, awareness training, patching, and trucking-specific security guidance.

Apr 15, 2026
Security Insights · hackingarticles.in

SSH Tunneling Guide Demonstrates Port Forwarding and RDP Pivoting

A lab walkthrough demonstrates SSH local, dynamic, and remote forwarding to reach loopback-bound services and tunnel RDP, including how GatewayPorts can expose a forwarded port across a network. It also recommends controls for limiting and monitoring SSH tunnels.

Apr 14, 2026
Security Insights · decodedsecurity.com

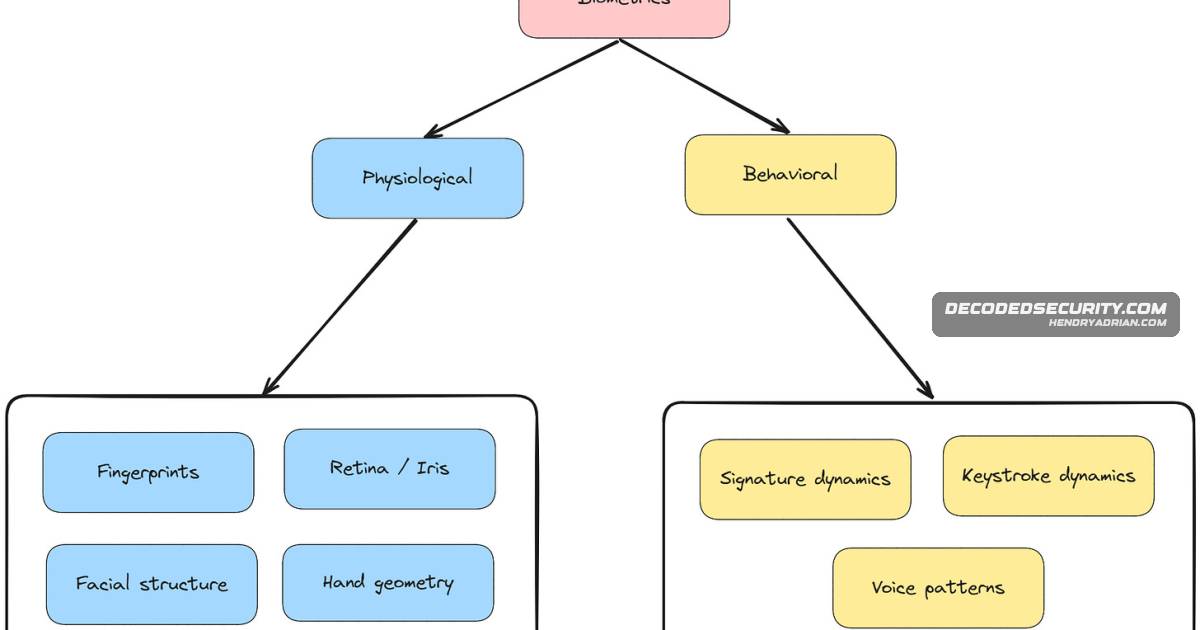
Biometric Authentication: False Acceptance, False Rejection, and CER

An explainer on physiological and behavioral biometrics, the trade-off between False Acceptance Rate and False Rejection Rate, and how the Crossover Error Rate compares systems. It also notes privacy, usability, and cost considerations.

Apr 14, 2026
Security Insights · cisecurity.org

CIS Explains How Hardened Images Apply Security Benchmarks to Cloud Deployments

CIS describes how its preconfigured Hardened Images apply CIS Benchmark settings to cloud virtual machines, aiming to reduce manual hardening, misconfiguration, and configuration drift.

Apr 14, 2026
Security Insights · wiz.io

GitHub Actions Security Risks: Dangerous Triggers, Script Injection, and Compromised Actions

A security explainer details how GitHub Actions misconfigurations enabled supply-chain attacks, secret theft, and script injection, and recommends safer trigger use, careful handling of untrusted inputs, and pinning third-party actions.

Apr 14, 2026
Security Insights · toxsec.com

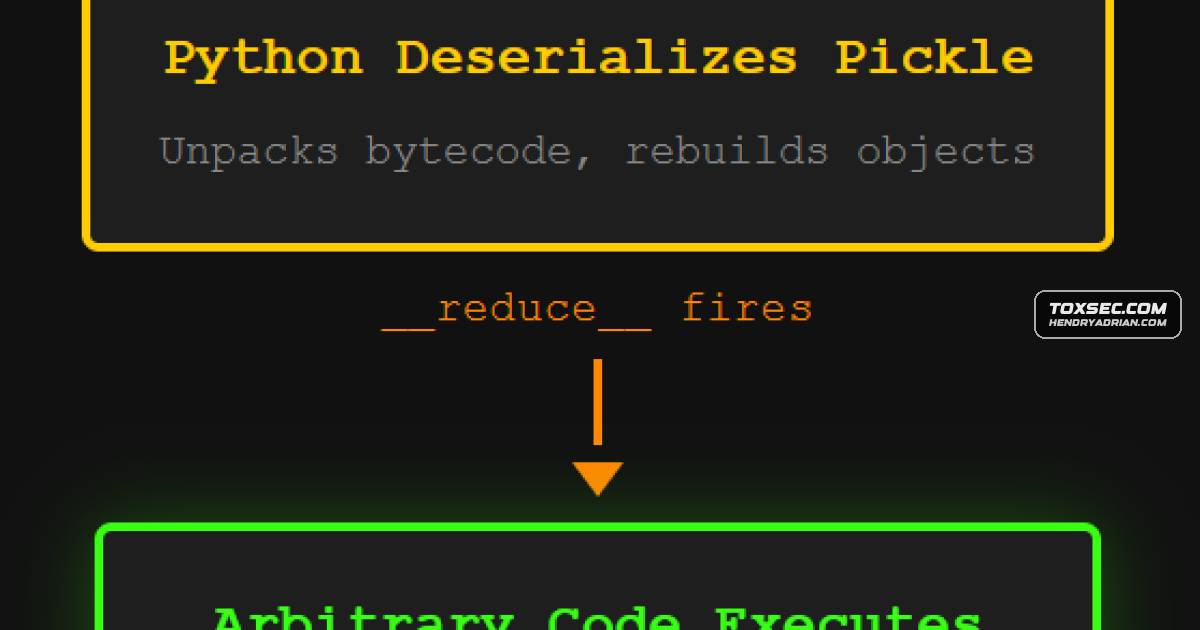
Local AI Models Face Pickle-Based Code Execution and Triggered-Behavior Risks

The article explains how pickle-serialized model files can execute code and how fine-tuned models may exhibit trigger-dependent behavior. It cites security research and recommends verified providers, SafeTensors, and hash checks.

Apr 13, 2026
Security Insights · hackingarticles.in

Guide Demonstrates Six Port-Forwarding Techniques for Reaching Isolated Services

A hands-on lab demonstrates six ways to reach an Apache2 service bound to localhost through a compromised host, then outlines defenses including SSH restrictions, monitoring for tunnels and listeners, and network segmentation.

Apr 13, 2026
Security Insights · trendmicro.com

Trend Micro Outlines Identity-First Security for Human, Machine and AI-Agent Risks

Trend Micro describes identity risks involving people, machine accounts and AI agents, and promotes unified visibility, risk prioritization and automated response as ways to detect and contain identity-based threats.

Apr 13, 2026
Security Insights · zscaler.com

Alibaba Incident Underscores Why Zero Trust Matters as AI Challenges Traditional Security

The article argues that the Alibaba incident highlights the limits of perimeter-based security and the value of Zero Trust, where access is context-based, pathways are constrained, and behavior is continuously validated.

Apr 13, 2026
Security Insights · hackingarticles.in

Ligolo-MP Guide Demonstrates Multi-Hop Network Pivoting

A hands-on lab guide shows how Ligolo-MP coordinates agents, routes and TCP redirectors for single- and double-hop pivoting, localhost-only service access and compile-time agent obfuscation, highlighting risks from weak segmentation and egress controls.

Apr 12, 2026
Security Insights · elastic.co

Elastic Details Security Platform and AI Deployment for Defence Cyber Marvel 2026

Elastic says its platform supported Defence Cyber Marvel 2026 with a multi-tenant deployment for 40 Blue Teams, testing across 6,000 agents, peak ingestion of 800,000 events per second, and guarded, audited AWS Bedrock AI services.

Apr 11, 2026
Security Insights · hackingarticles.in

Active Directory Enumeration and Abuse with Samba’s net rpc

A practical walkthrough demonstrates how Samba’s net rpc can enumerate and modify Active Directory accounts, groups, privileges and registry settings, and explains the risks of misconfigured ACLs and defenses for domain controllers.

Apr 11, 2026
Security Insights · wiz.io

Wiz Warns AI-Driven Vulnerability Discovery Could Accelerate Exploitation

Wiz says Anthropic’s unreleased Claude Mythos can autonomously find zero-days and develop exploits, and urges organizations to accelerate patching, reduce attack surfaces, and build AI-assisted security workflows.

Apr 10, 2026
Security Insights · cyberbuilders.substack.com

RSAC 2026 Takeaways: Agentic AI, Faster Threats and a Return to Security Basics

A field guide to RSAC 2026 argues that AI is reshaping security work and creating new risks around agents and non-human identities, while faster attacks make automation urgent and core security fundamentals remain essential.

Apr 10, 2026
Security Insights · huntress.com

Huntress Says Staging Environments Need Production-Level Security Attention

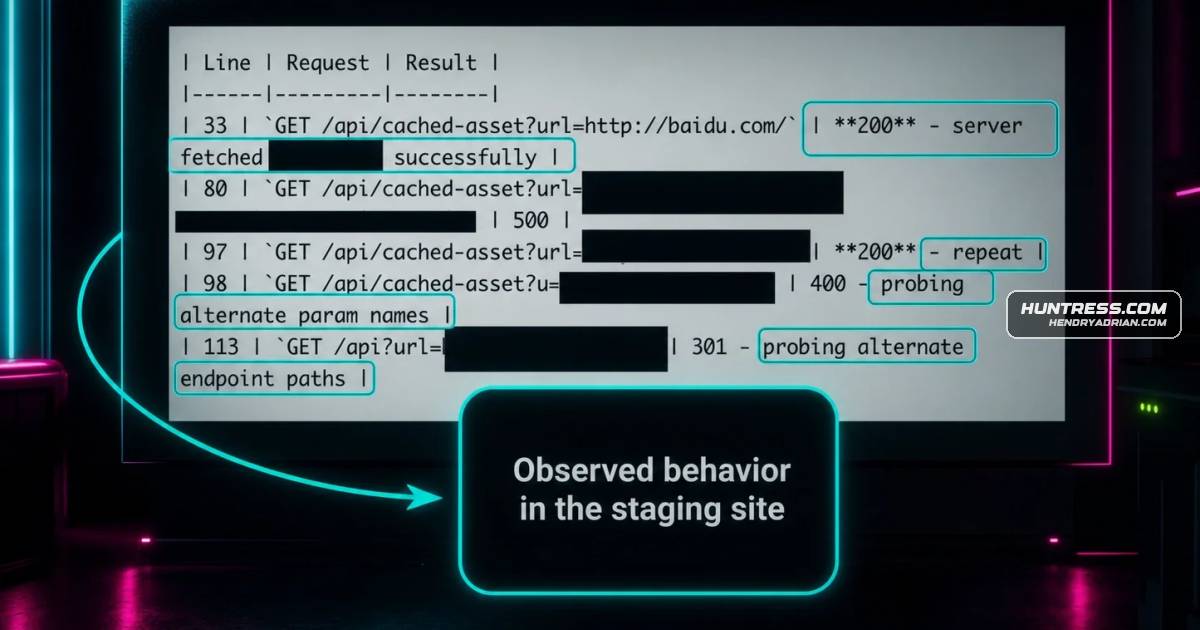
After an authorized researcher found a vulnerability in Huntress’s staging environment, the company says it fixed the issue within minutes, before the report arrived, with no customer impact. Huntress urges consistent security for non-production systems.

Apr 10, 2026
Security Insights · securityweek.com

Can Businesses Trust AI? Security Risks and Emerging Guardrails

The article examines AI risks including hallucinations, bias, sycophancy and model collapse, and describes emerging defenses such as data provenance, lifecycle guardrails, red teaming and prompt-injection controls.

Apr 9, 2026
Security Insights · thehackernews.com

Why AI Need Not Be Innovative to Raise Cyber Risk

The author argues that AI is not yet reliable enough for autonomous, sophisticated attacks but could scale low-cost attacks against standardized environments. The article recommends basic security hygiene, hardening, and active monitoring.

Apr 9, 2026
Security Insights · proofpoint.com

Anthropic Leak and Mercor Supply-Chain Attack: Lessons for Enterprise AI Security

The article uses the reported Anthropic source-code exposure and Mercor LiteLLM supply-chain compromise to highlight risks from release errors, dependencies and data flows, and urges stronger DLP, email security and visibility into AI use.

Apr 9, 2026
Security Insights · bleepingcomputer.com

How Credential Exposure Can Undermine Legacy MFA

Sponsored analysis uses a reported Figure exposure of nearly 967,200 email records to explain credential stuffing, targeted phishing, help-desk social engineering and real-time phishing relays, then promotes Token’s biometric, hardware-bound authentication.

Apr 9, 2026
Security Insights · hackingarticles.in

Using pywerview to Enumerate Active Directory and Identify Privilege Risks

An Active Directory enumeration walkthrough shows how pywerview queries can reveal privileged accounts, Kerberoastable service accounts, delegation settings, and group memberships that may enable privilege escalation.

Apr 8, 2026
Security Insights · darkowl.com

What Movies and TV Get Right—and Wrong—About Hacking

A review of Mr. Robot, WarGames, and Blackhat highlights realistic portrayals of social engineering and system access, contrasts them with Hollywood’s instant-hack tropes, and notes how WarGames influenced U.S. computer-security policy.

Apr 8, 2026
Security Insights · toxsec.com

Pillar Security Demonstrates Hidden-Unicode Backdoor Risk in AI Coding Rules Files

Pillar Security demonstrated how invisible Unicode instructions in shared AI coding rules files could prompt tools such as Cursor and GitHub Copilot to generate malicious code. The article also says explicit security constraints reduce insecure coding patterns.

Apr 8, 2026
PreviousPage 34 of 54 Next
© 2026 cyber.hendryadrian.com