cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · toxsec.com

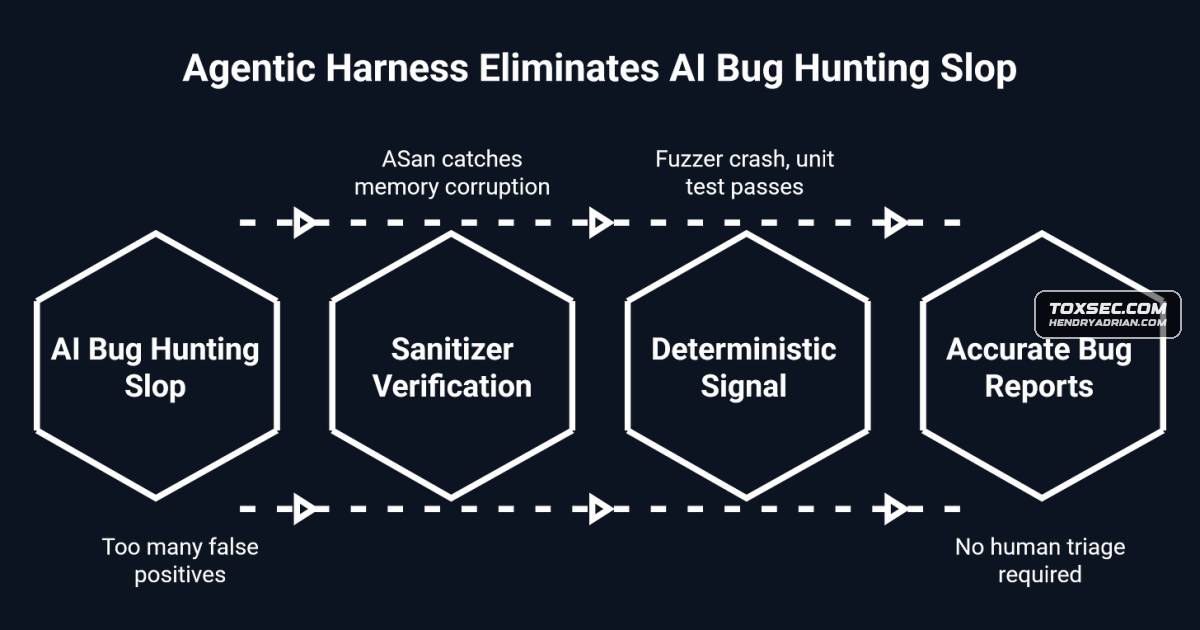
Mozilla’s AI Harness Found 271 Firefox Vulnerabilities Using AddressSanitizer

Mozilla says its agentic harness paired with Claude Mythos Preview found 271 vulnerabilities in Firefox 150, with fewer than 15 false positives. The article highlights AddressSanitizer-based validation and prior hardening that blocked some sandbox-escape attempts.

May 13, 2026
Security Insights · cisecurity.org

CIS Outlines Five Steps to Secure Cities Hosting Large-Scale Events

CIS recommends layered venue security, suspicious-activity reporting, cybersecurity controls, defenses against information operations, and coordinated communications to help cities prepare for large-scale events such as the 2026 FIFA World Cup.

May 12, 2026
Security Insights · blog.talosintelligence.com

How to Prepare for and Respond to State-Sponsored Cyber Intrusions

Talos explains how state-sponsored actors use legitimate credentials, trusted tools, and long-term access to evade detection, and outlines preparation and response measures including centralized logging, identity controls, OT segmentation, and supply-chain readiness.

May 12, 2026
Security Insights · wiz.io

How Wiz Uses Service Ownership to Make Security Findings Actionable

Wiz describes using its Service Catalog to group cloud risks by service, assign owners, and automate routing and remediation—reducing duplicate findings and helping security and engineering teams coordinate.

May 11, 2026
Security Insights · cyberscoop.com

Opinion: SMBs Need Affordable Cybersecurity Leadership

The article argues that vCISO and fractional CISO services can give small businesses affordable security leadership, and proposes government guidance, incentives and procurement requirements to encourage their use.

May 11, 2026
Security Insights · toxsec.com

Microsoft PyRIT Automates Multi-Turn LLM Red-Team Testing

A practical overview of Microsoft’s open-source PyRIT framework for automating LLM red-team tests, explaining its targets, converters, scorers, and orchestrators for multi-turn and indirect prompt-injection testing.

May 10, 2026
Security Insights · toxsec.com

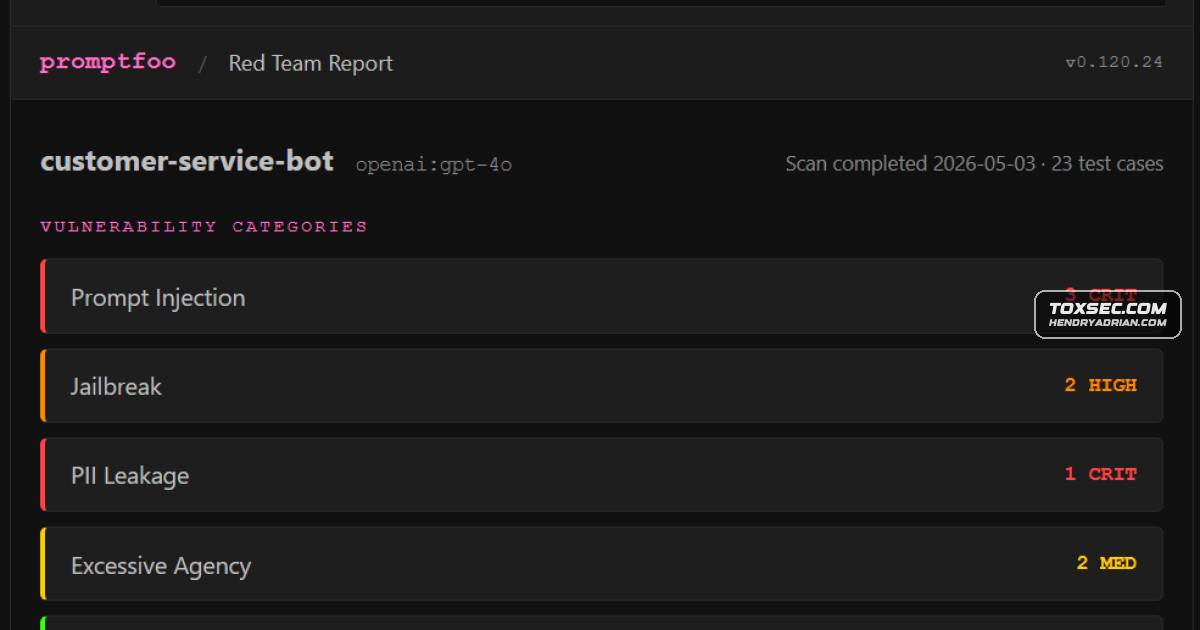
How Promptfoo Red-Teams LLM Applications in CI/CD

The article describes Promptfoo’s open-source LLM red-teaming workflow: YAML-configured tests use 50+ plugins and delivery strategies, run in CI/CD, and report findings with an LLM judge and framework mappings. It says OpenAI acquired the project in March 2026.

May 10, 2026
Security Insights · sentinelone.com

LABScon 2025 Talk Examines Risks in Overseas-Made Networked Devices

Joe FitzPatrick’s talk argues that hidden connectivity, supply-chain workarounds and mandatory activation undermine safeguards for imported devices. He recommends right-to-repair, offline-use guarantees, hardware and firmware bills of materials, and privacy legislation.

May 9, 2026
Security Insights · securitylabs.datadoghq.com

Kubernetes Secrets: Threat Models, Risks, and Protection Options

An explainer of Kubernetes secrets risks and protections covers storage in etcd and on worker nodes, exposure through APIs and workloads, and tradeoffs among Secret objects, mounted files, encryption, RBAC, and external providers.

May 8, 2026
Security Insights · decodedsecurity.com

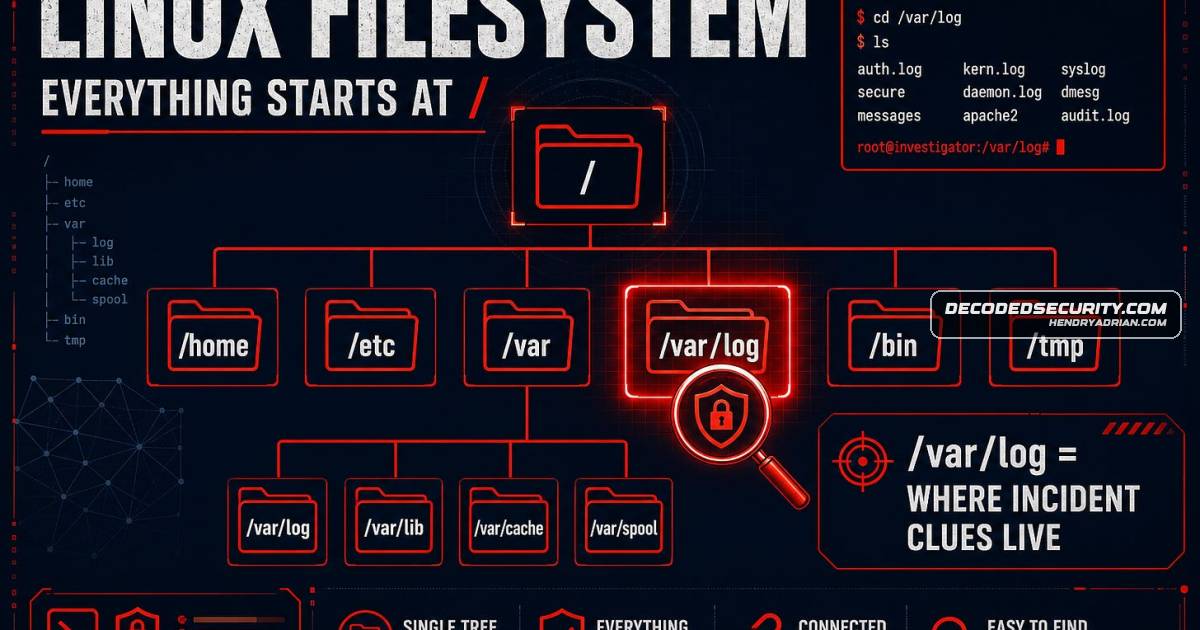
Linux Fundamentals for Beginners Entering Cybersecurity

A beginner’s guide to Linux concepts useful in cybersecurity, including the filesystem, permissions and distributions, with practice suggestions using Docker, dual booting and hands-on learning platforms.

May 8, 2026
Security Insights · toxsec.com

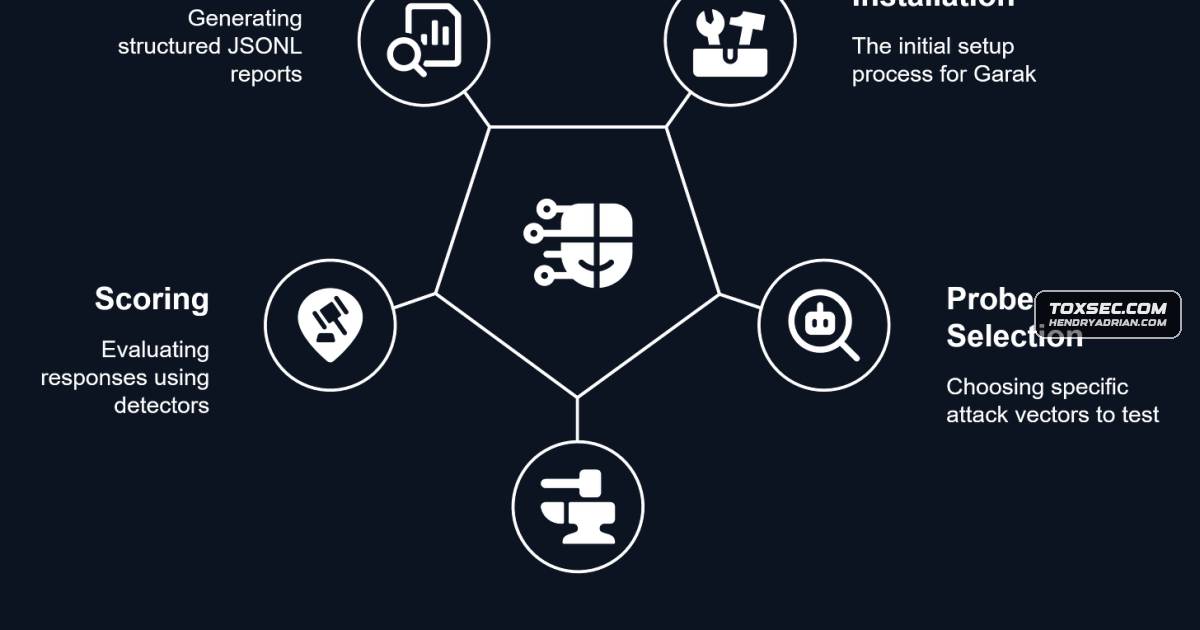
Garak Scans LLMs for Prompt Injection, Jailbreaks and Data Leakage

The article explains how NVIDIA’s open-source Garak scanner tests LLMs with probes, scores responses using detectors, and creates JSONL reports. It describes probe coverage, supported model connections, and an example scan’s findings.

May 6, 2026
Security Insights · darkowl.com

Webinar Explores Darknet Intelligence for Government and Enterprise Investigations

A DarkOwl webinar discusses how investigators use darknet data to track criminal activity, stolen credentials, marketplace listings, and actor movements, and how structured collection can support government and enterprise threat intelligence.

May 6, 2026
Security Insights · thehackernews.com

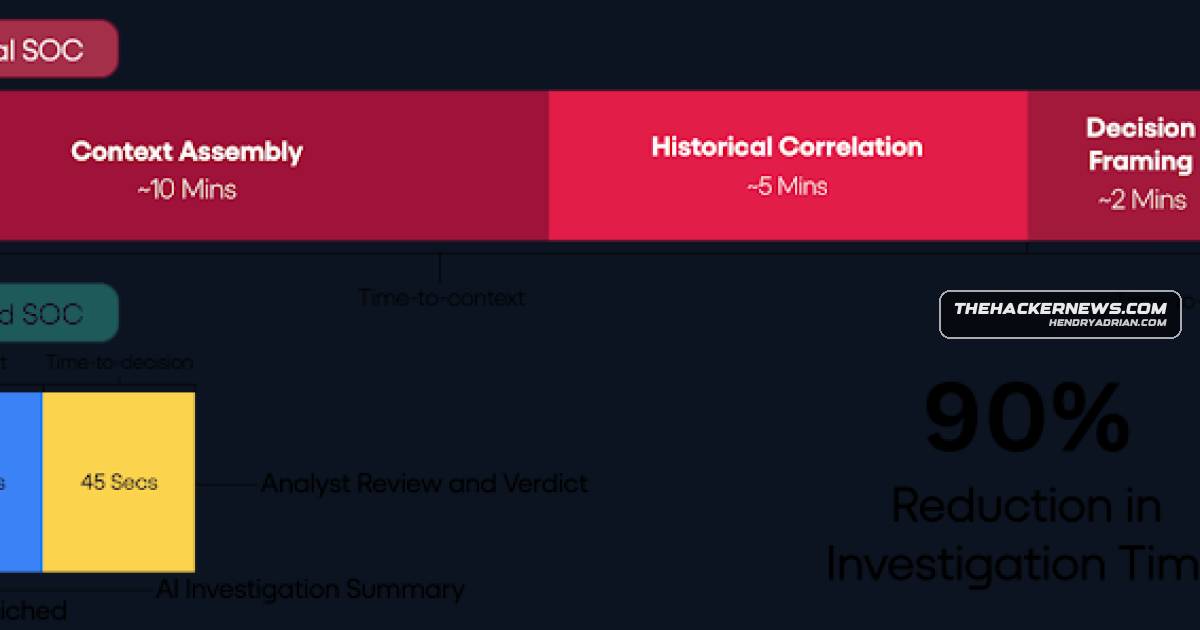
Offensive AI May Shrink Attack Timelines, Prompting Calls for Continuous Security Operations

The author argues that advances in offensive AI could shorten reconnaissance and exploit timelines, urging continuous alert investigation, detection evaluation and exposure-focused threat hunting; the article also promotes Prophet Security products.

May 6, 2026
Security Insights · trendmicro.com

Trend Micro Explains How Its TrendAI Platform Supports U.S. Cyber Strategy

Trend Micro maps its threat intelligence, compliance, zero-trust, AI, cloud, and legacy-system security capabilities to the first three pillars of the U.S. National Cyber Strategy, while promoting its Vision One platform to government agencies.

May 6, 2026
Security Insights · matthewrosenquist.substack.com

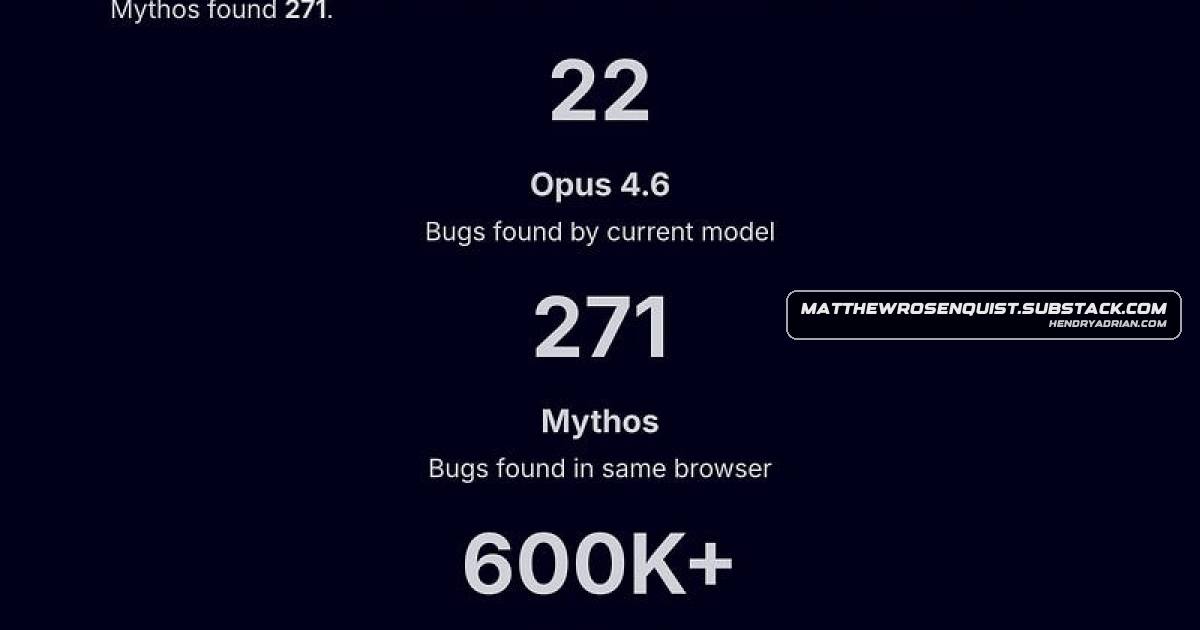
Anthropic’s Mythos Highlights the Cybersecurity Impact of AI-Accelerated Exploits

The article argues that Anthropic’s Mythos could accelerate vulnerability discovery, exploit creation and chaining, citing reported Mozilla Firefox testing and warning that defenders may need faster, AI-assisted discovery, response and patching.

May 5, 2026
Security Insights · securityweek.com

Joey Melo Explains AI Jailbreaking and Data Poisoning

CrowdStrike researcher Joey Melo describes how AI red teams probe model guardrails through prompt and context manipulation, and test susceptibility to data poisoning. He says jailbreaks have become harder, but ongoing AI changes bring new risks.

May 5, 2026
Security Insights · hackingarticles.in

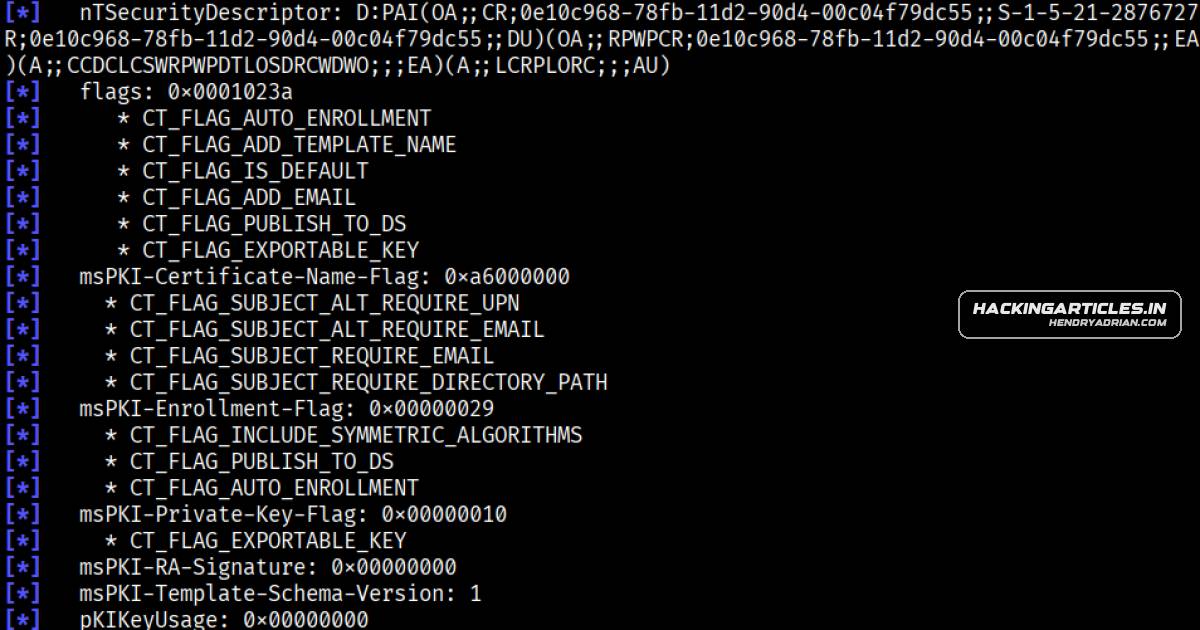
Metasploit Walkthrough Chains 13 Active Directory Attack Phases

A hands-on Metasploit lab walkthrough chains 13 Active Directory attack phases—from LDAP and Kerberos enumeration through AD CS abuse, RBCD, credential theft and Golden Tickets—and pairs them with defensive controls.

May 5, 2026
Security Insights · bleepingcomputer.com

HeroDevs Warns CVE Feeds Can Miss Vulnerabilities in End-of-Life Packages

A HeroDevs-sponsored analysis says scanners can miss vulnerabilities in end-of-life dependencies when advisories omit unsupported versions. It cites Spring Security 6.2 and software supply-chain data to illustrate the exposure.

May 5, 2026
Security Insights · bleepingcomputer.com

Why CVE Feeds and SCA Tools Can Miss End-of-Life Software

A sponsored HeroDevs analysis argues that CVE feeds and SCA tools can miss end-of-life dependencies when advisories omit unsupported versions. It cites a Spring Security example and reports 5.4 million EOL versions among 12 million package versions analyzed.

May 5, 2026
Security Insights · bleepingcomputer.com

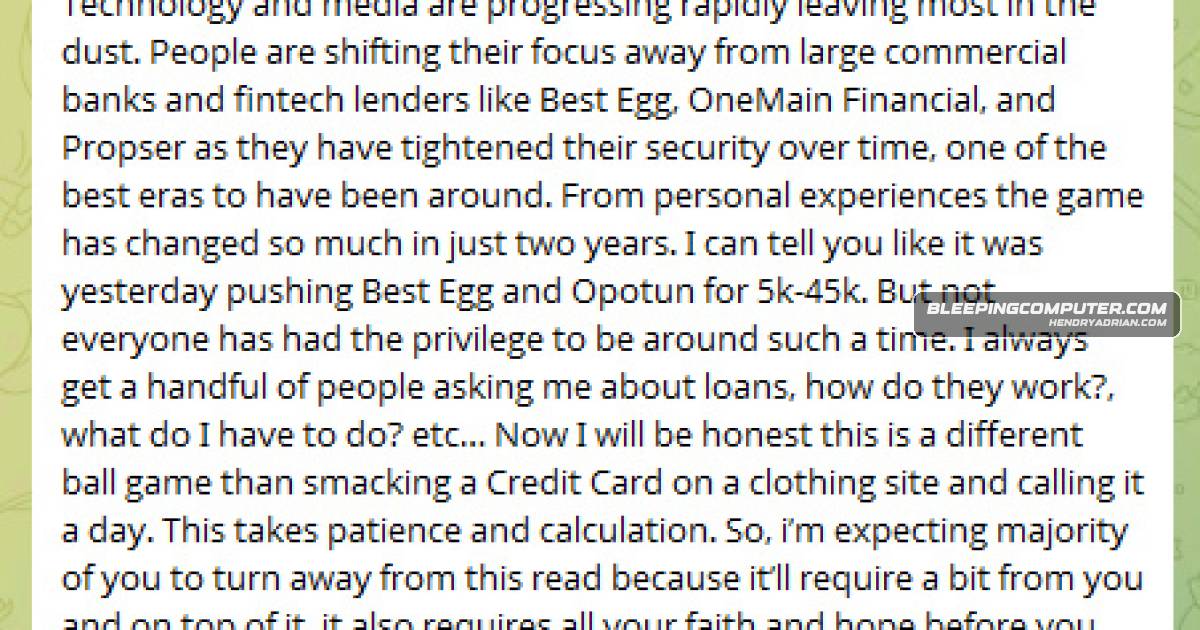
How Fraudsters Target Credit Unions With Stolen Identities

Flare researchers describe an underground loan-fraud method using stolen identities and prepared KBA answers to target small and midsize credit unions, secure loan approvals, and move funds before detection.

May 4, 2026
Security Insights · wiz.io

Wiz Guide Outlines Four Steps to Scale Cloud Security Operations

Wiz outlines four steps for scaling cloud security operations: automate risk remediation, integrate security into development, detect and respond to runtime threats, and measure program maturity.

May 4, 2026
Security Insights · decodedsecurity.com

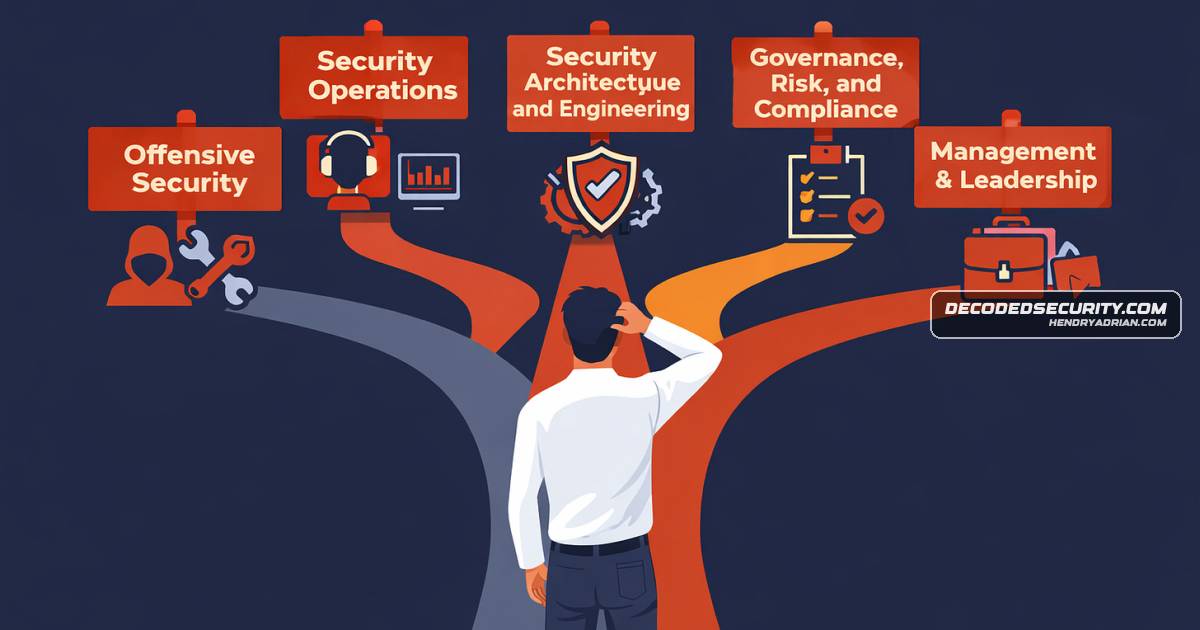
How to Choose Cybersecurity Certifications for Your Career Path

The article recommends choosing a cybersecurity role before selecting certifications, with role-specific paths for offensive security, SOC, cloud and engineering, GRC, and management. It emphasizes that credentials complement rather than replace skills and experience.

May 3, 2026
Security Insights · huntress.com

How Social Engineering Exploits Trusted Identities, Platforms, and Workflows

The article explains how attackers exploit trusted tools and workflows, including an EvilTokens campaign that used Microsoft device-code phishing to target 340+ organizations, and urges teams to prioritize identity behavior, clear ownership, and rapid response.

May 1, 2026
Security Insights · darktrace.com

Email-Borne Prompt Injections Could Expose Data Through Enterprise AI Assistants

Email-delivered prompt injections can manipulate AI assistants into exposing sensitive information or altering workflows. Darktrace reports increased signals of possible attempts and describes using prompt density, obfuscation, and behavioral context to detect them.

May 1, 2026
PreviousPage 31 of 54 Next
© 2026 cyber.hendryadrian.com