cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Security Insights

Curated cybersecurity insights, opinions, emerging technologies, AI security topics, and notable industry discussions.

1296 articles

Security Insights · cyberscoop.com

AI Agents Challenge Human-Centered Identity Security

Anthropic says it withheld Mythos after the model found thousands of previously unknown vulnerabilities. The article argues that AI-driven impersonation makes continuous identity checks, limited agent permissions, and behavioral monitoring increasingly important.
Apr 30, 2026
Security Insights · hackingarticles.in

Using Impacket-Net to Enumerate and Modify Active Directory

A lab walkthrough shows how Impacket-Net uses NTLM hashes, Kerberos tickets, and AES keys to enumerate and modify Active Directory users, groups, and computers, then outlines hardening and monitoring measures.

Apr 30, 2026
Security Insights · bleepingcomputer.com

Sponsored Analysis Warns Newly Exposed Assets Can Be Probed Within Minutes

A Sprocket Security-sponsored article describes how public assets may be scanned and probed soon after exposure, citing a study in which 80% of 320 honeypots were compromised within 24 hours and a company-reported unauthenticated API exposure.

Apr 30, 2026
Security Insights · threatfabric.com

How Fraud and Digital Scams Help Fuel Human Trafficking

An interview with Traffik Analysis Hub president Neil Giles explores how scams and digital payment channels can support human trafficking, and why prevention requires organizations to share intelligence and look beyond transactions.

Apr 30, 2026
Security Insights · darktrace.com

AI-Accelerated Vulnerability Discovery Challenges Disclosure-Led Defense

The article argues that AI may enable vulnerability discovery and exploitation before public disclosure, making patching alone insufficient. It advocates behavioral monitoring and rapid containment, and cites Darktrace detections that it says preceded CVE publication.

Apr 30, 2026
Security Insights · hackingarticles.in

Active Directory User Enumeration: 16 Techniques and Defenses

A hands-on guide demonstrates 16 ways to enumerate Active Directory users through LDAP, SAMR, RPC, LSARPC and Windows APIs, then outlines monitoring and hardening measures including LDAP auditing, RPC monitoring, honey accounts and privilege tiering.

Apr 29, 2026
Security Insights · wiz.io

Wiz Explains Applying Australia’s Modern Defensible Architecture to Cloud Security

Wiz outlines how its cloud security platform can support Australian government departments applying the ACSC’s Modern Defensible Architecture, including layered defenses, Zero Trust, secure-by-design practices, and continuous assurance.

Apr 29, 2026
Security Insights · decodedsecurity.com

A Beginner’s Study Roadmap for Cybersecurity GRC

The article proposes a beginner’s GRC learning path: study cybersecurity fundamentals first, then policies, access control, risk management, continuity, and legal topics, followed by practical scenario exercises.

Apr 29, 2026
Security Insights · team-cymru.com

Network Telemetry Reveals Nation-State Pre-Positioning in the Defense Industrial Base

The article describes how nation-state actors prepare access to Defense Industrial Base networks, often targeting smaller contractors and edge infrastructure, and argues that network telemetry and shared intelligence can help identify activity before it escalates.

Apr 29, 2026
Security Insights · thehackernews.com

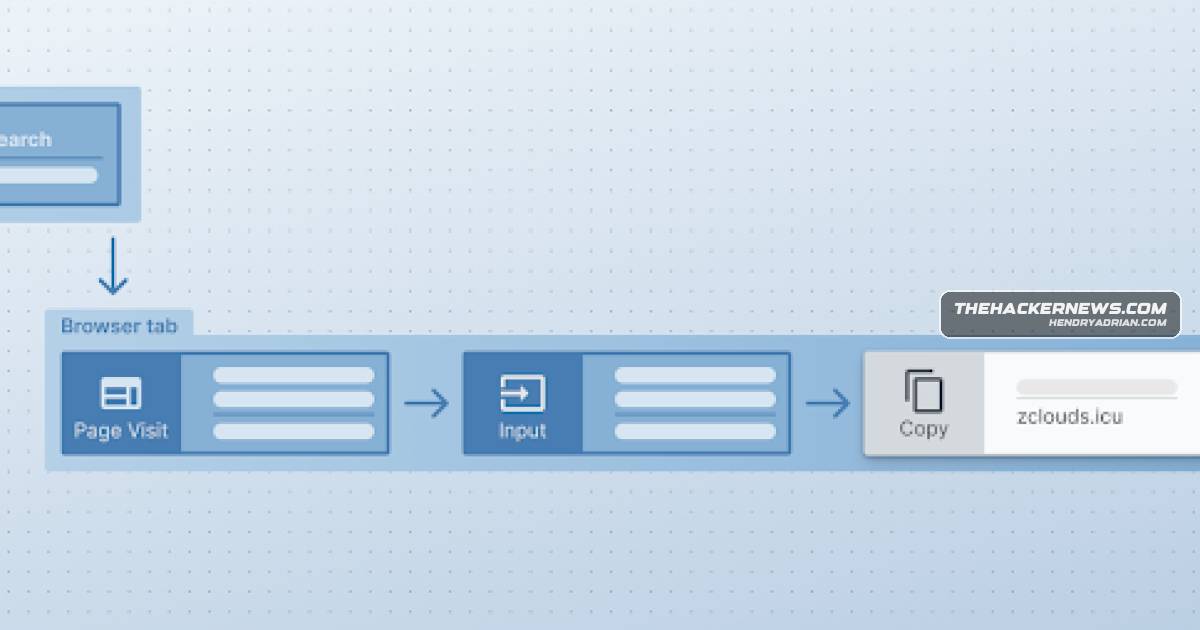
Why AI Is Exposing the Browser Security Visibility Gap

The article argues that browser-based work obscures user and agent actions from traditional security tools. A ClickFix example illustrates the gap, and the author advocates browser-level visibility, governance, and response.

Apr 28, 2026
Security Insights · cisecurity.org

What Cybersecurity Leaders Should Know About AI-Accelerated Vulnerability Discovery

CIS argues that AI may increase the speed and volume of vulnerability discovery, but established defenses remain relevant. It urges leaders to prioritize asset visibility, secure configurations, response readiness, and collaboration.

Apr 28, 2026
Security Insights · darkowl.com

What CIRCIA Requires of Critical Infrastructure Organizations

The article explains CIRCIA’s planned incident and ransomware-payment reporting deadlines, expected coverage, and how DarkOwl says its dark web intelligence and credential monitoring can support preparation.

Apr 28, 2026
Security Insights · picussecurity.com

Chinese State-Backed Threat Actors: Key Tactics and Defensive Priorities

A Picus overview of Chinese state-backed threat actors highlights shared relay networks built from compromised edge devices, contractor and tooling ecosystems, rapid appliance exploitation, stealth techniques, and defenses including patching, device replacement and en

Apr 28, 2026
Security Insights · thehackernews.com

Mythos Could Accelerate Vulnerability Discovery Faster Than Teams Can Remediate

The article argues Claude Mythos could accelerate vulnerability discovery while many teams lack workflows to triage and verify fixes, recommending centralized findings, risk-based prioritization and closed-loop remediation; it promotes PlexTrac.

Apr 27, 2026
Security Insights · helpnetsecurity.com

Why Traditional IAM Falls Short for AI Agents

The article argues that human-centric IAM cannot adequately govern AI agents across API workflows. It recommends application-centric runtime authorization with short-lived, least-privilege tokens using OAuth 2.0, token exchange and dynamic client registration.

Apr 27, 2026
Security Insights · helpnetsecurity.com

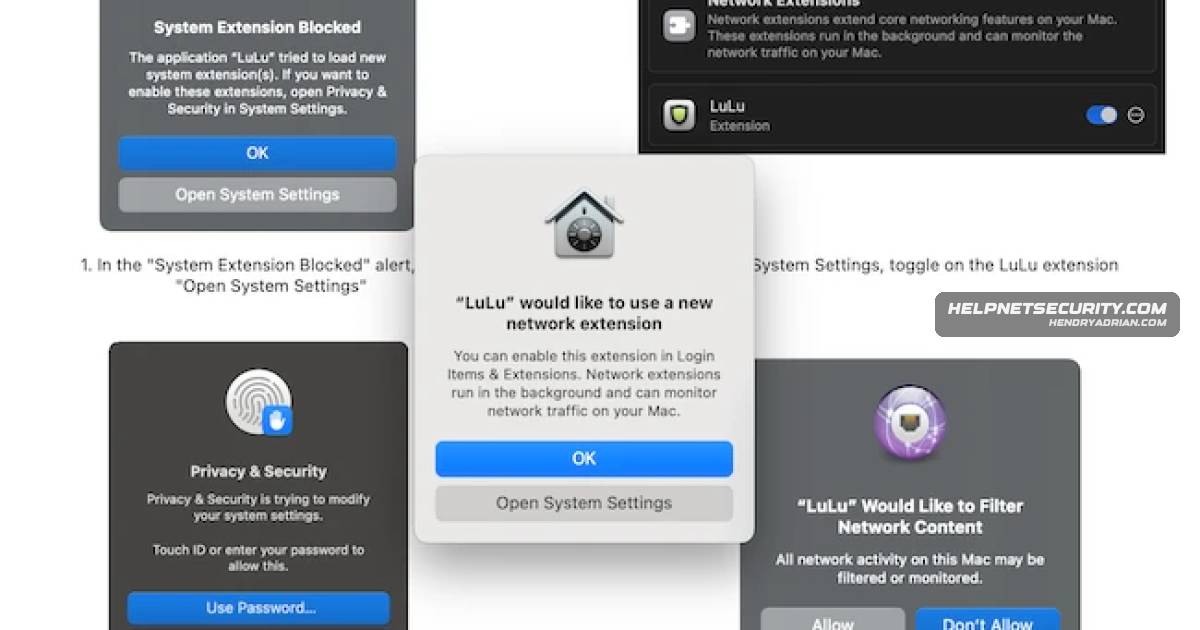
LuLu Firewall Helps Mac Users Monitor and Control Outbound Connections

A walkthrough of LuLu, a free, open-source macOS firewall that prompts users to allow or block apps’ outgoing connections, remembers rules, and offers live activity monitoring through Netiquette.

Apr 27, 2026
Security Insights · opensourcemalware.com

AI Coding Tools Can Reproduce Insecure Defaults in SaaS Applications

Following Vercel and Lovable security incidents, OpenSourceMalware describes recurring risks in AI-generated apps, including exposed secrets, weak authorization, permissive storage, unverified webhooks, and unvetted dependencies.

Apr 26, 2026
Security Insights · darkreading.com

Glasswing’s AI Code Discovery Highlights Security Gaps Beyond Code

Anthropic’s Project Glasswing and Mythos Preview’s reported discovery of a longstanding FFmpeg flaw illustrate the limits of pattern-based tools; the opinion argues teams must also continuously review identities, configurations, integrations and asset inventories.

Apr 25, 2026
Security Insights · hackingarticles.in

Lab Walkthrough Demonstrates Active Directory GPO Abuse and Defenses

An Active Directory lab walkthrough shows how low-privilege users with delegated write access to a domain-linked GPO can deploy tasks, scripts, local administrators, and reverse shells, and describes ways to detect and mitigate the abuse.

Apr 25, 2026
Security Insights · toxsec.com

Claude Opus 4.7’s New Tokenizer Raises Token-Level Security Concerns

The article says Claude Opus 4.7’s tokenizer change increased token counts and may introduce unmapped glitch tokens and tokenization mismatches affecting safety filters. It notes no full Opus 4.7 glitch sweep has been published and urges retesting.

Apr 24, 2026
Security Insights · securityweek.com

Why Autonomous AI Agents Should Be Secured as Identities

The article argues that organizations should treat autonomous AI agents as identities and extend identity-security controls to them, including behavioral monitoring, risk-based access, least privilege, and lifecycle management.

Apr 24, 2026
Security Insights · helpnetsecurity.com

Microsoft’s Kaja Ciglic Calls for Broader Responses to State-Backed Cyber Operations

Microsoft policy executive Kaja Ciglic says state cyber programs are now integrated tools of national power, with automation and AI accelerating activity. She calls for cross-domain consequences, clearer NATO response pathways and standing government-private sectorcoord

Apr 24, 2026
Security Insights · decodedsecurity.com

Disaster Recovery Plans Need Progressive Testing to Validate Recovery Readiness

Untested disaster recovery plans may fail in exams and operations. The article compares plan reviews, walkthroughs, tabletop exercises, execution tests, parallel runs and full interruption tests, emphasizing increasing assurance, cost and operational risk.

Apr 23, 2026
Security Insights · hackingarticles.in

Tutorial Demonstrates AppLocker Bypasses Using Ligolo-NG

A hands-on tutorial demonstrates bypassing AppLocker and PowerShell restrictions in a simulated Windows environment using trusted binaries, reflective shellcode injection, and Ligolo-NG to establish a reverse TLS tunnel.

Apr 23, 2026
PreviousPage 32 of 54 Next
© 2026 cyber.hendryadrian.com