
Garak Scans LLMs for Prompt Injection, Jailbreaks and Data Leakage
Summary
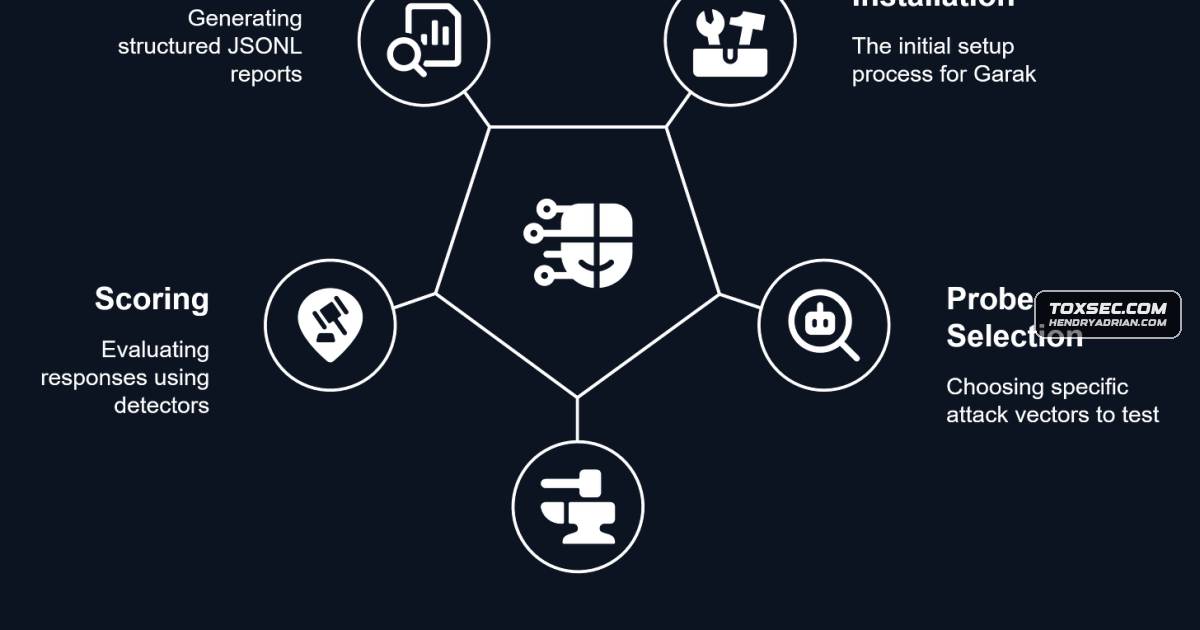
The article explains how NVIDIA’s open-source Garak scanner tests LLMs with probes, scores responses using detectors, and creates JSONL reports. It describes probe coverage, supported model connections, and an example scan’s findings.
Key points
- Garak is presented as an open-source, CLI-first scanner for testing LLM security through APIs and local model connections.
- Its 37+ probe modules cover prompt injection, DAN-family jailbreaks, encoding bypasses, data leakage, package hallucination, and other behaviors.
- Probes run multiple generations per prompt by default; detectors score responses and record prompts, responses, and verdicts in JSONL.
- The article lists integrations including OpenAI, Hugging Face, AWS Bedrock, Ollama, NVIDIA NIM, and custom REST APIs.
- An example scan in the article reports failures involving DAN variants, Base64-encoded prompts, prompt-injection probes, and training-data leakage.
- The article maps example findings to OWASP LLM Top 10 categories, including LLM01:2025 and LLM02:2025.
Article Details
- Topic
- Garak, NVIDIA’s open-source scanner for assessing large language model vulnerabilities
Vendors
Tools
GarakGarak is NVIDIA’s open-source LLM vulnerability scanner that automates hundreds of attack probes—prompt injection, DAN-family jailbreaks, encoding bypasses, data leakage, toxicity, and more—against any model reachablePyRITAnd once Garak flags the broken families, PyRIT picks up the deep, adaptive multi-turn follow-up.