
Metasploit Walkthrough Chains 13 Active Directory Attack Phases
Summary
A hands-on Metasploit lab walkthrough chains 13 Active Directory attack phases—from LDAP and Kerberos enumeration through AD CS abuse, RBCD, credential theft and Golden Tickets—and pairs them with defensive controls.
Key points
- The walkthrough uses Metasploit modules to enumerate users, groups, computers, domain policies and certificate templates in a Windows Server 2019 Active Directory lab.
- Demonstrated techniques include AS-REP roasting, Kerberoasting, credential dumping, pass-the-hash and pass-the-ticket, RBCD abuse, Shadow Credentials and certificate-template abuse.
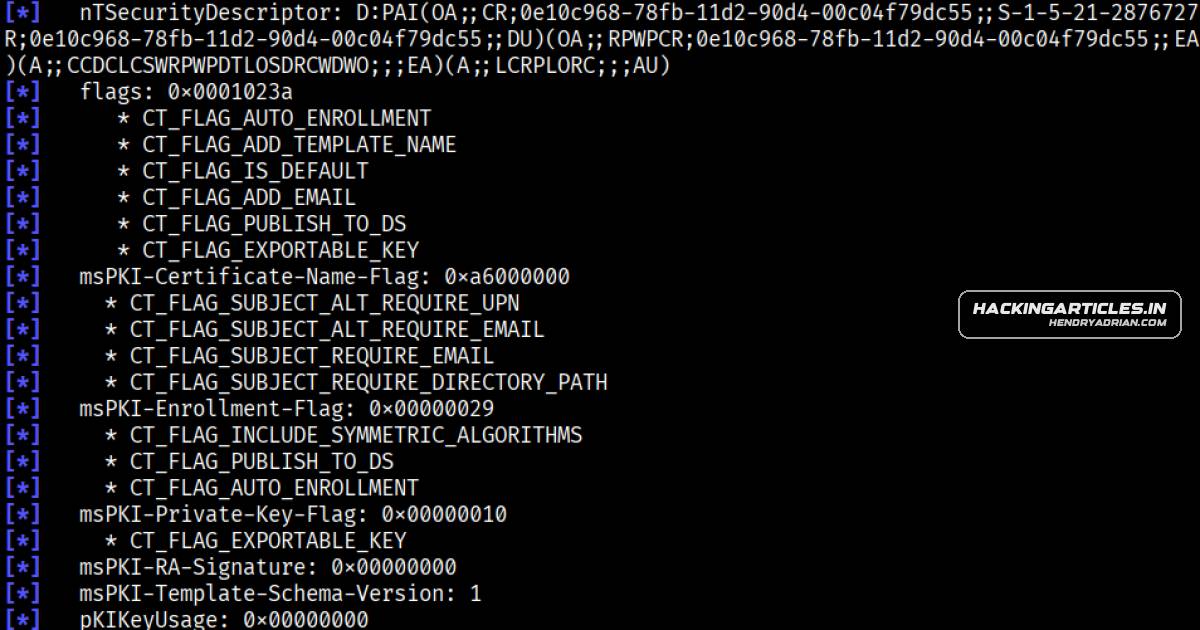
- The article shows how ESC1 and ESC4 certificate-template misconfigurations can enable privileged-account impersonation and credential extraction.
- It connects a default MachineAccountQuota of 10 to rogue computer-account creation and subsequent RBCD or Shadow Credentials techniques.
- The chain culminates in forged Kerberos tickets, including a Golden Ticket, for persistent domain-level access.
- Defensive recommendations include setting MachineAccountQuota to zero, hardening certificate templates, rotating the krbtgt secret, and monitoring LDAP changes and anomalous Kerberos activity.
Article Details
- Topic
- Metasploit-based Active Directory exploitation walkthrough and defensive mitigations
MITRE ATT&CK
T1003.002 · Security Account ManagerThe secretsdump workflow extracts local SAM account hashes.T1003.003 · NTDSThe walkthrough describes extracting domain credential hashes from NTDS.dit.T1021.002 · SMB/Windows Admin SharesThe operator uses SMB and the ADMIN$ share to access the Domain Controller remotely.T1136.002 · Domain AccountThe operator creates a new domain user account as a persistence mechanism.T1550.002 · Pass the HashThe operator uses recovered NTLM hashes to authenticate to hosts and execute commands through Pass-the-Hash.T1550.003 · Pass the TicketThe operator replays Kerberos service tickets and a forged ticket to access domain resources.T1558.001 · Golden TicketThe operator uses the krbtgt hash to forge a Golden Ticket for unrestricted domain access.T1558.003 · KerberoastingThe walkthrough requests Kerberos service tickets for SPNs and describes offline cracking of the returned material.T1558.004 · AS-REP RoastingThe walkthrough identifies accounts without Kerberos pre-authentication and requests AS-REP material for offline password cracking.T1569.002 · Service ExecutionThe PSEXEC workflows install and execute a service on the Domain Controller to obtain remote code execution.T1649 · Steal or Forge Authentication CertificatesThe operator abuses certificate templates to obtain authentication certificates impersonating privileged accounts.
Vendors
Products
Active Directory Certificate ServicesActive Directory Certificate Services HardeningMicrosoft Active Directoryprovides an end-to-end Metasploit-based walkthrough showing how an attacker can chain thirteen Active Directory attack phases to escalate from a low-privileged user to full domain compromise on a Windows ServerWindows Server 2019Directory attack phases to escalate from a low-privileged user to full domain compromise on a Windows Server 2019 environment.
Tools
certipyThe auxiliary/gather/ldap_esc_vulnerable_cert_finder module is Metasploit’s automated answer to Certipy’s find command.gmsadumperThe ENUM_GMSA_HASHES action queries this attribute and returns the blob ready for offline cracking with tools like gmsadumper or impacket-gMSADumper.hashcatMetasploit ships a dedicated auxiliary/gather/asrep module that constructs an unauthenticated AS-REQ for the target user and prints the resulting AS-REP encrypted blob in Hashcat format ($krb5asrep$).ImpacketTools: Metasploit, impacket-psexecimpacket-gMSADumperThe ENUM_GMSA_HASHES action queries this attribute and returns the blob ready for offline cracking with tools like gmsadumper or impacket-gMSADumper.impacket-psexecTools: Metasploit, impacket-psexecMetasploit FrameworkMetasploit Framework bundles dozens of auxiliary modules designed exclusively for Active Directory reconnaissance and exploitation.MimikatzThe ccache file can be replayed via impacket-psexec or any other Kerberos-aware tool, while the Kirbi format suits Mimikatz-based replay on Windows.PSPKIAuditAudit Template ACLs Quarterly: Run Certipy or PSPKIAudit against the entire template catalogue; any non-administrative principal with WriteProperty, WriteDacl, or WriteOwner on a template is an ESC4 vector.RubeusKerberos, AD CS, and SMB modules consolidate every primitive that historically required Impacket scripts, Rubeus binaries, Certipy installations, and Mimikatz invocations into a single, scriptable console.