
How to Choose Cybersecurity Certifications for Your Career Path
Summary
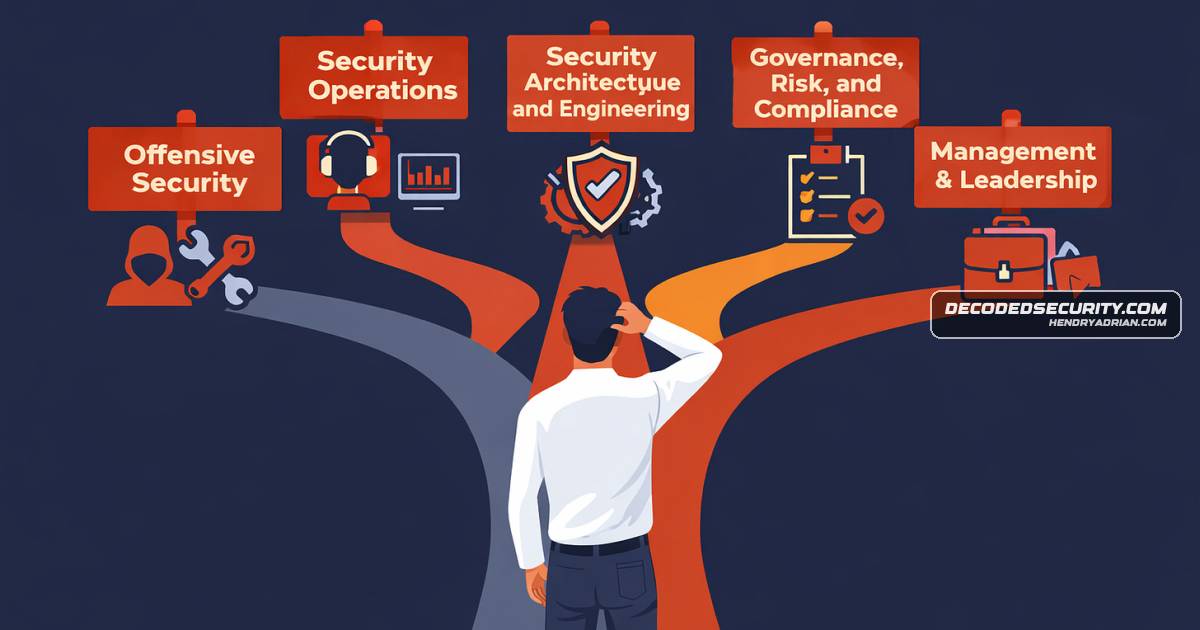
The article recommends choosing a cybersecurity role before selecting certifications, with role-specific paths for offensive security, SOC, cloud and engineering, GRC, and management. It emphasizes that credentials complement rather than replace skills and experience.
Key points
- For offensive security, the article recommends eJPT, then PenTest+, with OSCP as a practical credential.
- For SOC roles, it suggests Security+ followed by CySA+, with ISC2 CC as a free foundational option.
- For cloud security, choose AWS or Azure based on target employers and build depth on one platform.
- For engineering, it recommends Security+ and CASP+; software developers moving into security may consider CSSLP.
- For GRC, it maps CRISC to risk management, CISM to governance and management, and CISA to auditing and compliance.
- For senior management, it emphasizes CISSP while noting that certification does not replace experience or interview skills.
Article Details
- Topic
- Career-path-based recommendations for choosing cybersecurity certifications across offensive security, SOC, cloud engineering, GRC, and management.
Vendors
Amazon Web ServicesCloud and engineering roles require platform-specific certs—choose AWS or Azure and go deep on one.CompTIASOC roles: begin with CompTIA Security+ and progress to CompTIA CySA+ for detection and response skills.eLearnSecurityeJPT (eLearnSecurity Junior Penetration Tester) is the most realistic first cert for this path.ISC2ISC2 CC is worth considering before Security+ if you want a free way to prove foundational knowledge while you prepare.MicrosoftAWS Security Specialty or Microsoft SC-900 / AZ-500 are the right starting points, depending on which platform dominates your target market.