
Mozilla’s AI Harness Found 271 Firefox Vulnerabilities Using AddressSanitizer
Summary
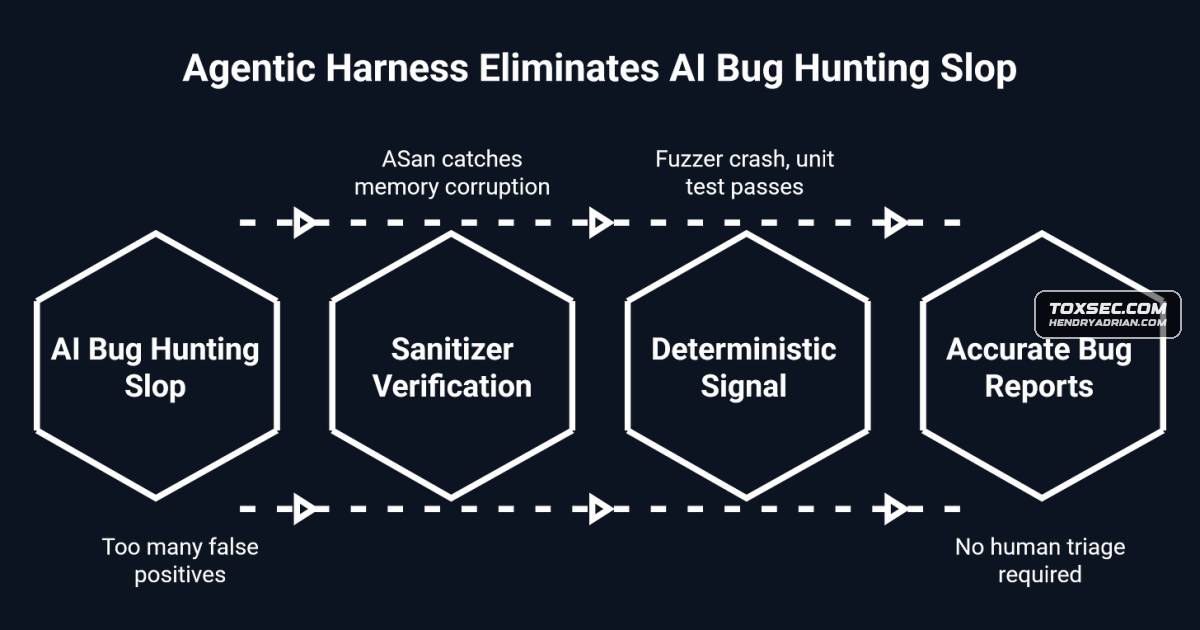
Mozilla says its agentic harness paired with Claude Mythos Preview found 271 vulnerabilities in Firefox 150, with fewer than 15 false positives. The article highlights AddressSanitizer-based validation and prior hardening that blocked some sandbox-escape attempts.
Key points
- The harness gave Claude Mythos Preview target Firefox source and a sanitizer build, then iterated on proof-of-concept code until AddressSanitizer reported a crash; a second model graded reports before engineering triage.
- Mozilla reports 271 vulnerabilities fixed in Firefox 150, plus additional fixes in versions 149.0.2, 150.0.1, and 150.0.2.
- Mozilla says the run produced fewer than 15 false positives; the reported bugs were rated 180 sec-high, 80 sec-moderate, and 11 sec-low.
- Examples included an IPC race involving IndexedDB refcounts and a use-after-free, a fake-object primitive, and a buffer over-read during HTTPS RR and ECH parsing.
- The article says previously frozen prototypes blocked the model’s attempts to use prototype pollution for sandbox escape.
- The article stresses that reproducing the results requires more than the model, including a sanitizer toolchain, verification and bug-lifecycle systems, and engineers to handle patches.
Article Details
- Topic
- Mozilla's agentic harness uses Claude Mythos Preview and AddressSanitizer crash verification to find vulnerabilities in Firefox.
People
Vendors
AnthropicMozilla used an agentic harness with Anthropic’s Claude Mythos Preview to test Firefox 150, and the setup found 271 vulnerabilities with fewer than 15 false positives by using AddressSanitizer crashes as the proofMozillaMozilla used an agentic harness with Anthropic’s Claude Mythos Preview to test Firefox 150, and the setup found 271 vulnerabilities with fewer than 15 false positives by using AddressSanitizer crashes as the proof
Products
Claude Mythos PreviewMozilla used an agentic harness with Anthropic’s Claude Mythos Preview to test Firefox 150, and the setup found 271 vulnerabilities with fewer than 15 false positives by using AddressSanitizer crashes as the proofMozilla FirefoxMozilla used an agentic harness with Anthropic’s Claude Mythos Preview to test Firefox 150, and the setup found 271 vulnerabilities with fewer than 15 false positives by using AddressSanitizer crashes as the proof