
How Data Classification Guides Security Controls
Summary
The article explains how organizations classify data by sensitivity and potential impact, then use those categories to set security requirements and guide access control, compliance, incident response, and DLP.
Key points
- Classify information by sensitivity and the potential impact of loss or unauthorized disclosure.
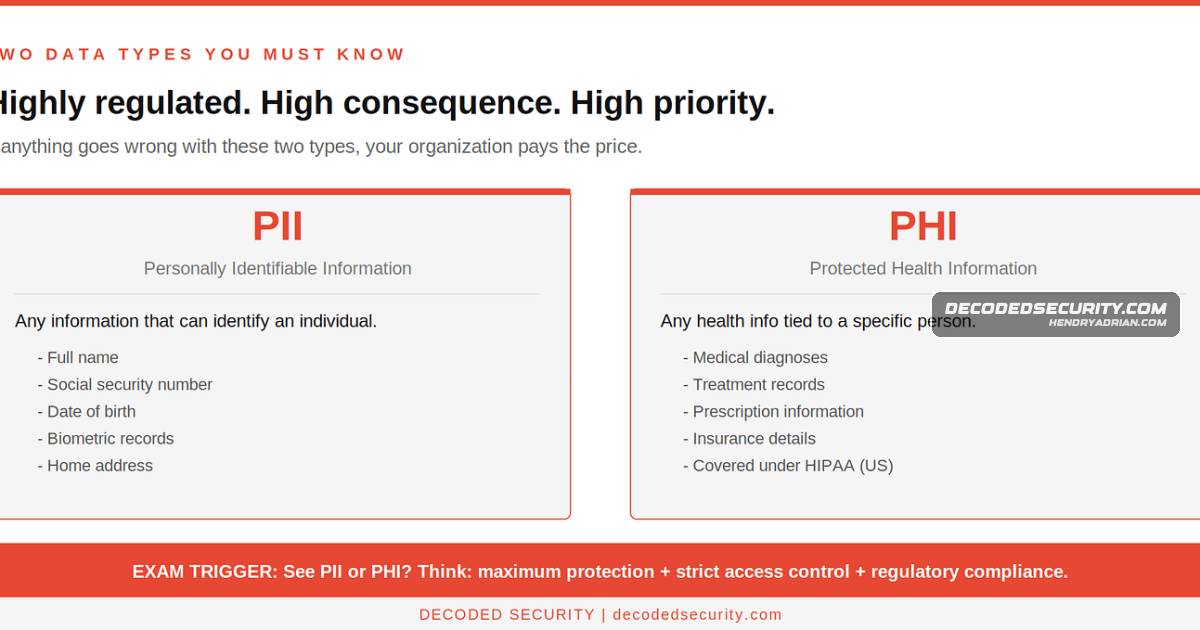
- PII and PHI require high-sensitivity classifications and strict protection.
- The proposed process is to define categories, set minimum requirements, classify data, then apply controls.
- Data owners should help classify information because they understand its value and use.
- Classification helps apply least privilege, meet compliance requirements, prioritize monitoring, and prepare incident response.
Article Details
- Topic
- Data classification and its role in information protection, access control, compliance, incident response, and data loss prevention