
VPN Basics: Trust, Tunnels, and Key Protocols Explained
Summary
A beginner-friendly VPN explainer covers encrypted tunnels, the trust shifted to VPN providers, client/tunnel/server components, and differences among PPTP, L2TP, and IPsec.
Key points
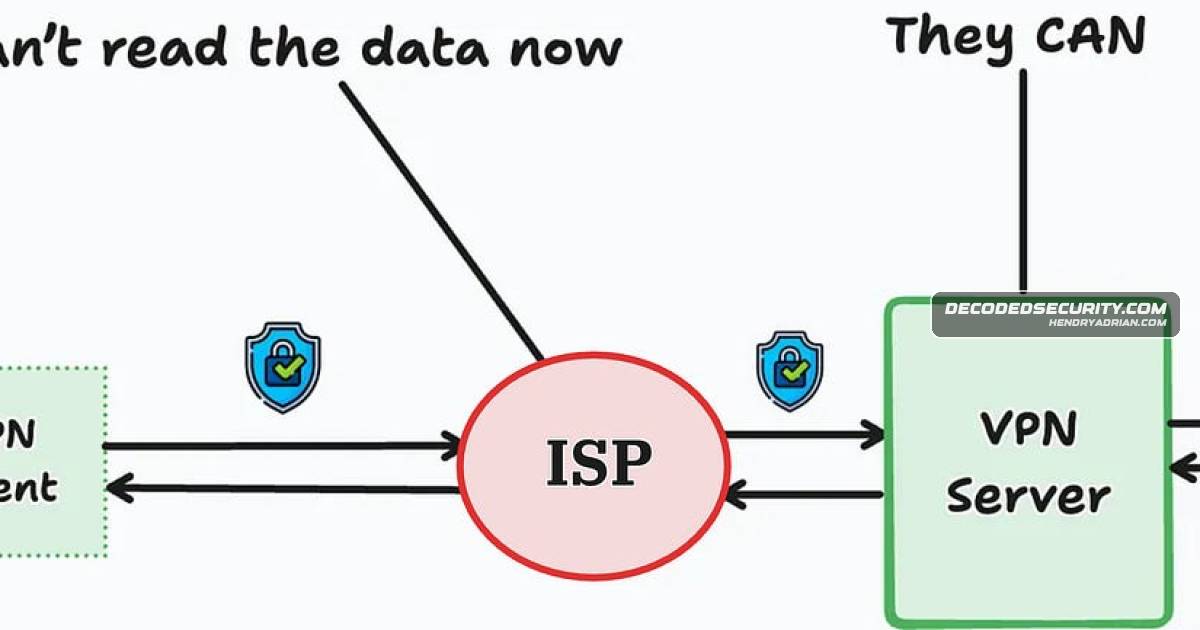
- A VPN creates an encrypted tunnel between a device and a remote server over an untrusted network.
- Using a VPN shifts trust from the ISP to the VPN provider; it does not make users anonymous.
- The VPN client manages the connection, the tunnel carries traffic, and the server decrypts and forwards it.
- The article describes PPTP as obsolete and insecure, and advises against using it.
- L2TP does not provide encryption on its own; the article says it is commonly paired with IPsec.
- IPsec is presented as a protocol suite; AH provides integrity and authentication without encryption, while ESP encrypts packet payloads.
Article Details
- Topic
- VPN fundamentals, trust considerations, and protocols including PPTP, L2TP, and IPsec