
Orchid Says Identity Visibility Platforms Can Expose Gaps Beyond Centralized IAM
Summary
Orchid Security describes IVIP as a way to uncover identity activity beyond centralized IAM, citing its application-level analysis and audit findings. The article also recommends attribution, audit trails, least privilege, and guardrails for AI agents.
Key points
- Orchid estimates that 46% of enterprise identity activity occurs outside centralized IAM visibility.
- The company says its platform uses binary analysis and dynamic instrumentation to inspect application authentication and authorization without APIs or source-code changes.
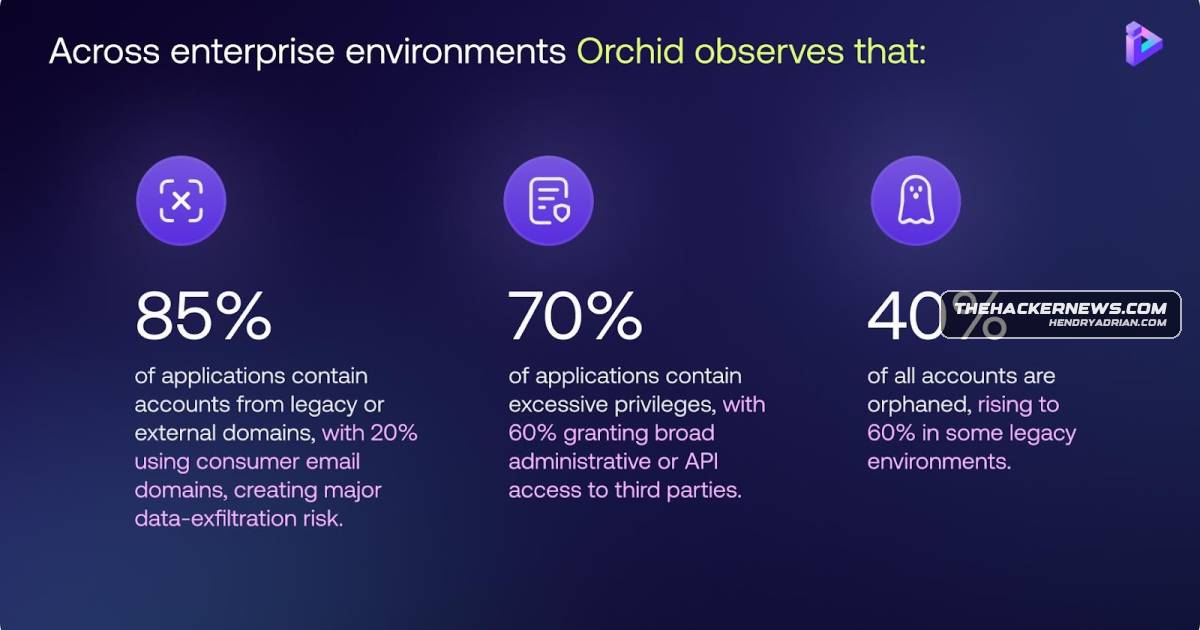
- Orchid reports that its audits found legacy or external-domain accounts in 85% of applications, excessive privileges in 70%, and orphaned accounts representing 40% of accounts; the article gives no audit scope or methodology.
- For AI agents, the article recommends human-owner attribution, activity audit trails, context-aware guardrails, least privilege, and automated remediation.
- IAM leaders are advised to assess machine-identity risks, coordinate across teams, remediate posture gaps, and use identity visibility when integrating acquired assets.
Article Details
- Topic
- Identity Visibility and Intelligence Platforms (IVIPs) for enterprise identity visibility, governance, and AI-agent security