cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Detection & Defense

Actionable detection engineering, threat hunting, hardening, and defensive response guidance.

624 articles

Detection & Defense · bleepingcomputer.com

How Security Teams Can Evaluate AI SOC Tools

A sponsored guide outlines ways to evaluate AI SOC tools, including testing with realistic identity and asset context, comparing AI decisions with analysts, checking for model drift and adversarial robustness, and keeping humans in control of high-impact actions.
Jul 20, 2026
Detection & Defense · jamf.com

Jamf Adds Passkey Sign-In to Jamf ID

Jamf ID now supports passkey-only sign-in or passkeys as a second factor. Users can register passkeys in their account security settings; the same credential works across Jamf products that accept Jamf ID.

Jul 20, 2026
Detection & Defense · recordedfuture.com

How Threat Intelligence Can Support Proactive Threat Hunting

The article outlines threat-hunting foundations, methods, and lifecycle, recommending that teams combine internal telemetry with external threat intelligence to identify activity that evades automated defenses.

Jul 20, 2026
Detection & Defense · toxsec.com

Context Bombs Use AI Safety Guardrails to Disrupt Prompt-Injection Attacks

Context bombs are decoy content designed to trigger an AI agent’s safety refusal when it reads a planted secret. They can alert defenders and stall an operation, but can be bypassed and do not replace incident response.

Jul 19, 2026
Detection & Defense · decodedsecurity.com

Isolate Smart-Home Devices on a Separate Network to Limit Risk

Smart devices on a shared home network may provide attackers a foothold to discover and reach other devices if compromised. The article recommends using a guest network or IoT VLAN to limit that access while preserving internet connectivity.

Jul 17, 2026
Detection & Defense · huntress.com

How to Prevent and Detect Business Email Compromise

The guide recommends layered BEC defenses: verify financial requests through trusted channels, use MFA and email authentication, train employees to spot red flags, and monitor identities and mailboxes for suspicious activity.

Jul 17, 2026
Detection & Defense · toxsec.com

Canary Tokens Can Detect Prompt Extraction but Won’t Prevent It

The article explains using unique canary strings in LLM context to detect prompt extraction by scanning outputs. It recommends placing markers in different context regions and stresses that canaries detect leaks but do not prevent attacks or catch other exfiltration.

Jul 16, 2026
Detection & Defense · blog.talosintelligence.com

Should AI Lead Threat Hunts? A Case for Guardrails and Human Oversight

Talos author David J. Bianco argues that AI can help scale threat hunting, but should operate within narrow, carefully controlled tasks while humans retain responsibility for hunt strategy and novel analysis.

Jul 16, 2026
Detection & Defense · cloud.google.com

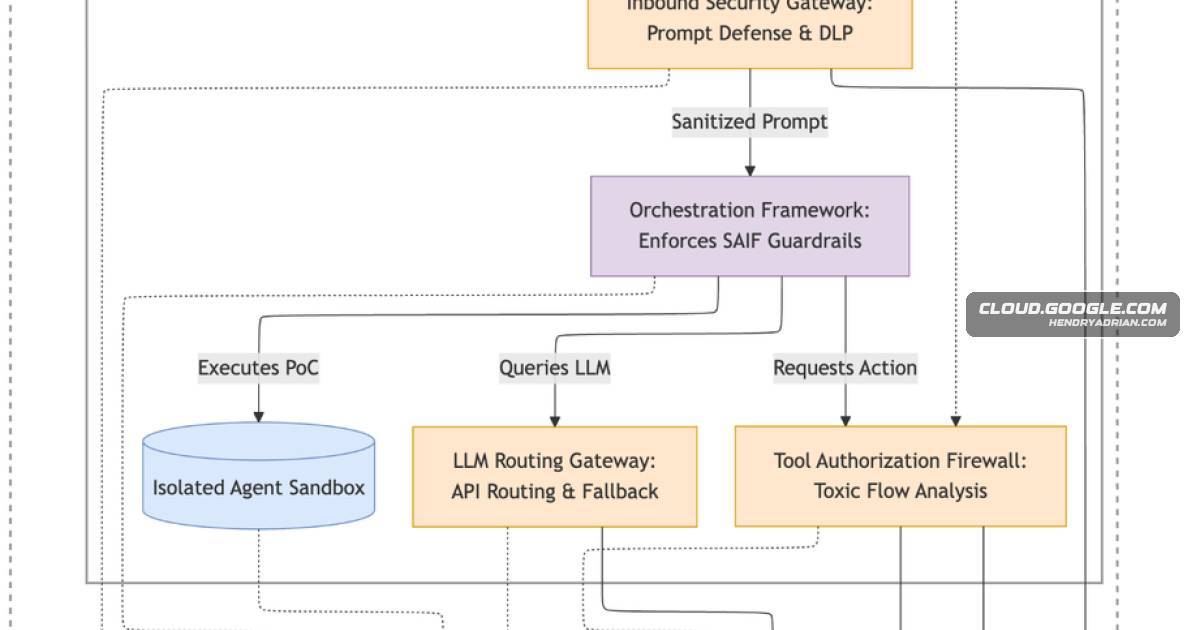
Mandiant Outlines Guardrails for AI-Assisted Vulnerability Management

Mandiant recommends combining AI agents with deterministic controls and human oversight to manage vulnerabilities safely, including sandboxing agents, restricting privileges, validating findings, and reviewing AI-generated fixes.

Jul 16, 2026
Detection & Defense · validin.com

Threat-Intelligence Pivots Uncover New Infrastructure Linked to SmartApeSG Campaign

A case study shows how analysts used Validin data and PacketWatch WireSight telemetry to investigate a fake software update campaign, pivot across infrastructure, identify dozens of potential indicators, and search client traffic for matches.

Jul 16, 2026
Detection & Defense · wazuh.com

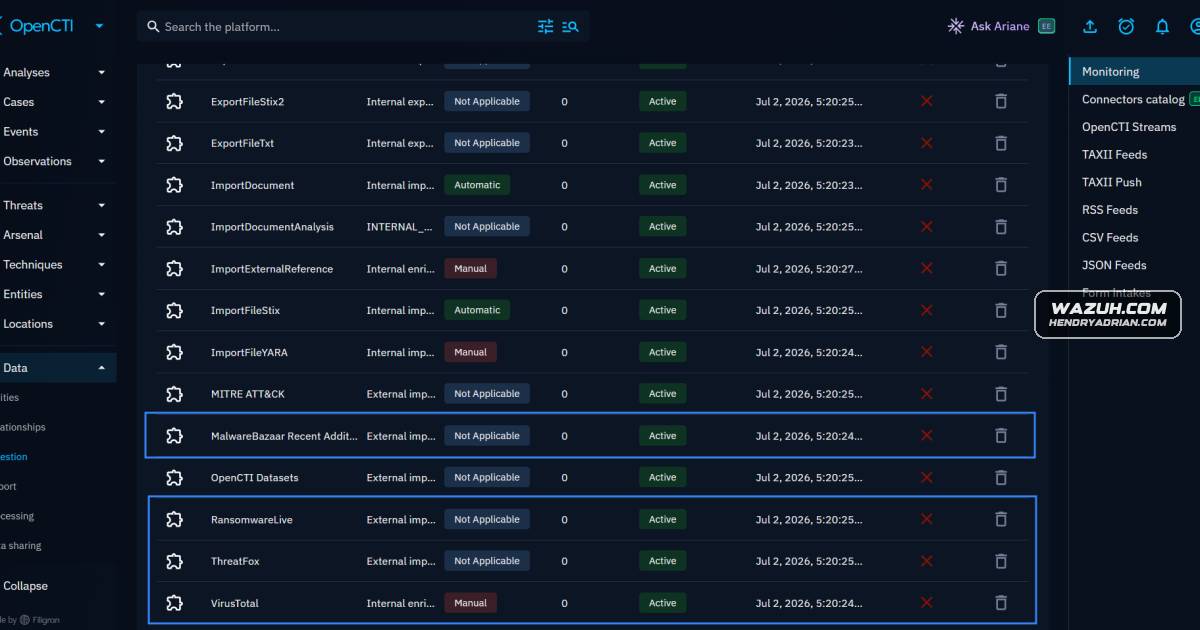
Wazuh and OpenCTI Integration Enriches Alerts with Real-Time Threat Intelligence

A Wazuh tutorial shows how to ingest threat intelligence into OpenCTI, query it from a custom integration, and use rules to enrich alerts with IOC matches, helping prioritize detections and support incident response.

Jul 15, 2026
Detection & Defense · cybersecuritypulse.net

A Field Guide to Detecting Risky Activity in AI Tooling Logs

A guide to visibility in logs from Claude Code, Cursor, OpenAI Enterprise and Codex, and Google Workspace Gemini, with detection ideas and limitations. It emphasizes combining log sources and adding context because no single source provides complete visibility.

Jul 15, 2026
Detection & Defense · cloud.google.com

Mandiant Details Risks and Hardening Measures for Exposed Cloud Run Services

Mandiant explains how vulnerabilities in publicly accessible serverless functions can expose files, enable command execution, and put cloud resources at risk, then recommends layered controls to reduce impact.

Jul 15, 2026
Detection & Defense · bleepingcomputer.com

How to Validate Exploitability Without Running a Live Exploit

In a sponsored article, Picus advocates testing exploitability by emulating attacker behaviors against deployed controls. A Nightmare-Eclipse example shows how defenders could test privilege escalation, credential access and Defender tampering without running the real 😅

Jul 14, 2026
Detection & Defense · cisa.gov

Joint Advisory Urges Router Hardening Against Russian FSB Center 16 Activity

A multinational advisory says Russian FSB Center 16 actors target exposed, poorly configured routers using SNMP and, at times, Cisco vulnerabilities. It urges SNMPv3, restricted management access, disabling Smart Install, and patching.

Jul 14, 2026
Detection & Defense · aikido.dev

Checklist Outlines Defenses Against Software Supply-Chain Attacks

A practical checklist recommends defenses against software supply-chain attacks, including package-age policies, pinned CI dependencies, scoped agent permissions, prompt-injection safeguards, and audit logging.

Jul 14, 2026
Detection & Defense · huntress.com

Huntress Highlights Five Identity-Based Threat Patterns for Defenders to Watch

Huntress outlines five common threat patterns, from stolen-credential ransomware and mailbox compromise to ClickFix lures, and explains how defenders can spot them by correlating identity, device, and network signals.

Jul 14, 2026
Detection & Defense · team-cymru.com

Four Steps to Improve Windows Logging for Incident Response

The article recommends expanding Windows Security log capacity, maintaining Sysmon, enabling Volume Shadow Copies, and correctly sizing the USN Journal to preserve forensic evidence. It also advises human verification when using AI in DFIR workflows.

Jul 14, 2026
Detection & Defense · aikido.dev

How Dependency Firewalls Block Malicious Packages

The article explains how install-time dependency firewalls can block malicious packages and outlines checks for malware, suspicious releases, typosquats and risky install scripts. It also promotes Aikido's tools and reports its package-analysis figures.

Jul 13, 2026
Detection & Defense · huntress.com

How to Build a Risk-Based Patch Management Strategy

A practical guide to patch management recommends maintaining an asset inventory, prioritizing updates by risk, testing and deploying patches in phases, verifying remediation, and tracking program health.

Jul 13, 2026
Detection & Defense · huntress.com

System Hardening Checklist Covers Access, Network, Logging, and Platform Controls

A practical guide to reducing attack surface through system hardening, covering access controls, network and firewall settings, patching, Windows and Linux configurations, logging, physical security, and ongoing audits.

Jul 10, 2026
Detection & Defense · wiz.io

How Wiz’s Product Security Team Uses Cloud Security Controls and Detection

Wiz describes how its Product Security team uses the platform for CI/CD scanning, cloud configuration guardrails, custom threat detection, alert triage, threat modeling, and security testing.

Jul 9, 2026
Detection & Defense · huntress.com

Huntress Details Conditional Access Gaps Behind Railway and LSHIY Microsoft 365 Attacks

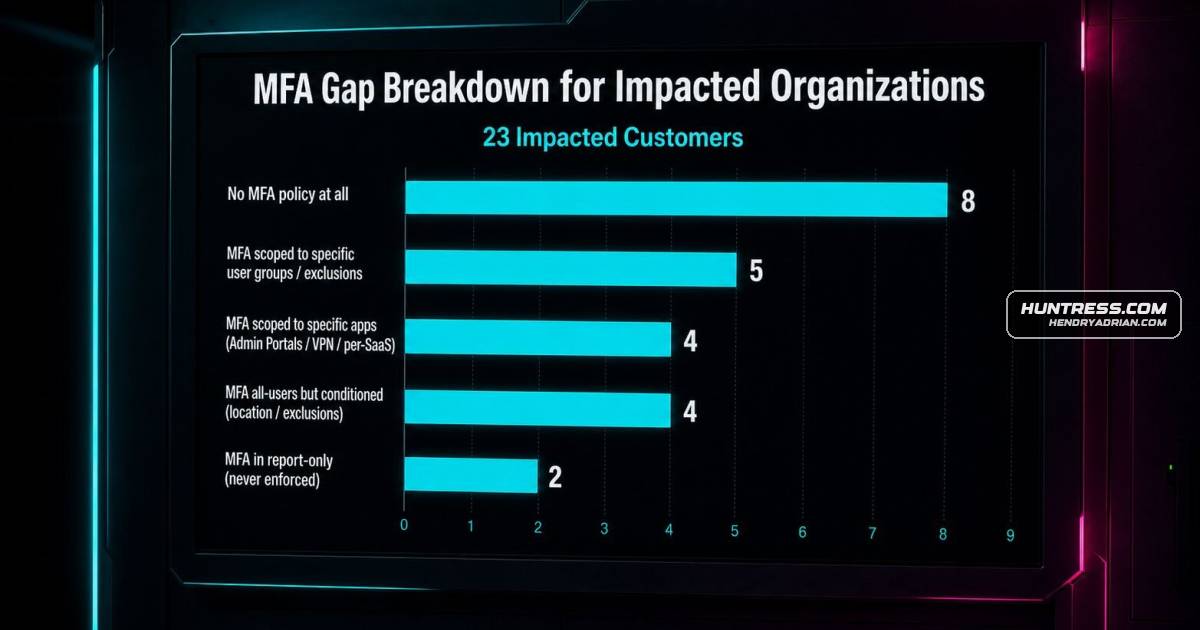
Huntress links two Microsoft 365 campaigns to Conditional Access gaps: device-code phishing using Railway[.]com infrastructure and ROPC password spraying via Azure CLI. It recommends blocking device code flow and applying MFA policies across users, cloud apps, and auth.

Jul 9, 2026
Detection & Defense · bleepingcomputer.com

How AI Strengthens Service Desk Impersonation—and Ways to Prevent It

A sponsored Specops article explains how AI can make service-desk impersonation, reconnaissance and social-engineering campaigns more convincing and scalable. It recommends secure credential enrollment, biometric liveness checks and identity verification before high-st4

Jul 8, 2026
PreviousPage 14 of 26 Next
© 2026 cyber.hendryadrian.com