cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · thecyberexpress.com

MediaTek Android Boot-Chain Flaw Could Expose Encryption Keys and Wallet Seeds

Ledger researchers demonstrated that brief USB access could exploit a boot-chain flaw in some MediaTek Android devices using Trustonic TEE to recover PINs and wallet seeds. MediaTek sent a firmware fix to OEMs; device updates are still needed.
Mar 12, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited n8n RCE Flaw to KEV Catalog

CISA added n8n flaw CVE-2025-68613 to its KEV catalog based on evidence of active exploitation. Patches were released in December 2025, but Shadowserver reported over 24,700 exposed unpatched instances.

Mar 12, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited n8n RCE Flaw

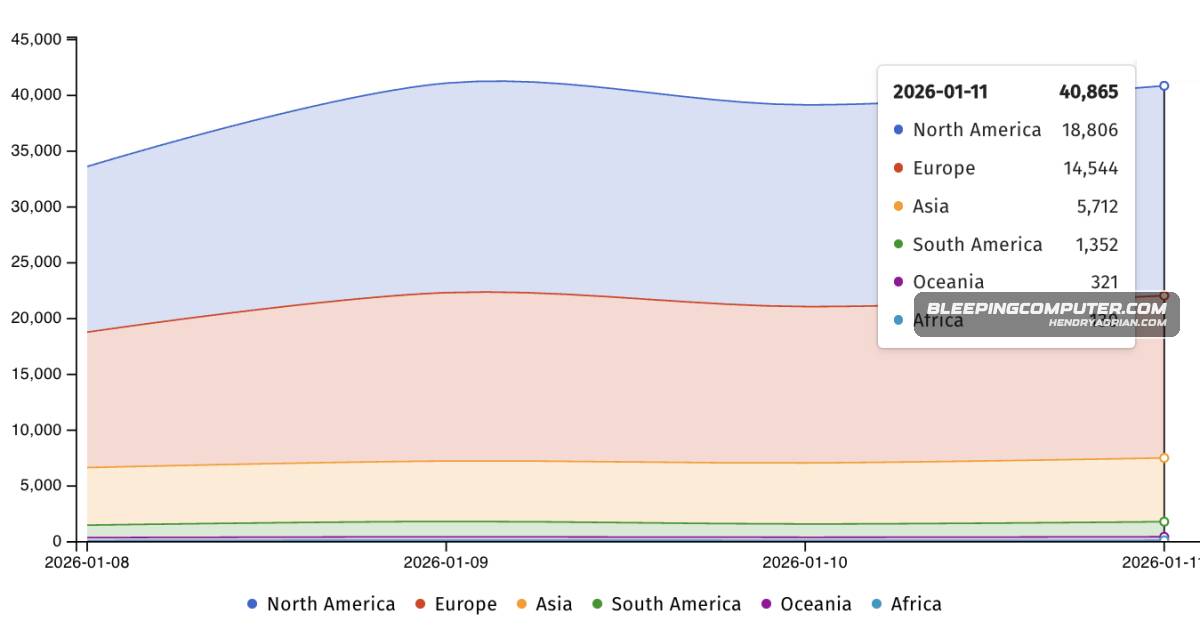
CISA added n8n flaw CVE-2025-68613 to its KEV catalog and ordered U.S. federal agencies to patch by March 25. The n8n team fixed the authenticated RCE in v1.122.0; Shadowserver reports over 40,000 unpatched instances exposed online.

Mar 11, 2026
Vulnerability & Exploit · bleepingcomputer.com

Elementor Ally SQL Injection Flaw Leaves Over 250,000 Sites Vulnerable

CVE-2026-2313 allows unauthenticated, time-based blind SQL injection in Elementor’s Ally WordPress plugin under specific conditions. Elementor fixed it in Ally 4.1.0, but over 250,000 sites reportedly remain vulnerable.

Mar 11, 2026
Vulnerability & Exploit · thehackernews.com

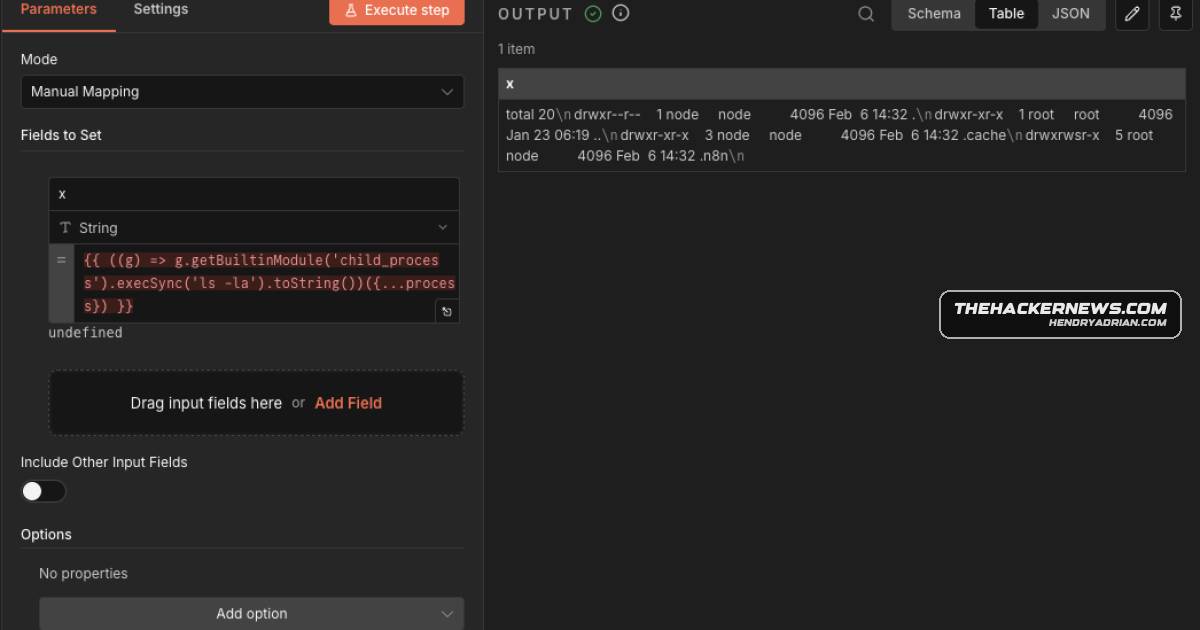
Critical n8n Flaws Could Enable Remote Code Execution and Credential Exposure

Researchers disclosed four critical n8n flaws, including unauthenticated expression injection and sandbox escapes that could enable remote code execution and expose stored credentials. Fixes are available; temporary mitigations include restricting workflow permissions.

Mar 11, 2026
Vulnerability & Exploit · therecord.media

CISA Shortens Patch Deadlines for SolarWinds and Ivanti Vulnerabilities

CISA set an immediate patch deadline for SolarWinds Web Help Desk flaw CVE-2025-26399 and two-week deadlines for two other vulnerabilities, including Ivanti’s CVE-2026-1603. Exploitation and nation-state targeting have been reported.

Mar 11, 2026
Vulnerability & Exploit · bleepingcomputer.com

‘Zombie ZIP’ Technique Can Evade Antivirus Scanning by Manipulating Archive Headers

Researcher Chris Aziz says Zombie ZIP marks DEFLATE-compressed data as STORED, leading scanners to inspect compressed bytes; his PoC reportedly bypassed 50 of 51 VirusTotal engines. CERT/CC assigned CVE-2026-0866 and recommends validating archive headers.

Mar 10, 2026
Vulnerability & Exploit · securityweek.com

SAP Patches Critical FS-QUO and NetWeaver Vulnerabilities

SAP released 15 security notes for March 2026, including fixes for critical deserialization flaws in FS-QUO and NetWeaver and a high-severity Supply Chain Management DoS vulnerability. SAP did not report in-the-wild exploitation.

Mar 10, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Says Patched Ivanti EPM Flaw Is Actively Exploited

CISA added CVE-2026-1603, an unauthenticated Ivanti Endpoint Manager flaw, to its KEV catalog as actively exploited and ordered federal agencies to patch by March 23. Ivanti says it knew of no customer exploitation before disclosure; EPM 2024 SU5 fixes the flaw.

Mar 10, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Three SolarWinds, Workspace ONE and Ivanti Flaws to KEV Catalog

CISA added three flaws affecting SolarWinds Web Help Desk, Workspace ONE UEM and Ivanti Endpoint Manager to its KEV catalog. The article reports active exploitation but says Ivanti exploitation details are unavailable and its bulletin is not updated.

Mar 10, 2026
Vulnerability & Exploit · thecyberexpress.com

Nginx UI Flaw Exposes Server Backups and Decryption Keys

CVE-2026-27944 lets unauthenticated users download Nginx UI backups and obtain the AES key and IV in the same response, potentially exposing credentials, configuration, session tokens, and private SSL keys. Version 2.3.3 contains a fix.

Mar 9, 2026
Vulnerability & Exploit · securityaffairs.com

Nginx UI Flaw CVE-2026-27944 Exposes Server Backup Keys

An advisory reports that Nginx UI’s unauthenticated /api/backup endpoint exposes the AES-256 key and IV in a response header, letting attackers download and decrypt backups containing sensitive data.

Mar 9, 2026
Vulnerability & Exploit · securityweek.com

Cisco Warns of Active Exploitation of Two Catalyst SD-WAN Flaws

Cisco says two patched Catalyst SD-WAN flaws, CVE-2026-20128 and CVE-2026-20122, are being exploited. It has not shared attack details; the advisory suggests the flaws may be chained with others.

Mar 5, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Warns Two More SD-WAN Flaws Are Actively Exploited

Cisco says attackers are actively exploiting two Catalyst SD-WAN Manager flaws: an arbitrary file overwrite requiring read-only API credentials and an information disclosure requiring local vManage credentials. Cisco urges customers to upgrade.

Mar 5, 2026
Vulnerability & Exploit · bleepingcomputer.com

Hackers Exploit WordPress Membership Plugin Flaw to Create Admin Accounts

Hackers are exploiting critical flaw CVE-2026-1492 in the User Registration & Membership WordPress plugin to create admin accounts without authentication. Version 5.1.3 fixes the flaw; admins should update or disable the plugin.

Mar 5, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco patches two maximum-severity Secure FMC flaws enabling root access

Cisco patched two remotely exploitable Secure FMC flaws that could let unauthenticated attackers gain root access or run arbitrary code. Cisco PSIRT reports no evidence of active exploitation or public PoC code.

Mar 4, 2026
Vulnerability & Exploit · bleepingcomputer.com

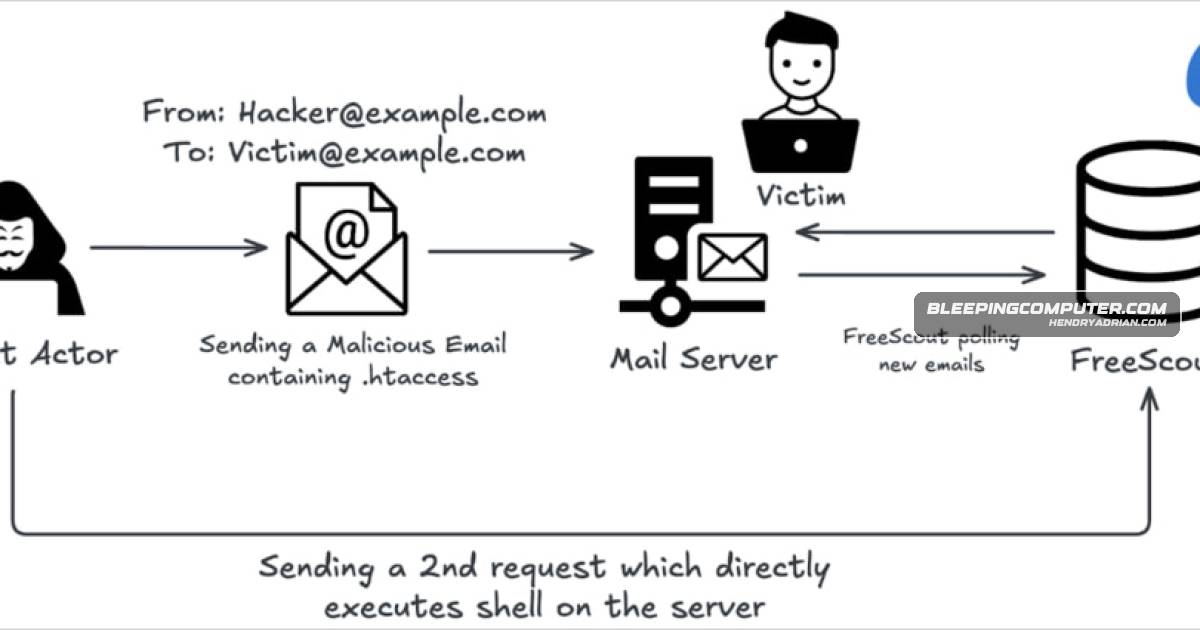
FreeScout Flaw Enables Zero-Click Remote Code Execution via Email Attachment

CVE-2026-28289 lets unauthenticated attackers exploit FreeScout via a crafted email attachment, bypassing an earlier fix with a zero-width space. Versions through 1.8.206 are affected; upgrade to 1.8.207.

Mar 4, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Adds VMware Aria Operations RCE Flaw to KEV Catalog Amid Unverified Exploitation Reports

CISA added VMware Aria Operations flaw CVE-2026-22719 to its KEV catalog. Broadcom says it cannot independently verify exploitation reports; patches and a temporary workaround are available.

Mar 4, 2026
Vulnerability & Exploit · securityweek.com

Researcher and Honeywell Dispute Impact of IQ4 Controller Vulnerability

Researcher Gjoko Krstic says Honeywell IQ4 controllers may expose an unauthenticated HMI and allow early administrator-account creation. Honeywell disputes the risk; SecurityWeek confirmed many interfaces are internet-exposed but not the other claims.

Mar 3, 2026
Vulnerability & Exploit · bleepingcomputer.com

Google Patches Android Zero-Day Reportedly Exploited in Targeted Attacks

Google's March 2026 Android updates address 129 vulnerabilities, including CVE-2026-21385, which Google says may be under limited, targeted exploitation. Qualcomm describes an integer overflow affecting 235 chipsets.

Mar 3, 2026
Vulnerability & Exploit · securityweek.com

MS-Agent Vulnerability CVE-2026-2256 Allows Arbitrary Command Execution

CVE-2026-2256 lets crafted content consumed by ModelScope MS-Agent bypass Shell tool checks and trigger arbitrary commands with the agent process’s privileges. The flaw was found in version 1.5.2; recommended mitigations include sandboxing and least privilege.

Mar 3, 2026
Vulnerability & Exploit · thehackernews.com

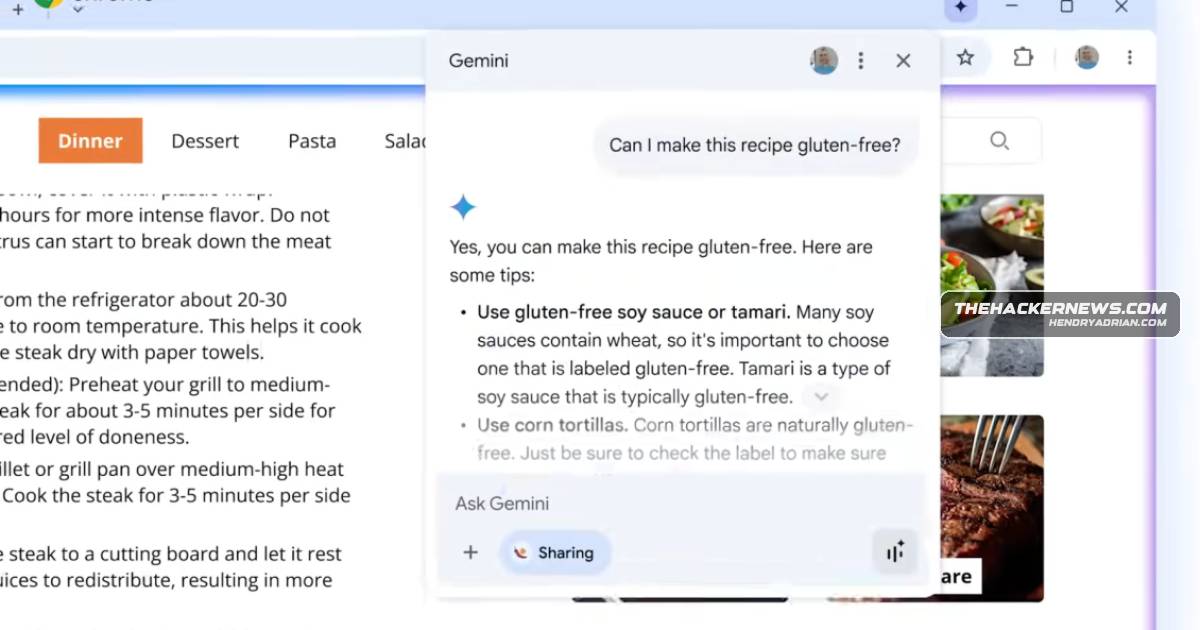
Chrome Flaw Could Let Malicious Extensions Hijack Gemini Side Panel

CVE-2026-0628 (Glic Jack) allowed malicious Chrome extensions to inject code into the Gemini side panel, potentially accessing sensitive device capabilities and local files. Google patched the flaw in Chrome 143 in January 2026.

Mar 3, 2026
Vulnerability & Exploit · securityweek.com

Chrome Flaw Could Have Let Extensions Hijack Gemini Live AI Assistant

Palo Alto Networks says CVE-2026-0628 could have let malicious Chrome extensions inject JavaScript into Gemini Live and access privileged capabilities. Google patched the flaw in Chrome 143.

Mar 2, 2026
Vulnerability & Exploit · securityweek.com

OpenClaw Flaw Could Let Malicious Websites Hijack AI Agents

Oasis Security reported that malicious websites could exploit OpenClaw’s localhost gateway to guess passwords and gain agent administrator access. OpenClaw fixed the high-severity flaw; users should update to version 2026.2.25 or later.

Mar 2, 2026
PreviousPage 60 of 65 Next
© 2026 cyber.hendryadrian.com