cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · thehackernews.com

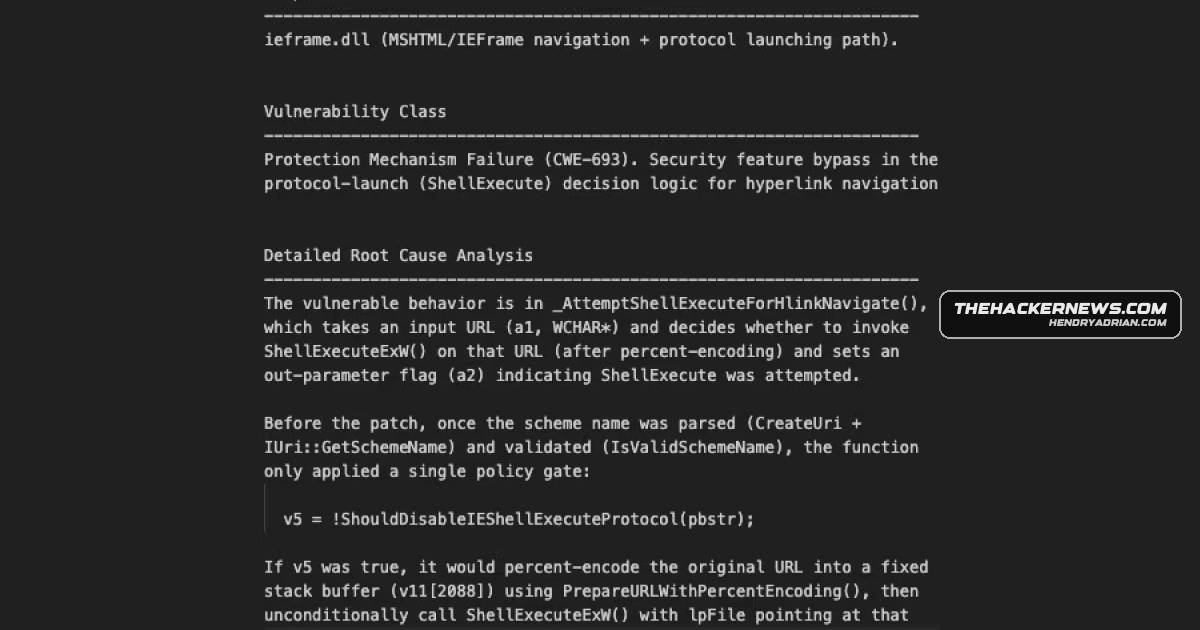
Akamai Links APT28 Activity to Exploitation of Patched MSHTML Zero-Day

Microsoft patched CVE-2026-21513 in February 2026 and said it was exploited as a zero-day. Akamai linked a VirusTotal sample and wellnesscaremed[.]com infrastructure to APT28, describing crafted LNK/HTML files that bypass browser protections.

Mar 2, 2026
Vulnerability & Exploit · bleepingcomputer.com

ClawJacked Flaw Let Malicious Websites Hijack OpenClaw

Oasis Security reported that ClawJacked let malicious websites brute-force OpenClaw’s localhost gateway and gain admin access. OpenClaw fixed the flaw in version 2026.2.26; users should update.

Mar 2, 2026
Vulnerability & Exploit · thehackernews.com

ClawJacked Flaw Could Let Malicious Sites Take Over Local OpenClaw AI Agents

OpenClaw patched ClawJacked in version 2026.2.25. Oasis Security said malicious websites could exploit the local gateway’s password and device-registration weaknesses to gain control of an agent. The article also details malicious skills and recommends updates and safer

Mar 1, 2026
Vulnerability & Exploit · bleepingcomputer.com

Trend Micro patches two critical Apex One RCE flaws

Trend Micro patched CVE-2025-71210 and CVE-2025-71211, path traversal flaws that can enable remote code execution in Apex One. Exploitation requires access to the management console; fixes are available in SaaS updates and Critical Patch Build 14136.

Feb 27, 2026
Vulnerability & Exploit · thecyberexpress.com

Talos Says UAT-8616 Exploited Cisco SD-WAN Zero-Day Since 2023

Cisco Talos says UAT-8616 exploited CVE-2026-20127 in Catalyst SD-WAN since at least 2023, gaining administrative access and adding rogue peers. Partners say attackers likely chained CVE-2022-20775 for root access; Cisco issued patches.

Feb 26, 2026
Vulnerability & Exploit · securityweek.com

Claude Code Flaws Could Let Malicious Repositories Run Commands and Steal API Keys

Check Point researchers found Claude Code configuration flaws that could trigger commands without approval, bypass MCP consent, and redirect API traffic to steal keys. Anthropic patched the issues and added warnings and confirmations.

Feb 26, 2026
Vulnerability & Exploit · bleepingcomputer.com

Zyxel Patches Critical UPnP Command-Injection Flaw Enabling Remote Code Execution

Zyxel patched a critical UPnP flaw that can enable unauthenticated remote command execution on affected devices when both UPnP and WAN access are enabled. It also patched two post-authentication flaws and recommends replacing certain end-of-life routers.

Feb 25, 2026
Vulnerability & Exploit · securityweek.com

Broadcom Patches Three VMware Aria Operations Vulnerabilities

Broadcom patched three VMware Aria Operations flaws: an unauthenticated command-injection vulnerability that could lead to remote code execution, stored XSS, and privilege escalation. The advisory does not mention in-the-wild exploitation.

Feb 24, 2026
Vulnerability & Exploit · bleepingcomputer.com

SolarWinds Patches Four Critical Serv-U Flaws Enabling Root-Level Code Execution

SolarWinds patched four critical Serv-U flaws in version 15.5.4 that could enable root or admin-level code execution. All require existing high privileges; the article also notes historical targeting and differing estimates of exposed servers.

Feb 24, 2026
Vulnerability & Exploit · securityweek.com

TeamT5 Says CVE-2024-7694 Was Likely Exploited in Targeted Attack

TeamT5 says CVE-2024-7694, a flaw in its ThreatSonar product, was exploited in targeted attacks in 2024 against a few customers. The firm attributes the activity likely to Chinese APTs Slime57 and Slime62; the flaw was fixed in August 2024.

Feb 24, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Flags Two Roundcube Flaws as Exploited and Orders Federal Agencies to Patch

CISA added two Roundcube flaws to its KEV catalog and ordered U.S. federal agencies to patch by March 13. The article reports prior exploitation of CVE-2025-49113 but says CISA provided no details on attacks using either flaw.

Feb 23, 2026
Vulnerability & Exploit · securityweek.com

Grandstream GXP1600 Vulnerability Could Enable Call Interception

Rapid7 reported that CVE-2026-2329, a stack-based buffer overflow in Grandstream GXP1600 phones, could let unauthenticated attackers gain root access and intercept calls. Firmware 1.0.7.81 patches the flaw.

Feb 21, 2026
Vulnerability & Exploit · cisa.gov

CISA Warns of Four Critical Vulnerabilities in USR-W610 Routers

CISA says four vulnerabilities affect Jinan USR IOT PUSR USR-W610 firmware versions up to 3.1.1.0, potentially enabling authentication bypass, credential exposure, or denial of service. CISA reports no known public exploitation.

Feb 21, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Two Actively Exploited Roundcube Flaws to KEV Catalog

CISA added two Roundcube vulnerabilities to its KEV catalog, citing evidence of active exploitation. A researcher said CVE-2025-49113 was weaponized within 48 hours of disclosure; FCEB agencies must remediate both flaws by March 13, 2026.

Feb 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Flags BeyondTrust RCE Flaw as Used in Ransomware Campaigns

CISA added BeyondTrust CVE-2026-1731 to its KEV catalog and flagged its use in ransomware campaigns. The pre-authentication RCE was exploited in the wild; SaaS instances were patched automatically, while self-hosted users must update.

Feb 21, 2026
Vulnerability & Exploit · cisa.gov

CISA Warns of Missing-Authentication Flaw in Welker OdorEyes System

CISA says CVE-2026-24790 affects all versions of Welker’s OdorEyes EcoSystem Pulse Bypass System with XL4 Controller. The CVSS 8.2 flaw could cause over- or under-odorization; no public exploitation has been reported.

Feb 20, 2026
Vulnerability & Exploit · securityweek.com

CISA Flags BeyondTrust CVE-2026-1731 for Ransomware Exploitation

CISA updated its KEV entry for critical BeyondTrust CVE-2026-1731 to flag use in ransomware campaigns. No specific ransomware groups have been publicly linked; Palo Alto reported broader exploitation but did not identify ransomware activity.

Feb 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited Dell RecoverPoint Flaw

CISA ordered federal agencies to remediate Dell RecoverPoint flaw CVE-2026-22769 by Feb. 21. Mandiant and Google TAG say it has been exploited since at least mid-2024 by suspected UNC6201, which deployed GRIMBOLT and other malware.

Feb 19, 2026
Vulnerability & Exploit · bleepingcomputer.com

Grandstream VoIP Flaw Enables Unauthenticated Root Access and Call Eavesdropping

Rapid7 reports that CVE-2026-2329 lets unauthenticated attackers exploit a stack overflow in affected Grandstream GXP1600 phones for root access and call eavesdropping. Grandstream fixed the flaw in firmware 1.0.7.81.

Feb 19, 2026
Vulnerability & Exploit · thecyberexpress.com

Researchers Find Critical Flaws in Four VS Code Extensions With 128M+ Installs

OX Security researchers reported vulnerabilities in four VS Code extensions with more than 128 million combined installations, warning of potential code execution, file exfiltration, and lateral movement. Microsoft Live Preview's issue was fixed in version 0.4.16.

Feb 19, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Warns of Critical Account-Takeover Flaw in Honeywell CCTV Cameras

CISA warns that CVE-2026-1670 lets unauthenticated attackers change recovery emails and take over accounts on several Honeywell CCTV models. No public exploitation was known as of February 17; users should limit network exposure and contact Honeywell for patch guidance.

Feb 18, 2026
Vulnerability & Exploit · thehackernews.com

Flaws in Four VS Code Extensions Could Expose Local Files or Enable Code Execution

Researchers disclosed flaws in four VS Code extensions with over 125 million combined installs. Three vulnerabilities remain unpatched; Microsoft Live Preview’s flaw was fixed in version 0.4.16.

Feb 18, 2026
Vulnerability & Exploit · thehackernews.com

Grandstream GXP1600 VoIP Phones Affected by Unauthenticated Root RCE Flaw

Rapid7 disclosed CVE-2026-2329, an unauthenticated stack overflow in Grandstream GXP1600-series phones that can enable root RCE. A Metasploit module demonstrates credential extraction and SIP-proxy call interception; firmware 1.0.7.81 fixes it.

Feb 18, 2026
Vulnerability & Exploit · therecord.media

CISA Orders Federal Agencies to Patch Actively Exploited Dell RecoverPoint Flaw

CISA confirmed active exploitation of critical Dell RecoverPoint for Virtual Machines flaw CVE-2026-22769 and ordered federal agencies to patch by Saturday. Google and Mandiant attribute activity to UNC6201 and report BRICKSTORM and GRIMBOLT backdoors.

Feb 18, 2026
PreviousPage 61 of 65 Next
© 2026 cyber.hendryadrian.com