
CISA Orders Federal Agencies to Patch Actively Exploited n8n RCE Flaw
Summary
CISA added n8n flaw CVE-2025-68613 to its KEV catalog and ordered U.S. federal agencies to patch by March 25. The n8n team fixed the authenticated RCE in v1.122.0; Shadowserver reports over 40,000 unpatched instances exposed online.
Key points
- CVE-2025-68613 allows authenticated attackers to execute code with the privileges of the n8n process.
- CISA added the flaw to its Known Exploited Vulnerabilities catalog and ordered Federal Civilian Executive Branch agencies to patch by March 25 under BOD 22-01.
- The n8n team fixed the vulnerability in version 1.122.0.
- For administrators unable to upgrade immediately, the n8n team advises limiting workflow creation and editing to trusted users and restricting operating-system privileges and network access.
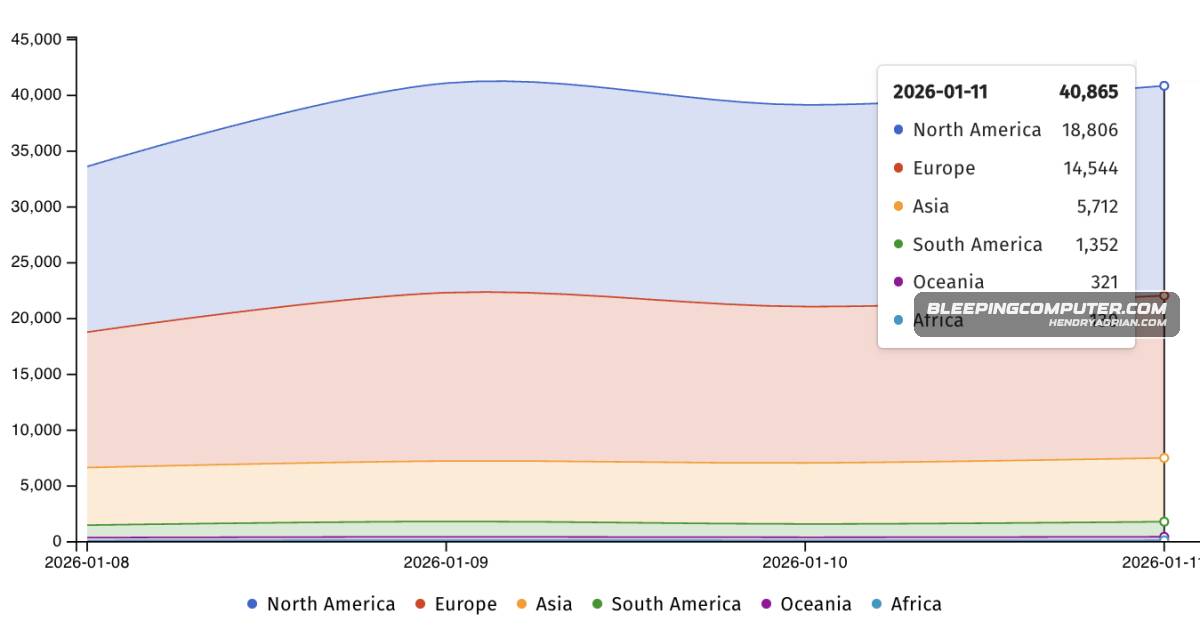
- Shadowserver reports more than 40,000 unpatched n8n instances exposed online, including over 18,000 IPs in North America and over 14,000 in Europe.
- CISA encouraged all network defenders to secure systems against ongoing attacks exploiting the flaw.
Article Details
- Vulnerability Types
- Remote code execution (RCE)
- Improper control of dynamically managed code resources in workflow expression evaluation
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Limit workflow creation and editing permissions to fully trusted users.
- Restrict operating system privileges and network access.