
Critical n8n Flaws Could Enable Remote Code Execution and Credential Exposure
Summary
Researchers disclosed four critical n8n flaws, including unauthenticated expression injection and sandbox escapes that could enable remote code execution and expose stored credentials. Fixes are available; temporary mitigations include restricting workflow permissions.
Key points
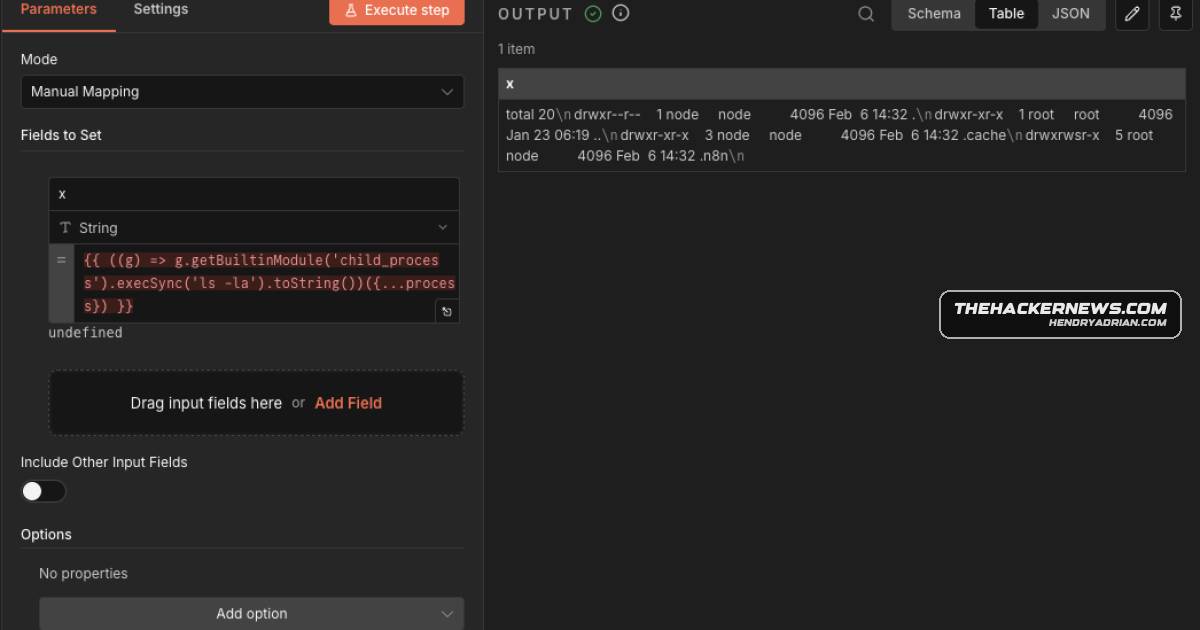
- CVE-2026-27577 is an expression-compiler sandbox escape that could let an authenticated user with workflow permissions execute system commands.
- CVE-2026-27493 allows unauthenticated expression evaluation through public Form nodes; crafted input in a form field could lead to command execution when chained with a sandbox escape.
- Pillar Security said exploitation could expose the N8N_ENCRYPTION_KEY, potentially enabling decryption of credentials stored in n8n’s database.
- The same releases also fix CVE-2026-27495, involving JavaScript Task Runner sandbox code injection, and CVE-2026-27497, involving code execution and arbitrary file writes through the Merge node’s SQL mode.
- The fixes are in n8n versions 2.10.1, 2.9.3, and 1.123.22.
- Until patched, n8n recommends limiting workflow editing to trusted users and disabling affected nodes; it notes workarounds do not fully remediate the risk.
Article Details
- Vulnerability Types
- Expression sandbox escape
- Unauthenticated expression evaluation
- Code injection
- SQL query mode code execution
- Severity
- Critical; CVSS 9.4 for CVE-2026-27577, 9.5 for CVE-2026-27493, and 9.4 each for CVE-2026-27495 and CVE-2026-27497.
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Limit workflow creation and editing permissions to fully trusted users.
- Disable the Form node by adding n8n-nodes-base.form to NODES_EXCLUDE.
- Disable the Form Trigger node by adding n8n-nodes-base.formTrigger to NODES_EXCLUDE.
- Use external runner mode (N8N_RUNNERS_MODE=external) for CVE-2026-27495.
- Disable the Merge node by adding n8n-nodes-base.merge to NODES_EXCLUDE.
- Deploy in a hardened environment with restricted operating-system privileges and network access.
MITRE ATT&CK
T1059 · Command and Scripting InterpreterThe flaws can be used to execute arbitrary shell commands or other code on the host running n8n.T1059.007 · JavaScriptCVE-2026-27495 involves code injection in the JavaScript Task Runner sandbox to execute code outside the sandbox.T1190 · Exploit Public-Facing ApplicationCVE-2026-27493 allows unauthenticated expression evaluation through public n8n Form endpoints.
CVE
CVE-2026-27493n8n-io · n8nTwo critical bugs—CVE-2026-27577 (sandbox escape leading to RCE) and CVE-2026-27493 (unauthenticated expression evaluation via Form nodes)—were disclosed and patched.CVE-2026-27495n8n-io · n8nn8n fixed these issues in releases 2.10.1, 2.9.3, and 1.123.22 and also addressed related critical flaws CVE-2026-27495 and CVE-2026-27497.CVE-2026-27497n8n-io · n8nn8n fixed these issues in releases 2.10.1, 2.9.3, and 1.123.22 and also addressed related critical flaws CVE-2026-27495 and CVE-2026-27497.CVE-2026-27577n8n-io · n8nTwo critical bugs—CVE-2026-27577 (sandbox escape leading to RCE) and CVE-2026-27493 (unauthenticated expression evaluation via Form nodes)—were disclosed and patched.