
Chrome Flaw Could Let Malicious Extensions Hijack Gemini Side Panel
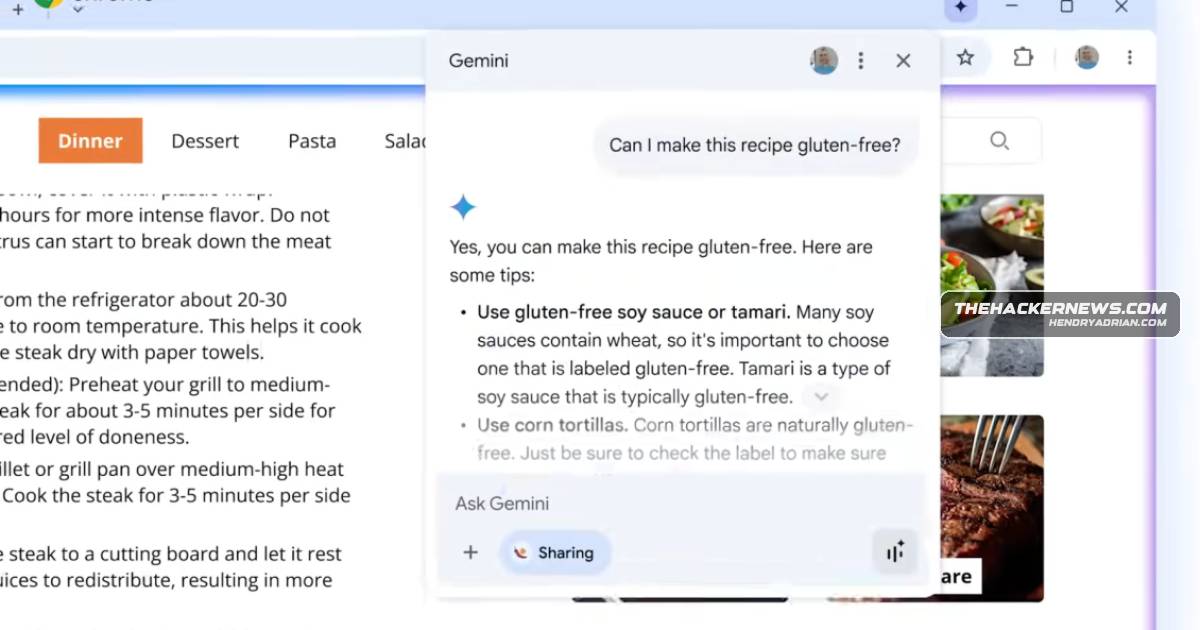
Summary
CVE-2026-0628 (Glic Jack) allowed malicious Chrome extensions to inject code into the Gemini side panel, potentially accessing sensitive device capabilities and local files. Google patched the flaw in Chrome 143 in January 2026.
Key points
- CVE-2026-0628 was an insufficient policy enforcement flaw involving Chrome’s WebView-based Gemini Live side panel.
- A malicious extension using the declarativeNetRequest API could inject JavaScript into the panel and run code at gemini.google[.]com/app.
- Successful exploitation could enable access to local files, screenshots, the camera, and microphone.
- Palo Alto Networks Unit 42 researcher Gal Weizman reported the flaw on November 23, 2025.
- Google patched the vulnerability in Chrome 143.0.7499.192/.193 for Windows and Mac and 143.0.7499.192 for Linux in early January 2026.
Article Details
- Vulnerability Types
- Insufficient policy enforcement in the WebView tag
- Privilege escalation
- Severity
- High (CVSS 8.8)
- Affected Versions
- Google Chrome versions prior to 143.0.7499.192
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
T1005 · Data from Local SystemSuccessful exploitation could allow access to local files on the victim's system.T1059.007 · JavaScriptThe extension could inject JavaScript into the privileged Gemini panel and execute arbitrary code at the Gemini app.T1068 · Exploitation for Privilege EscalationExploitation of CVE-2026-0628 could allow a malicious extension to escalate privileges through the Chrome WebView-based Gemini panel.T1113 · Screen CaptureSuccessful exploitation could enable the attacker to take screenshots of websites.T1123 · Audio CaptureSuccessful exploitation could provide access to the victim's microphone.T1125 · Video CaptureSuccessful exploitation could provide access to the victim's camera.T1176 · Software ExtensionsA specially crafted malicious Chrome extension using declarativeNetRequest could inject JavaScript into the Gemini side panel.
CVE
People
Vendors
Products
Gemini Liveresearchers disclosed a now-patched Chrome vulnerability (CVE-2026-0628) in the WebView-based Gemini Live side panel that could let malicious extensions escalate privileges and access local files, camera, andGoogle ChromeCybersecurity researchers disclosed a now-patched Chrome vulnerability (CVE-2026-0628) in the WebView-based Gemini Live side panel that could let malicious extensions escalate privileges and access local files, camera,