
CISA Says Patched Ivanti EPM Flaw Is Actively Exploited
Summary
CISA added CVE-2026-1603, an unauthenticated Ivanti Endpoint Manager flaw, to its KEV catalog as actively exploited and ordered federal agencies to patch by March 23. Ivanti says it knew of no customer exploitation before disclosure; EPM 2024 SU5 fixes the flaw.
Key points
- CISA added CVE-2026-1603 to its Known Exploited Vulnerabilities catalog, but provided no details about attacks.
- The flaw reportedly lets unauthenticated remote attackers bypass authentication and steal credentials through a low-complexity cross-site scripting attack requiring no user interaction.
- Ivanti EPM 2024 SU5 addresses CVE-2026-1603; the update also fixes an SQL injection flaw that could let authenticated remote attackers read database data.
- CISA ordered Federal Civilian Executive Branch agencies to patch by March 23.
- Ivanti said it was unaware of customers being exploited before public disclosure.
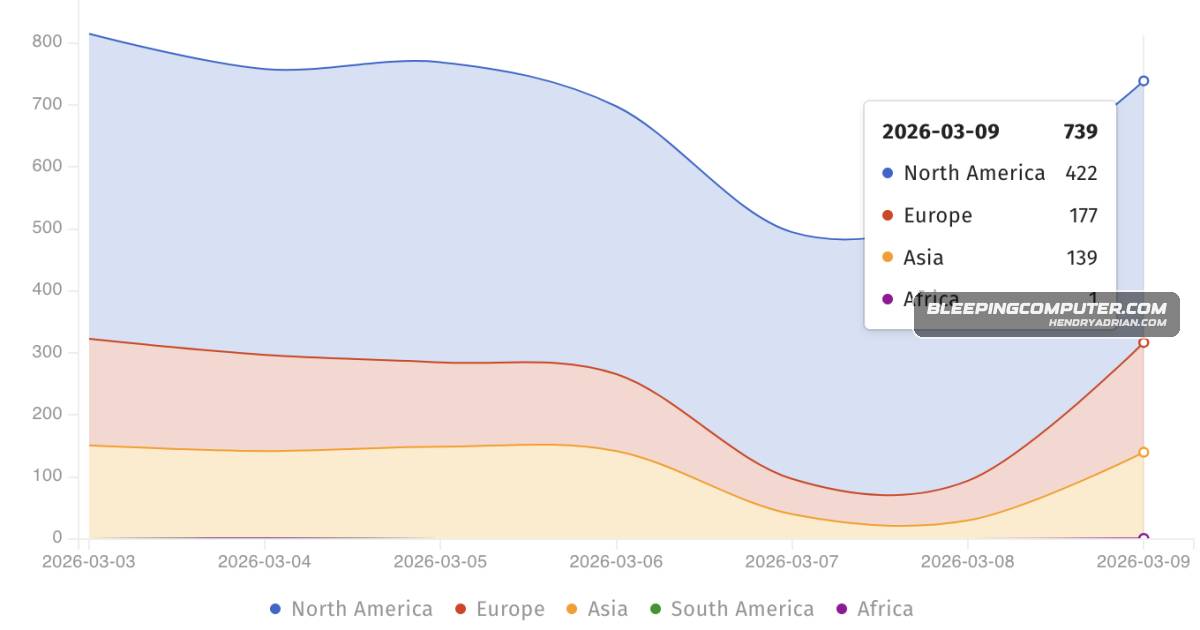
- Shadowserver tracks more than 700 internet-facing Ivanti EPM instances, but how many remain vulnerable is unknown.
Article Details
- Vulnerability Types
- Cross-site scripting (XSS) enabling authentication bypass and credential theft
- SQL injection allowing remote authenticated attackers to read arbitrary database data
- Severity
- High
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
CVE-2024-13159Ivanti · Endpoint ManagerOne year ago, CISA warned federal agencies to secure their networks against three other EPM flaws (CVE-2024-13159, CVE-2024-13160, and CVE-2024-13161) that were exploited in the wild.CVE-2024-13160Ivanti · Endpoint ManagerOne year ago, CISA warned federal agencies to secure their networks against three other EPM flaws (CVE-2024-13159, CVE-2024-13160, and CVE-2024-13161) that were exploited in the wild.CVE-2024-13161Ivanti · Endpoint ManagerOne year ago, CISA warned federal agencies to secure their networks against three other EPM flaws (CVE-2024-13159, CVE-2024-13160, and CVE-2024-13161) that were exploited in the wild.CVE-2024-29824ivanti · endpoint_manager; Ivanti · EPMgovernment agencies to patch another actively exploited EPM flaw (CVE-2024-29824) in October 2024.CVE-2026-1603Ivanti · Endpoint ManagerCISA has classified a high-severity Ivanti Endpoint Manager vulnerability (CVE-2026-1603) as actively exploited and ordered U.S.