
FreeScout Flaw Enables Zero-Click Remote Code Execution via Email Attachment
Summary
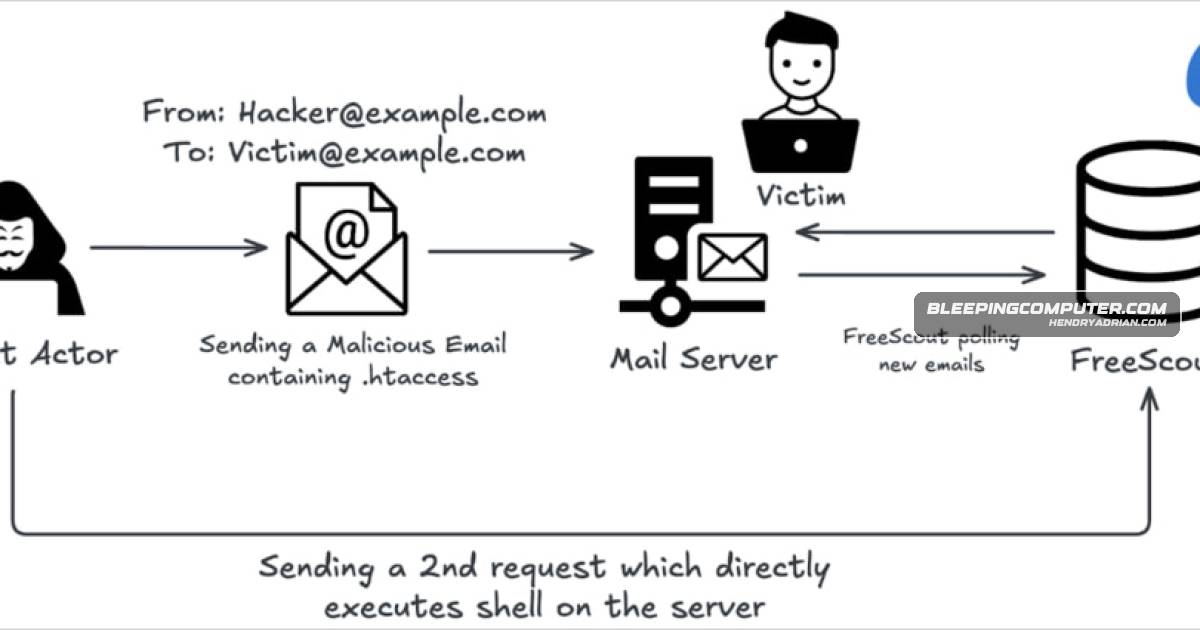
CVE-2026-28289 lets unauthenticated attackers exploit FreeScout via a crafted email attachment, bypassing an earlier fix with a zero-width space. Versions through 1.8.206 are affected; upgrade to 1.8.207.
Key points
- OX Security researchers say a crafted email attachment can trigger unauthenticated, zero-click remote code execution on a FreeScout server.
- The flaw bypasses CVE-2026-27636 by using a leading zero-width space that is later removed, allowing a dangerous dotfile to be saved.
- Attachments are stored under /storage/attachment/, where the resulting payload can be accessed and executed through the web interface.
- FreeScout versions through 1.8.206 are affected; version 1.8.207 contains the fix.
- FreeScout and OX Security advise upgrading; OX Security also recommends disabling AllowOverrideAll in Apache.
- The article reports no observed exploitation of CVE-2026-28289 in the wild at the time of writing.
Article Details
- Vulnerability Types
- Remote code execution (RCE)
- File-upload validation bypass
- Severity
- Maximum severity
- Affected Versions
- FreeScout versions up to and including 1.8.206
- Exploitation Status
- not_reported
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Disable AllowOverrideAll in the Apache configuration on the FreeScout server.
CVE
CVE-2026-27636freescout-help-desk · freescoutResearchers at OX Security say the flaw bypasses a previous fix (CVE-2026-27636) using a leading zero-width space to create executable dotfiles; administrators should upgrade to FreeScout 1.8.207 and consider disablingCVE-2026-28289freescout-help-desk · freescoutA maximum-severity remote code execution vulnerability in the FreeScout helpdesk platform (CVE-2026-28289) allows unauthenticated attackers to achieve server compromise by delivering a single crafted email attachment.
Products
Apachedotfiles; administrators should upgrade to FreeScout 1.8.207 and consider disabling AllowOverrideAll in Apache.FreeScoutA maximum-severity remote code execution vulnerability in the FreeScout helpdesk platform (CVE-2026-28289) allows unauthenticated attackers to achieve server compromise by delivering a single crafted email attachment.