cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · thehackernews.com

CISA Adds Cisco SD-WAN Authentication Bypass to KEV After Active Exploitation

CISA added CVE-2026-20182, a CVSS 10.0 authentication bypass in Cisco Catalyst SD-WAN, to KEV after active exploitation was confirmed. Cisco attributes activity with high confidence to UAT-8616; FCEB agencies must remediate by May 17, 2026.
May 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

Attackers Exploit Burst Statistics WordPress Plugin Flaw to Gain Admin Access

Attackers are exploiting CVE-2026-8181, an authentication-bypass flaw in Burst Statistics versions 3.4.0 and 3.4.1. Wordfence reports blocking more than 7,400 attacks; users should update to 3.4.2 or disable the plugin.

May 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Patches Actively Exploited Catalyst SD-WAN Authentication Bypass

Cisco says attackers exploited CVE-2026-20182, a critical authentication bypass in Catalyst SD-WAN, to gain administrative access. Cisco released fixes; CISA added the flaw to its Known Exploited Vulnerabilities Catalog.

May 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

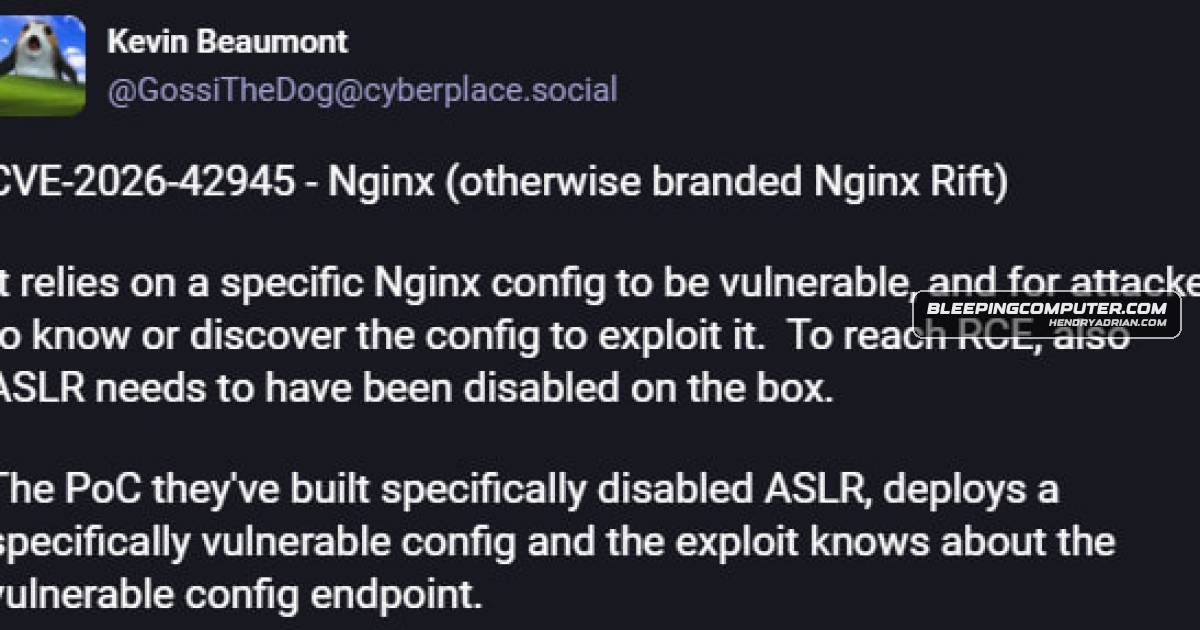
18-Year-Old NGINX Flaw Can Cause DoS, With RCE Demonstrated Under Specific Conditions

CVE-2026-42945 is a heap buffer overflow in NGINX that can reliably crash workers and may enable RCE under specific conditions. F5 released fixes; researchers say dependable RCE with ASLR enabled is not established.

May 14, 2026
Vulnerability & Exploit · securityweek.com

Fragnesia Linux Kernel Flaw Enables Local Root Privilege Escalation

Fragnesia (CVE-2026-46300) affects Linux’s XFRM ESP-in-TCP subsystem and can let a local unprivileged attacker gain root. A PoC is available, but no in-the-wild exploitation is confirmed; distributions are releasing patches.

May 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

Fragnesia Linux Kernel Flaw Enables Local Root Escalation

Fragnesia (CVE-2026-46300) is a Linux XFRM ESP-in-TCP flaw that can let unprivileged local attackers write to read-only files’ kernel page cache and gain root. A PoC is available; patches are rolling out, with module removal as a limited workaround.

May 14, 2026
Vulnerability & Exploit · securityweek.com

PraisonAI Authentication Bypass Probed Within Four Hours of Disclosure

Sysdig says a scanner probed internet-exposed PraisonAI instances within 3 hours and 44 minutes of CVE-2026-44338 disclosure. The flaw affects versions 2.5.6–4.6.33 and is fixed in 4.6.34.

May 14, 2026
Vulnerability & Exploit · securityweek.com

Broadcom Patches VMware Fusion Privilege-Escalation Flaw

Broadcom patched CVE-2026-41702, a VMware Fusion TOCTOU flaw involving a SETUID binary that could let a local non-administrator escalate privileges to root. The advisory does not report exploitation in attacks.

May 14, 2026
Vulnerability & Exploit · securityweek.com

Researcher Publishes PoCs for Two Unpatched Windows Flaws, Including BitLocker Bypass

A researcher released PoCs for two purported Windows zero-days: YellowKey reportedly bypasses BitLocker with physical access, while GreenPlasma enables privilege escalation. Researchers tested YellowKey; Microsoft says it is investigating the claims.

May 14, 2026
Vulnerability & Exploit · thehackernews.com

18-Year-Old NGINX Rewrite Flaw Could Enable Unauthenticated RCE

F5 disclosed an 18-year-old heap overflow in NGINX’s rewrite module, which crafted HTTP requests can trigger without authentication, potentially causing remote code execution or worker crashes. F5 also patched three other flaws and recommends upgrades or a configuration

May 14, 2026
Vulnerability & Exploit · huntress.com

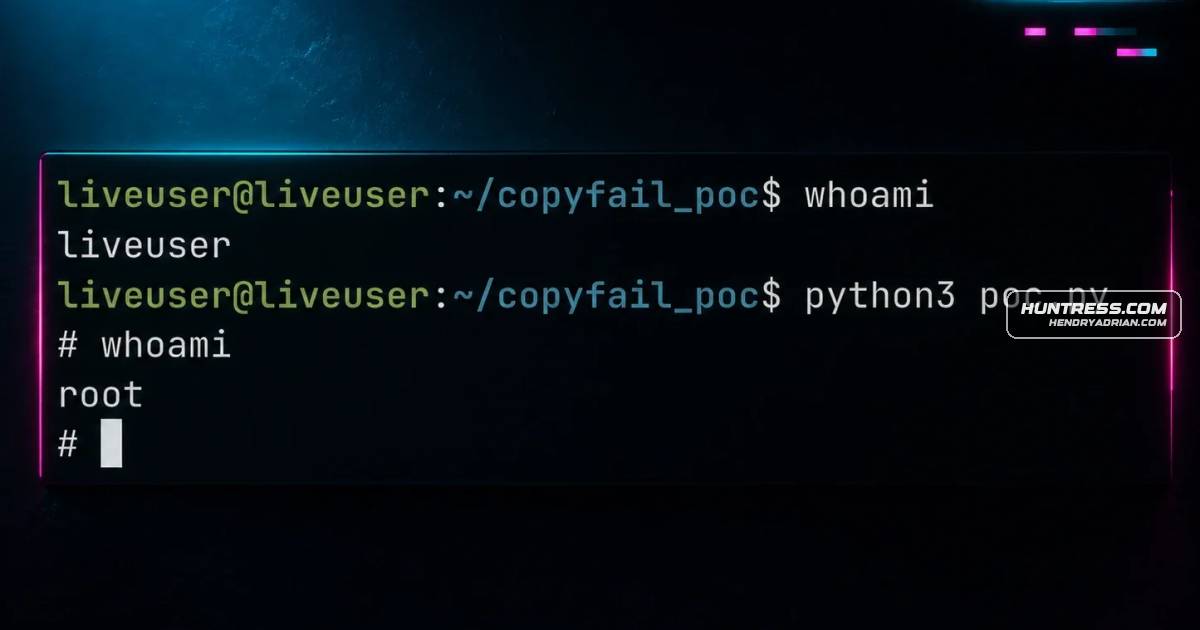
CopyFail, Dirty Frag and Fragnesia Flaws Can Give Local Linux Users Root Access

Three Linux kernel flaws let attackers with an existing foothold exploit page-cache corruption to gain root. Patching is the recommended fix; temporary module-disabling mitigations may disrupt IPsec, VPN or RxRPC workloads.

May 14, 2026
Vulnerability & Exploit · bleepingcomputer.com

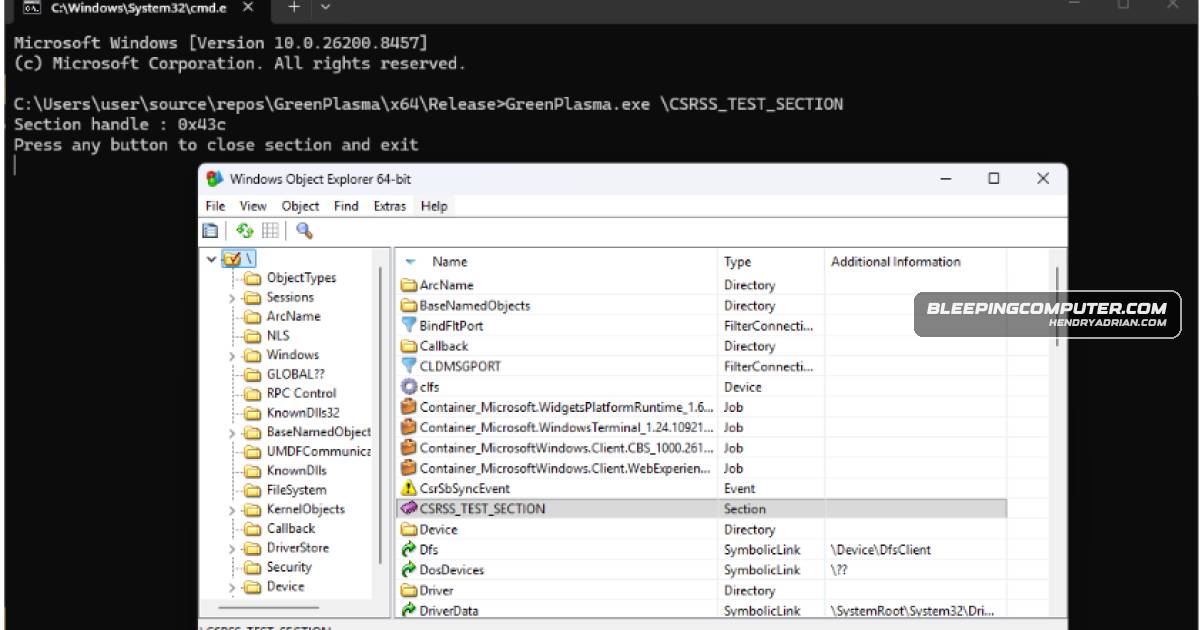
Researcher Releases PoCs for Windows BitLocker Bypass and Privilege-Escalation Flaws

Chaotic Eclipse released PoCs for YellowKey, a BitLocker bypass affecting Windows 11 and Server 2022/2025, and GreenPlasma, an incomplete privilege-escalation exploit. Researchers differ on whether YellowKey works with TPM and PIN.

May 13, 2026
Vulnerability & Exploit · bleepingcomputer.com

Critical Exim Flaw Enables Unauthenticated Remote Code Execution

CVE-2026-45185 is a use-after-free in Exim 4.97–4.99.2 builds using GnuTLS, STARTTLS and CHUNKING that may enable unauthenticated RCE via BDAT traffic. Exim 4.99.3 fixes it; OpenSSL builds are unaffected.

May 13, 2026
Vulnerability & Exploit · wiz.io

Fragnesia Linux Kernel Flaw Enables Local Privilege Escalation to Root

Fragnesia is a Linux kernel flaw in XFRM ESP-in-TCP that lets unprivileged local attackers corrupt read-only file contents in the page cache and gain root. Vendor patches are recommended; restricting unprivileged user namespaces may partially mitigate risk.

May 13, 2026
Vulnerability & Exploit · securityweek.com

Microsoft Patches CVE-2026-40361, a Critical Zero-Click Outlook Flaw

Microsoft patched CVE-2026-40361, which it describes as a critical RCE flaw affecting Word. Researcher Haifei Li says it could enable zero-click RCE via Outlook email preview; his PoC is not a working exploit.

May 13, 2026
Vulnerability & Exploit · bleepingcomputer.com

Fortinet Patches Critical RCE Flaws in FortiAuthenticator and FortiSandbox

Fortinet patched two critical flaws that could let unauthenticated attackers execute commands or code in FortiAuthenticator and FortiSandbox. FortiAuthenticator Cloud is not affected; the flaws were not reported as exploited in the wild.

May 12, 2026
Vulnerability & Exploit · thehackernews.com

Exim Fixes GnuTLS BDAT Flaw That Could Enable Code Execution

CVE-2026-45185, a use-after-free in Exim BDAT handling on GnuTLS builds, can cause heap corruption and potentially enable code execution. Versions 4.97–4.99.2 are affected; Exim 4.99.3 fixes the flaw.

May 12, 2026
Vulnerability & Exploit · bleepingcomputer.com

SAP Patches Critical Code Execution and SQL Injection Flaws in Commerce Cloud and S/4HANA

SAP’s May 2026 updates fix 15 vulnerabilities, including unauthenticated code execution in Commerce Cloud and low-complexity SQL injection in S/4HANA. SAP says it has found no evidence that the flaws were exploited in the wild.

May 12, 2026
Vulnerability & Exploit · thehackernews.com

Ollama Flaws Enable Remote Memory Disclosure and Persistent Windows Code Execution

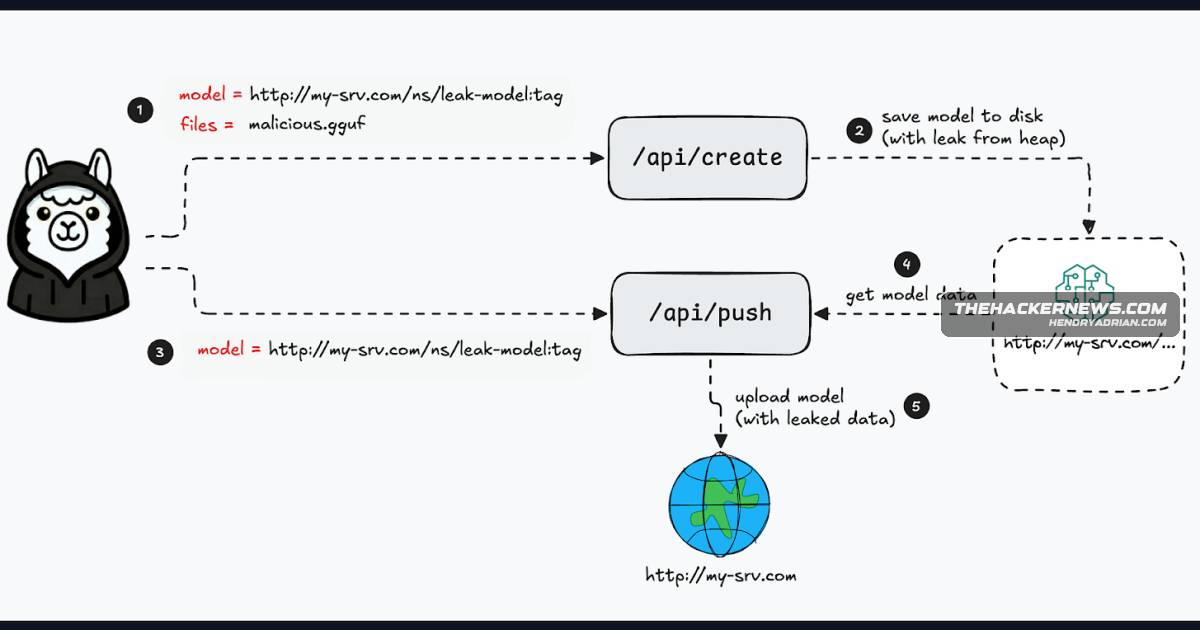
Researchers disclosed CVE-2026-7482, an Ollama GGUF-loader flaw that may expose process memory to remote attackers; two unpatched Windows updater flaws, CVE-2026-42248 and CVE-2026-42249, can enable persistent user-level code execution.

May 10, 2026
Vulnerability & Exploit · thehackernews.com

cPanel and WHM Patch Three Flaws Enabling Code Execution and Possible Privilege Escalation

cPanel and WHM patched three flaws enabling arbitrary file read, authenticated Perl code execution, and denial-of-service or possible privilege escalation. The article reports no evidence these flaws were exploited and lists fixed releases, including 110.0.114 for older

May 9, 2026
Vulnerability & Exploit · sysdig.com

Dirty Frag Linux Kernel Flaws Enable Local Privilege Escalation to Root

Dirty Frag (CVE-2026-43284 and CVE-2026-43500) lets unprivileged local users corrupt Linux page-cache data and gain root. The article details the ESP and RxRPC flaws, public PoC, detection options, and mitigations.

May 8, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Gives Federal Agencies Four Days to Patch Actively Exploited Ivanti EPMM Flaw

CISA gave U.S. federal agencies until May 10 to patch CVE-2026-6973, an actively exploited flaw enabling authenticated administrators to execute code remotely on on-prem Ivanti EPMM systems. Ivanti released fixed versions and recommends reviewing admin accounts and, ifs

May 8, 2026
Vulnerability & Exploit · cyberscoop.com

LayerX Says Claude Chrome Extension Flaw Let Other Extensions Hijack AI Agent

LayerX reported that other Chrome extensions could exploit a flaw in Claude’s extension to inject instructions and access connected Google Drive, Gmail, and GitHub data. LayerX said Anthropic’s May 6 fix left some takeover scenarios open.

May 8, 2026
Vulnerability & Exploit · netskope.com

DirtyFrag Linux Kernel Bugs Enable Root Access Across Major Distributions

DirtyFrag exploits two Linux kernel page-cache write bugs for local root access. A public PoC is available, but no in-the-wild exploitation is confirmed; one bug remains unpatched, and distribution kernels had not yet shipped fixes.

May 8, 2026
PreviousPage 51 of 65 Next
© 2026 cyber.hendryadrian.com