cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · wiz.io

Dirty Frag Linux Kernel Flaws Could Let Local Attackers Gain Root

Dirty Frag (CVE-2026-43284 and CVE-2026-43500) chains Linux kernel ESP and RxRPC flaws to enable local privilege escalation. No official patches are available; disabling vulnerable modules is a temporary mitigation.
May 8, 2026
Vulnerability & Exploit · bleepingcomputer.com

Linux “Dirty Frag” Zero-Day Enables Local Root Escalation on Major Distributions

Researcher Hyunwoo Kim says Dirty Frag chains two Linux kernel flaws to enable local root escalation across major distributions. At publication, no CVE or patch was available; disabling three kernel modules is a temporary mitigation with service trade-offs.

May 8, 2026
Vulnerability & Exploit · securityweek.com

LayerX Reports Claude Chrome Extension Flaw That Could Let Attackers Control AI Agent

LayerX says a flaw in Claude in Chrome lets a zero-permission extension send privileged commands and bypass user-confirmation protections. It says Anthropic’s partial fix can be bypassed by switching the extension to privileged mode.

May 8, 2026
Vulnerability & Exploit · securityweek.com

Ivanti Patches EPMM Zero-Day Exploited in Targeted Attacks

Ivanti patched five EPMM vulnerabilities, including CVE-2026-6973, a high-severity flaw the vendor says was exploited in a very limited number of targeted attacks. CISA added it to KEV and set a May 10 deadline for federal agencies.

May 8, 2026
Vulnerability & Exploit · cyberscoop.com

Ivanti Patches Actively Exploited EPMM Zero-Day Requiring Admin Access

Ivanti says attackers have exploited CVE-2026-6973, an EPMM flaw requiring authenticated administrative access for remote code execution. It released patches for five vulnerabilities; the company reported very limited exploitation and did not disclose the number of-imp

May 8, 2026
Vulnerability & Exploit · bleepingcomputer.com

Ivanti Patches EPMM Zero-Day RCE Exploited in Limited Attacks

Ivanti says CVE-2026-6973, an admin-authenticated RCE affecting EPMM 12.8.0.0 and earlier, has seen very limited zero-day exploitation. Fixes are available; Ivanti also patched four other high-severity EPMM flaws.

May 8, 2026
Vulnerability & Exploit · securityweek.com

Palo Alto Networks Firewall Zero-Day Exploited in Campaign With Possible China Links

Palo Alto Networks says attackers exploited CVE-2026-0300 for root-level remote code execution in its firewalls, using tunneling tools and deleting logs. The company has not attributed the campaign to a specific country.

May 7, 2026
Vulnerability & Exploit · wiz.io

Critical PAN-OS Buffer Overflow Enables Unauthenticated Root RCE; Exploitation Reported

CVE-2026-0300 is a critical PAN-OS buffer overflow enabling unauthenticated root-level RCE through the User-ID Authentication Portal. Palo Alto Networks reports limited exploitation; internet-exposed portals are at greater risk.

May 6, 2026
Vulnerability & Exploit · securityweek.com

Palo Alto Networks Reports Limited Exploitation of PAN-OS Zero-Day CVE-2026-0300

Palo Alto Networks says CVE-2026-0300, a PAN-OS buffer overflow in the User-ID Authentication Portal, has seen limited exploitation. It affects certain PA and VM firewalls; patches were expected beginning May 13, 2026.

May 6, 2026
Vulnerability & Exploit · thehackernews.com

Apache HTTP Server CVE-2026-23918 Enables DoS and Potential RCE

Apache HTTP Server 2.4.66 has a mod_http2 double-free flaw that can cause unauthenticated DoS and may enable RCE under specific conditions. Version 2.4.67 fixes the issue; MPM prefork is reported unaffected.

May 5, 2026
Vulnerability & Exploit · securityweek.com

Ollama Bug Could Expose Sensitive Data From 300,000 Deployments

Cyera says unauthenticated attackers could exploit Ollama CVE-2026-7482 to read sensitive heap data. It reports roughly 300,000 deployments are internet-exposed; Ollama fixed the flaw in version 0.17.1.

May 5, 2026
Vulnerability & Exploit · securityweek.com

Google Patches Critical Android RCE Vulnerability in adbd

Google released an Android update for CVE-2026-0073, a critical flaw affecting the adbd process that can allow remote code execution as the shell user without user interaction. No malicious exploitation has been reported.

May 5, 2026
Vulnerability & Exploit · bleepingcomputer.com

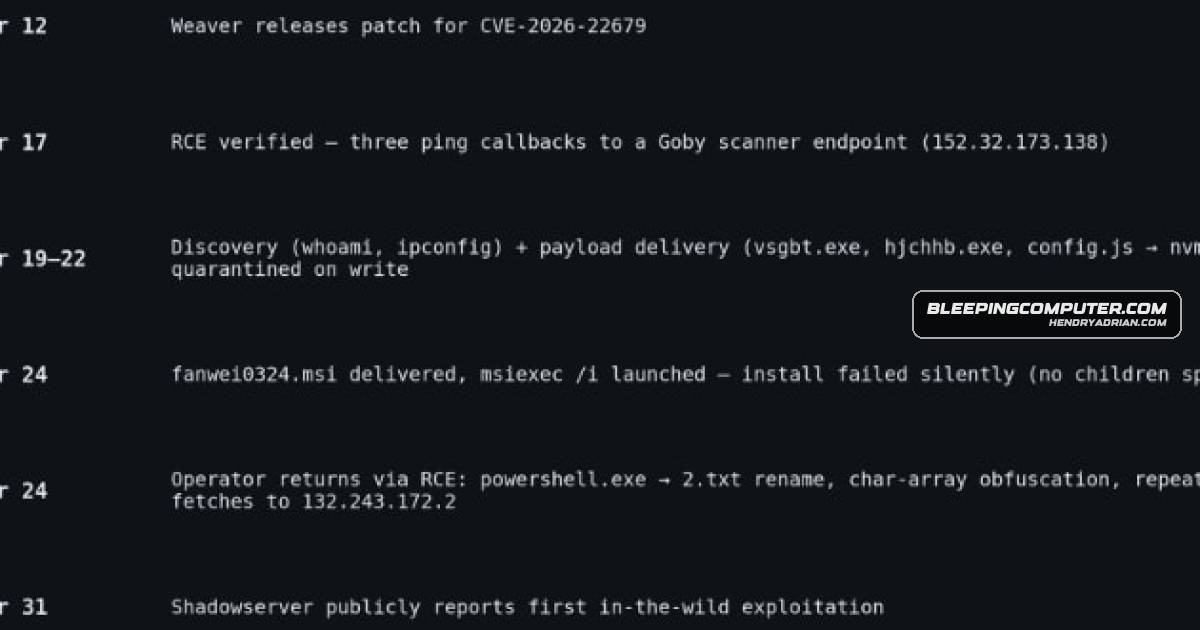
Weaver E-cology RCE Flaw Exploited in Attacks Since Mid-March

Vega reported attacks exploiting CVE-2026-22679, an unauthenticated RCE flaw in Weaver E-cology 10.0. Endpoint defenses blocked payloads, and researchers saw no persistent access. The vendor's build 20260312 removes the vulnerable debug endpoint.

May 5, 2026
Vulnerability & Exploit · cyberscoop.com

Linux “Copy Fail” Flaw Added to CISA Exploited List Amid AI Disclosure Controversy

CVE-2026-31431, a Linux kernel flaw enabling local privilege escalation, was added to CISA’s exploited-vulnerability catalog. The article reports active exploitation, notes patches preceded disclosure, and warns about numerous copycat AI-generated PoCs.

May 5, 2026
Vulnerability & Exploit · thehackernews.com

Progress Patches Critical MOVEit Automation Authentication Bypass and Input Validation Flaws

Progress patched two MOVEit Automation flaws that could enable authentication bypass and privilege escalation, potentially exposing data or administrative access. Affected versions have updates available; no workarounds are listed.

May 4, 2026
Vulnerability & Exploit · bleepingcomputer.com

Progress Patches Critical MOVEit Automation Authentication Bypass

Progress patched CVE-2026-4670, a critical authentication bypass affecting earlier MOVEit Automation versions, and CVE-2026-5174, a high-severity privilege escalation flaw. It recommends upgrading with the full installer, which causes an outage.

May 4, 2026
Vulnerability & Exploit · securityweek.com

Copy Fail Linux Kernel Vulnerability Exploited in the Wild

CISA added Linux kernel flaw CVE-2026-31431, dubbed Copy Fail, to its KEV catalog. Microsoft reports limited exploitation, mainly PoC testing, and warns the flaw can enable local privilege escalation to root.

May 4, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited Linux Copy Fail Flaw to KEV

CISA added Linux kernel flaw CVE-2026-31431 (Copy Fail) to its KEV catalog, citing active exploitation. The local privilege-escalation flaw can grant root; fixes are available in kernel versions 6.18.22, 6.19.12, and 7.0.

May 3, 2026
Vulnerability & Exploit · bleepingcomputer.com

CVE-2026-41940 cPanel Flaw Exploited in Sorry Ransomware Attacks

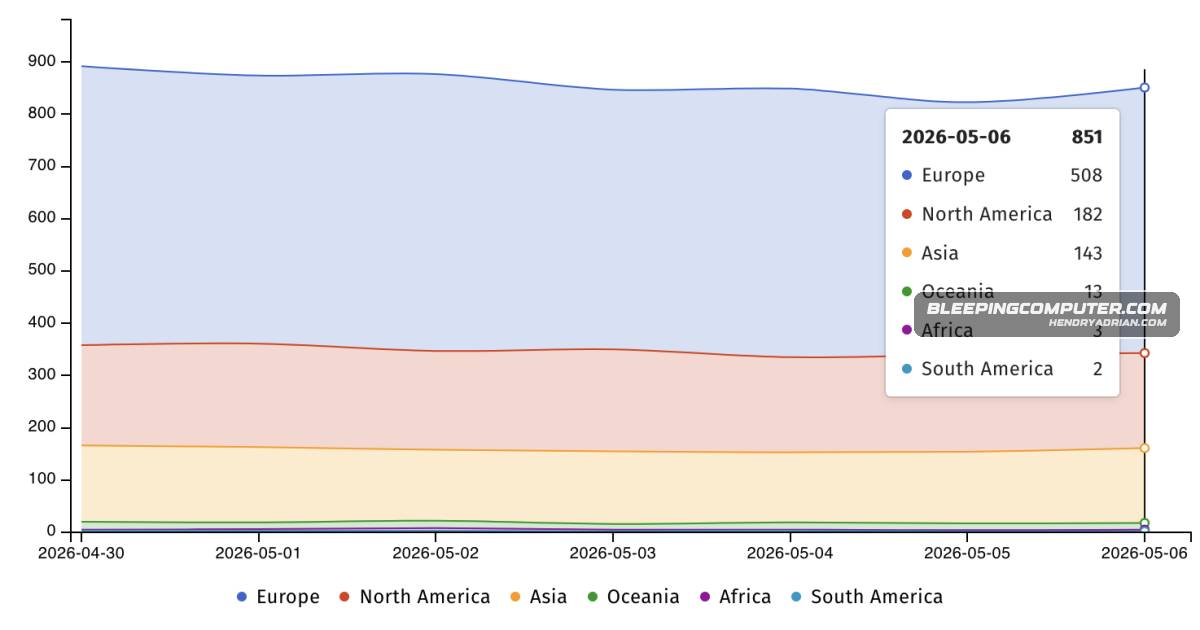
A critical WHM and cPanel authentication bypass, CVE-2026-41940, is reportedly being exploited to deploy the Sorry Linux encryptor. Shadowserver reports at least 44,000 cPanel IP addresses compromised; an emergency update is available.

May 3, 2026
Vulnerability & Exploit · therecord.media

CISA Orders Federal Agencies to Patch Actively Exploited cPanel Bug by May 3

CISA ordered federal agencies to patch CVE-2026-41940 in cPanel & WHM by May 3. The 9.8-rated flaw is being exploited and could give attackers control of affected hosts; vendors released fixes and detection tools.

May 2, 2026
Vulnerability & Exploit · wiz.io

Copy Fail Linux Kernel Flaw Enables Local Privilege Escalation to Root

CVE-2026-31431 lets unprivileged local users exploit a Linux kernel flaw to gain root and, in some scenarios, escape containers. Upstream has fixed it, but distribution patches remain uneven; teams should prioritize updates and mitigations.

May 1, 2026
Vulnerability & Exploit · sysdig.com

Copy Fail Linux Kernel Flaw Enables Local Root Escalation

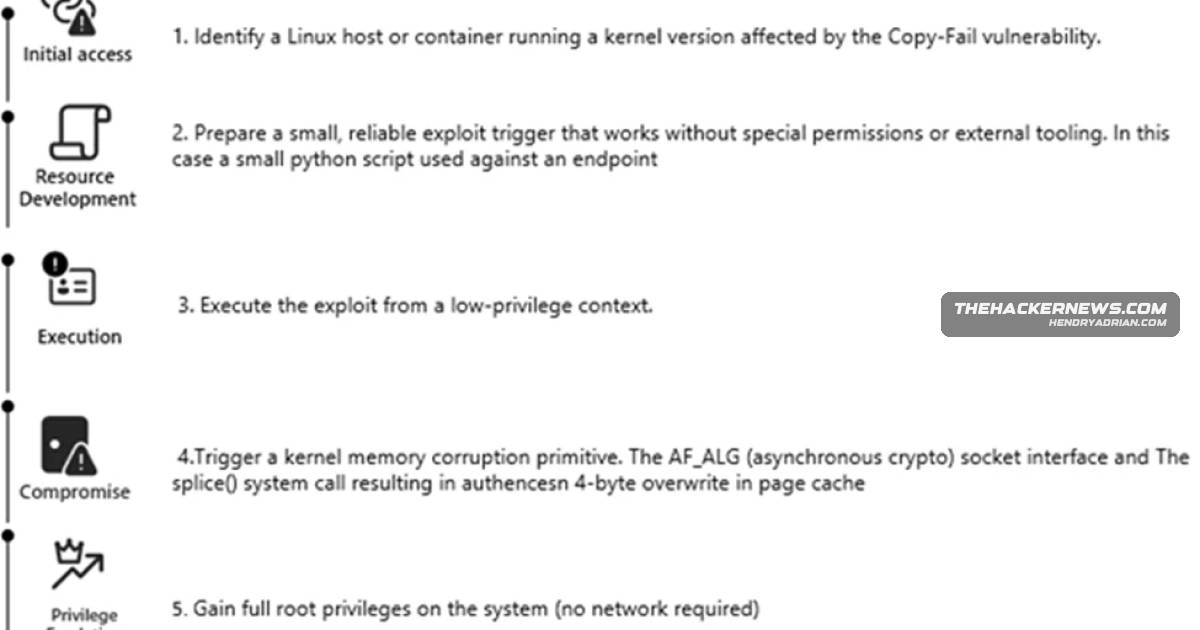
CVE-2026-31431 (“Copy Fail”) lets an unprivileged local user exploit Linux’s algif_aead interface with AF_ALG and splice() to corrupt setuid binaries’ page cache and gain root. Fixes are available in kernels 7.0, 6.19.12 and 6.18.22.

May 1, 2026
Vulnerability & Exploit · helpnetsecurity.com

cPanel Zero-Day CVE-2026-41940 Exploited Since February; Patches Released

CVE-2026-41940, an authentication bypass in cPanel/WHM, has reportedly been exploited since Feb. 23. WebPros released patches April 28; guidance includes updating, restarting cpsrvd, and restricting exposed ports.

Apr 30, 2026
Vulnerability & Exploit · bleepingcomputer.com

Linux Copy Fail Flaw Enables Local Root Access on Affected Kernels

Copy Fail (CVE-2026-31431) lets an unprivileged local attacker gain root through a controlled page-cache write. A public 732-byte PoC targets major Linux distributions; upstream fixes and interim AF_ALG/algif_aead mitigations are available.

Apr 30, 2026
PreviousPage 52 of 65 Next
© 2026 cyber.hendryadrian.com