cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · bleepingcomputer.com

Microsoft Issues Mitigations for YellowKey Windows BitLocker Zero-Day

Microsoft is tracking the publicly disclosed YellowKey BitLocker flaw as CVE-2026-45585 and advises removing autofstx.exe from BootExecute, restoring WinRE trust, and using TPM+PIN until a security update is available.
May 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

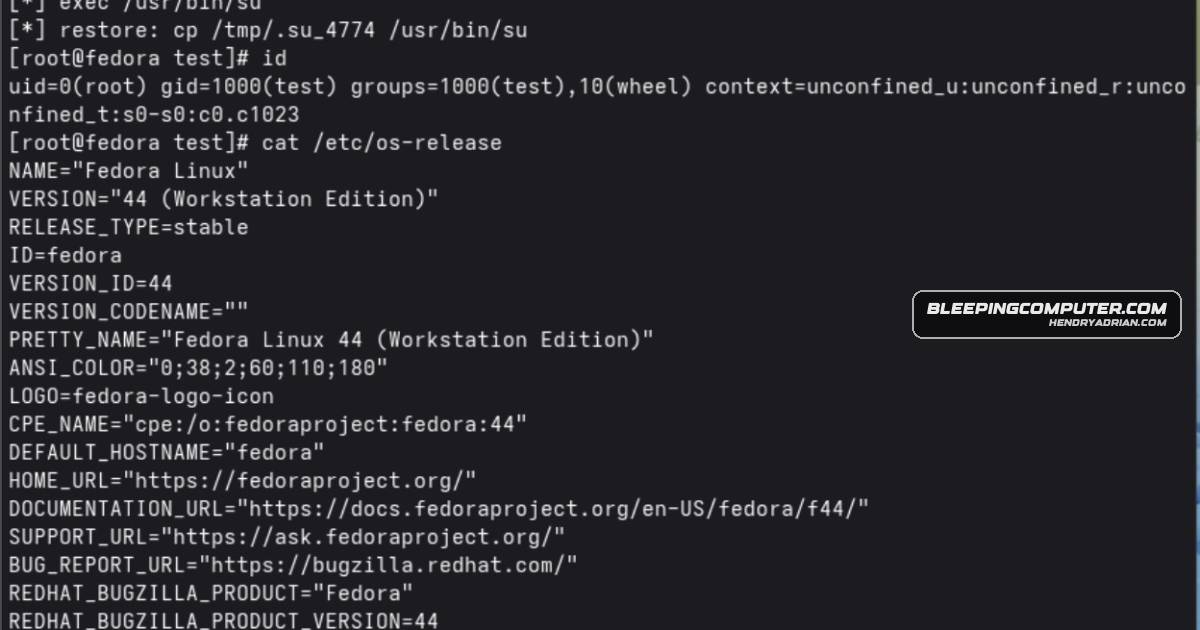
PoC exploit released for patched PinTheft Linux privilege-escalation flaw

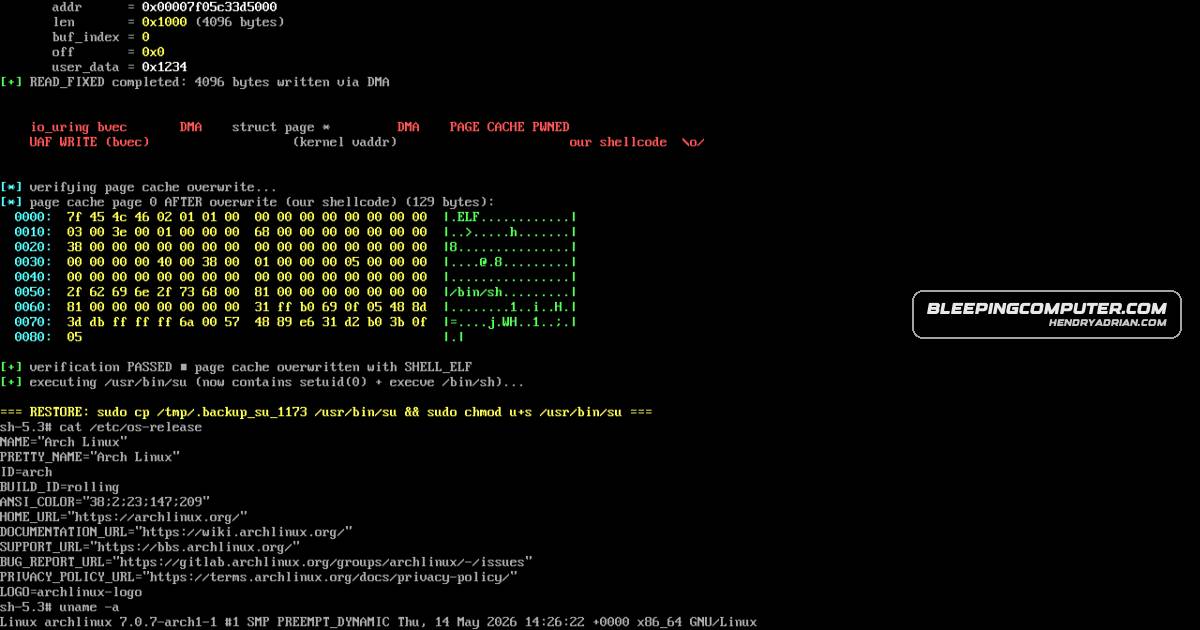
A public PoC targets the patched PinTheft Linux kernel flaw, which can provide root access under specific conditions. Exploitation requires RDS, io_uring, a readable SUID-root binary, and x86_64 support.

May 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

Drupal Warns Exploits Could Follow Core Security Update Within Hours

Drupal warned that exploits for an undisclosed core vulnerability could emerge within hours of its planned security update. Administrators should prepare to patch; Drupal 8 and 9 will not receive patches, though hotfixes are planned for certain legacy releases.

May 20, 2026
Vulnerability & Exploit · bleepingcomputer.com

Max-Severity ChromaDB Flaw Enables Unauthenticated Code Execution on Exposed Servers

HiddenLayer reports that CVE-2026-45829 lets unauthenticated attackers execute code on exposed ChromaDB Python servers by loading a malicious model before authentication. Versions 1.0.0–1.5.8 are affected; 1.5.9's status is unclear.

May 20, 2026
Vulnerability & Exploit · thehackernews.com

DirtyDecrypt PoC Targets Linux Kernel Local Privilege-Escalation Flaw

A PoC has been released for DirtyDecrypt, a Linux kernel page-cache write flaw in rxgk_decrypt_skb() associated with CVE-2026-31635. It may enable local privilege escalation on systems with CONFIG_RXGK; developers are considering a runtime killswitch.

May 19, 2026
Vulnerability & Exploit · securityweek.com

Drupal Plans Patch for Highly Critical Vulnerability, Warns Exploit Could Follow Quickly

Drupal says patches for an undisclosed highly critical vulnerability will be released May 20 for supported versions 11.3.x, 11.2.x, 10.6.x and 10.5.x. Developers warn an exploit may emerge within hours or days of disclosure.

May 19, 2026
Vulnerability & Exploit · securityweek.com

Unpatched ChromaDB Flaw Could Enable Pre-Authentication Server Takeover

HiddenLayer reports that CVE-2026-45829 lets unauthenticated attackers execute a malicious HuggingFace model before ChromaDB authentication, potentially gaining server-process control. ChromaDB 1.5.8 remains unpatched; restricting network access is a mitigation.

May 19, 2026
Vulnerability & Exploit · securityweek.com

Critical Flaw Enables Remote Code Execution on Universal Robots Cobots

CVE-2026-8153 is a critical command-injection flaw in Universal Robots’ PolyScope 5 Dashboard Server. An unauthenticated attacker with network access may execute commands on a robot; the vendor patched it in PolyScope 5.25.1.

May 19, 2026
Vulnerability & Exploit · bleepingcomputer.com

PoC Exploit Targets DirtyDecrypt Linux Kernel Privilege-Escalation Flaw

A proof-of-concept for the patched DirtyDecrypt (DirtyCBC) Linux kernel privilege-escalation flaw can grant root on systems with CONFIG_RXGK enabled. Researchers say it aligns with CVE-2026-31635; users are urged to update or apply a temporary mitigation.

May 18, 2026
Vulnerability & Exploit · securityweek.com

Cyera Details Four OpenClaw Flaws That Can Enable Sandbox Escape and Backdoors

Cyera says four OpenClaw flaws, dubbed Claw Chain, can be chained from code execution inside the sandbox to access data, escalate privileges, and plant host backdoors. OpenClaw rolled out patches the day after disclosure.

May 18, 2026
Vulnerability & Exploit · bleepingcomputer.com

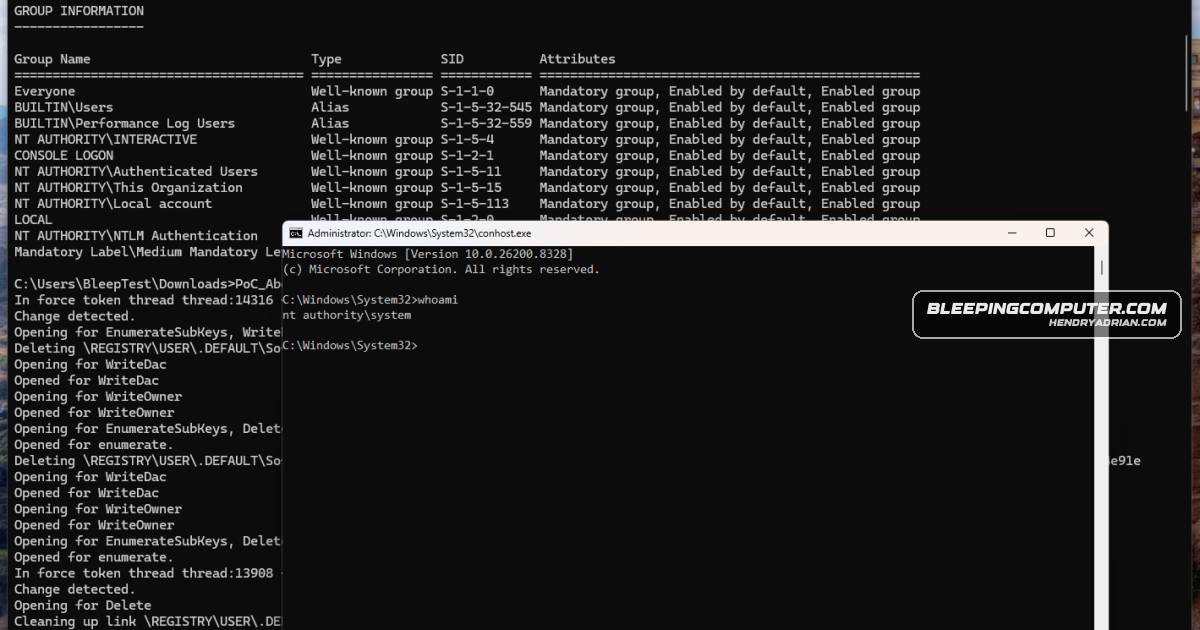
MiniPlasma PoC reportedly grants SYSTEM access on patched Windows 11

Chaotic Eclipse says MiniPlasma can exploit CVE-2020-17103 for SYSTEM access on patched Windows 11. BleepingComputer and a vulnerability analyst reported successful tests on public builds, but not the latest Canary build.

May 18, 2026
Vulnerability & Exploit · thehackernews.com

VulnCheck Reports Exploitation Attempts Against NGINX and openDCIM Flaws

VulnCheck reports honeypot-detected exploitation attempts against NGINX CVE-2026-42945 and openDCIM flaws. The NGINX heap overflow can crash workers; RCE requires a specific configuration and disabled ASLR. Three openDCIM flaws can be chained for RCE.

May 17, 2026
Vulnerability & Exploit · bleepingcomputer.com

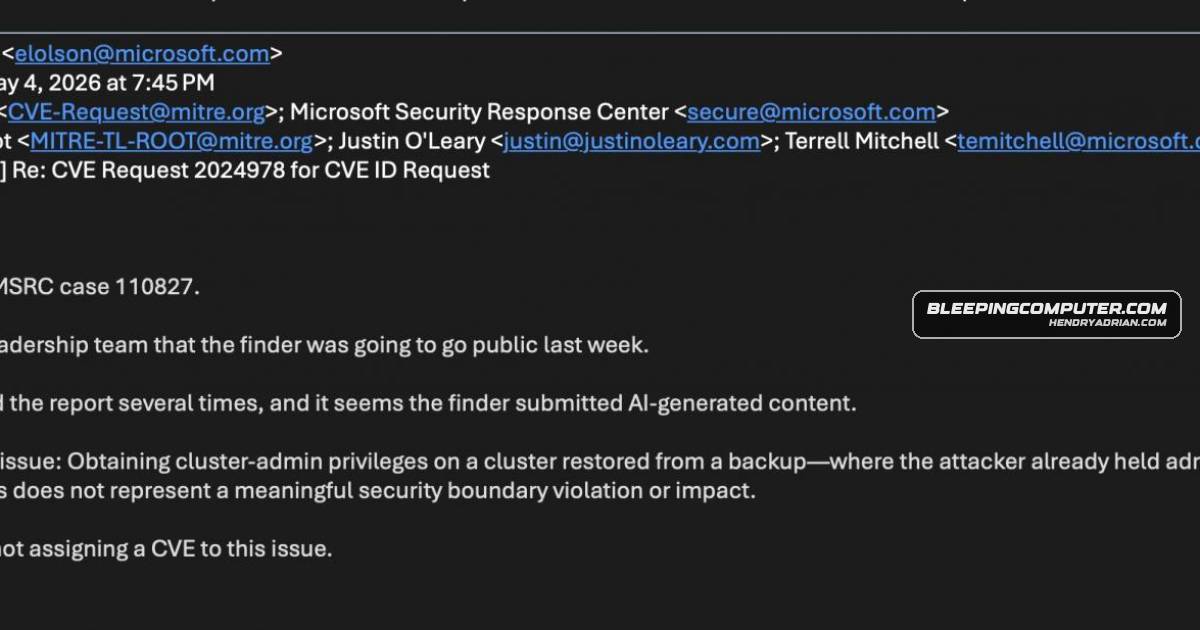
Researcher Claims Azure Backup for AKS Flaw Was Quietly Fixed After Rejection

Justin O’Leary says Azure Backup for AKS let Backup Contributors gain cluster-admin via Trusted Access. Microsoft rejects the vulnerability and says it made no changes; CERT/CC reportedly validated it, and O’Leary says the attack path later stopped working.

May 17, 2026
Vulnerability & Exploit · thehackernews.com

Actively Exploited Funnel Builder Flaw Enables WooCommerce Checkout Skimming

Sansec reports active exploitation of a Funnel Builder flaw affecting versions before 3.15.0.3, allowing unauthenticated JavaScript injection into WooCommerce checkout pages. The injected skimmer targets payment data; site owners should update and review External Script

May 16, 2026
Vulnerability & Exploit · securityweek.com

PoC Exploit Published for Critical NGINX Flaw as Exploitation Begins

PoC code is available for CVE-2026-42945, a critical heap buffer overflow in NGINX’s ngx_http_rewrite_module. F5 says it can cause DoS and potentially RCE if ASLR is disabled; exploitation has started, and patched versions are listed.

May 16, 2026
Vulnerability & Exploit · bleepingcomputer.com

Funnel Builder WordPress Flaw Exploited to Inject WooCommerce Checkout Skimmer

An unauthenticated flaw in Funnel Builder versions before 3.15.0.3 is being exploited to inject a payment card skimmer into WooCommerce checkouts. FunnelKit released a fix and advises updating and checking External Scripts.

May 15, 2026
Vulnerability & Exploit · therecord.media

CISA Sets Sunday Deadline to Patch Exploited Cisco SD-WAN Flaw

CISA ordered federal agencies to patch CVE-2026-20182 in Cisco SD-WAN by Sunday. Cisco says the critical flaw allows remote authentication bypass and admin access; exploitation was observed this month. CISA also urged agencies to follow February’s compromise-hunting

May 15, 2026
Vulnerability & Exploit · thehackernews.com

Four OpenClaw Flaws Could Enable Data Theft, Privilege Escalation and Persistence

Cyera disclosed four linked OpenClaw flaws, dubbed Claw Chain, that could enable sandbox escapes, sensitive-file access, privilege escalation and persistence. OpenClaw fixed them in version 2026.4.22.

May 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

Avada Builder WordPress Plugin Flaws Could Expose Files and Database Credentials

Wordfence reports two Avada Builder flaws: one permits authenticated arbitrary file reads, while another enables conditional unauthenticated SQL injection. Version 3.15.3 fixes both; site owners are urged to update.

May 15, 2026
Vulnerability & Exploit · cyberscoop.com

Cisco Warns of Ongoing Exploitation of SD-WAN Zero-Day CVE-2026-20182

Cisco says UAT-8616 is exploiting CVE-2026-20182, a critical authentication bypass in Catalyst SD-WAN Controller and Manager. Cisco released a patch; controller compromise could enable administrative access and affect the wider SD-WAN fabric.

May 15, 2026
Vulnerability & Exploit · securityweek.com

Microsoft Warns Exchange Server Zero-Day Is Being Exploited

Microsoft disclosed CVE-2026-42897, an Exchange Server OWA spoofing and XSS flaw reported exploited in attacks. It affects Subscription Edition, 2016 and 2019; Microsoft says crafted email interaction can trigger browser-context JavaScript and recommends mitigations.

May 15, 2026
Vulnerability & Exploit · bleepingcomputer.com

Microsoft Shares Mitigations for Exchange Zero-Day CVE-2026-42897

Microsoft says CVE-2026-42897, an Exchange Server spoofing flaw exploited in attacks, can trigger arbitrary JavaScript in Outlook on the web. EEMS and EOMT mitigations are available; patches are planned, with some updates limited to ESU customers.

May 15, 2026
Vulnerability & Exploit · darkreading.com

Cisco SD-WAN Authentication Bypass CVE-2026-20182 Exploited in the Wild

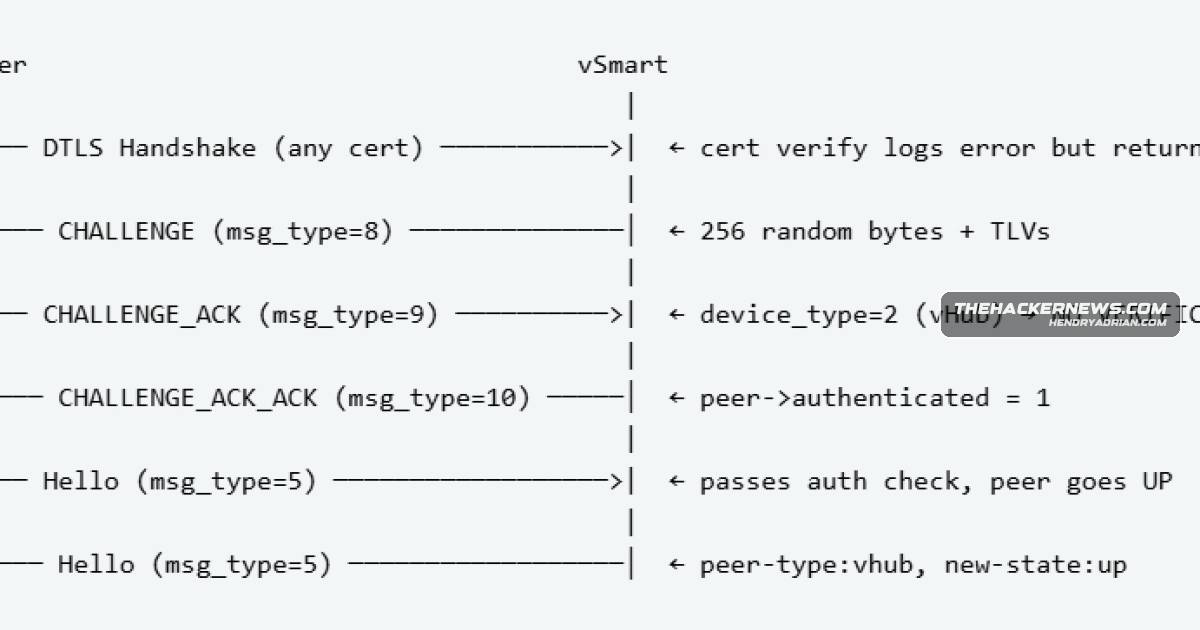
Cisco Talos reports UAT-8616 is exploiting CVE-2026-20182, a CVSS 10 authentication bypass in Cisco Catalyst SD-WAN Controllers. Observed follow-on activity includes SSH-key additions, NETCONF changes and root escalation; Cisco has released a patch.

May 15, 2026
Vulnerability & Exploit · thehackernews.com

Cisco Patches Actively Exploited Catalyst SD-WAN Authentication Bypass

Cisco released updates for CVE-2026-20182, a CVSS 10.0 authentication bypass in Catalyst SD-WAN Controller and Manager. Cisco reported limited exploitation in May 2026; successful attacks could enable administrative access and network configuration changes.

May 15, 2026
PreviousPage 50 of 65 Next
© 2026 cyber.hendryadrian.com