
18-Year-Old NGINX Flaw Can Cause DoS, With RCE Demonstrated Under Specific Conditions
Summary
CVE-2026-42945 is a heap buffer overflow in NGINX that can reliably crash workers and may enable RCE under specific conditions. F5 released fixes; researchers say dependable RCE with ASLR enabled is not established.
Key points
- CVE-2026-42945 affects NGINX versions 0.6.27 through 1.30.0 and involves a heap buffer overflow in ngx_http_rewrite_module.
- The flaw can be triggered by particular configurations combining rewrite and set directives; a crafted request can reliably crash worker processes.
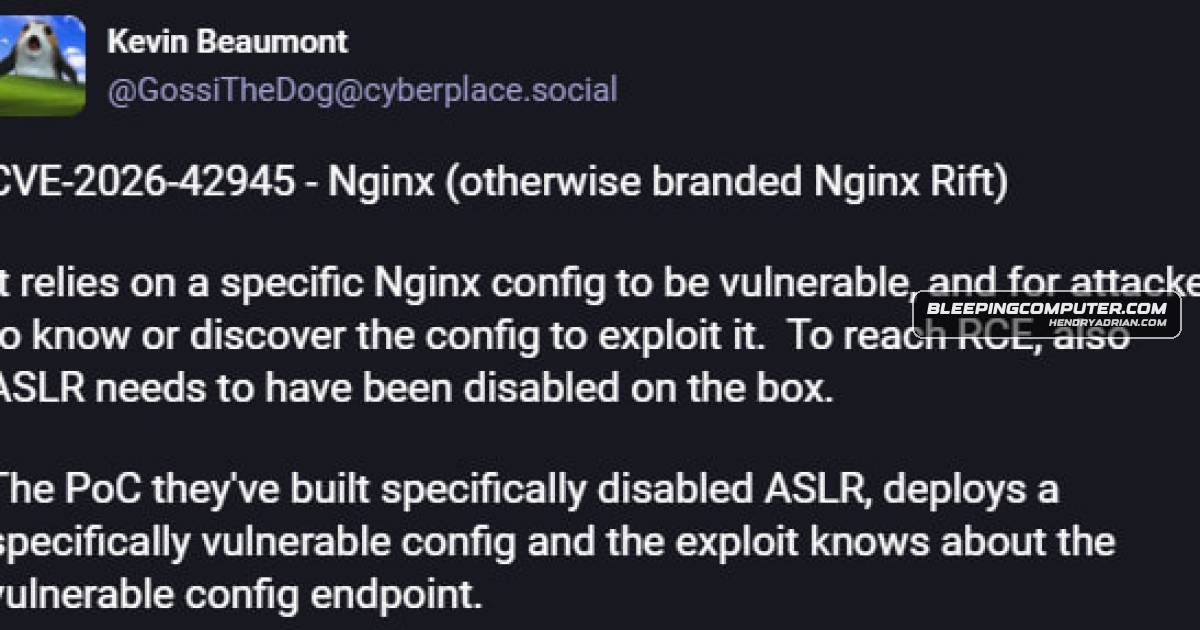
- DepthFirst AI demonstrated unauthenticated RCE in a setup with ASLR disabled. Researchers cited in the article say dependable RCE on systems with ASLR enabled is not established.
- The article also reports three other NGINX memory-corruption flaws: CVE-2026-42946, CVE-2026-40701, and CVE-2026-42934.
- F5 released fixes including NGINX Open Source 1.31.0 and 1.30.1; affected products also include NGINX Plus and other F5 NGINX products.
- For systems that cannot be upgraded, F5 recommends replacing unnamed PCRE capture groups in vulnerable rewrite rules with named captures.
Article Details
- Vulnerability Types
- Heap buffer overflow
- Excessive memory allocation
- Use-after-free
- Off-by-one UTF-8 parsing bug causing out-of-bounds reads
- Severity
- CVE-2026-42945 is rated critical (CVSS 9.2). The other flaws are described as medium severity, although CVE-2026-42946 is also labeled high in one passage.
- Affected Versions
- NGINX Open Source 0.6.27 through 1.30.0
- NGINX Plus R32 through R36
- NGINX Instance Manager 2.16.0 through 2.21.1
- F5 WAF for NGINX 5.9.0 through 5.12.1
- NGINX App Protect WAF 4.9.0 through 4.16.0 and 5.1.0 through 5.8.0
- F5 DoS for NGINX 4.8.0
- NGINX App Protect DoS 4.3.0 through 4.7.0
- NGINX Gateway Fabric 1.3.0 through 1.6.2 and 2.0.0 through 2.5.1
- NGINX Ingress Controller 3.5.0 through 3.7.2, 4.0.0 through 4.0.1, and 5.0.0 through 5.4.1
- Exploitation Status
- reported
- Exploit Availability
- public_poc
- Patch Status
- available
- Workarounds
- For vulnerable rewrite rules, replace unnamed PCRE capture groups ($1, $2, etc.) with named captures.
MITRE ATT&CK
T1190 · Exploit Public-Facing ApplicationResearchers demonstrated unauthenticated exploitation of NGINX using specially crafted HTTP requests against configurations with specific rewrite and set directives.T1499.004 · Application or System ExploitationA crafted request can trigger the heap buffer overflow and reliably crash NGINX worker processes, causing denial of service.
CVE
CVE-2026-40701F5 · NGINX Open Source; F5 · NGINX PlusCVE-2026-40701 — use-after-free in asynchronous OCSP DNS resolution handling (medium severity)CVE-2026-42934F5 · NGINX Open Source; F5 · NGINX PlusCVE-2026-42934 — off-by-one UTF-8 parsing bug causing out-of-bounds reads (medium severity)CVE-2026-42945F5 · NGINX Open Source; F5 · NGINX Plus; +21 moreAn 18-year-old heap buffer overflow in NGINX, tracked as CVE-2026-42945, can cause denial of service and may allow remote code execution under specific conditions.CVE-2026-42946F5 · NGINX Open Source; F5 · NGINX PlusCVE-2026-42946 — excessive memory allocation in SCGI/UWSGI modules that can crash workers via ~1 TB allocations (high severity)
People
Vendors
Products
F5 DoS for NGINXF5 DoS for NGINX 4.8.0F5 WAF for NGINXF5 WAF for NGINX 5.9.0 through 5.12.1NGINXAn 18-year-old heap buffer overflow in NGINX, tracked as CVE-2026-42945, can cause denial of service and may allow remote code execution under specific conditions.NGINX App Protect DoSNGINX App Protect DoS 4.3.0 through 4.7.0NGINX App Protect WAFNGINX App Protect WAF 4.9.0 through 4.16.0 and 5.1.0 through 5.8.0NGINX Gateway FabricNGINX Gateway Fabric 1.3.0 through 1.6.2 and 2.0.0 through 2.5.1NGINX Ingress ControllerNGINX Ingress Controller 3.5.0 through 3.7.2, 4.0.0 through 4.0.1, and 5.0.0 through 5.4.1NGINX Instance ManagerNGINX Instance Manager 2.16.0 through 2.21.1NGINX Open SourceNGINX Open Source versions 0.6.27 through 1.30.0NGINX PlusNGINX Plus R32 through R36
Industries
E-commerceOwned and maintained by American tech firm F5, the web server is used by cloud providers, SaaS companies, banks, media platforms, e-commerce sites, and in Kubernetes clusters.MediaOwned and maintained by American tech firm F5, the web server is used by cloud providers, SaaS companies, banks, media platforms, e-commerce sites, and in Kubernetes clusters.SaaSOwned and maintained by American tech firm F5, the web server is used by cloud providers, SaaS companies, banks, media platforms, e-commerce sites, and in Kubernetes clusters.