
Researcher Releases PoCs for Windows BitLocker Bypass and Privilege-Escalation Flaws
Summary
Chaotic Eclipse released PoCs for YellowKey, a BitLocker bypass affecting Windows 11 and Server 2022/2025, and GreenPlasma, an incomplete privilege-escalation exploit. Researchers differ on whether YellowKey works with TPM and PIN.
Key points
- YellowKey reportedly affects Windows 11 and Windows Server 2022/2025 and can expose a BitLocker-protected volume through a shell launched in Windows Recovery Environment.
- The PoC uses specially crafted FsTx files and NTFS transaction handling; it can be placed on a USB drive, while the researcher also claims an EFI-partition method.
- Kevin Beaumont confirmed the exploit; Will Dormann reproduced it using a USB drive but not the EFI-partition method.
- The researcher claims YellowKey can work with TPM and PIN, but that PoC has not been released. Dormann says the current exploit relies on TPM-only auto-unlock and does not work with TPM and PIN.
- The current YellowKey exploit requires the original device and does not work against stolen drives, according to the article. Dormann recommends a BitLocker PIN and BIOS password as mitigation.
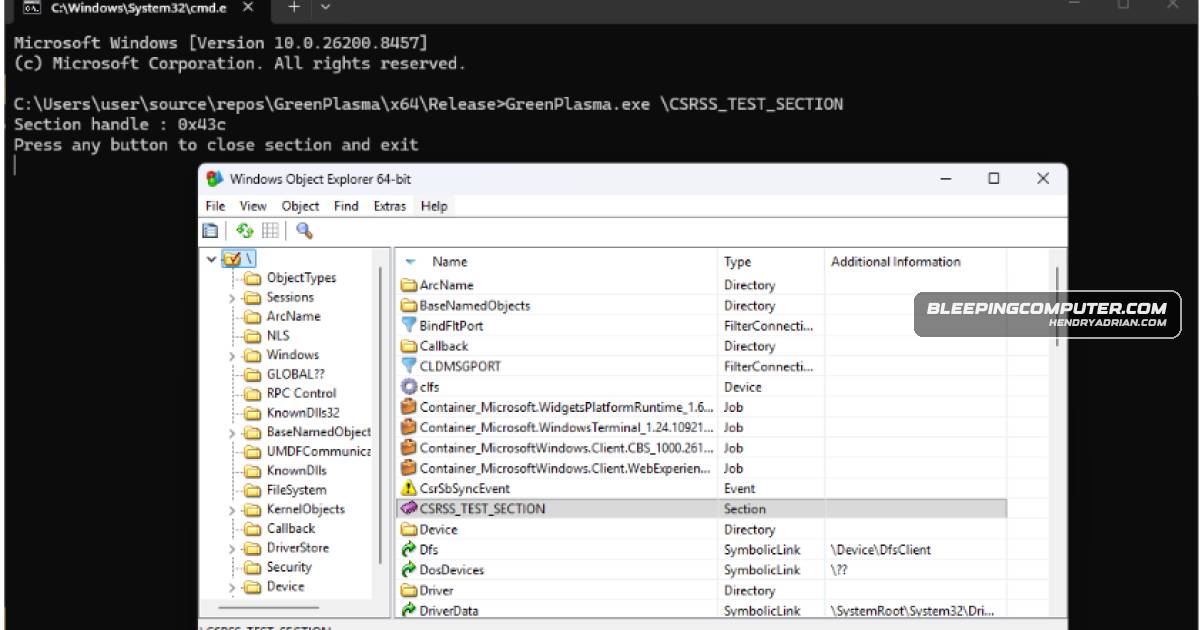
- GreenPlasma is described as a Windows privilege-escalation flaw involving arbitrary memory-section objects in directories writable by SYSTEM. Its incomplete PoC lacks the component needed for a full SYSTEM shell.
Article Details
- Vulnerability Types
- BitLocker bypass
- Privilege escalation
- Affected Versions
- Windows 11
- Windows Server 2022
- Windows Server 2025
- Exploitation Status
- unknown
- Exploit Availability
- public_poc
- Patch Status
- unavailable
- Workarounds
- Kevin Beaumont recommended using a BitLocker PIN and a BIOS password as mitigation.
MITRE ATT&CK
CVE
People
Chaotic EclipseReleased proof-of-concept exploits for YellowKey and GreenPlasma; the article says the researcher is known as Nightmare Eclipse on GitHub.Kevin BeaumontIndependent security researcher who confirmed the YellowKey exploit and recommended a BitLocker PIN and BIOS password as mitigation.Will DormannPrincipal vulnerability analyst at Tharros Labs who confirmed testing the YellowKey exploit with FsTx files on USB and explained its interaction with NTFS transactions and Windows Recovery.
Vendors
Products
BitLockerA researcher known as Chaotic Eclipse or Nightmare Eclipse has released proof-of-concept exploits for two unpatched Windows flaws, YellowKey and GreenPlasma, affecting BitLocker and privilege escalation.Microsoft WindowsA researcher known as Chaotic Eclipse or Nightmare Eclipse has released proof-of-concept exploits for two unpatched Windows flaws, YellowKey and GreenPlasma, affecting BitLocker and privilege escalation.