
CISA Gives Federal Agencies Four Days to Patch Actively Exploited Ivanti EPMM Flaw
Summary
CISA gave U.S. federal agencies until May 10 to patch CVE-2026-6973, an actively exploited flaw enabling authenticated administrators to execute code remotely on on-prem Ivanti EPMM systems. Ivanti released fixed versions and recommends reviewing admin accounts and, ifs
Key points
- CVE-2026-6973 allows attackers with administrative authentication to execute arbitrary code remotely on on-prem EPMM 12.8.0.0 and earlier.
- CISA added the flaw to its list of vulnerabilities exploited in attacks and ordered federal agencies to patch by midnight Sunday, May 10.
- Ivanti said exploitation was very limited at disclosure and that successful exploitation requires admin authentication.
- Ivanti released fixes in EPMM versions 12.6.1.1, 12.7.0.1, and 12.8.0.1; it also advised reviewing admin accounts and rotating credentials where needed.
- Ivanti said the issue affects only on-prem EPMM, not Ivanti Neurons for MDM or its other products.
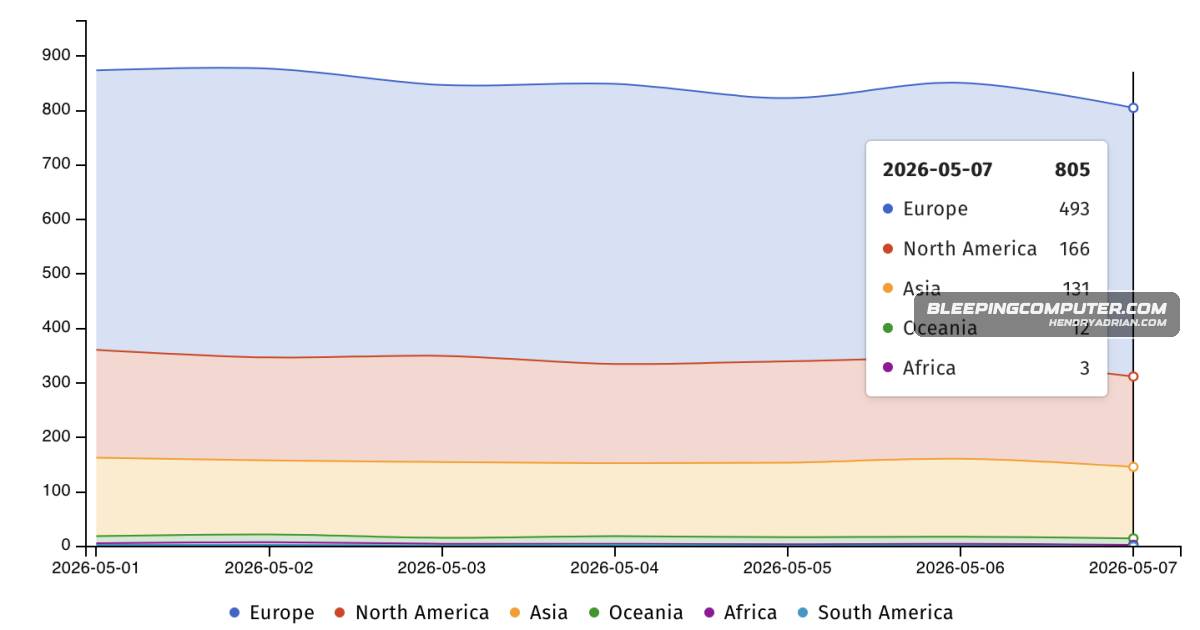
- Shadowserver tracks more than 800 EPMM appliances exposed online, but the article says the number already patched is unknown.
Article Details
- Vulnerability Types
- Authenticated remote code execution
- Severity
- High
- Affected Versions
- Ivanti EPMM 12.8.0.0 and earlier
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Review accounts with Admin rights and rotate those credentials where necessary.
CVE
CVE-2026-1281Ivanti · Endpoint Manager MobileIn late January, Ivanti patched two other critical EPMM security issues (CVE-2026-1281 and CVE-2026-1340) that were exploited in zero-day attacks affecting a “very limited number of customers.” On April 8, CISA alsoCVE-2026-1340Ivanti · Endpoint Manager MobileIn late January, Ivanti patched two other critical EPMM security issues (CVE-2026-1281 and CVE-2026-1340) that were exploited in zero-day attacks affecting a “very limited number of customers.” On April 8, CISA alsoCVE-2026-6973Ivanti · Endpoint Manager Mobilefederal agencies to patch an actively exploited zero-day in Ivanti Endpoint Manager Mobile (EPMM), tracked as CVE-2026-6973, within four days due to the risk of remote code execution on exposed systems.