
MiniPlasma PoC reportedly grants SYSTEM access on patched Windows 11
Summary
Chaotic Eclipse says MiniPlasma can exploit CVE-2020-17103 for SYSTEM access on patched Windows 11. BleepingComputer and a vulnerability analyst reported successful tests on public builds, but not the latest Canary build.
Key points
- Chaotic Eclipse released MiniPlasma source code and a compiled proof of concept, claiming CVE-2020-17103 remains exploitable despite Microsoft's reported December 2020 fix.
- The exploit targets the cldflt.sys Cloud Filter driver and its HsmOsBlockPlaceholderAccess routine, using the undocumented CfAbortHydration API.
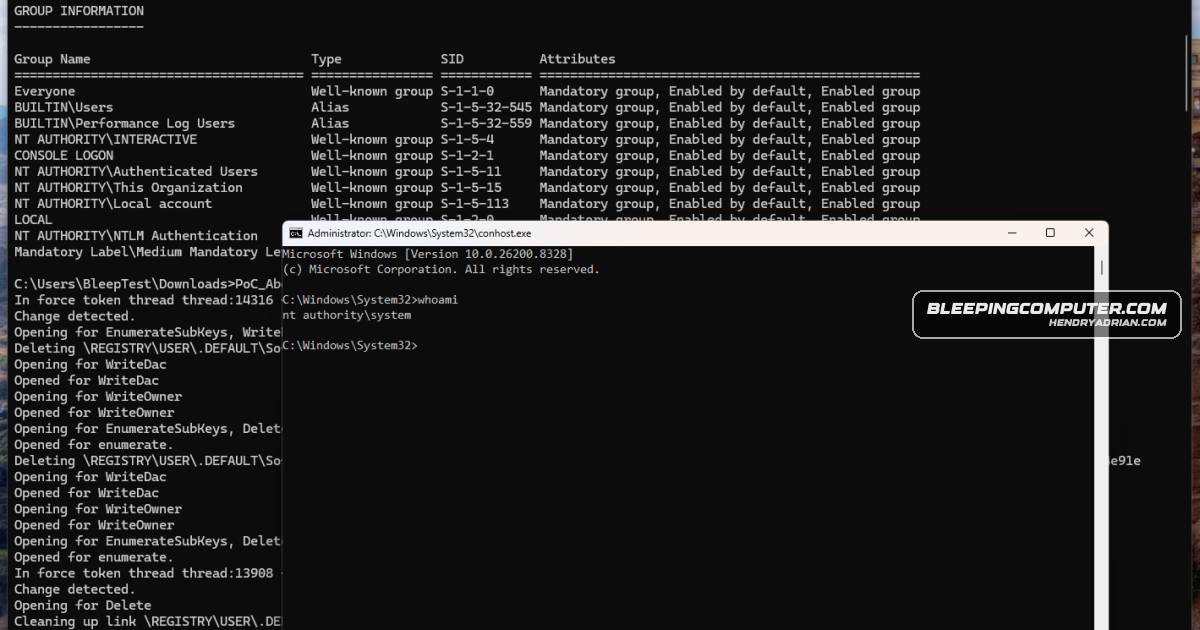
- BleepingComputer reported that the exploit launched a SYSTEM-privileged command prompt from a standard account on fully patched Windows 11 Pro with May 2026 updates.
- Vulnerability analyst Will Dormann said the exploit worked on the latest public Windows 11 version but not on the latest Insider Preview Canary build.
- Microsoft had not responded to BleepingComputer's inquiry at the time of publication.
Article Details
- Vulnerability Types
- Windows local privilege escalation through registry-key creation without proper access checks
- Affected Versions
- Windows 11 (latest public versions; the latest Canary build was reported not to be affected)
- Exploitation Status
- unknown
- Exploit Availability
- public_poc
- Patch Status
- unknown
MITRE ATT&CK
CVE
People
Chaotic EclipseReleased the MiniPlasma proof of concept and compiled exploit; the article also identifies the researcher as Nightmare Eclipse.James ForshawGoogle Project Zero researcher who originally reported the underlying flaw to Microsoft in 2020.Will DormannPrincipal vulnerability analyst at Tharros who confirmed MiniPlasma worked on the latest public Windows 11 version in his tests.