
Cisco Patches Actively Exploited Catalyst SD-WAN Authentication Bypass
Summary
Cisco released updates for CVE-2026-20182, a CVSS 10.0 authentication bypass in Catalyst SD-WAN Controller and Manager. Cisco reported limited exploitation in May 2026; successful attacks could enable administrative access and network configuration changes.
Key points
- CVE-2026-20182 affects Cisco Catalyst SD-WAN Controller and Manager and carries a CVSS score of 10.0.
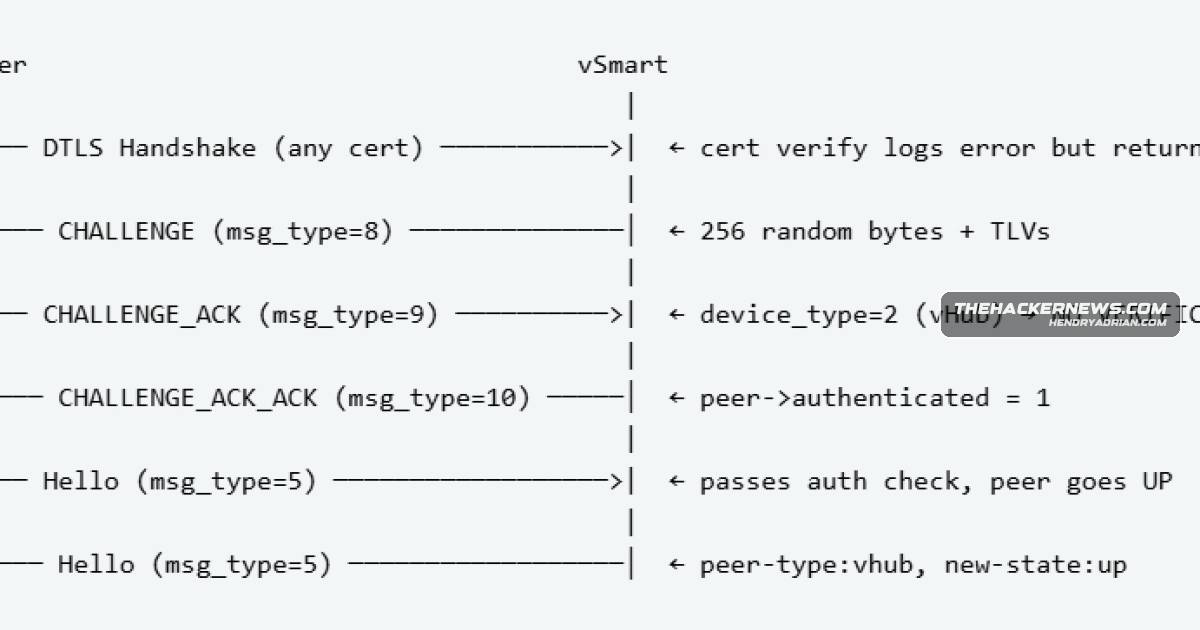
- Crafted requests can exploit a peering authentication failure to let a remote, unauthenticated attacker gain administrative privileges.
- Successful exploitation could enable access to NETCONF and allow changes to the SD-WAN fabric configuration.
- Cisco said it observed limited exploitation in May 2026 and released updates to address the flaw.
- Rapid7 said the flaw affects the vdaemon service over DTLS on UDP port 12346, like CVE-2026-20127, but is a distinct issue rather than a patch bypass.
- Cisco advises customers to update and review authentication and peering logs for suspicious activity, especially on internet-accessible systems.
Article Details
- Vulnerability Types
- Authentication bypass
- Severity
- Maximum severity; CVSS 10.0
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
MITRE ATT&CK
CVE
CVE-2026-20127Cisco · Cisco Catalyst SD-WAN ManagerThe flaw can let a remote unauthenticated attacker gain administrative access, manipulate SD-WAN network configuration, and is linked to similar issues previously observed in CVE-2026-20127 and activity by UAT-8616.CVE-2026-20182Cisco · Cisco Catalyst SD-WAN Controller; Cisco · Cisco Catalyst SD-WAN ManagerCisco has released updates for CVE-2026-20182, a maximum-severity authentication bypass in Catalyst SD-WAN Controller and Manager that has already seen limited exploitation.
People
Threat Actors
Vendors
Products
Cisco Catalyst SD-WAN Controller“A vulnerability in the peering authentication in Cisco Catalyst SD-WAN Controller, formerly SD-WAN vSmart, and Cisco Catalyst SD-WAN Manager, formerly SD-WAN vManage, could allow an unauthenticated, remote attacker toCisco Catalyst SD-WAN Managerthe peering authentication in Cisco Catalyst SD-WAN Controller, formerly SD-WAN vSmart, and Cisco Catalyst SD-WAN Manager, formerly SD-WAN vManage, could allow an unauthenticated, remote attacker to bypass