cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1554 articles

Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited LiteSpeed cPanel Flaw

CISA ordered U.S. federal agencies to patch CVE-2026-48172 by May 29. The actively exploited LiteSpeed cPanel plugin flaw can let unauthenticated attackers run scripts as root; LiteSpeed released updates.
May 27, 2026
Vulnerability & Exploit · securityweek.com

CISA Urges Patching of Actively Exploited LiteSpeed cPanel Plugin Flaw

CVE-2026-48172, an actively exploited privilege-escalation flaw in LiteSpeed’s cPanel user-end plugin, could enable root-level script execution. CISA added it to the KEV catalog and set a May 29 patch-or-remove deadline for federal agencies.

May 27, 2026
Vulnerability & Exploit · bleepingcomputer.com

KnowledgeDeliver flaw exploited as zero-day to deploy web shells

Mandiant reported zero-day exploitation of CVE-2026-5426 in KnowledgeDeliver LMS servers. Attackers abused shared ASP.NET machine keys to achieve remote code execution, deploy Godzilla, and deliver Cobalt Strike through fake software prompts.

May 26, 2026
Vulnerability & Exploit · thehackernews.com

Microsoft Patches SharePoint RCE Flaw Exploitable by Authenticated Users

Microsoft released fixes for SharePoint RCE flaw CVE-2026-45659. Untrusted deserialization could let an authenticated attacker with minimum Site Member permissions execute code remotely; Microsoft rates it 8.8 and says exploitation is less likely.

May 26, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited Drupal Flaw

CISA added Drupal SQL injection CVE-2026-9082 to its Known Exploited Vulnerabilities Catalog and ordered federal agencies to patch. Imperva reported over 15,000 attack attempts across nearly 6,000 sites.

May 26, 2026
Vulnerability & Exploit · securityweek.com

Underminr Flaw Lets Attackers Hide Malicious Connections on Shared CDNs

ADAMnetworks reports that attackers are exploiting Underminr, a shared-CDN routing flaw, to conceal connections to malicious domains and evade Protective DNS. The company estimates about 88 million domains could be affected.

May 23, 2026
Vulnerability & Exploit · thehackernews.com

CISA Adds Actively Exploited Drupal Core SQL Injection Flaw to KEV

CISA added Drupal Core SQL injection flaw CVE-2026-9082 to its KEV catalog after exploitation was detected. Imperva reported over 15,000 attempts against nearly 6,000 sites; most observed activity appeared to be probing.

May 23, 2026
Vulnerability & Exploit · thehackernews.com

LiteSpeed Says CVE-2026-48172 in cPanel Plugin Is Actively Exploited to Run Scripts as Root

LiteSpeed says CVE-2026-48172, a critical flaw in its cPanel plugin that can let attackers run scripts as root, is actively exploited. Users should check logs and upgrade to plugin v2.4.7 or later, or uninstall it.

May 23, 2026
Vulnerability & Exploit · securityweek.com

Drupal Reports Exploitation Attempts Against PostgreSQL-Specific CVE-2026-9082

Drupal says exploitation attempts target CVE-2026-9082, an unauthenticated SQL injection flaw affecting PostgreSQL-backed sites. Imperva reported more than 15,000 attempts against nearly 6,000 sites across 65 countries.

May 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

Ubiquiti Patches Five UniFi OS Flaws, Including Three Maximum-Severity Issues

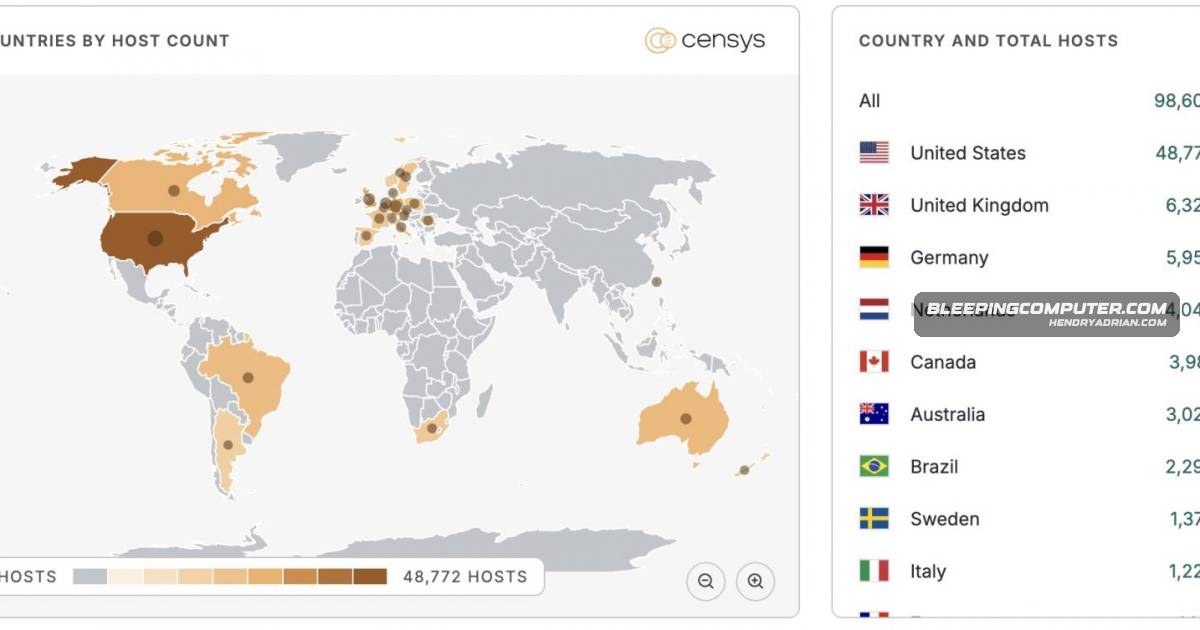
Ubiquiti patched five UniFi OS vulnerabilities, including three maximum-severity flaws involving access control, path traversal and command injection. Censys tracks nearly 100,000 internet-exposed endpoints; in-the-wild exploitation is unknown.

May 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

Drupal Warns of Exploitation Attempts Against Critical SQL Injection Flaw

Drupal says exploitation attempts targeting unauthenticated SQL injection flaw CVE-2026-9082 are being detected. The flaw affects multiple Drupal branches; administrators are urged to update, including those not using PostgreSQL.

May 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

Trend Micro Patches Apex One Zero-Day After Observed Exploitation Attempt

Trend Micro patched CVE-2026-34926, a directory traversal flaw in on-premises Apex One that could enable code injection by an attacker with server access and admin credentials. CISA added it to its exploited-vulnerabilities list.

May 22, 2026
Vulnerability & Exploit · securityweek.com

TrendAI Patches Apex One Zero-Day Exploited in the Wild

TrendAI patched CVE-2026-34926, a medium-severity Apex One directory-traversal flaw reported exploited in the wild. It affects on-premises installations, requires server admin credentials, and was added to CISA’s KEV catalog.

May 22, 2026
Vulnerability & Exploit · thehackernews.com

Cisco Patches CVSS 10.0 Secure Workload Flaw Allowing Cross-Tenant Data Access

Cisco patched CVE-2026-20223, a CVSS 10.0 flaw in Secure Workload REST API endpoints that could let unauthenticated remote attackers read sensitive data and change configurations across tenants. Cisco reports no evidence of exploitation.

May 22, 2026
Vulnerability & Exploit · thehackernews.com

Microsoft Says Two Defender Flaws Are Under Active Exploitation

Microsoft says Defender flaws CVE-2026-41091 and CVE-2026-45498 are actively exploited. One enables local SYSTEM privilege escalation; the other causes denial of service. Microsoft lists fixed platform versions, and CISA added both to KEV.

May 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

Exposed Chromium Flaw Can Keep JavaScript Running After Browser Closes

Google accidentally exposed details of an unfixed Chromium flaw that researcher Lyra Rebane says can keep JavaScript running after a browser closes. She found the issue still present in Chrome Dev 150 and Edge 148; no patch had shipped.

May 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Patches Secure Workload Flaw That Could Grant Unauthenticated Site Admin Access

Cisco patched CVE-2026-20223, a maximum-severity Secure Workload flaw that could let unauthenticated attackers gain Site Admin privileges, expose sensitive data, and change configurations across tenant boundaries. Cisco reports no known in-the-wild exploitation.

May 21, 2026
Vulnerability & Exploit · securityweek.com

Cisco Patches Critical Secure Workload Vulnerability Allowing Site Admin Access

Cisco patched CVE-2026-20223, a critical Secure Workload REST API flaw that could allow Site Admin access and cross-tenant data reading and configuration changes. Cisco also patched three medium-severity flaws in other products.

May 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

Microsoft Patches Two Defender Zero-Days Exploited in Attacks

Microsoft patched two exploited Defender zero-days: CVE-2026-41091 can enable SYSTEM privilege escalation, while CVE-2026-45498 can cause denial of service. CISA added both to its KEV Catalog and set a June 3 patch deadline for federal agencies.

May 21, 2026
Vulnerability & Exploit · securityweek.com

Microsoft Patches Two Defender Zero-Days Exploited in the Wild

Microsoft patched two Defender vulnerabilities it says were exploited in the wild: a local privilege-escalation flaw and a denial-of-service bug. CISA added both to its KEV list and set a June 3 patch deadline for federal agencies.

May 21, 2026
Vulnerability & Exploit · thehackernews.com

Drupal Patches Critical PostgreSQL SQL Injection Flaw in Core

Drupal patched CVE-2026-9082, an SQL injection flaw exploitable by anonymous users on PostgreSQL-backed sites that could lead to information disclosure, privilege escalation, or remote code execution.

May 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

SonicWall Gen6 VPN MFA Bypass Exploited When Required Remediation Is Incomplete

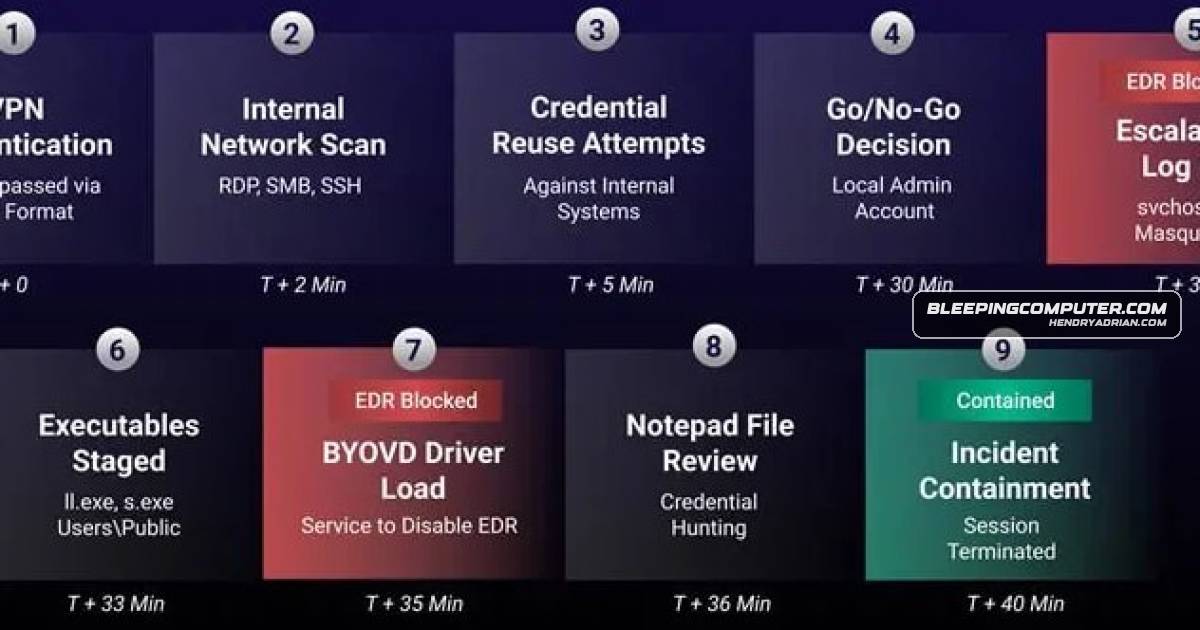
ReliaQuest reported intrusions exploiting CVE-2024-12802 to bypass MFA on SonicWall Gen6 SSL-VPN appliances. Firmware alone does not fix the issue: administrators must also reconfigure LDAP. EDR blocked attempted Cobalt Strike and driver deployment.

May 21, 2026
Vulnerability & Exploit · securitylabs.datadoghq.com

Kubernetes CVE-2021-25740 Lets Tenants Redirect Shared Load-Balancer Traffic

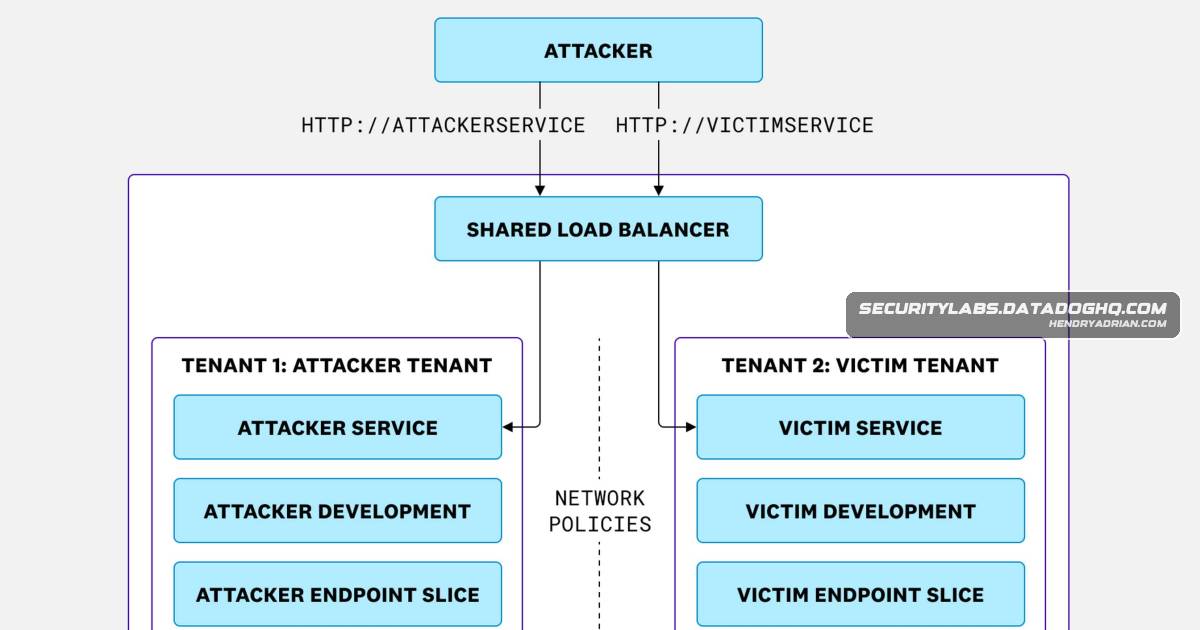
CVE-2021-25740 allows users who can modify EndpointSlice objects to redirect shared Kubernetes ingress or load-balancer traffic to workloads in other tenants’ namespaces. Mitigations include restricting EndpointSlice access and avoiding shared load balancers.

May 21, 2026
Vulnerability & Exploit · securityweek.com

Microsoft Mitigates YellowKey BitLocker Bypass Vulnerability

Microsoft released mitigations for CVE-2026-45585 (YellowKey), a physical-access BitLocker bypass using USB-triggered FsTx activity in Windows Recovery Environment. Chaotic Eclipse claims the exploit also works with a BitLocker PIN.

May 20, 2026
PreviousPage 49 of 65 Next
© 2026 cyber.hendryadrian.com