
Researcher Claims Azure Backup for AKS Flaw Was Quietly Fixed After Rejection
Summary
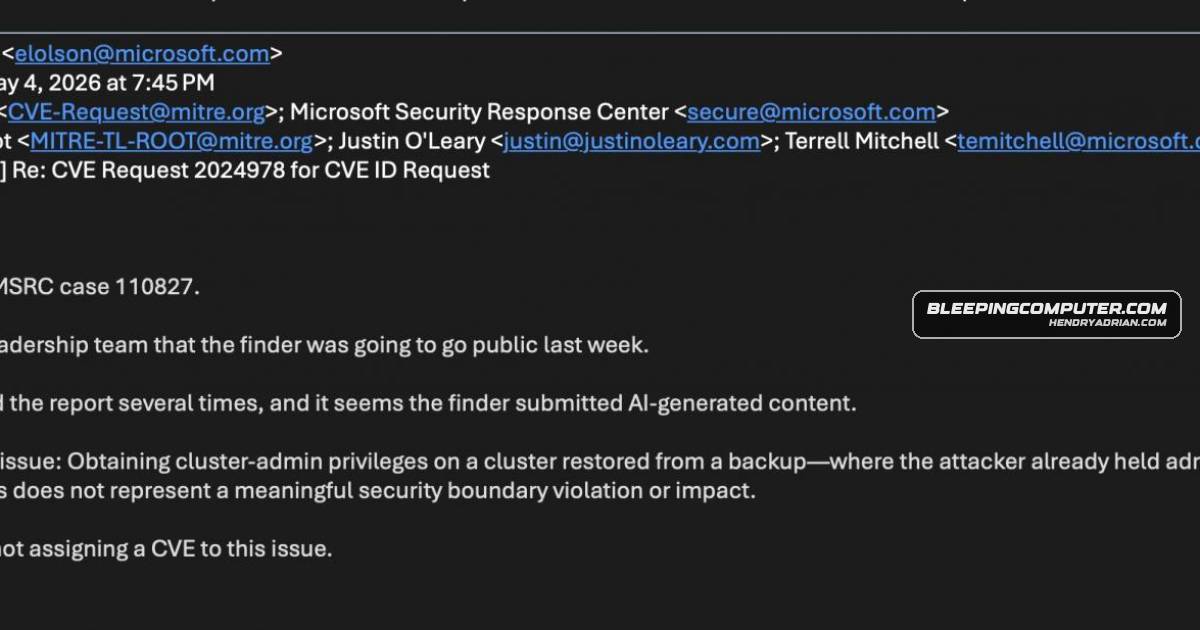
Justin O’Leary says Azure Backup for AKS let Backup Contributors gain cluster-admin via Trusted Access. Microsoft rejects the vulnerability and says it made no changes; CERT/CC reportedly validated it, and O’Leary says the attack path later stopped working.
Key points
- Justin O’Leary reported a critical Azure Backup for AKS privilege-escalation flaw to Microsoft on March 17.
- O’Leary says a user with the Backup Contributor role could trigger Trusted Access and gain cluster-admin without prior Kubernetes permissions.
- Microsoft rejected the report, saying the behavior was expected and required pre-existing administrative privileges.
- CERT/CC reportedly validated the issue on April 16; the article says the case later closed under CNA hierarchy rules without a CVE.
- O’Leary says the original attack path later stopped working and that new permission checks appeared, while Microsoft says no product changes were made.
- The researcher says the lack of a CVE or advisory limits defenders’ ability to track possible exposure and remediation.
Article Details
- Vulnerability Types
- Confused Deputy (CWE-441)
- Privilege escalation
- Severity
- Critical as classified by the researcher; Microsoft disputes that the behavior is a vulnerability.
- Exploitation Status
- unknown
- Exploit Availability
- unknown
- Patch Status
- unknown
MITRE ATT&CK
People
Vendors
Products
AKSMicrosoft is accused of quietly fixing an Azure Backup for AKS privilege escalation flaw after rejecting the researcher’s report and helping block a CVE.Azure Backup for AKSMicrosoft is accused of quietly fixing an Azure Backup for AKS privilege escalation flaw after rejecting the researcher’s report and helping block a CVE.