CVE-2026-16812: Critical Unauthenticated Command Injection in VeloCloud Orchestrator
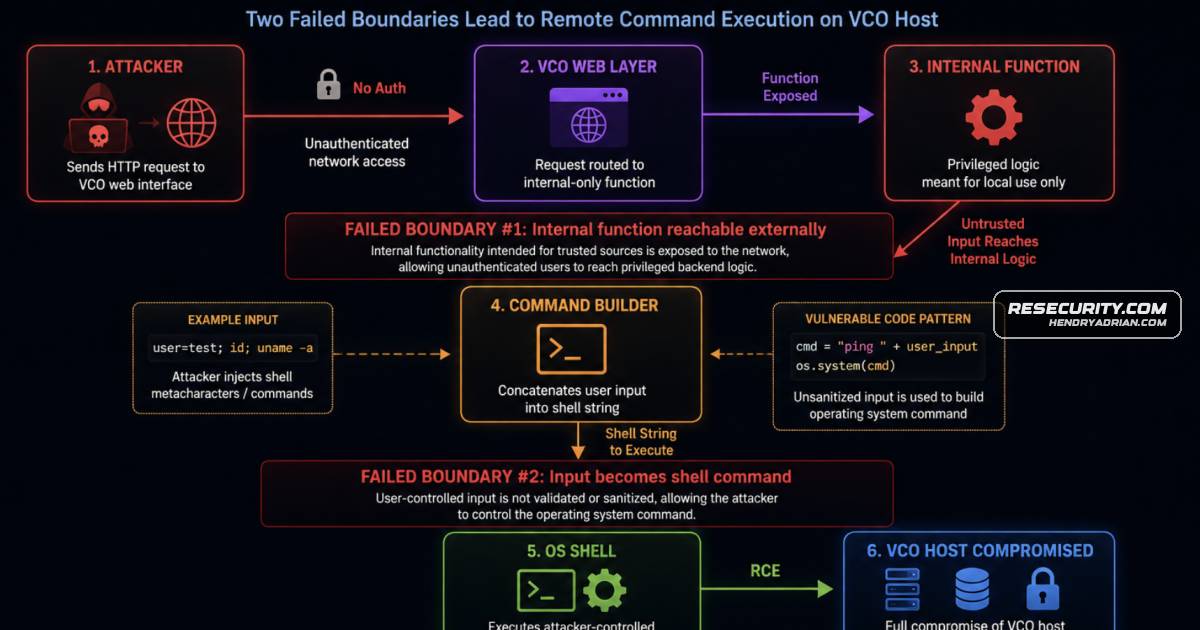
Arista says CVE-2026-16812, an unauthenticated OS command injection in on-premises VeloCloud Orchestrator, is actively exploited. The flaw could expose SD-WAN management assets; fixed releases are available.