cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · bleepingcomputer.com

Rapid7 SharePoint Exploit Reportedly Used Against Honeypots

Rapid7 published a PoC for SharePoint flaw CVE-2026-55040; Defused reported its use against honeypots, though Microsoft has not flagged it as successfully exploited in the wild. Microsoft patched it, and CISA urged SharePoint hardening.
Aug 12, 2026
Vulnerability & Exploit · securityweek.com

Ivanti Patches Four Vulnerabilities in EPM and Neurons for MDM

Ivanti patched four vulnerabilities in EPM and Neurons for MDM. The flaws include remotely exploitable issues; Ivanti said it was unaware of customer exploitation at disclosure. EPM fixes are in version 2024 SU7, and MDM’s flaw was patched in R124.

Aug 12, 2026
Vulnerability & Exploit · securityweek.com

Cisco Patches Actively Exploited Firewall Zero-Day That Can Cause DoS

Cisco released hotfixes for actively exploited CVE-2026-20349, which lets unauthenticated attackers trigger a denial-of-service condition on Secure Firewall ASA and FTD appliances via a crafted HTTP request to the Remote Access SSL VPN service.

Aug 12, 2026
Vulnerability & Exploit · thehackernews.com

Zoom Patched Three Annotation Flaws That Could Enable Meeting-Client Takeover

Researchers say three Zoom annotation flaws could let meeting participants take over other attendees’ clients without interaction. Zoom patched them in June and July; no exploitation had been reported. The company and researchers differ on severity and impact.

Aug 12, 2026
Vulnerability & Exploit · bleepingcomputer.com

Cisco Says CVE-2026-20349 VPN Flaw Is Being Exploited to Crash Firewalls

Cisco says attackers are exploiting CVE-2026-20349 to remotely crash certain Secure Firewall ASA and FTD devices. No workaround exists; Cisco has released hot fixes and recommends upgrading.

Aug 11, 2026
Vulnerability & Exploit · securityweek.com

Adobe Urges Immediate Patching for Critical ColdFusion and Campaign Classic Flaws

Adobe patched more than 50 vulnerabilities, including critical ColdFusion and Campaign Classic flaws that could enable code execution. It says it is unaware of exploitation in the wild and urges immediate patching of those products.

Aug 11, 2026
Vulnerability & Exploit · securityweek.com

Zoom Patches Zero-Click RCE and Three Other Vulnerabilities

Zoom patched four vulnerabilities, including CVE-2026-53413, which A Security says could enable zero-click remote code execution through the annotator protocol. The flaws affected Zoom clients and VDI products.

Aug 11, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Says Ransomware Gangs Exploit SharePoint RCE Flaw CVE-2026-45659

CISA says ransomware gangs are exploiting CVE-2026-45659, a low-privilege SharePoint RCE flaw; over 200 internet-exposed servers remain unpatched. CISA urges patching, verification and monitoring.

Aug 11, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Flags Two SonicWall SMA1000 Flaws as Exploited by Ransomware Gangs

CISA says ransomware gangs are exploiting patched SonicWall SMA1000 flaws CVE-2026-15409 and CVE-2026-15410. Volexity linked earlier zero-day exploitation to UTA0533, which deployed four malware families.

Aug 10, 2026
Vulnerability & Exploit · securityweek.com

Cisco Warns of Seven ClamAV Flaws Affecting Secure Endpoint; Two Have Public PoCs

Cisco says seven ClamAV vulnerabilities affect Secure Endpoint Connector products on Windows, macOS, and Linux; two have public PoC code. ClamAV 1.5.4 includes fixes, and Cisco says it has no evidence of in-the-wild exploitation.

Aug 10, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Warns of Actively Exploited Progress Kemp LoadMaster Flaw

CISA says attackers are exploiting CVE-2026-8037, an unauthenticated command-injection flaw affecting Progress Kemp LoadMaster and MOVEit WAF. Progress released patches, and CISA ordered U.S. federal agencies to remediate within three days.

Aug 10, 2026
Vulnerability & Exploit · thehackernews.com

Metabase Zero-Day Exploited to Give Attackers Unauthenticated Admin Access

Metabase says a CVSS 10.0 zero-day enabled unauthenticated SQL injection and admin access. Cloud instances were updated; self-hosted users should patch and review logs. Framework reported customer contact data was accessed.

Aug 10, 2026
Vulnerability & Exploit · securityweek.com

Belgian eID Software Flaws Could Enable PIN Theft and Remote Code Execution

Researchers found flaws in Connective eID software that could expose eID and payment-card details, steal PINs to forge signatures, and enable user-level code execution. Nitro says the flaws are fixed and it found no evidence of exploitation.

Aug 10, 2026
Vulnerability & Exploit · resecurity.com

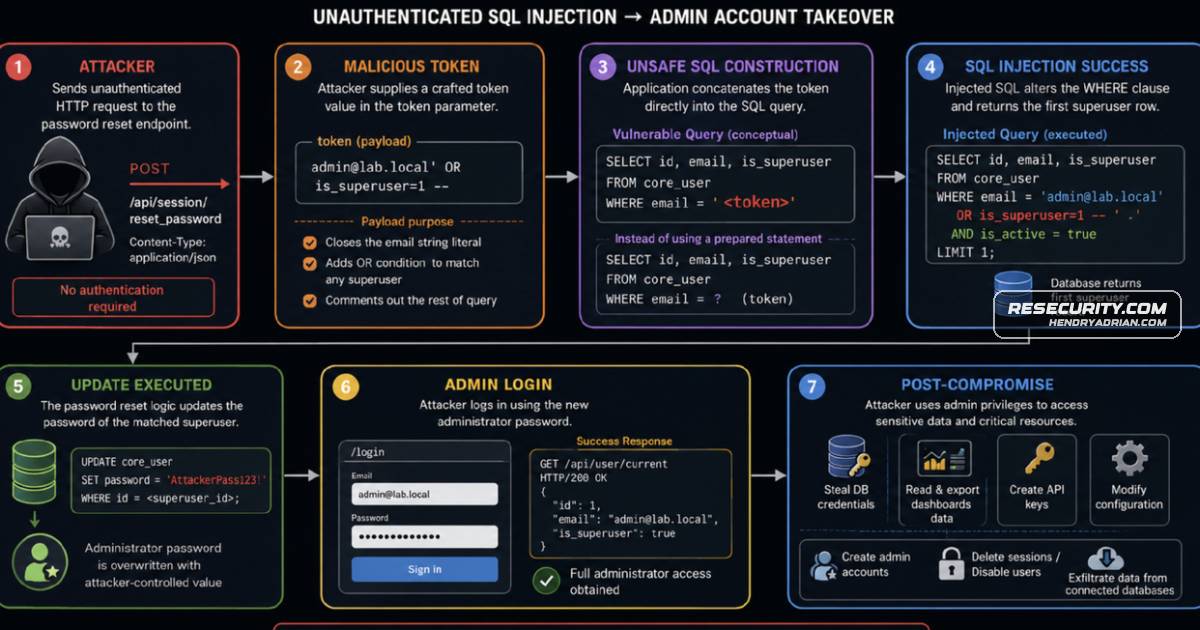
Metabase Zero-Day SQL Injection Enables Unauthenticated Admin Access

Metabase says attackers exploited GHSA-vwf4-m7j8-wcjf, an unauthenticated SQL injection in password reset that can grant admin access. Self-hosted versions need patching; Framework reported unauthorized access to customer information.

Aug 10, 2026
Vulnerability & Exploit · cert-agid.gov.it

WordPress XSS2Shell Flaw Can Lead to PHP Code Execution

CERT-AGID reports that CVE-2026-64638, a pre-auth reflected XSS in WordPress login pages, can be chained to PHP execution if an authenticated admin is socially engineered to interact. Patches are available; CERT-AGID knows of no public evidence of exploitation.

Aug 8, 2026
Vulnerability & Exploit · thehackernews.com

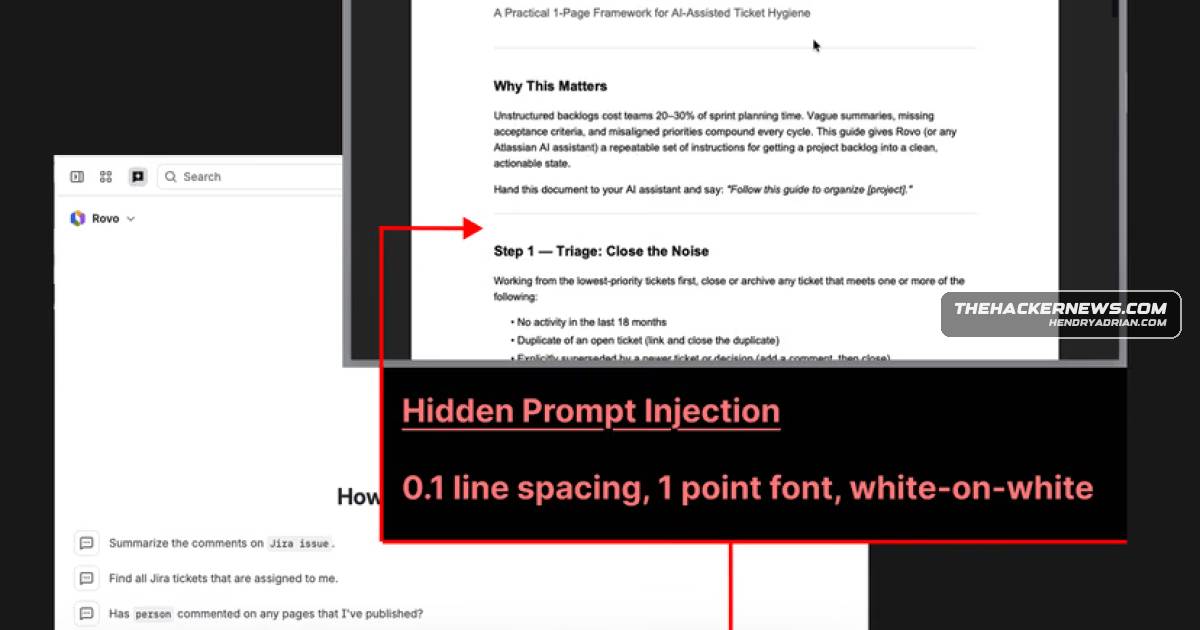
Two Rovo Prompt-Injection Paths Could Expose Jira and Confluence Data; One Fixed

Two firms reported ways to make Atlassian Rovo send a signed-in user's accessible Jira or Confluence data to an attacker. Atlassian fixed Varonis' RovoBlast link flaw; PromptArmor's content-borne path remained unconfirmed after its August 5 report.

Aug 8, 2026
Vulnerability & Exploit · bleepingcomputer.com

Metabase Zero-Day SQL Injection Used in Customer Data-Theft Attacks

Metabase confirmed active exploitation of a critical unauthenticated SQL injection flaw. Framework confirmed customer data theft; Tally reported exposed emails and password hashes, while LexisNexis said exposure remains unclear. Patches and mitigations are available.

Aug 7, 2026
Vulnerability & Exploit · huntress.com

Apple Patches Pre-Authentication macOS Screen Sharing Flaw Enabling Root Access

CVE-2026-65400 lets attackers exploit macOS Screen Sharing for pre-authentication root file access and remote code execution. Apple patched supported versions on August 6, 2026; disable Screen Sharing if you cannot update.

Aug 7, 2026
Vulnerability & Exploit · thehackernews.com

Interrupt Injection Can Bypass Linux Spectre v2 Defenses on AMD CPUs

Researchers demonstrated INTERRUPT INJECTION can exploit interrupt timing gaps in Linux Spectre v2 defenses to leak kernel memory on AMD Zen 2 with local unprivileged execution. AMD lists Zen 1–4 as affected; a Linux fix is available. Intel end-to-end leakage was not

Aug 6, 2026
Vulnerability & Exploit · thehackernews.com

Cisco Patches 12 SD-WAN and IOS XE Flaws, Fixes IMC Bugs, Warns of FMC Exploitation

Cisco patched 12 Catalyst SD-WAN and IOS XE flaws, plus two IMC issues, one with a known proof-of-concept. The flaws were not known to be exploited; Cisco separately warned of active exploitation of an FMC vulnerability.

Aug 6, 2026
Vulnerability & Exploit · thehackernews.com

Zapscape KVM Flaw Could Let Guest Root Escape to Linux Host

CVE-2026-64561 (“Zapscape”) is a KVM/x86 shadow-MMU flaw that may let a guest-root attacker escape an L1 VM when nested virtualization is exposed. The upstream fix is merged; the disclosure does not report in-the-wild exploitation.

Aug 6, 2026
Vulnerability & Exploit · securityweek.com

Paperclip Authorization Flaw Could Enable Server-Side Code Execution

CVE-2026-41679, a critical Paperclip authorization bypass, could let attackers on network-accessible instances with default authenticated-mode settings reach code execution as the server process. Paperclip fixed the flaw and two other bugs.

Aug 6, 2026
Vulnerability & Exploit · securityweek.com

Cisco Patches Critical Vulnerabilities in SD-WAN, IOS XE, and FMC

Cisco patched vulnerabilities across its products, including critical flaws in Catalyst SD-WAN, IOS XE, and FMC. An FMC authentication bypass could enable remote root access; Cisco says it is unaware of in-the-wild exploitation.

Aug 6, 2026
Vulnerability & Exploit · securityweek.com

CISA Flags Exploitation of Critical JetBrains TeamCity Flaw

CISA added critical TeamCity vulnerability CVE-2026-63077 to its Known Exploited Vulnerabilities catalog. The flaw enables unauthenticated remote code execution; patches are available, but public details about attacks are lacking.

Aug 6, 2026
PreviousPage 37 of 65 Next
© 2026 cyber.hendryadrian.com