
Critical Rails Active Storage Flaw Enables Unauthenticated File Reads
Summary
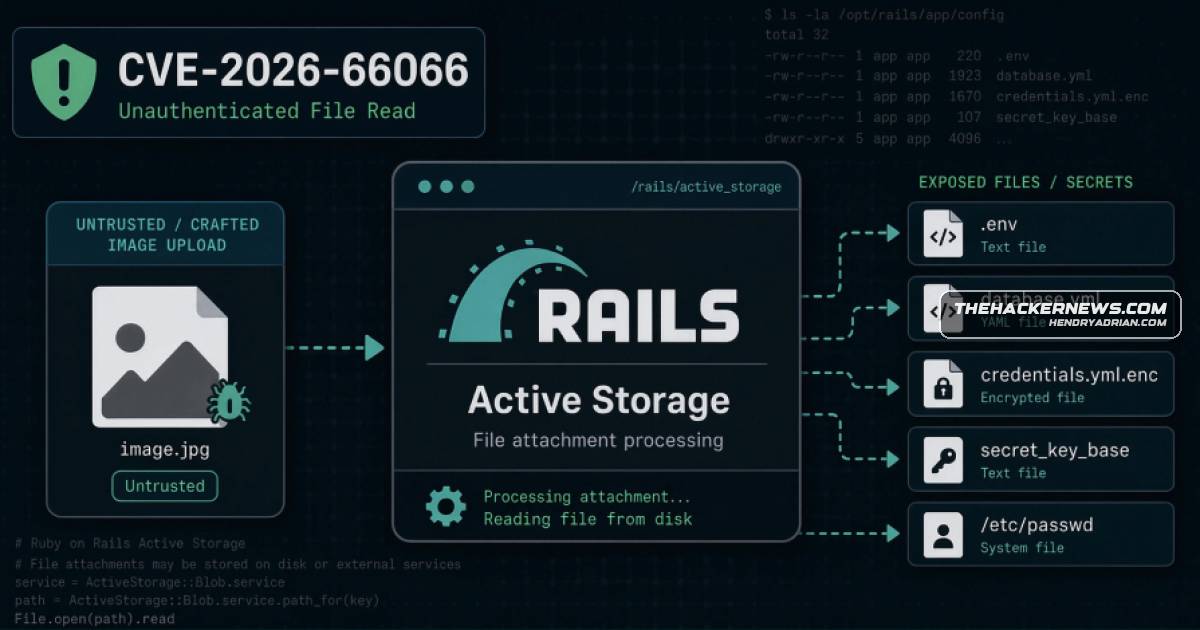
CVE-2026-66066 can let unauthenticated attackers read files through crafted image uploads to affected Rails Active Storage apps using libvips. Rails released fixes; operators should upgrade and rotate accessible secrets. No in-the-wild exploitation was reported.
Key points
- CVE-2026-66066 affects Rails Active Storage applications that use libvips to process untrusted image uploads.
- A crafted upload can invoke unsafe libvips operations and disclose files readable by the Rails worker, including application secrets and credentials.
- The article assesses that exposed credentials could enable further access or RCE, depending on what the credentials permit.
- Fixed versions are Rails 7.2.3.2, 8.0.5.1, and 8.1.3.1; Rails 7.0 and 7.1 users must upgrade to a supported fixed branch.
- Operators should rotate secrets accessible to the application and ensure libvips 8.13 or later and, when installed, ruby-vips 2.2.1 or later.
- A temporary mitigation is to block untrusted libvips operations; earlier libvips versions cannot use this mitigation.
- As of July 29, 2026, no proof of concept or in-the-wild exploitation had been reported in the article.
Article Details
- Vulnerability Types
- Arbitrary file read
- Severity
- Critical (CVSS 9.5)
- Affected Versions
- Ruby on Rails 7.0.0 through 7.2.3.1
- Ruby on Rails 8.0.0 through 8.0.5
- Ruby on Rails 8.1.0 through 8.1.3
- Ruby on Rails 6.0.0 through 6.1.7.10 when Active Storage is configured to use Vips
- Exploitation Status
- not_reported
- Exploit Availability
- none_reported
- Patch Status
- available
- Workarounds
- With libvips 8.13 or later, set VIPS_BLOCK_UNTRUSTED.
- With ruby-vips 2.2.1 or later, call Vips.block_untrusted(true).
- If unable to upgrade Rails immediately, upgrade libvips or remove it from the application.
MITRE ATT&CK
T1005 · Data from Local SystemSuccessful exploitation could provide an arbitrary file-read primitive for files readable by the Rails worker.T1190 · Exploit Public-Facing ApplicationThe flaw could let unauthenticated attackers exploit a Rails application through crafted image uploads accepted by Active Storage.
CVE
People
André BaptistaCredited by Rails as one of the Ethiack researchers who independently reported the vulnerability.Bruno MendesCredited by Rails as one of the Ethiack researchers who independently reported the vulnerability.Rafael CastilhoCredited by Rails as one of the Ethiack researchers who independently reported the vulnerability.RyotaKCredited by Rails as a GMO Flatt Security researcher who independently reported the vulnerability.
Products
Active StorageRuby on Rails has fixed CVE-2026-66066, a critical Active Storage flaw that could let unauthenticated attackers read arbitrary files through crafted image uploads when libvips is used.libvipsRuby on Rails has fixed CVE-2026-66066, a critical Active Storage flaw that could let unauthenticated attackers read arbitrary files through crafted image uploads when libvips is used.Ruby on RailsRuby on Rails has fixed CVE-2026-66066, a critical Active Storage flaw that could let unauthenticated attackers read arbitrary files through crafted image uploads when libvips is used.ruby-vipsPatched installations require libvips 8.13 or later and, when ruby-vips is installed, ruby-vips 2.2.1 or later.