
CVE-2026-16812: Critical Unauthenticated Command Injection in VeloCloud Orchestrator
Summary
Arista says CVE-2026-16812, an unauthenticated OS command injection in on-premises VeloCloud Orchestrator, is actively exploited. The flaw could expose SD-WAN management assets; fixed releases are available.
Key points
- The flaw allows unauthenticated remote OS command execution on affected on-premises VeloCloud Orchestrator (VCO) deployments.
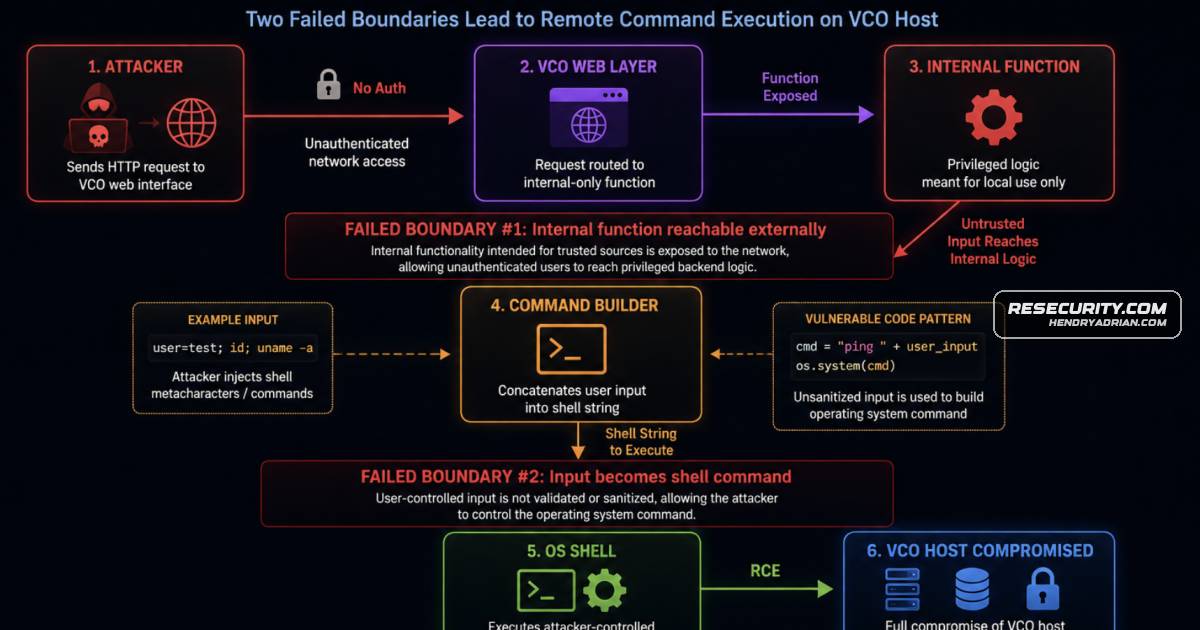
- The article attributes the issue to an internal backend function being reachable through the web interface and attacker-controlled input reaching OS command execution.
- Affected release trains should be upgraded to 5.2.3.14, 6.1.3.4, 6.4.2.4, or 7.0.0.1, as applicable. Hosted/dedicated VCO, Gateway, and Edge deployments are reported as not directly affected.
- Arista is reported to have confirmed active exploitation; CISA added the CVE to its KEV Catalog on July 27, 2026, with a July 30 remediation deadline for affected federal agencies.
- The article says some observed network hosts remained vulnerable as of August 7, 2026.
- The article provides a local simulated lab and conceptual examples, while noting that the actual vulnerable endpoint and payload have not been released.
- Recommended response includes patching, investigating logs and host activity, reviewing managed Edge configurations, and rotating sensitive credentials and certificates if compromise is suspected.
Article Details
- Vulnerability Types
- Unauthenticated OS command injection (CWE-78)
- Exposure of a privileged internal backend function through the VCO web interface
- Severity
- Critical; CVSS 10.0 under CVSS v3.1 and CVSS v4.0
- Affected Versions
- On-premises VeloCloud Orchestrator (VCO) 5.2.x before 5.2.3.14
- On-premises VeloCloud Orchestrator (VCO) 6.1.x before 6.1.3.4
- On-premises VeloCloud Orchestrator (VCO) 6.4.x before 6.4.2.4
- On-premises VeloCloud Orchestrator (VCO) 7.0.x before 7.0.0.1
- Exploitation Status
- active
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Restrict access to the Orchestrator management interface with firewalls, VPNs, IP allowlists, or dedicated management networks; avoid exposing it directly to the public Internet.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 206[.]72[.]242[.]124 | Listed in the article as an attacker IP address; the article recommends investigating historical connections and considering blocking it. |
| IPV4 | 206[.]72[.]242[.]162 | Listed in the article as an attacker IP address; the article recommends investigating historical connections and considering blocking it. |
| IPV4 | 8[.]19[.]75[.]217 | Listed in the article as an attacker IP address; the article recommends investigating historical connections and considering blocking it. |
MITRE ATT&CK
T1059.004 · Unix ShellThe article's conceptual and lab examples show injected input being interpreted by a shell to execute operating system commands; it notes that the real VCO endpoint and payload were not disclosed.T1190 · Exploit Public-Facing ApplicationThe described attack sends a crafted HTTP request to the VCO web interface to reach a privileged backend function exposed to unauthenticated network requests.