
Azure Cosmos DB Flaw Could Have Exposed Cross-Tenant Account Keys
Summary
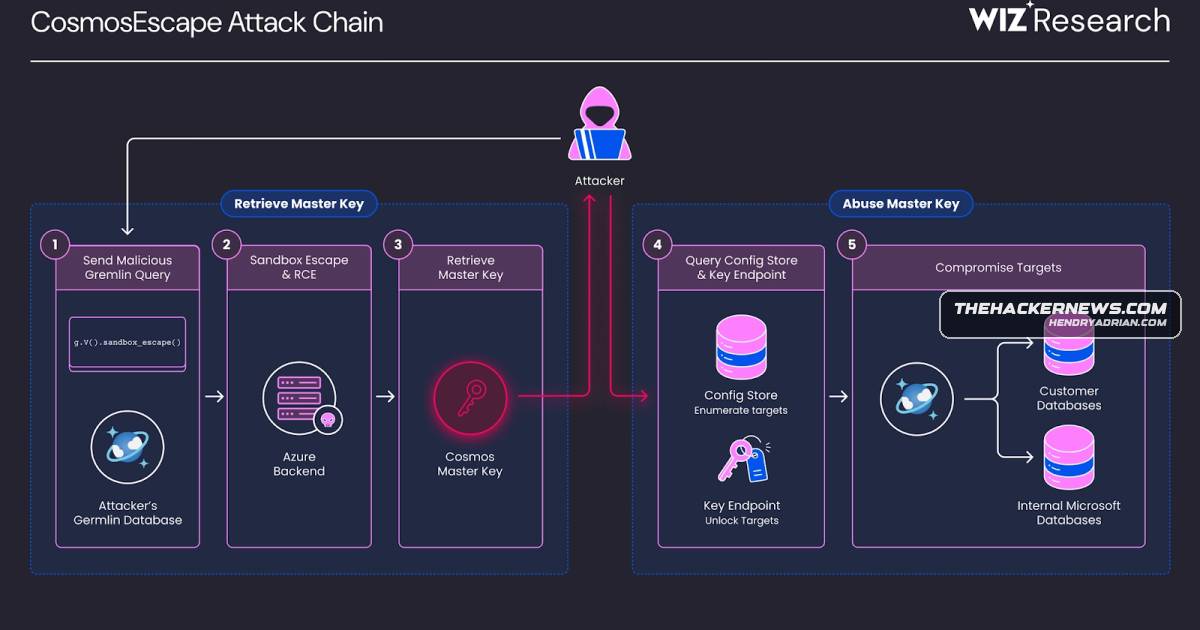
Wiz said CosmosEscape could escape Azure Cosmos DB’s Gremlin sandbox and expose account keys across tenants. Microsoft says it patched the flaw, removed the shared signing key and found no evidence of customer impact or unauthorized activity.
Key points
- Wiz said a crafted query against an attacker-controlled Gremlin database could escape the query sandbox.
- The researchers said .NET reflection enabled file-read and file-write primitives, leading to code execution on a multi-tenant gateway.
- Wiz said the gateway's signing key and regional account directory could help retrieve primary keys for accounts across tenants and regions.
- Microsoft blocked the vulnerable entry point within 48 hours of Wiz's November 2025 report and later removed the shared key across all regions.
- Microsoft said it found no evidence of customer impact or unauthorized activity outside the researchers' testing; no customer action is required.
- Wiz did not publish the full crafted query or clarify all exploit prerequisites, and the duration of potential exposure is unknown.
Article Details
- Vulnerability Types
- Gremlin query sandbox escape
- Arbitrary code execution
- Exploitation Status
- not_reported
- Exploit Availability
- none_reported
- Patch Status
- available
MITRE ATT&CK
Vendors
Products
Azure Cosmos DBA now-patched flaw in Azure Cosmos DB could have let an attacker break out of the Gremlin query sandbox and gain cross-tenant read and write access through a chain Wiz named CosmosEscape.Azure Service FabricThe code execution landed on a component Wiz calls the DB Gateway, which executes customer queries on multi-tenant Azure Service Fabric clusters.