
Coldcard Firmware Flaw Linked to $70.2 Million Bitcoin Theft in 41 Minutes
Summary
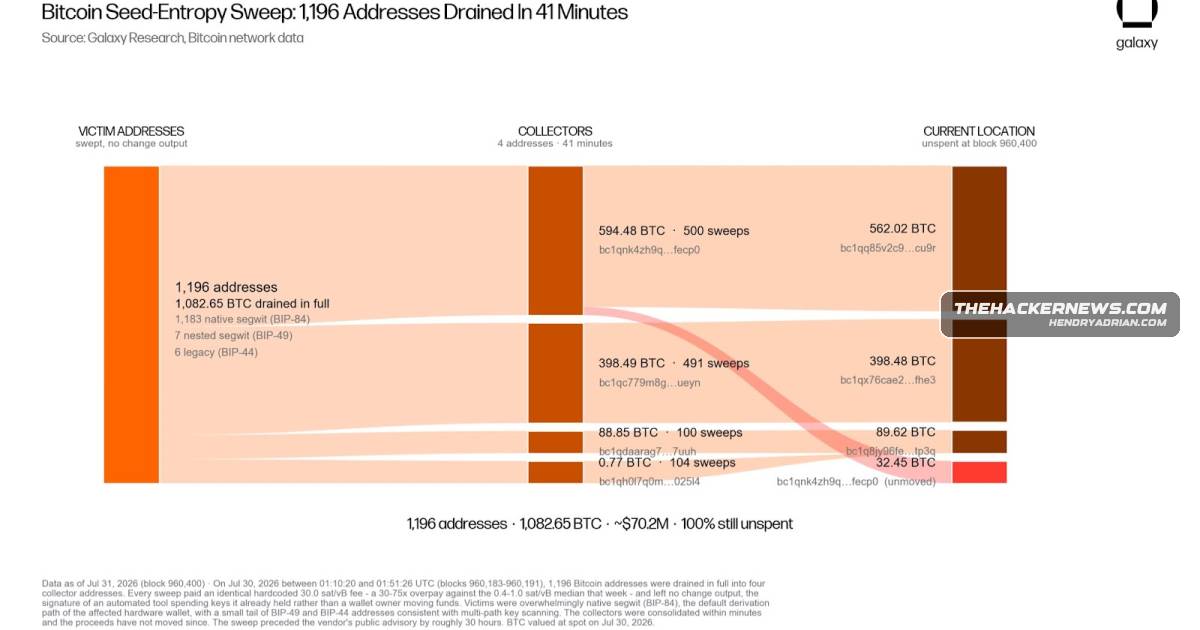
Researchers linked the July 30 theft of 1,082.65 BTC from 1,196 addresses to a Coldcard firmware bug that used a deterministic PRNG for seed generation. Coinkite issued fixes, but owners must replace exposed seeds and move funds.
Key points
- An attacker drained 1,196 Bitcoin addresses in 41 minutes on July 30, taking 1,082.65 BTC worth about $70.2 million at the time.
- Galaxy Research and Block linked the sweep to a Coldcard firmware bug that routed seed generation to a deterministic software PRNG instead of the hardware RNG.
- Block said constrained device identifiers and state could let an attacker reproduce candidate seeds offline and check derived addresses against public blockchain data.
- Coinkite issued emergency firmware on July 31, but updating firmware does not repair an existing seed; owners with exposed seeds should generate new ones and move their funds.
- Exposure depends on the firmware used when a seed was created. Block identified affected older releases across Mk2, Mk3, Mk4, Mk5 and Q models; Coinkite’s listed fixes include Mk3 4.2.0, Mk4/Mk5 5.6.0 and Q 1.5.0Q.
- No attacker has been identified, and no public report has reconstructed a victim’s seed and matched it to a drained address.
Article Details
- Vulnerability Types
- Deterministic pseudorandom number generation caused insufficient entropy in seed generation, potentially enabling offline seed reconstruction
- Affected Versions
- Coldcard Mk2 firmware 4.0.0–4.1.9 (Block's assessment; Coinkite did not name Mk2)
- Coldcard Mk3 firmware 4.0.0–4.1.9 (Block's assessment; Coinkite lists 4.0.1–4.1.9); fixed in 4.2.0
- Coldcard Mk4 and Mk5 firmware before 5.6.0
- Coldcard Q firmware before 1.5.0Q
- Coldcard Mk4 and Mk5 Edge builds before 6.6.0X
- Coldcard Q Edge builds before 6.6.0QX
- Exploitation Status
- reported
- Exploit Availability
- unknown
- Patch Status
- available
- Workarounds
- Install the emergency firmware; seeds created on affected firmware must also be replaced.
- Generate a new seed on patched firmware and move funds to it.
- Coinkite says seeds created with at least 50 fair, independent, private dice rolls are not at risk from this bug alone; migrate if the number or privacy of the rolls is uncertain.