cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Vulnerability & Exploit

Concrete vulnerability and exploit disclosures, advisories, tracking, patches, and mitigations.

1553 articles

Vulnerability & Exploit · securityweek.com

Unpatched Fastjson Vulnerability Exploited in Attacks

Researchers report attacks exploiting critical unauthenticated RCE CVE-2026-16723 in Fastjson 1.2.68–1.2.83. No official patch is available; recommended mitigations include migrating to Fastjson 2.x or enabling SafeMode.
Jul 28, 2026
Vulnerability & Exploit · securityweek.com

Arista Patches Critical VeloCloud Orchestrator Flaw It Says Was Exploited as Zero-Day

Arista says CVE-2026-16812, a critical OS injection flaw in on-prem VeloCloud Orchestrator, is actively exploited. The remotely exploitable issue requires no credentials; Arista released patches, and CISA added it to KEV.

Jul 28, 2026
Vulnerability & Exploit · bleepingcomputer.com

Check Point Patches Actively Exploited SmartConsole Authentication Bypass

Check Point addressed actively exploited CVE-2026-16232, which can let unauthenticated attackers obtain administrator access to exposed SmartConsole management servers. CISA added the flaw to its known exploited vulnerabilities catalog and urged prompt patching.

Jul 28, 2026
Vulnerability & Exploit · bleepingcomputer.com

Arista Patches Actively Exploited VeloCloud Orchestrator Zero-Day

Arista patched CVE-2026-16812, a maximum-severity unauthenticated command injection flaw in on-premises VeloCloud Orchestrator. The flaw is actively exploited; affected organizations are urged to update and review systems for compromise.

Jul 28, 2026
Vulnerability & Exploit · bleepingcomputer.com

Hackers Actively Exploit FastJson RCE Vulnerability CVE-2026-16723

ThreatBook and Imperva report active exploitation of CVE-2026-16723 in FastJson 1.2.68–1.2.83. The flaw enables remote code execution in certain Spring Boot deployments; Alibaba has not issued a fix.

Jul 28, 2026
Vulnerability & Exploit · bleepingcomputer.com

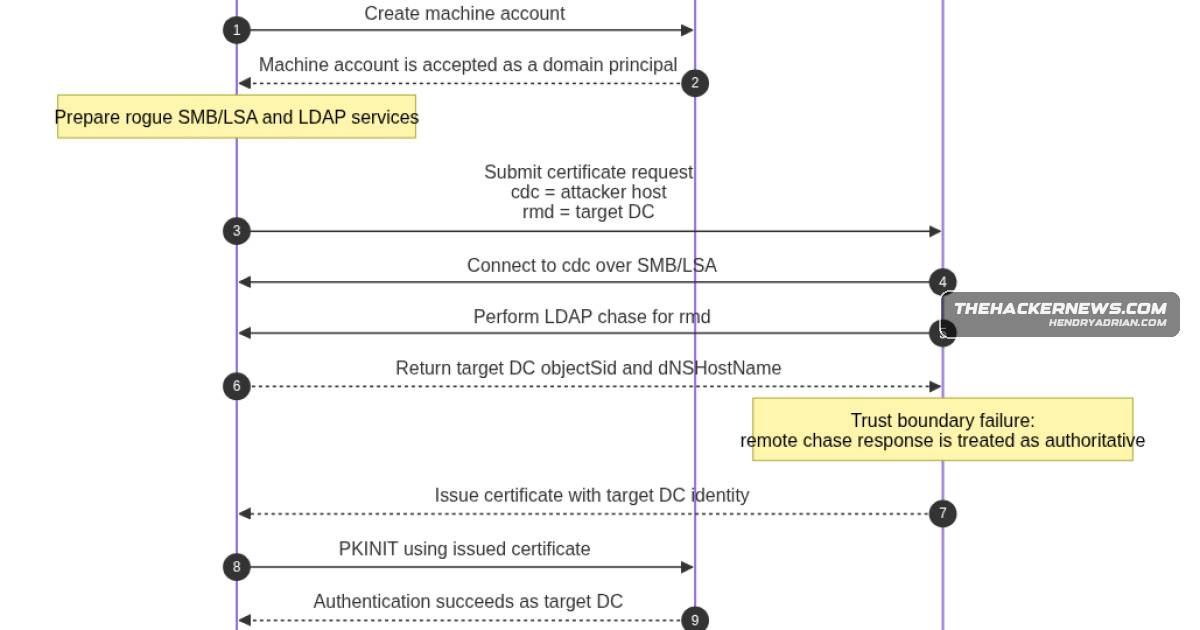
Certighost PoC Shows How CVE-2026-54121 Can Enable Windows Domain Compromise

A proof of concept for the AD CS flaw CVE-2026-54121 demonstrates how an authenticated attacker could impersonate a domain controller. Microsoft patched the flaw in July 2026; researchers describe a temporary workaround.

Jul 27, 2026
Vulnerability & Exploit · thehackernews.com

Public Exploit Details Expose Patched vBulletin Pre-Auth RCE

A July 27 public exploit details CVE-2026-61511, an unauthenticated vBulletin template-engine RCE already patched in affected branches and vBulletin 6.2.2. No in-the-wild attacks were confirmed; exposure remains on unpatched self-hosted forums.

Jul 27, 2026
Vulnerability & Exploit · securityweek.com

PTC Windchill Flaw Exploited in Reported Extortion Campaign

Reports say a Cl0p affiliate exploited unauthenticated RCE CVE-2026-12569 in PTC Windchill and FlexPLM, deploying JSP webshells and exfiltrating data for extortion. The actor attribution remains unconfirmed, and Cl0p has not publicly claimed the campaign.

Jul 27, 2026
Vulnerability & Exploit · thehackernews.com

ThreatBook and Imperva Report Fastjson CVE-2026-16723 Exploitation; No Fastjson 1.x Patch Available

ThreatBook and Imperva reported in-the-wild exploitation of CVE-2026-16723, affecting Fastjson 1.2.68–1.2.83 in certain Spring Boot fat-JAR applications. Alibaba has no fixed Fastjson 1.x release and recommends SafeMode or migration to Fastjson2.

Jul 25, 2026
Vulnerability & Exploit · securityweek.com

Rockwell Patches Four Code-Execution Flaws in Arena Simulation Software

Rockwell patched four high-severity Arena Simulation flaws that could enable code execution when a user opens a malicious file. Versions up to 17.00.00 are affected; version 17.00.01 fixes the issues. No in-the-wild exploitation is reported.

Jul 25, 2026
Vulnerability & Exploit · thehackernews.com

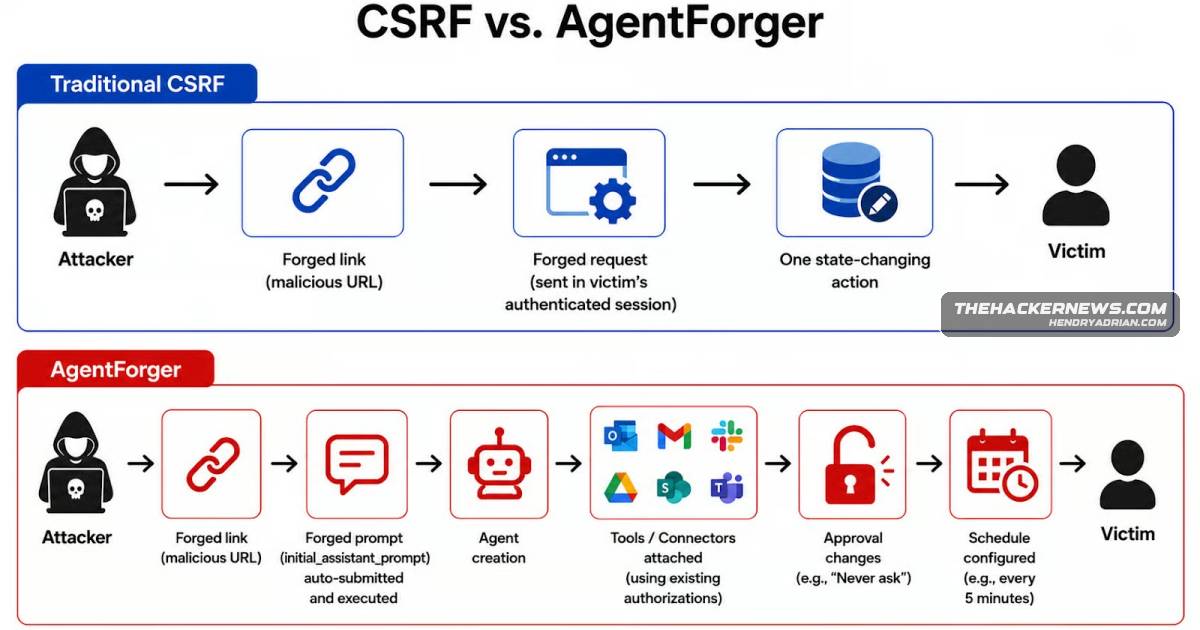
AgentForger Flaw Could Let Phishing Links Deploy Rogue ChatGPT Agents

Zenity Labs reported that AgentForger could let a phishing link create and schedule a rogue ChatGPT Workspace Agent using a victim’s authorized connectors. OpenAI fixed the flaw on June 8, 2026.

Jul 24, 2026
Vulnerability & Exploit · thehackernews.com

Certighost AD CS Flaw Lets Low-Privilege Users Impersonate Domain Controllers

Researchers disclosed Certighost, an AD CS flaw that can let a low-privilege domain user obtain a Domain Controller certificate and perform DCSync. Microsoft patched CVE-2026-54121 on July 14; a public proof of concept followed.

Jul 24, 2026
Vulnerability & Exploit · cyberscoop.com

Officials Say Laundry Bear Used Zimbra Zero-Day to Steal Sensitive Data

A joint advisory says Russian-linked Laundry Bear exploited Zimbra CVE-2025-66376 from July 2025 until its November patch, using a no-click view to steal emails, passwords and 2FA tokens. Unpatched systems remain targeted.

Jul 23, 2026
Vulnerability & Exploit · securityweek.com

OpenAI Fixes AgentForger Flaw That Could Let Attackers Control ChatGPT Workspace Agents

Zenity disclosed AgentForger, a CSRF flaw in ChatGPT Workspace Agents that could let attackers trick a phished, logged-in user into creating an attacker-controlled agent with access to authorized connectors. OpenAI fixed it within three days.

Jul 23, 2026
Vulnerability & Exploit · bleepingcomputer.com

RefluXFS Linux Kernel Flaw Enables Local Root Privilege Escalation

Qualys disclosed RefluXFS (CVE-2026-64600), an XFS reflink race condition affecting Linux kernel 4.11 and later. It can let local attackers overwrite protected files and gain root; kernel patches are available.

Jul 23, 2026
Vulnerability & Exploit · thehackernews.com

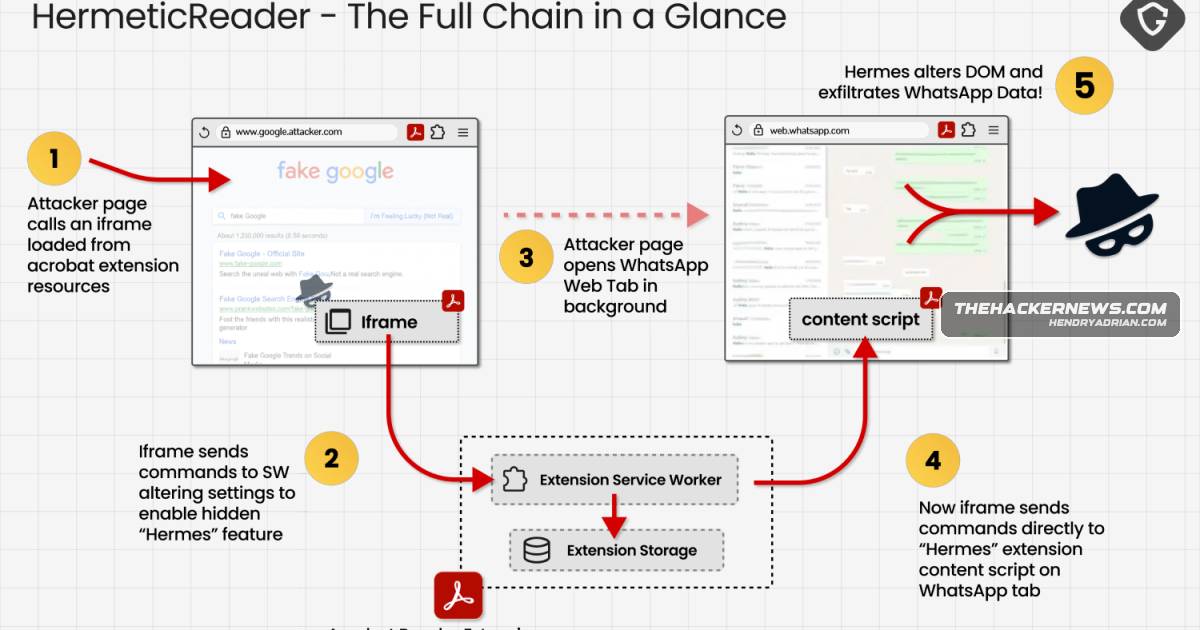
Adobe Acrobat Chrome Extension Flaw Could Expose WhatsApp Web Data

Guardio Labs describes HermeticReader (CVE-2026-48294), a patched Adobe Acrobat Chrome extension flaw affecting versions through 26.5.2.2 that could expose WhatsApp Web data when a user visits a crafted page.

Jul 22, 2026
Vulnerability & Exploit · thehackernews.com

CVE-2026-8933 Could Give Local Users Root on Default Ubuntu Desktop Installs

CVE-2026-8933 is a CVSS 7.8 snap-confine race-condition flaw affecting default Ubuntu Desktop 24.04, 25.10 and 26.04 installs. FUSE and symlink abuse could enable root command execution; apply snapd updates.

Jul 22, 2026
Vulnerability & Exploit · thehackernews.com

VulnCheck Reports Active Exploitation of Windmill File-Read Flaw

VulnCheck reports active exploitation of Windmill CVE-2026-29059, an unauthenticated path-traversal flaw enabling arbitrary file reads. CISA added four exploited flaws to KEV; the article also details WordPress and Langflow attack activity.

Jul 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

Adobe Acrobat Chrome Flaw Could Expose Rendered WhatsApp Web Chats

Guardio says CVE-2026-48294 let a malicious webpage abuse Adobe Acrobat’s Chrome extension to access rendered WhatsApp Web content without authentication. Adobe fixed versions 26.5.2.1 and earlier in 26.5.2.3; Guardio reported no sign of active exploitation.

Jul 22, 2026
Vulnerability & Exploit · securityweek.com

Adobe Acrobat Chrome Extension Flaw Could Expose WhatsApp Data

A flaw in Adobe’s Acrobat Chrome extension could let an attacker who lured a user to a malicious webpage activate a dormant integration and scrape WhatsApp data. Adobe patched the vulnerability, CVE-2026-48294, in June.

Jul 22, 2026
Vulnerability & Exploit · bleepingcomputer.com

CISA Orders Federal Agencies to Patch Actively Exploited Langflow RCE Flaw

CISA ordered U.S. federal agencies to patch CVE-2026-0770 in Langflow by Friday. KEVIntel reported active exploitation attempts, including attempts to deploy malware and access AWS credentials and metadata.

Jul 22, 2026
Vulnerability & Exploit · thehackernews.com

Apple Patches Hide My Email Flaw That Could Expose Real Addresses in Mail Logs

Apple patched a Hide My Email flaw that could expose users’ real addresses in mail logs when messages were rejected as spam. The issue was reported in June 2025; addresses may remain in logs from before the fix.

Jul 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

Attackers Exploit SharePoint Flaw to Steal Machine Keys and Maintain Access

watchTowr and Defused report exploitation of CVE-2026-50522 against on-premises SharePoint. The flaw can expose machine keys for forged authentication tokens; Microsoft patched it in July updates, and watchTowr advises rotating credentials on potentially exposed assets.

Jul 21, 2026
Vulnerability & Exploit · bleepingcomputer.com

WordPress Patches wp2shell Flaws After Webshell Exploitation

Attackers are exploiting WordPress flaws CVE-2026-63030 and CVE-2026-60137 via unauthenticated REST API requests to install webshells and malicious plugins. WordPress patched the flaws; Wiz reported no observed lateral movement or data exfiltration.

Jul 21, 2026
PreviousPage 39 of 65 Next
© 2026 cyber.hendryadrian.com