Huntress Details In-the-Wild Exploitation of Wing FTP Server RCE
Summary
Huntress traced a July 1, 2025, Wing FTP Server RCE exploit on one customer to null-byte/Lua injection and subsequent attacker activity. Microsoft Defender blocked a downloaded beacon; Huntress recommends updating to version 7.4.4.
Key points
- Huntress observed exploitation of CVE-2025-47812 on one customer on July 1, 2025, one day after public disclosure.
- The flaw affects Wing FTP Server versions before 7.4.4; a crafted username with a null byte can enable Lua injection and remote code execution.
- The attack required authentication using valid credentials or, if enabled, an anonymous account; a subsequent request triggered the injected session data.
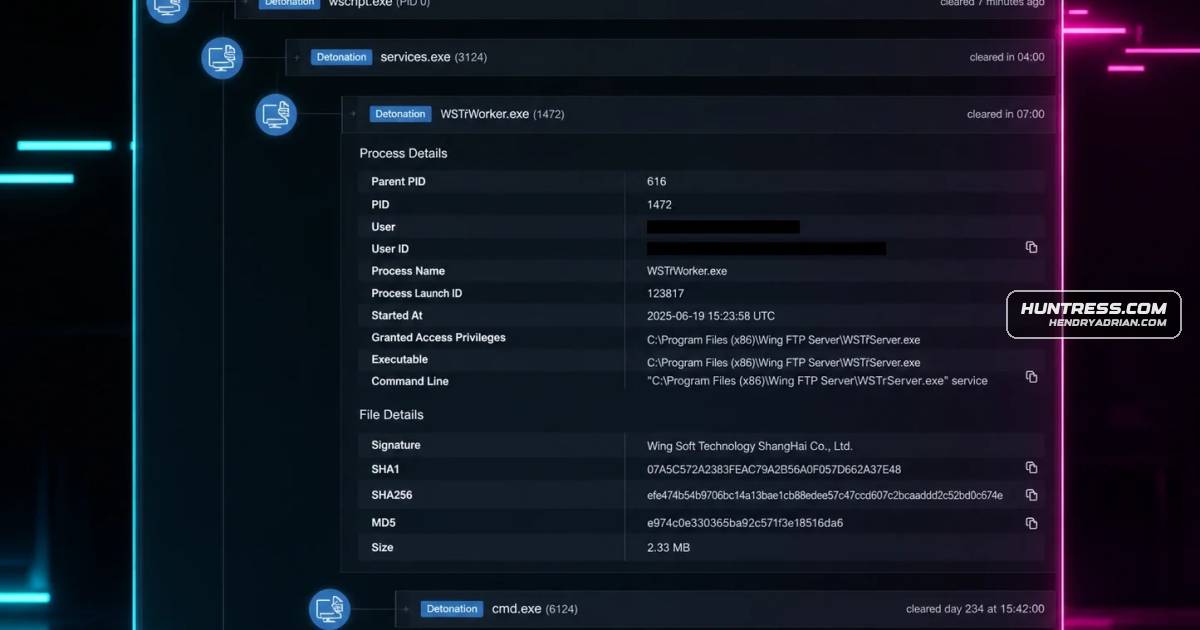
- Huntress identified suspicious Lua session files, truncated login-log entries, and commands showing reconnaissance and attempts to create Windows users for persistence.
- An attacker attempted to download and run a beacon using certutil; Microsoft Defender detected the file as Trojan:Win32/Ceprolad.A, and the server process crashed.
- Attackers also attempted to use ScreenConnect, but Huntress found no evidence it was installed; the machine was isolated shortly afterward.
- Huntress recommends updating Wing FTP Server to version 7.4.4 and identifies session object files as a key source for investigating exploitation.
Article Details
- Attack Vectors
- Attackers exploited CVE-2025-47812 by sending a POST request to Wing FTP Server's loginok.html endpoint with a null byte in the username field, followed by Lua code injected into the session object.
- A subsequent request to another page could trigger the application to deserialize the modified session and execute the injected Lua code.
- After exploitation, an attacker used certutil to attempt to download and run a beacon, created local user accounts, performed host and account reconnaissance, and sent a POST request to a webhook endpoint to track infections.
- An attacker attempted to download a ScreenConnect installer; the article reports no evidence that the installer was run or ScreenConnect installed.
- Defensive Notes
- Update Wing FTP Server to version 7.4.4, the fixed version identified in the article.
- Review Wing FTP Server Domain logs for truncated login entries such as an incomplete User 'anonymous line, while noting that log entries may not retain the authenticating client's IP address.
- Inspect session files in the Wing FTP Server session directory, especially unusually large .lua files with 64-character hexadecimal filenames, for injected Lua functions or encoded commands.
- Correlate Wing FTP Server process activity with command execution, new local accounts, downloads, and Microsoft Defender alerts.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| HOSTNAME | instance-y9tbyl-relay[.]screenconnect[.]com | ScreenConnect callback hostname extracted from the installer recovered from the attacker's download link. |
| IPV4 | 103[.]88[.]141[.]42 | Source-listed IP address of the third attacker attempting to connect to the victim machine. |
| IPV4 | 146[.]70[.]11[.]39 | Source-listed IP address of the fifth attacker observed connecting to the victim machine. |
| IPV4 | 149[.]248[.]44[.]88 | Source-listed IP address of the second attacker attempting to connect to the victim machine. |
| IPV4 | 185[.]196[.]9[.]225 | Source-listed IP address of the fourth attacker; session artifacts associate it with post-exploitation activity. |
| IPV4 | 223[.]160[.]131[.]104 | Source-listed IP address of the first attacker attempting to connect to the victim machine. |
| SHA256 | c637ec00bd22da4539ec6def89cd9f7196a303d17632b1131a89d65e4f5698f4 | SHA-256 hash listed for the beacon that the attacker attempted to download and execute; Microsoft Defender detected the resulting file as Trojan:Win32/Ceprolad.A. |
| SHA256 | f0fcc638cd93bdd6fb4745d75b491395a7a1b2cb08e0153a2eb417cb2f58d8ac | SHA-256 hash of the ScreenConnect installer recovered from the attacker-used download link. |
| URL | hxxps[:]//oooooooo11[.]screenconnect[.]com/bin/screenconnect.clientsetup.msi | Attacker-used URL for downloading a ScreenConnect installer; the article reports no evidence it was run. |
| URL | hxxps[:]//pastebin[.]com/raw/vqq8tr8mg | Specific Pastebin resource referenced in attacker Lua code for an attempted batch-file download; the article says the curl command was malformed. |
| URL | hxxps[:]//webhook[.]site/5d112487-6133-4942-ac87-3f473d44bd81 | Webhook endpoint the attacker used to track infections; Huntress confirmed a successful connection from the victim host. |
MITRE ATT&CK
T1016 · System Network Configuration DiscoveryThe attacker ran ipconfig and arp -a during network reconnaissance.T1027 · Obfuscated Files or InformationThe beacon command was represented as a hex-encoded string inside injected Lua code.T1033 · System Owner/User DiscoveryThe attacker repeatedly ran whoami commands to identify the current user and inspect privileges.T1059.001 · PowerShellThe attacker attempted to launch powershell.exe on the compromised host.T1059.003 · Windows Command ShellAttack commands were executed through cmd.exe, including reconnaissance, account creation, and download commands.T1059.011 · LuaThe vulnerability was used to inject Lua code into session files, which the application later deserialized.T1071.001 · Web ProtocolsThe attacker used curl to send a POST request to a webhook endpoint to track infections.T1087.001 · Local AccountThe attacker used net user commands to enumerate local accounts and inspect the newly created wing account.T1105 · Ingress Tool TransferThe attacker attempted to download a beacon with certutil and also attempted to retrieve a batch file and a ScreenConnect installer.T1136.001 · Local AccountThe attacker used net user commands to create local accounts named wingftp and wing.T1140 · Deobfuscate/Decode Files or InformationInjected Lua code decoded the hex-encoded command before passing it to Windows cmd.exe.T1190 · Exploit Public-Facing ApplicationThe attackers exploited CVE-2025-47812 through Wing FTP Server's loginok.html endpoint.
CVE
People
Malware
Vendors
HuntressTL;DR: Huntress saw active exploitation of Wing FTP Server remote code execution (CVE-2025-47812) on a customer on July 1, 2025.MicrosoftIt seems like the attacker (the fourth one we had seen this day) had a difficult time running some commands, maybe due to their unfamiliarity with them, or because Microsoft Defender stopped part of their attack.
Products
Microsoft Defender Antimalware PlatformIt seems like the attacker (the fourth one we had seen this day) had a difficult time running some commands, maybe due to their unfamiliarity with them, or because Microsoft Defender stopped part of their attack.ScreenConnectAt this point, they opted for installing ScreenConnect, for a better experience that might have made them more successful.Wing FTP ServerWing FTP Server Remote Code Execution (CVE-2025-47812) Exploited in the Wild