cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2499 articles

Threat Research · cloudsek.com

APT36 Uses Fake Viber App to Distribute CapraRAT Android Spyware

Researchers linked APT36 infrastructure to CapraRAT APKs, including one impersonating Viber. The spyware requests permissions that could enable surveillance, message interception, and access to device data.
Jun 3, 2025
Threat Research · wiz.io

JINX-0132 Exploits Exposed DevOps Tools to Deploy XMRig Cryptominers

Wiz researchers describe JINX-0132 exploiting exposed or misconfigured Nomad, Consul, Docker API, and Gitea instances to run XMRig miners, and outline exposure findings and defenses.

Jun 2, 2025
Threat Research · blog.talosintelligence.com

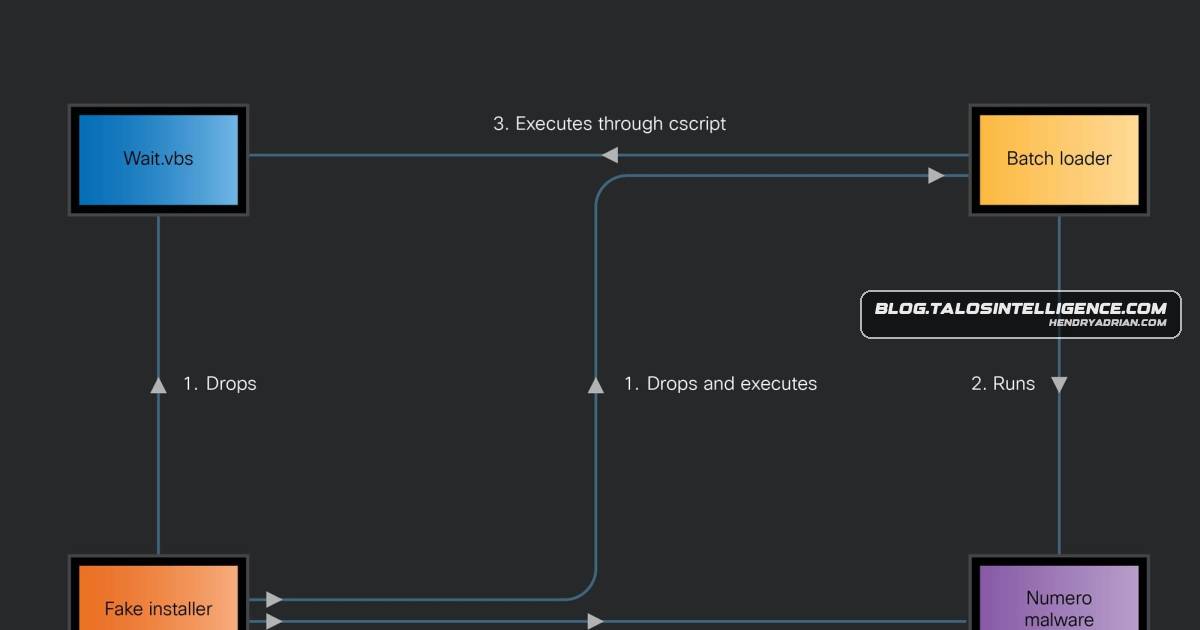
Fake AI Installers Deliver CyberLock and Lucky_Gh0$t Ransomware, Destructive Numero Malware

Cisco Talos details three threats disguised as AI tool installers: CyberLock and Lucky_Gh0$t ransomware, and Numero, which disrupts Windows interfaces. The installers spread through fake sites, search results, and a malicious ChatGPT-themed package.

May 29, 2025
Threat Research · huntress.com

Huntress Details Intrusion Targeting Executive at Market Research Company

Huntress describes a 2025 intrusion at a market research company, with reconnaissance and credential-related registry changes on a server followed by a Mesh Agent loader on an executive’s workstation. Huntress suspects state-aligned espionage actors.

May 27, 2025
Threat Research · cloudsek.com

Unauthenticated LFI Exposed Files and Credentials on a Travel Company’s Server

CloudSEK says its BeVigil scanner found unauthenticated LFI endpoints on a travel-industry subdomain that could expose server files, source code, credentials, and configuration data.

May 23, 2025
Threat Research · team-cymru.com

Researchers Detail DanaBot’s Multi-Tier Command Infrastructure

Team Cymru and Black Lotus Labs map DanaBot’s multi-tier C2 and management infrastructure, reporting more than 150 active C2 servers on average and Russian-linked backend systems. The article also describes the Operation Endgame II takedown.

May 22, 2025
Threat Research · wiz.io

Wiz Details Active Exploitation of Ivanti EPMM Vulnerability Chain

Wiz reports active exploitation of Ivanti EPMM vulnerabilities CVE-2025-4427 and CVE-2025-4428, detailing Sliver payloads, database dumping, web shells and reverse shells. Ivanti patches are available.

May 20, 2025
Threat Research · hunt.io

Shared SSH Keys Link Phishing Infrastructure Targeting Kuwait and Gulf Businesses

Hunt.io researchers link more than 230 domains impersonating Gulf-region businesses to shared SSH keys and hosting patterns. The ongoing campaign uses cloned sites, including mobile payment lures targeting Zain customers.

May 15, 2025
Threat Research · cloudsek.com

CloudSek Finds Hacktivist Claims Against India Overstated, Details APT36’s Crimson RAT Campaign

CloudSek says many hacktivist claims against Indian targets were exaggerated or unsupported, while detailing APT36’s phishing campaign using Crimson RAT to target government and defense networks.

May 11, 2025
Threat Research · huntress.com

Huntress Details Post-Exploitation Activity Targeting Samsung MagicINFO 9

Huntress observed three incidents involving exploitation of Samsung MagicINFO 9. Attackers attempted to install services using downloaded executables; one host showed execution evidence. Huntress advises keeping servers off the internet until a patch is available.

May 9, 2025
Threat Research · bitdefender.com

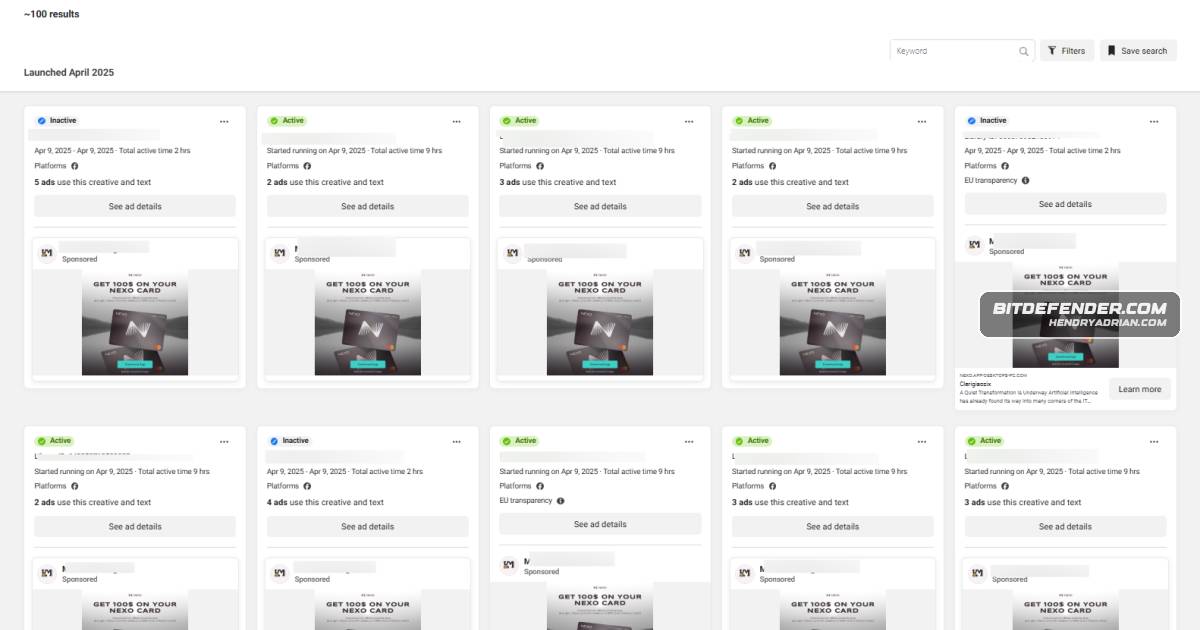
Facebook Ads Spread Evasive Malware Impersonating Cryptocurrency Platforms

Bitdefender details an active malvertising campaign using cryptocurrency-brand impersonation and targeted Facebook ads to deliver malware. Its scripts coordinate with a local service to run payloads and collect system data while evading analysis.

May 8, 2025
Threat Research · huntress.com

Huntress Finds Attackers Reused Tactics in CrushFTP and CentreStack Intrusions

Huntress compared intrusions exploiting CrushFTP and CentreStack/Triofox, finding shared infrastructure and tools despite different file-transfer methods. In some incidents, security tools detected and quarantined files before further activity.

May 6, 2025
Threat Research · hunt.io

ClickFix Campaign Spoofs India’s Defence Ministry to Target Windows and Linux Users

Researchers detail a campaign using a cloned Indian Defence Ministry portal and clipboard-based commands to deliver malware on Windows and Linux. The Windows payload uses mshta.exe; the observed Linux script only opens an image.

May 5, 2025
Threat Research · darktrace.com

SocGholish Campaigns Use WebDAV and SCF Files to Steal Credentials Before RansomHub Deployment

Darktrace details SocGholish infections leading to RansomHub activity, including fake browser updates, WebDAV and SCF-based forced authentication to expose NTLM hashes, Python backdoors, and port-hopping C2.

May 1, 2025
Threat Research · aquasec.com

Overly Broad AWS Default Roles Could Enable Cross-Service Privilege Escalation

Aqua researchers found that overly permissive default IAM roles in AWS services and the Ray framework could let attackers misuse S3 access to tamper with other services and potentially escalate privileges. AWS changed several policies and guidance.

Apr 29, 2025
Threat Research · volexity.com

Russian Actors Abuse Microsoft 365 OAuth Workflows to Phish Accounts

Volexity describes campaigns by suspected Russian actors UTA0352 and UTA0355 that use targeted social engineering and legitimate Microsoft OAuth workflows to steal authorization codes and access victims’ Microsoft 365 accounts.

Apr 22, 2025
Threat Research · hunt.io

Researchers Map Dormant Infrastructure Resembling APT34 Tradecraft

An investigation links staged domains and M247 servers to APT34-like infrastructure through shared SSH keys, fabricated company websites, and a port 8080 404 response pattern, offering indicators defenders can monitor before activity begins.

Apr 22, 2025
Threat Research · huntress.com

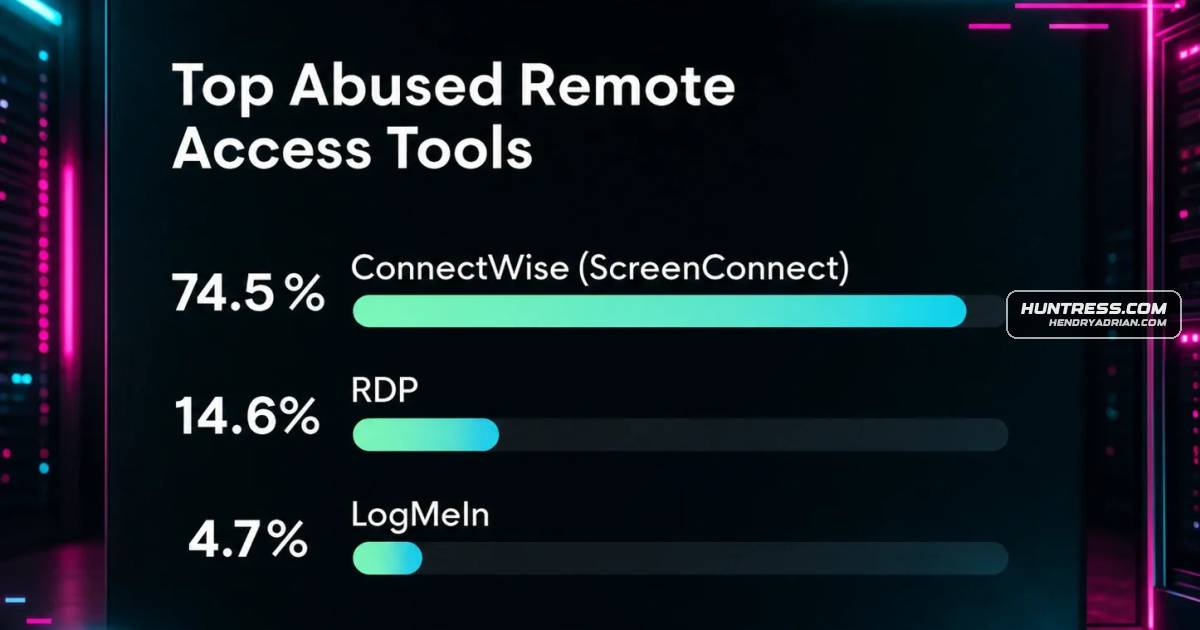
Huntress Details Attacks Using Multiple RMM Tools, Including Akira Ransomware Deployment

Huntress reconstructs two incidents involving abused or attacker-installed RMM tools, including one ending in Akira ransomware. It recommends asset inventory, attack-surface reduction, and endpoint monitoring.

Apr 17, 2025
Threat Research · hunt.io

Exposed Server Reveals RedGolf-Linked Fortinet Exploits and Shiseido Reconnaissance

A briefly exposed server linked to KeyPlug and RedGolf/APT41 contained Fortinet exploit scripts, a PHP webshell, reverse-shell tools, and reconnaissance files listing Shiseido-related domains and authentication portals.

Apr 17, 2025
Threat Research · cloudsek.com

Fake PDF Converters Deliver Arechclient2 Information Stealer

Researchers analyzed fake PDF-to-DOCX sites impersonating pdfcandy[.]com that trick users into running PowerShell, delivering Arechclient2/SectopRAT. The report details the redirect chain, Windows execution stages, IOCs and defenses.

Apr 15, 2025
Threat Research · hunt.io

Phishing Kit Shifts Credential and OTP Validation Server-Side to Evade Analysis

Researchers identified phishing pages impersonating employee and member portals that steal credentials and OTPs. The PHP-based kit uses server-side validation, while related domains and hosting infrastructure provide indicators for defenders to investigate.

Apr 15, 2025
Threat Research · huntress.com

Huntress Traces RDP Brute Force to Suspected Ransomware Infrastructure

Huntress traced a successful RDP brute-force intrusion, credential-file searching and domain enumeration to infrastructure it suspects is linked to ransomware operators and initial access brokers.

Apr 10, 2025
Threat Research · hunt.io

GoPhish Infrastructure Linked to Domains Spoofing Polish Energy and Government Organizations

Hunt.io identified a GoPhish server linked to domains impersonating Polish energy and government organizations, as well as other brands. No phishing content was active during review, but the infrastructure appeared maintained for possible credential collection.

Apr 10, 2025
Threat Research · hunt.io

Hunt.io Details Gamaredon DNS Patterns and ShadowPad-Linked Infrastructure

Hunt.io researchers describe Gamaredon’s short-TTL, rotating DNS infrastructure and a separate server cluster linked to a ShadowPad backdoor, detailing its delivery chain, shared certificate clues, and indicators of compromise.

Apr 8, 2025
PreviousPage 92 of 105 Next
© 2026 cyber.hendryadrian.com