
SEO Poisoning Campaign Abuses .gov.br Subdomains to Generate More Than 630,000 URLs
Summary
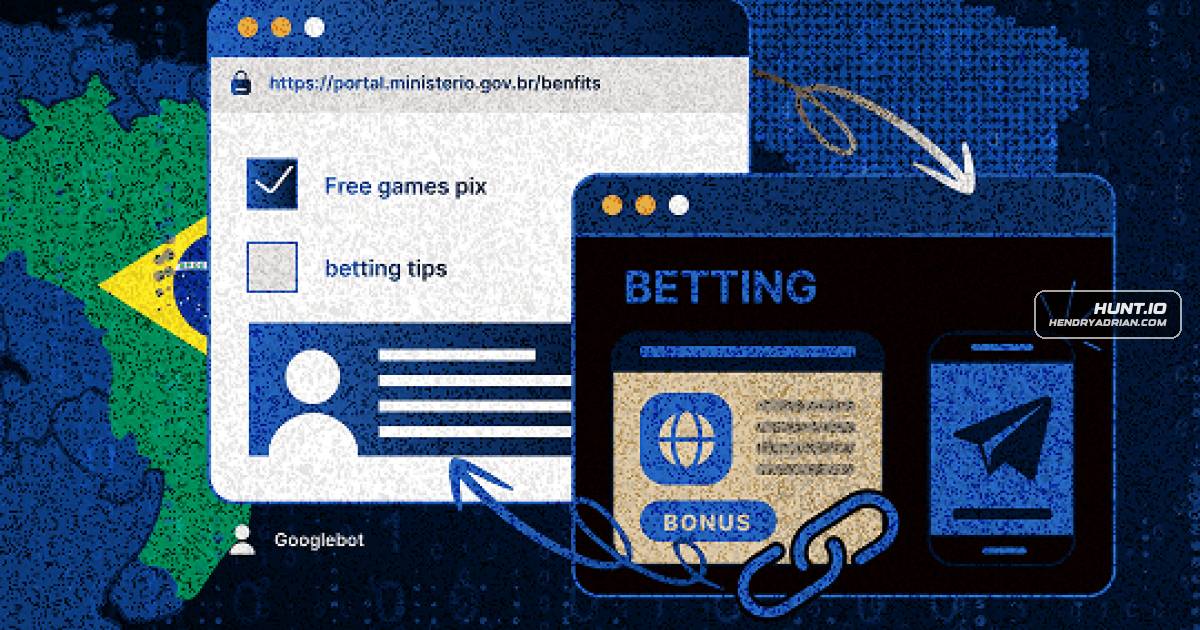
Researchers traced an SEO-poisoning campaign abusing .gov.br subdomains to a server that generated more than 630,000 URLs. Search crawlers received fake government-style pages, while real users were redirected to gambling, betting, or scam sites.
Key points
- Researchers discovered the campaign on June 27, 2025, and traced its automation infrastructure to an exposed server hosted by Kaopu Cloud HK Limited.
- The server used a Flask application, Python scripts, MySQL databases, keyword lists, and HTML templates to generate search-optimized pages.
- The operation reportedly generated more than 630,000 URLs using hijacked .gov.br subdomains.
- Cloaking served keyword-stuffed fake pages to search crawlers while redirecting real users to betting, gambling, or other scam destinations.
- The attackers cloned a legitimate .gov.br page template and used automated content assembly and keyword stuffing to make pages appear credible and rank in search results.
- The report says the exact weakness used to compromise the subdomains has not been identified; the investigation was ongoing with Brazil's CTIR.
- Recommended measures include restricting unauthorized HTML/SHTML uploads, scanning for suspicious files, and monitoring government sites for unexpected content and outbound links.
Article Details
- Attack Vectors
- Hijacked .gov.br subdomains hosted or redirected malicious pages.
- SEO poisoning used keyword-stuffed, templated pages to manipulate search results.
- Cloaking served search-engine crawlers fake government-style content while redirecting real users to betting or scam destinations.
- Defensive Notes
- Enforce strict file-upload controls to prevent unauthorized HTML/SHTML placement, scan for suspicious files, and use robust input validation.
- Audit site content and outbound links, monitor unexpected domain references and search-visibility changes, and use Google Search Console to detect and disavow malicious backlinks.
- Advise users to verify URLs, treat gaming or unfamiliar search results cautiously, download apps only from verified stores, and avoid sharing banking details with unknown sites.
MITRE ATT&CK
Tools
Countries
Industries
GamblingThese compromised subdomains are being used in a large-scale SEO poisoning campaign, where unsuspecting users searching online are funneled toward fraudulent gambling, betting, or scam pages.GovernmentDigging deeper, I realized this infrastructure was actively generating fake government-style pages by hijacking subdomains under