BeaverTail and OtterCookie Add Keylogging and Screenshot Capabilities
Summary
Cisco Talos details how a trojanized Chessfi Node.js application delivered merged BeaverTail and OtterCookie malware, including a new module that captures keystrokes and screenshots, and examines a possibly related malicious VS Code extension.
Key points
- Talos linked the campaign to Famous Chollima, a North Korea-aligned group known for fake job offers targeting job seekers.
- A malicious npm package, node-nvm-ssh, was installed as a dependency of a trojanized Chessfi application and used a post-install process to run obfuscated malware.
- The campaign's OtterCookie v5 added a module that logs keystrokes and periodically captures screenshots, sending the data to command-and-control infrastructure.
- Other OtterCookie modules support remote command execution, clipboard theft, file collection, and theft of browser credentials and cryptocurrency wallet data.
- The malware combines BeaverTail and OtterCookie functionality; Talos says moving capabilities into JavaScript may reduce reliance on Python components.
- Talos found a malicious VS Code extension containing OtterCookie code, but could not confidently attribute it to Famous Chollima.
- Talos reported Snort rules and ClamAV detections for the threat and published indicators of compromise.
Article Details
- Attack Vectors
- A user was likely deceived by a fake job offer and induced to install a trojanized Chessfi Node.js application. Its dependencies included the malicious npm package node-nvm-ssh, whose postinstall instructions led to execution of the payload.
- The payload combined BeaverTail and OtterCookie functionality, including browser credential and cryptocurrency-wallet theft, file collection, clipboard monitoring, keylogging, screenshots, and remote command execution.
- A malicious VS Code extension containing OtterCookie code was found. Talos said it may attempt to run OtterCookie if installed, but attribution to Famous Chollima is uncertain.
- Defensive Notes
- Talos recommends Cisco security products including Secure Endpoint, Secure Email, Secure Firewall, Secure Network/Cloud Analytics, Secure Malware Analytics, Secure Access, Umbrella, Secure Web Appliance, and Duo for detecting or blocking activity.
- The article lists Snort2 rules 65336 and Snort3 rules 301315 and 65336, and ClamAV detections Js.Infostealer.Ottercookie-10057842-0 and Js.Malware.Ottercookie-10057860-0.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| IPV4 | 135[.]181[.]123[.]177 | OtterCookie C2 server listed for logging activity. |
| IPV4 | 138[.]201[.]50[.]5 | C2 server used by a discovered OtterCookie cryptocurrency-extension stealer sample. |
| IPV4 | 144[.]172[.]112[.]50 | OtterCookie C2 server listed for logging activity. |
| IPV4 | 144[.]172[.]96[.]35 | OtterCookie C2 server listed for logging activity. |
| IPV4 | 172[.]86[.]113[.]12 | IP listed among OtterCookie C2 URLs. |
| IPV4 | 172[.]86[.]73[.]46 | IP listed among OtterCookie C2 URLs. |
| IPV4 | 172[.]86[.]88[.]188 | OtterCookie C2 server used for command communication and stolen-data uploads. |
| IPV4 | 23[.]227[.]202[.]244 | BeaverTail C2 server used to deliver Python components and receive stolen data. |
| SHA256 | 0904eff1edeff4b6eb27f03e0ccc759d6aa8d4e1317a1e6f6586cdb84db4a731 | Hash listed for a sample similar to the reported campaign. |
| SHA256 | 51ddd8f6ff30d76de45e06902c45c55163ddbec7d114ad89b21811ffedb71974 | Hash listed for a sample similar to the reported campaign. |
| SHA256 | 6a9b4e8537bb97e337627b4dd1390bdb03dc66646704bd4b68739d499bd53063 | Hash listed for a sample similar to the reported campaign. |
| SHA256 | 72ebfe69c69d2dd173bb92013ab44d895a3367f91f09e3f8d18acab44e37b26d | Hash listed among BeaverTail evolution samples. |
| SHA256 | 77aec48003beeceb88e70bed138f535e1536f4bbbdff580528068ad6d184f379 | Hash listed for a sample similar to the reported campaign. |
| SHA256 | 83c145aedfdf61feb02292a6eb5091ea78d8d0ffaebf41585c614723f36641d8 | Hash listed for the malicious npm package campaign artifact, test.list. |
| SHA256 | 8efa928aa896a5bb3715b8b0ed20881029b0a165a296334f6533fa9169b4463b | Hash listed among BeaverTail evolution samples. |
| SHA256 | 9e65de386b40f185bf7c1d9b1380395e5ff606c2f8373c63204a52f8ddc01982 | Hash listed for the malicious VS Code extension. |
| SHA256 | a6914ded72bdd21e2f76acde46bf92b385f9ec6f7e6b7fdb873f21438dfbff1d | Hash listed for a sample similar to the reported campaign. |
| SHA256 | caad2f3d85e467629aa535e0081865d329c4cd7e6ff20a000ea07e62bf2e4394 | Hash listed among BeaverTail evolution samples. |
| SHA256 | d27c9f75c3f1665ee19642381a4dd6f2e4038540442cf50948b43f418730fd0a | Hash listed for a sample similar to the reported campaign. |
| SHA256 | d89c45d65a825971d250d12bc7a449321e1977f194e52e4ca541e8a908712e47 | Hash listed for a sample similar to the reported campaign. |
| SHA256 | dff2a0fb344a0ad4b2c129712b2273fda46b5ea75713d23d65d5b03d0057f6dd | Hash listed for the malicious VS Code extension raw.js artifact. |
| SHA256 | f08e3ee84714cc5faefb7ac300485c879356922003d667587c58d594d875294e | Hash listed as an early OtterCookie sample. |
MITRE ATT&CK
T1005 · Data from Local SystemThe file-upload module traverses local drives and searches for files matching targeted names and extensions.T1027 · Obfuscated Files or InformationThe article describes JavaScript obfuscation using Obfuscator.io and XOR-based obfuscation of downloaded modules.T1041 · Exfiltration Over C2 ChannelBeaverTail and OtterCookie upload stolen files, credentials, clipboard data, keystrokes, and screenshots to C2 servers.T1056.001 · KeyloggingThe OtterCookie module records keyboard input and uploads the keystrokes to its C2 server.T1059.001 · PowerShellOn Windows, OtterCookie invokes powershell Get-Clipboard to retrieve clipboard contents.T1059.007 · JavaScriptThe payload executes JavaScript code, including code loaded from the server and evaluated by OtterCookie.T1071.001 · Web ProtocolsOtterCookie communicates with its C2 server over HTTP and WebSocket.T1082 · System Information DiscoveryThe OtterCookie module collects and reports infected-system and host information.T1105 · Ingress Tool TransferBeaverTail downloads a Python distribution and Python client payload from its C2 server.T1113 · Screen CaptureThe module periodically captures desktop screenshots and sends them to the OtterCookie C2 server.T1115 · Clipboard DataOtterCookie monitors clipboard contents and sends them to its C2 server.T1195.002 · Compromise Software Supply ChainThe trojanized application installation pulled in the malicious node-nvm-ssh npm dependency, which ran payload-launching postinstall instructions.T1204.002 · Malicious FileThe infection required the user to install and run the trojanized Chessfi application after being deceived by a fake job offer.T1497.001 · System ChecksOtterCookie checks for virtual or sandbox environments to distinguish analysis environments from actual infections.T1555.003 · Credentials from Web BrowsersThe malware targets saved browser credentials and browser Login data.
People
Threat Actors
Malware
BeaverTailBeaverTail and OtterCookie evolve with a new Javascript moduleGolangGhosttechniques and payload variants of credential and cryptocurrency remote access trojans (RATs) known as GolangGhost and PylangGhost. InvisibleFerretuses BeaverTail and OtterCookie, with many individual sub-clusters of activities installing InvisibleFerret, a Python based modular payload. Although BeaverTail and OtterCookie originated asOtterCookieBeaverTail and OtterCookie evolve with a new Javascript modulePylangGhostvariants of credential and cryptocurrency remote access trojans (RATs) known as GolangGhost and PylangGhost.
Vendors
Products
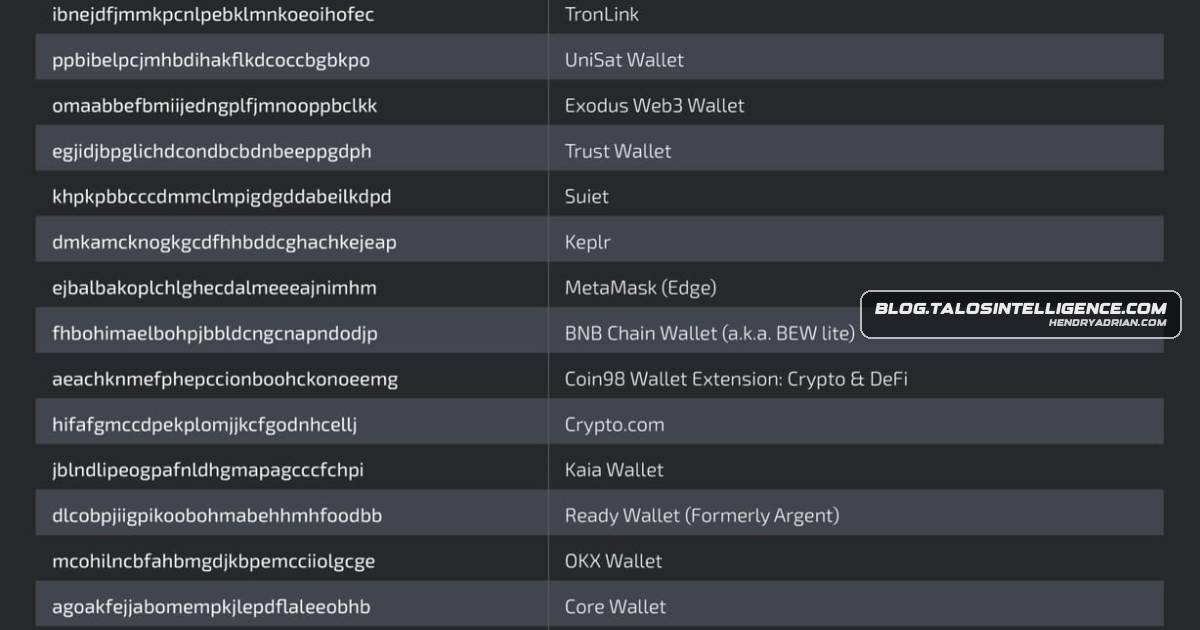
AnyDeskInvisibleFerret Python stealer payload modules and installation of a remote access module, typically an AnyDesk client, which would allow the attacker to take over the control of the infected machine remotely.BitbucketNode-nvm-ssh infection path. The initial infection vector was a modified Chessfi application hosted on Bitbucket. ChessFi is a web3-based multiplayer chess platform where players can challenge each other and betBrave1. Cryptocurrency modules targeted by OtterCookie. The cryptocurrency module targets Google Chrome and Brave browsers. If any extensions are found in any of the browser profiles, the extension files as well as theCisco DuoCisco Duo provides multi-factor authentication for users to ensure only those authorized are accessing your network. Cisco Secure AccessCisco Secure Access is a modern cloud-delivered Security Service Edge (SSE) built on Zero Trust principles. Secure Access provides seamless transparent and secure access to the internet, cloud services or privateCisco Secure EmailCisco Secure Email (formerly Cisco Email Security) can block malicious emails sent by threat actors as part of their campaign. You can try Secure Email for free here. Cisco Secure EndpointCisco Secure Endpoint (formerly AMP for Endpoints) is ideally suited to prevent the execution of the malware detailed in this post. Try Secure Endpoint for free here. Cisco Secure FirewallCisco Secure Firewall (formerly Next-Generation Firewall and Firepower NGFW) appliances such as Threat Defense Virtual, Adaptive Security Appliance and Meraki MX can detect malicious activity associated with thisCisco Secure Malware AnalyticsCisco Secure Malware Analytics (Threat Grid) identifies malicious binaries and builds protection into all Cisco Secure products. Cisco Secure Network/Cloud AnalyticsCisco Secure Network/Cloud Analytics (Stealthwatch/Stealthwatch Cloud) analyzes network traffic automatically and alerts users of potentially unwanted activity on every connected device. Cisco Secure Web ApplianceCisco Secure Web Appliance (formerly Web Security Appliance) automatically blocks potentially dangerous sites and tests suspicious sites before users access them. ClamAVClamAV detections are also available for this threat: Js.Infostealer.Ottercookie-10057842-0, Js.Malware.Ottercookie-10057860-0 Google ChromeTable 1. Cryptocurrency modules targeted by OtterCookie. The cryptocurrency module targets Google Chrome and Brave browsers. If any extensions are found in any of the browser profiles, the extension files as well as theMozilla Firefoxextensions and saved browser credentials. Targeted browsers include Brave, Google Chrome, Opera and Mozilla Firefox. Node.jswas compromised-likely because a user was deceived by a fake job offer and installed a trojanized Node.js application called "Chessfi." npmThe malicious software was distributed via a Node.js package named "node-nvm-ssh" on the official NPM repository.Operabrowser extensions and saved browser credentials. Targeted browsers include Brave, Google Chrome, Opera and Mozilla Firefox. SnortOpen-source Snort Subscriber Rule Set customers can stay up to date by downloading the latest rule pack available for purchase on Snort.org. UmbrellaUmbrella, Cisco’s secure internet gateway (SIG), blocks users from connecting to malicious domains, IPs and URLs, whether users are on or off the corporate network. VS CodeWhile searching for related threats, Talos also found a malicious VS Code extension containing BeaverTail and OtterCookie code. Although attribution to Famous Chollima is not certain, this suggests the group may be