
Sekoia Analyzes EvilTokens Device-Code Phishing Kit and Microsoft 365 Account-Takeover Capabilities
Summary
Sekoia analyzes EvilTokens, a phishing-as-a-service kit that uses Microsoft device-code flows to steal tokens and enable account access, reconnaissance, and BEC. The report details its backend, campaigns, and tracking methods.
Key points
- Sekoia says it identified EvilTokens in March 2026; phishing pages were circulating from mid-February and were rapidly adopted in BEC campaigns.
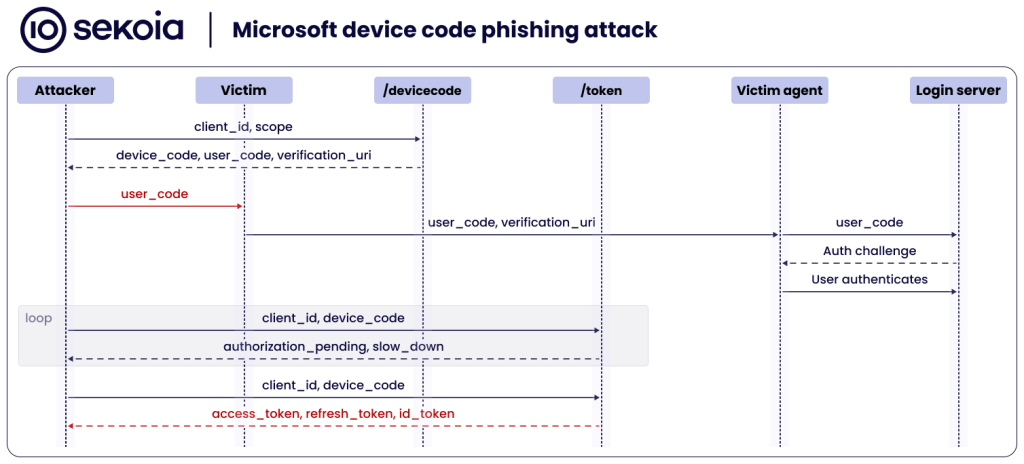
- The kit tricks users into entering an attacker-generated device code on a legitimate Microsoft sign-in page, enabling the attacker to obtain access and refresh tokens.
- Sekoia’s backend analysis describes refresh-token conversion to Primary Refresh Tokens, browser-cookie generation, and Graph and Azure reconnaissance; analysts could not confirm that every feature is fully operational.
- Campaign lures were delivered through PDF, HTML, XLSX, SVG, and DOCX attachments, targeting employees in finance, HR, logistics, and sales across multiple regions.
- Sekoia reported more than 1,000 results associated with EvilTokens pages through its tracking heuristics as of March 23, 2026.
- The report identifies tracking opportunities including device-flow API requests, the X-Antibot-Token header, Cloudflare Workers page patterns, and a YARA rule.
Article Details
- Attack Vectors
- Affiliates deliver attachments in PDF, HTML, XLSX, SVG, or DOCX formats containing QR codes or links to EvilTokens phishing pages.
- Phishing pages impersonate trusted services or document workflows and persuade victims to enter a device code on the legitimate Microsoft sign-in page.
- The backend captures access and refresh tokens through Microsoft device authorization flows, converts refresh tokens to PRTs, and can generate browser-session cookies.
- The kit supports post-compromise account reconnaissance and access to email, documents, and other Microsoft 365 resources.
- Defensive Notes
- Track the reported Cloudflare Workers hostname patterns used by EvilTokens phishing pages.
- Monitor HTTP POST requests to /api/device/start and polling requests to /api/device/status/.
- Monitor for the X-Antibot-Token HTTP header, which Sekoia identifies as an indicator associated with EvilTokens pages.
- Use the article’s YARA rule, phishing_eviltokens_phishing_page, to detect characteristic phishing-page strings.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | authdocspro[.]com | Affiliate-hosted domain listed as an EvilTokens device-code phishing domain. |
| DOMAIN | backdoor-hub[.]com | Affiliate-hosted domain listed as an EvilTokens device-code phishing domain. |
| DOMAIN | bumpgames[.]net | Affiliate-hosted domain listed as an EvilTokens device-code phishing domain. |
| DOMAIN | carbatterygurgaon[.]com | Affiliate-hosted domain listed as an EvilTokens device-code phishing domain. |
| DOMAIN | dao[.]com[.]au | Affiliate-hosted domain listed as an EvilTokens device-code phishing domain. |
| DOMAIN | eventcalender-schedule[.]com | Affiliate-hosted domain listed as an EvilTokens device-code phishing domain. |
| DOMAIN | evobothub[.]org | Affiliate-hosted domain listed as an EvilTokens device-code phishing domain. |
| HOSTNAME | adobe-7bf[.]signature-on-invoice-required-mail-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | adobe-b6d[.]tuwilika-fcsnam-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | adobe-h7l[.]gregcausey-hyundaicrenshaw-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | adobe-lar[.]denise-chxhistory-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | adobe-t9r[.]thomas-gibson-clyde-enq-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | careldutoit-el[.]co[.]za | Affiliate-hosted hostname listed as an EvilTokens device-code phishing domain. |
| HOSTNAME | docusend[.]networkssolutionmail[.]com | Affiliate-hosted hostname listed as an EvilTokens device-code phishing domain. |
| HOSTNAME | docusign-d0e[.]admin-treyripple-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | docusign-gmx[.]medea-locallovechs-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | docusign-t0o[.]accountsreceivable-greens-au-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | docusign-vs4[.]finance-zltnservices-org-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | eqfit[.]co[.]za | Affiliate-hosted hostname listed as an EvilTokens device-code phishing domain. |
| HOSTNAME | index-8ni[.]shirdav-mail-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | index-izk[.]rifkit-protonmail-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | onedrive-23n[.]sbutler-stateservice-us-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | onedrive-33i[.]amittal-prodwaresol-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | onedrive-7fp[.]davarius-thackery-dropmeon-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | onedrive-ac4[.]ryker-samik-dropmeon-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | onedrive-au8[.]hayixa9795-pazard-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | onedrive-hea[.]jhaas-hapnehartmedia-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | page-custommmvx6290-9kb[.]snpfs90-outlook-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | page-voicemail-3i6[.]ucbqzm9-ucl-ac-uk-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
| HOSTNAME | sharepoint-uo2[.]angela-warrconstructioninc-onmicrosoft-com-s-account[.]workers[.]dev | EvilTokens administrator-hosted Cloudflare Workers phishing hostname. |
MITRE ATT&CK
T1069.003 · Cloud GroupsThe backend queries the Microsoft Graph /groups endpoint during post-compromise reconnaissance.T1078.004 · Cloud AccountsAfter victims complete the device-code flow, attackers use the resulting account access to reach the victims’ Microsoft cloud resources.T1087.004 · Cloud AccountThe backend queries Microsoft Graph endpoints including /users and /organization for account and organization reconnaissance.T1098.005 · Device RegistrationThe article describes using a harvested refresh token to register an additional Entra ID device and then request a PRT.T1114.002 · Remote Email CollectionThe article says attackers can access and exfiltrate victims’ Exchange Online emails after compromising their accounts.T1528 · Steal Application Access TokenThe backend captures victims’ Microsoft access and refresh tokens through the device-code authorization flow.T1530 · Data from Cloud StorageThe article describes accessing and exfiltrating victims’ documents from SharePoint Online and OneDrive.T1550.001 · Application Access TokenThe backend exchanges harvested refresh tokens for access tokens used to access resources such as Outlook, Graph, Azure, and SharePoint.T1550.004 · Web Session CookieThe kit generates an x-ms-RefreshTokenCredential cookie to access a live browser session without a password or MFA prompt.T1566.001 · Spearphishing AttachmentAffiliates delivered phishing lures as PDF, HTML, XLSX, SVG, or DOCX attachments containing QR codes or links to EvilTokens pages.T1580 · Cloud Infrastructure DiscoveryThe backend enumerates Azure subscriptions, resource groups, and resources through Azure Management.
Threat Actors
Vendors
CloudflareThe kit has been rapidly adopted by affiliates for BEC campaigns and is tracked across 1,000+ domains deployed via Cloudflare Workers and affiliate hosting.MicrosoftSekoia discovered EvilTokens, a new Phishing-as-a-Service that provides turnkey Microsoft device code phishing pages and a full backend for token harvesting, PRT conversion, cookie generation, and post-compromise
Products
Azureto Primary Refresh Tokens (PRTs), generating x-ms-RefreshTokenCredential cookies, and performing Graph/Azure reconnaissance.DocuSignThe platform supplies phishing templates (Adobe, DocuSign, OneDrive, calendar invites, payroll, etc.) that launch genuine Microsoft device login flows to harvest user and device tokens.Entra IDThis short-lived token issued by Entra ID grants access to a target resource for 60-90 minutes, randomly determined. It is tied to the authenticated user, the authorised permission scopes, and the target resource.Exchange OnlineDepending on the targeted service, the attacker can access emails via Exchange Online, documents from Microsoft SharePoint Online and OneDrive, or conversation history in Microsoft Teams.Microsoft 365 Apps for EnterpriseTo compromise Microsoft 365 accounts, EvilTokens pages rely on device code phishing, a technique that differs from the common AitM tactic of replicating Microsoft authentication pages.Microsoft Graphexchange those tokens with a Primary Refresh Token and additional tokens granting access to Outlook, Microsoft Graph, Azure, Substrate (Microsoft Cloud), and SharePoint.Microsoft Officea Microsoft first-party application, for example Microsoft Office client).Microsoft OneDriveThe platform supplies phishing templates (Adobe, DocuSign, OneDrive, calendar invites, payroll, etc.) that launch genuine Microsoft device login flows to harvest user and device tokens.Microsoft TeamsDepending on the targeted service, the attacker can access emails via Exchange Online, documents from Microsoft SharePoint Online and OneDrive, or conversation history in Microsoft Teams.SharePoint OnlineDepending on the targeted service, the attacker can access emails via Exchange Online, documents from Microsoft SharePoint Online and OneDrive, or conversation history in Microsoft Teams.
Tools
Countries
AustraliaThe most affected countries are the United States, Australia, Canada, France, India, Switzerland and the United Arab Emirates.CanadaThe most affected countries are the United States, Australia, Canada, France, India, Switzerland and the United Arab Emirates.FranceThe most affected countries are the United States, Australia, Canada, France, India, Switzerland and the United Arab Emirates.IndiaThe most affected countries are the United States, Australia, Canada, France, India, Switzerland and the United Arab Emirates.SwitzerlandThe most affected countries are the United States, Australia, Canada, France, India, Switzerland and the United Arab Emirates.United Arab EmiratesThe most affected countries are the United States, Australia, Canada, France, India, Switzerland and the United Arab Emirates.United StatesThe most affected countries are the United States, Australia, Canada, France, India, Switzerland and the United Arab Emirates.