
Infinity Stealer Uses ClickFix Lures to Target macOS
Summary
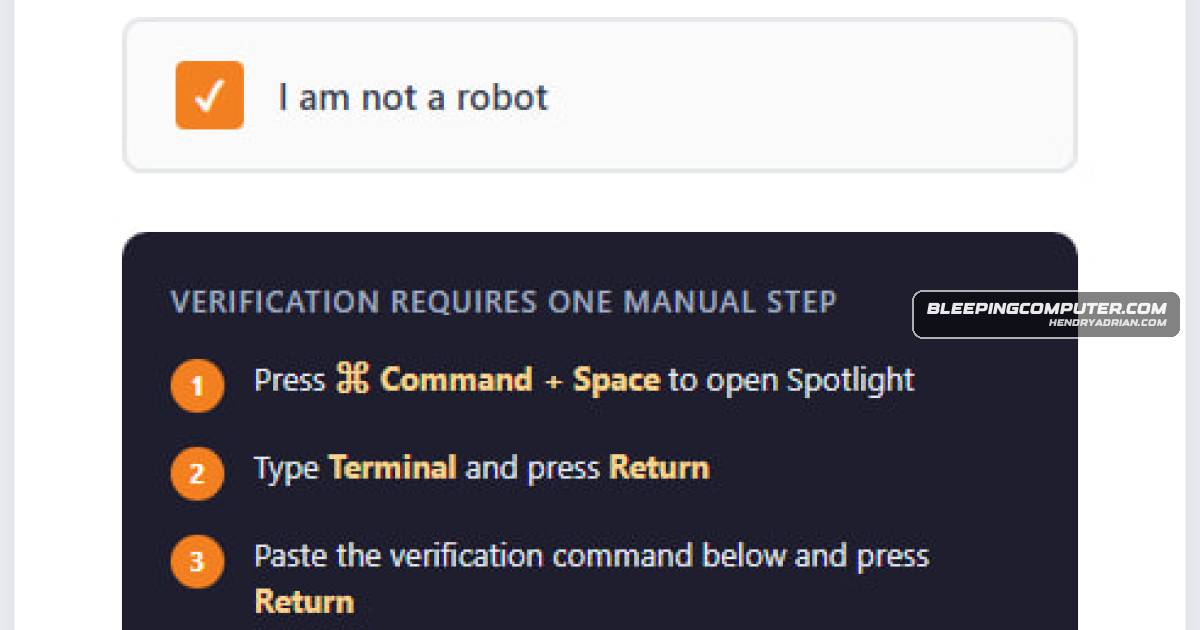
Malwarebytes describes Infinity Stealer, a macOS infostealer delivered through a fake Cloudflare CAPTCHA and a Nuitka-built loader. It can collect credentials, Keychain entries, wallets, screenshots and developer secrets, then exfiltrate data over HTTP.
Key points
- The campaign uses a fake Cloudflare CAPTCHA to trick users into pasting a base64-obfuscated command into macOS Terminal.
- The command launches a Bash loader that downloads and executes a Nuitka-built Mach-O binary.
- The loader contains a compressed archive holding the Infinity Stealer payload, named UpdateHelper.bin.
- The malware checks for virtualized or sandboxed environments before collecting data.
- Malwarebytes says the infostealer can collect browser credentials, macOS Keychain entries, cryptocurrency wallets, screenshots and plaintext developer secrets.
- Stolen data is sent to a command-and-control server via HTTP POST; operators receive Telegram notifications.
Article Details
- Attack Vectors
- A fake Cloudflare CAPTCHA on update-check[.]com tells users to paste a base64-obfuscated curl command into macOS Terminal.
- The command runs a Bash loader that places the Nuitka-built loader in /tmp, removes its quarantine flag, and executes it.
- The loader extracts UpdateHelper.bin, which performs anti-analysis checks, steals sensitive data, and exfiltrates it via HTTP POST to a C2.
- Defensive Notes
- Do not paste commands from websites into Terminal unless you understand and trust them.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | update-check[.]com | Domain hosting the fake CAPTCHA lure used to deliver the Infinity Stealer campaign. |
MITRE ATT&CK
T1027.010 · Command ObfuscationThe curl command supplied by the lure is base64-obfuscated.T1041 · Exfiltration Over C2 ChannelStolen data is sent to the C2 via HTTP POST.T1059.004 · Unix ShellThe pasted command runs a Bash loader that writes and executes the stage-2 payload.T1070.004 · File DeletionThe loader deletes itself after execution.T1071.001 · Web ProtocolsThe article reports HTTP communication with the C2 for data exfiltration.T1105 · Ingress Tool TransferThe curl-based delivery chain places the Nuitka loader on the Mac.T1113 · Screen CaptureThe malware can capture screenshots.T1140 · Deobfuscate/Decode Files or InformationThe command decodes the obfuscated content to produce a Bash script.T1204.004 · Malicious Copy and PasteThe lure persuades users to copy and paste a command into macOS Terminal.T1497.001 · System ChecksInfinity Stealer checks whether it is running in a virtualized or sandboxed environment.T1552.001 · Credentials In FilesThe malware searches developer files, including .env files, for plaintext secrets.T1553.001 · Gatekeeper BypassThe loader removes the quarantine flag before execution.T1555.001 · KeychainThe malware harvests macOS Keychain entries.T1555.003 · Credentials from Web BrowsersThe malware steals credentials from Chromium-based browsers and Firefox.
Malware
Products
macOSA new info-stealing campaign called Infinity Stealer targets macOS by delivering a Python payload compiled into a native executable with the Nuitka compiler and lures users via a ClickFix fake Cloudflare CAPTCHA.Telegramand plaintext developer secrets, and exfiltrates data to a C2 via HTTP while notifying operators via Telegram; users should never paste unknown commands into Terminal.