
CloakGuard Malware Uses Fake Blue Screens to Hide Remote Access
Summary
Analysis of the signed Go-based CloakGuard agent found it disguises itself as a Windows service, can disable Defender, hides operator activity behind fake crash or update screens, and installed ScreenConnect in a sandbox.
Key points
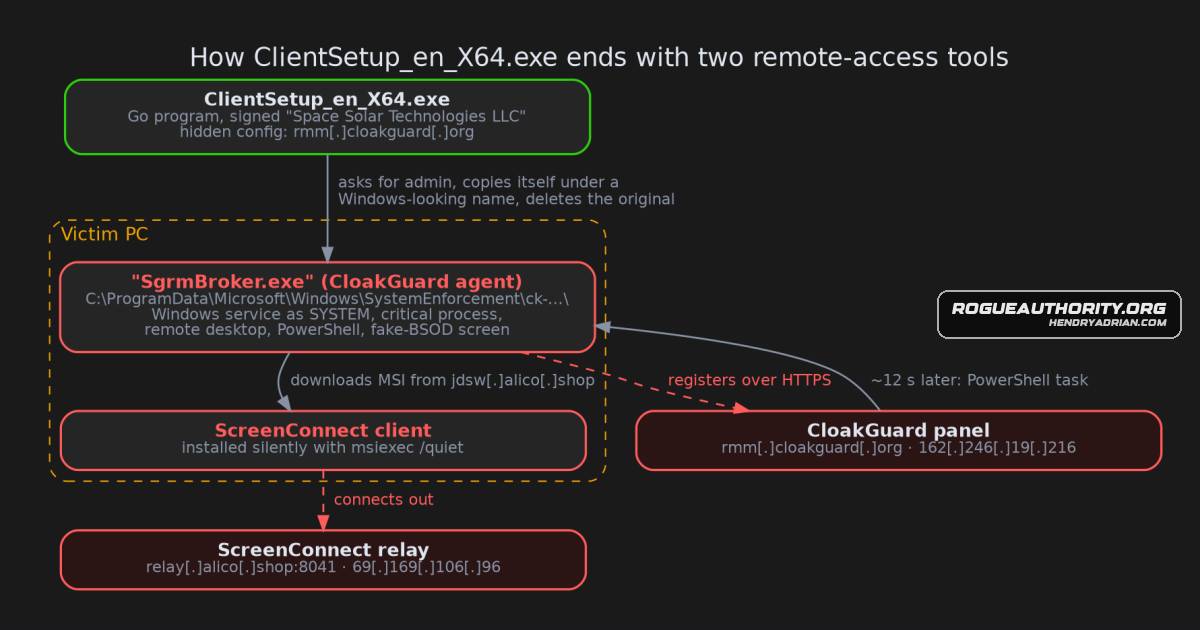
- The analysis identifies ClientSetup_en_X64.exe as a signed Go program that installs as SgrmBroker.exe under ProgramData and runs as a Windows service.
- CloakGuard can make itself difficult to terminate, disable Microsoft Defender protections, and fall back to a WindowsManagementHost startup entry.
- Its fake blue-screen, update, or black-screen overlay is excluded from screen capture while blocking the victim’s keyboard and mouse, allowing the operator to interact with the real desktop.
- In a sandbox run on October 27, 2026, the server sent a PowerShell script that silently installed ScreenConnect from jdsw[.]alico[.]shop; the client connected to relay[.]alico[.]shop on port 8041.
- The agent checks for virtual machines, debuggers, sandbox artifacts, and analysis tools, then reports a calculated risk score to its server.
- The investigators could not decrypt the server’s instructions or determine whether the CloakGuard and ScreenConnect servers were operated by the same people.
- The article recommends hunting for the disguised service and unusual screen-capture exclusion behavior, and checking ScreenConnect instances for unexpected relay connections.
Article Details
- Attack Vectors
- The sample is a code-signed Windows executable that disguises itself as SgrmBroker.exe and installs under a Microsoft-looking path in ProgramData. The article says no lure or scam call was observed.
- After enrolling with its control server over HTTPS, the sample received a PowerShell script that downloaded and silently installed ScreenConnect.
- CloakGuard can run PowerShell and command-line commands, install packages, and provide remote desktop access. The article does not establish who operated the servers or whether the CloakGuard and ScreenConnect infrastructure had the same operators.
- Defensive Notes
- Hunt for SgrmBroker.exe outside C:\Windows\System32, especially under C:\ProgramData\Microsoft\Windows\SystemEnforcement\.
- Look for services named CloakGuardRemoteAgent*, the WindowsManagementHost startup value, and the Global\SgrmBrokerInstance mutex.
- Alert on unexpected non-system processes setting themselves as critical and on unexpected use of SetWindowDisplayAffinity with WDA_EXCLUDEFROMCAPTURE.
- Inventory ScreenConnect instances and investigate relays for instances that were not deployed by the organization.
- Block the reported CloakGuard and ScreenConnect infrastructure indicators.
- The article advises users not to install unsolicited support software and to disconnect from the network if a suspicious fake crash or update screen appears.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | relay[.]alico[.]shop | Reported ScreenConnect relay configured for the second remote-access tool installed by the sample. |
| DOMAIN | rmm[.]cloakguard[.]org | Reported CloakGuard control server used by the sample. |
| IPV4 | 162[.]246[.]19[.]216 | Reported IP address for the CloakGuard control server. |
| IPV4 | 69[.]169[.]106[.]96 | Reported IP address of the ScreenConnect relay used by the installed client. |
| SHA256 | 5e3372db2b25f1e1fda89dcffc574a15702670bc04243f78fa3aa6b35b2f6929 | SHA-256 hash of the reported CloakGuard installer, ClientSetup_en_X64.exe. |
| URL | hxxps[:]//jdsw[.]alico[.]shop/Bin/ScreenConnect.ClientSetup.msi?e=Access&y=Guest | Specific reported URL used to download the ScreenConnect installer delivered by the CloakGuard server. |
MITRE ATT&CK
T1027 · Obfuscated Files or InformationThe sample XOR-scrambles its disguise names, scheduled-task names, and server API paths, then unscrambles them at startup.T1036.005 · Match Legitimate Resource Name or LocationCloakGuard installs under the Windows component name SgrmBroker.exe and uses a Microsoft-looking folder path.T1057 · Process DiscoveryCloakGuard checks running processes and includes process inventory among its collection capabilities.T1059.001 · PowerShellThe server sent a PowerShell script that downloaded and silently installed ScreenConnect.T1071.001 · Web ProtocolsThe sample enrolled with its control server over HTTPS and communicated with it using HTTPS.T1105 · Ingress Tool TransferThe server-supplied script downloaded ScreenConnect.ClientSetup.msi from the reported jdsw[.]alico[.]shop URL.T1219 · Remote Access ToolsCloakGuard provides remote desktop control, and the sample installed ScreenConnect as a second remote-access tool.T1497.001 · System ChecksCloakGuard checks for virtual machines and sandbox artifacts and reports a resulting risk score to its server.T1518.001 · Security Software DiscoveryThe sample checks antivirus status and for analysis tools, including x64dbg, Ghidra, and WinDbg.T1543.003 · Windows ServiceCloakGuard installs itself as a Windows service named CloakGuardRemoteAgent with a variable suffix.T1547.001 · Registry Run Keys / Startup FolderIf service creation fails, the sample uses the WindowsManagementHost startup entry in the Run registry key.T1562.001 · Disable or Modify ToolsThe agent can disable Microsoft Defender real-time, behavior, and script scanning, cloud protection, and sample submission.T1573 · Encrypted ChannelThe article reports that the CloakGuard server's messages were encrypted and could not be read in the sandbox.T1622 · Debugger EvasionThe agent checks for attached debuggers and includes debugger presence in its reported risk score.
Malware
Products
Microsoft Defender Antimalware PlatformIn practice it hides under the name of a real Windows component, makes itself very hard to kill, and can switch off Microsoft Defender.Microsoft WindowsClientSetup_en_X64.exe is a code-signed Windows program written in Go that calls itself CloakGuard.ScreenConnectIn the public sandbox run, its control server answered within seconds and installed a second remote-access tool, ScreenConnect.