
Operation Endgame Disrupts StealC Ecosystem After Researchers Expose C2 Flaw
Summary
Proofpoint and IBM X-Force supported an Operation Endgame disruption targeting StealC and Amadey infrastructure. Researchers detailed a StealC C2 path-traversal flaw and used client emulation to track payloads, including XTinyLoader delivering LockBit Black.
Key points
- The June 2026 operation targeted 66 domains and 296 servers associated with StealC and Amadey.
- Authorities seized more than 25.6 million unique stolen credentials from over 385,000 compromised systems.
- Researchers found a path-traversal flaw in StealC’s PHP-based C2 panel; the developers patched it in February 2026. Law enforcement used an exploit to support searches and infrastructure seizures.
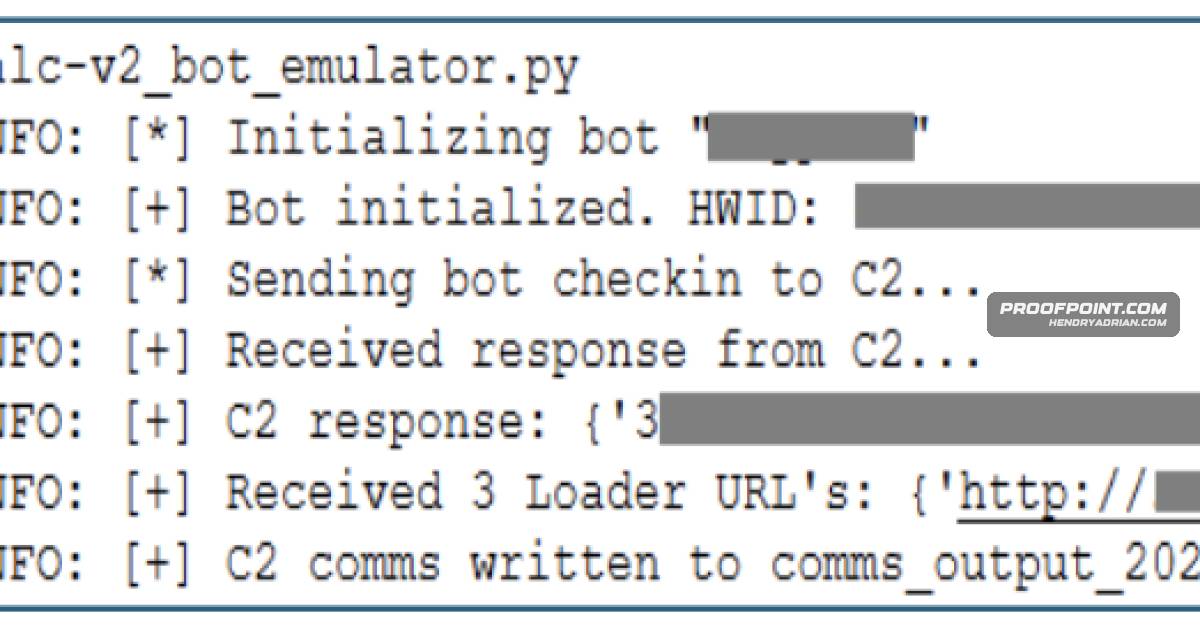
- Proofpoint and IBM X-Force extracted StealC configurations and emulated bot communications to track C2 operations and retrieve payload URLs.
- Researchers observed payload chains in which StealC delivered XTinyLoader, which then downloaded LockBit Black ransomware; other observed payloads included AsyncRAT, RedLine Stealer, and Vidar.
- The article says the same C2 flaw may also have been exploited by an affiliate to steal data from other affiliates.
Article Details
- Attack Vectors
- StealC malware steals credentials and other sensitive data, then exfiltrates it to its C2 panel.
- StealC's optional loader can download and execute secondary payloads from URLs supplied by its C2 server.
- A path-traversal vulnerability in the StealC C2 panel's file extraction logic could write files to unintended locations, including enabling web-shell upload.
- Defensive Notes
- The StealC developers patched the C2-panel vulnerability in February 2026.
- Proofpoint and IBM X-Force used malware samples, sandbox analysis, configuration extraction, and C2 emulation to track StealC operations and create detections and customer protections, including via Emerging Threats.
- Law enforcement and private-sector partners disrupted infrastructure associated with StealC and Amadey; the article reports that the action affected 66 domains and 296 servers.
MITRE ATT&CK
T1027 · Obfuscated Files or InformationStealC stores configurations and other values in encrypted or obfuscated form before decrypting them during execution.T1041 · Exfiltration Over C2 ChannelStealC sends stolen data to its C2 server through its normal communications.T1071.001 · Web ProtocolsStealC communicates with its C2 panel using RC4-encrypted HTTP POST requests containing JSON.T1105 · Ingress Tool TransferStealC clients can download and execute secondary payloads from URLs provided by the C2 server.T1132.001 · Standard EncodingStealC encodes exfiltrated data as Base64 in the JSON request sent to its C2 panel.
Malware
AmadeyProofpoint, IBM X-Force, and Europol supported an Operation Endgame disruption against the StealC ecosystem, seizing 25.6 million stolen credentials and impacting 66 domains and 296 servers tied to StealC and Amadey.AsyncRATObserved payload chains included malware such as XTinyLoader, LockBit Black, AsyncRAT, RedLine Stealer, Vidar, and XMRig.HijackLoaderHijackLoader (aka. DOILoader, IDAT Loader) LockBit BlackResearchers also exposed a StealC C2 vulnerability, built a StealC emulator, and observed payload delivery chains involving XTinyLoader, LockBit Black, and other malware families.RedLine StealerObserved payload chains included malware such as XTinyLoader, LockBit Black, AsyncRAT, RedLine Stealer, Vidar, and XMRig.StealCProofpoint, IBM X-Force, and Europol supported an Operation Endgame disruption against the StealC ecosystem, seizing 25.6 million stolen credentials and impacting 66 domains and 296 servers tied to StealC and Amadey.VidarObserved payload chains included malware such as XTinyLoader, LockBit Black, AsyncRAT, RedLine Stealer, Vidar, and XMRig.XMRigObserved payload chains included malware such as XTinyLoader, LockBit Black, AsyncRAT, RedLine Stealer, Vidar, and XMRig.XTinyLoaderResearchers also exposed a StealC C2 vulnerability, built a StealC emulator, and observed payload delivery chains involving XTinyLoader, LockBit Black, and other malware families.
Vendors
IBMProofpoint, IBM X-Force, and Europol supported an Operation Endgame disruption against the StealC ecosystem, seizing 25.6 million stolen credentials and impacting 66 domains and 296 servers tied to StealC and Amadey.MicrosoftAdditionally, Microsoft’s Digital Crimes Unit filed a lawsuit against multiple alleged enablers involved in StealC and Amadey, and was able to take down infrastructure associated with the malware.ProofpointProofpoint, IBM X-Force, and Europol supported an Operation Endgame disruption against the StealC ecosystem, seizing 25.6 million stolen credentials and impacting 66 domains and 296 servers tied to StealC and Amadey.