Google Details Turla’s STOCKSTAY Backdoor and Its Operations Against Ukrainian Targets
Summary
Google’s threat intelligence team analyzes STOCKSTAY, a .NET backdoor used by Turla since at least 2022 for espionage, chiefly against Ukrainian government and military targets, and details its capabilities, delivery methods, and links to KAZUAR.
Key points
- STOCKSTAY is a multi-component .NET backdoor that uses encrypted configuration, WebSocket command-and-control, and inter-process communication.
- Its operators can run commands, manipulate files and registry values, capture screens, collect system information, and transfer files.
- Turla has delivered the malware through phishing and malicious RDP files, as well as HTA files and archives exploiting WinRAR vulnerability CVE-2025-8088.
- The campaign has primarily targeted Ukrainian government and military organizations; Google also identified activity involving entities associated with European foreign affairs.
- The malware has used compromised infrastructure to host payloads and relay C2 traffic, and has disguised itself as benign applications.
- Google assesses with moderate confidence that STOCKSTAY and Turla’s KAZUAR toolkit share development links, including code and architectural similarities.
- The report includes indicators of compromise and YARA detection rules; Google marked affected accounts for additional authentication checks and notified affected users in the November 2025 phishing activity.
Article Details
- Attack Vectors
- Spear-phishing emails used malicious RDP attachments to connect victims to actor-controlled infrastructure, after which STOCKSTAY.MARKETMAKER was deployed.
- A compromised diplomatic education platform distributed malicious RDP files disguised as access to an online training portal. GTIG could not confirm STOCKSTAY deployment in that operation.
- A military cash-benefit calculator lure used an HTA containing JScript to rename and execute a bundled STOCKSTAY.MARKETMAKER downloader.
- November 2025 phishing emails linked to malicious RAR archives exploiting WinRAR path traversal vulnerability CVE-2025-8088 to install STOCKSTAY components and place execution shortcuts in the startup directory.
- Compromised Ukrainian websites, including government and WordPress infrastructure, hosted STOCKSTAY payload archives.
- In a compromised Ukrainian network, Turla deployed malware through malicious GPO installation from a compromised domain controller; STOCKSTAY components and configuration archives were staged on that controller.
- Malicious MSI installers installed STOCKSTAY components and established persistence through registry Run keys.
- Defensive Notes
- The article supplies YARA rules for STOCKSTAY configuration files, cryptographic-container parsing, window names, component handlers, the MARKETMAKER downloader, and K1MORPHER obfuscation.
- Google Security Operations detection rules were pending deployment for archive extraction into Windows startup locations, registry Run-key writes, phishing-related RDP files, RDP connections from staging directories, and suspicious Onrender subdomain DNS queries.
- Later-stage STOCKSTAY configurations use host, user, or domain attributes for environmental keying, which can prevent configuration decryption outside the intended environment.
- Most analyzed STOCKSTAY configurations restricted operation to Monday through Friday, 0900–1800 on the victim's system; GTIG assessed that this likely helps blend C2 traffic into business activity.
- STOCKSTAY encrypts outbound responses before sending them through intermediary WebSocket servers, preventing those servers and hosting operators from inspecting message contents.
- For the November phishing activity, Google marked affected Google accounts for additional authentication checks and issued Government Backed Attack Warning notifications. GTIG could not confirm how many recipients downloaded or executed payloads.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| SHA256 | 0a545dd1b703cddfb3d582c8c70f65f556bbd580bfa836a387121eb837bda61b | STOCKSTAY.STOCKTRADER backdoor in the December 2023 archive. |
| SHA256 | 0d6b083208097d5b3e189891338540f6c64faaaaf268b0bb0b085dd53d5857b4 | Malicious military cash-benefit calculator HTA lure that executes STOCKSTAY.MARKETMAKER. |
| SHA256 | 1682e8d82016b3f10434d2ebac995fd3b6aa812f079bfd7888652e94a994d851 | External STOCKSTAY module containing backdoor command handlers. |
| SHA256 | 19e6ed42248f9d03beb343a7c09a864dcd3cd671c29e1e5eac93579225224ac9 | File indicator for GitHub-hosted DiplomacyEduAI.msi installers containing STOCKSTAY. |
| SHA256 | 1a2ca8b8e0344fe3d80da7352206a470245443e2349a237bc093df934ddc011f | sample.conf configuration file for the early STOCKSTAY sample. |
| SHA256 | 1fc23ec18a94a599a34c74ef5f49a1e27acd37a07d5846661702b5e7e81a6a24 | StockMarketNews.exe combined STOCKSTAY executable. |
| SHA256 | 249a4c7cacdd8e99a2a089a5c0ce904f2eff22e0e40fcfb10f7824dca6c51ecb | STOCKSTAY file indicator listed for the February 2024 Italy-associated installer. |
| SHA256 | 2623c6e3c1f5a7b5e735a64813bc0e1382ae45831f5fadffb08c0e7b096627f7 | default.conf configuration file in the December 2023 STOCKSTAY archive. |
| SHA256 | 2af7b513c05e76d7da5f75bb0a223c894a706c99ef2c2ddfe4eae542f95a08e0 | STOCKSTAY.STOCKMARKET artifact listed for the March–April 2025 operation and referenced in its controller YARA rule. |
| SHA256 | 34fcbe7e90fc87a4f3766469c19a64f24672d7adb99e0198f5ba10d58911368b | STOCKSTAY.STOCKBROKER tunneler in the December 2023 archive. |
| SHA256 | 3627f582420ad2782d452fe6d13fae42658d1484296351d3916703e25dcadd14 | MSViewer.lnk shortcut intended to execute STOCKSTAY.STOCKMARKET. |
| SHA256 | 391e51354118fb87dc57650cbbd94258c3f7c0a0d6868040b7a473ad626ff25e | Artifact referenced by the K1MORPHER Squirrel3 implementation hunting rule. |
| SHA256 | 40a3b969d81ef1ef35dd9ebcc6774e060b1b8949d3d74f38ca6b7d789c95cdb3 | Encrypted STOCKSTAY configuration artifact named fonts. |
| SHA256 | 40b1208dda0cd5dd95c6b57764b2cfe7145b3ed9457f498408b4aaa05bf3ef50 | STOCKSTAY file indicator listed for the February 2024 Italy-associated installer. |
| SHA256 | 447f430b46fad5a3f8e8c5aad1f8f7f79af069489c3d9c29224bb9f14f0c7bf4 | EditorToolsPdf.zip archive containing core STOCKSTAY components. |
| SHA256 | 45bb8d1ab2c13bf4354294e13d3c9be15de625d807301905b98462f43f93e893 | ViewPdf.exe STOCKSTAY artifact also referenced by K1MORPHER hunting rules. |
| SHA256 | 4e3bed10a8eff3e9205c1f37f647512464271d5ac65df7ae4709735621a38320 | File indicator associated with the GitHub-hosted STOCKSTAY MSI samples. |
| SHA256 | 55249f296b63a8bcf911b8bc96de43c1ac2b4a56c150a19d33d892a47e57352c | ConverterDDSNet.exe STOCKSTAY artifact in the military-calculator operation. |
| SHA256 | 626330d22f77d9cbca9d40cc06568041703f194610c4c5a84bbb05a2e4ee7459 | styles.dat.exe STOCKSTAY.MARKETMAKER downloader executed by the HTA lure. |
| SHA256 | 6298f3150ad94a242e649886d47c59c634a4d04b9af5ee15e3bf335c40b5e58e | File indicator for GitHub-hosted DiplomacyEduAI.msi installers containing STOCKSTAY. |
| SHA256 | 667a8f568a611f2f3d84a366b7946b360e055bece9699c95aad619637ab72a38 | STOCKSTAY file indicator from the November 2025 WinRAR-exploitation phishing wave. |
| SHA256 | 6cee9e838792ac5e2098362d68ce93a9a2c095d476dc16b289fe8509c99b2b8b | Plaintext STOCKSTAY configuration artifact referenced in the supplied YARA rule. |
| SHA256 | 6da0b4c1a5d0d3fb6e6a2990a82ba51db1f68a3bba818baa46526a29731e2342 | calculator.rar archive containing the malicious military-calculator HTA lure and downloader. |
| SHA256 | 7615140f78d9a0ce31cc9fe8c54c60028a7439cb32526fd97b10afef7145dd78 | models.py database definitions supporting the STOCKSTAY C2 controller. |
| SHA256 | 77417df21b4b4e8d86b8bda4afeef93fd36f355362586b2d1f51121a82244167 | MSRender.lnk shortcut intended to execute STOCKSTAY.STOCKTRADER. |
| SHA256 | 80f6c010fd260d0bcf18a4b6a8d62505adbed50d2e615ed9522c4bfd61c00661 | ClientMNGR.exe STOCKSTAY artifact in the military-calculator operation. |
| SHA256 | 813c78b5b6ef28a9c0ed35f2c6cd88fc50880ab91f8777dfe7aaccb1c24b08d5 | MSDriver.lnk shortcut intended to execute STOCKSTAY.STOCKBROKER. |
| SHA256 | 81aabf646619ea5f4a72457cd3aa17c5988003d67e6454f45e7cb33613021bac | apps_libwallets_v1.3.rar archive containing STOCKSTAY components. |
| SHA256 | 82707cfdf24dcb762f4615f01e1ba4d3dfdec4abe9cd588558d2634d7e6a5eeb | STOCKSTAY artifact listed with Copia.msi and referenced by component-detection YARA rules. |
| SHA256 | 9164054d0bf0b7c8820da4f742860940998984555e65820e4fa8dd07b6bd67ec | STOCKSTAY.STOCKMARKET orchestrator in the December 2023 archive. |
| SHA256 | 98ce3c6e4dd05887ea619f2bbfeb2e2c2805ed07e85e119b79b828b7ef8be397 | GR3.exe STOCKSTAY.STOCKBROKER sample with junk code and K1MORPHER string obfuscation. |
| SHA256 | 9fe944147c15a87963b06baf6473288d64c23655a0ba9369c35566272d8efc73 | docs.zip archive containing STOCKSTAY components. |
| SHA256 | a40bf9c75d1bfa6d66f1179f2321de6589f80d3089d992797a9cb0e84f6196ce | STOCKSTAY file indicator from the November 2025 WinRAR-exploitation phishing wave. |
| SHA256 | b064a3efb04ed77e6c57955089ce639e193d166c8ea2216c98c3e9b701ea2cff | Copia.msi installer containing STOCKSTAY components. |
| SHA256 | b287347a5bff8af360ce0e6500c336b6fe6d97920abc26202c9d843ffebc5f89 | External STOCKSTAY module containing cryptographic and obfuscation routines. |
| SHA256 | b55f3b8a7334af049ba3f70a9ad3fe78574b1e180c68baf9a7110d104387a636 | wtools.py utility functions supporting the STOCKSTAY C2 controller. |
| SHA256 | b728eba4f0d6d16602fbad05a591f14391594262d3584b2e249e97f86e4dcc5a | STOCKSTAY file indicator listed for the February 2024 Italy-associated installer. |
| SHA256 | c905cb512018cc55512c6a22677c3d6f389c47afd54d7c85797868fc4fcb90e9 | STOCKSTAY file indicator from the November 2025 WinRAR-exploitation phishing wave. |
| SHA256 | d1e54270433a94aa3d45d888e4c62299bee3480eb2cb4a5489c7dda69d476c3e | Actor-compiled websocket-sharp.dll bundled with STOCKSTAY.STOCKBROKER and presented as a tracking artifact. |
| SHA256 | d3fd32f915c239872c9e7ed9408b1f36dfcef03aa68f9a396d05c437667cdb43 | ClientMNGR2.exe STOCKSTAY.STOCKBROKER sample listed in the May 2025 file indicators. |
| SHA256 | d8fe8f3fe838d5b1a1043096f6f6bb6f524f5f1b0c9f83a081078a824daa0cf3 | File indicator associated with the GitHub-hosted STOCKSTAY MSI samples. |
| SHA256 | da8a96bc74e265f945f1cc6992c6dc0f9ea36ed1991f7b8d312db79d9bf78c40 | MicrosoftUpdateOneDrive.exe STOCKSTAY.MARKETMAKER downloader used in the March–April 2025 Ukrainian operation. |
| SHA256 | dfd5cb91d06b9649d4cab500343af80ad1144a9e46641cc406f43dd169003c22 | SMNet.exe STOCKSTAY.STOCKBROKER artifact from the March–April 2025 Ukrainian operation. |
| SHA256 | e1d16fb635060d23e889b0617d77f0cf06d00cc19b43a2c8b5ac53ac027ac722 | SMEditor.exe STOCKSTAY artifact from the March–April 2025 Ukrainian operation. |
| SHA256 | e2a0f4440f67998a0215d49be31746ea192bfcb4dc4ee532a218f8cf13605714 | External STOCKSTAY module containing IPC logic. |
| SHA256 | e316b1e13154dc6115e1e0c023f6fe3d17861cae839d4a4a81779b6aad9a24f8 | STOCKSTAY file indicator from the November 2025 WinRAR-exploitation phishing wave. |
| SHA256 | e3364ee21cae6725451e8bc9ab9933df0000fd19814170bd132da68d1906d5ff | STOCKSTAY file indicator listed for the military-calculator operation. |
| SHA256 | e6d8192960a89d5480868b94088cccdaa1560f9c8a0b0282ced2b7c1f72341b6 | DriversPrinterGraphic.rar archive containing an early STOCKSTAY sample. |
| SHA256 | e83f274bf9914c6cfc0c6b3cdadf089565f49dace4aca93287c22aba9641c8f3 | File indicator from the November 2025 STOCKSTAY phishing wave. |
| SHA256 | f04f43b6f7c2d86109c495179b497f7fb45fd95816623de1b77900f71b4f99ed | server.py Python implementation of the STOCKSTAY C2 controller. |
| SHA256 | f964353b9ae4bedbe62de6c0d7eafa9fb8b87897bbaea483aedaa8ae191834da | File indicator from the November 2025 STOCKSTAY phishing wave. |
| URL | hxxps[:]//basecon[.]com[.]ua/calculator[.]rar | Malicious HTA and STOCKSTAY.MARKETMAKER archive hosted on compromised Ukrainian IT-company infrastructure. |
| URL | hxxps[:]//circoloesteri[.]elezioni[.]idnet[.]it/admin-election/riepilogo[.]php | Specific Italian-language voting lure URL opened by the malicious Copia.msi installer. |
| URL | hxxps[:]//online[.]zp[.]ua/wp-content/uploads/Tools/EditorToolsPdf[.]zip | Specific STOCKSTAY payload archive on compromised WordPress infrastructure. |
| URL | hxxps[:]//www[.]drs[.]gov[.]ua/wp-content/themes/twentytwentyfive/docs[.]zip | Specific payload archive URL on compromised State Regulatory Service of Ukraine infrastructure. |
MITRE ATT&CK
T1005 · Data from Local SystemSTOCKTRADER's Get command collected specified local files or files matching selected extensions.T1012 · Query RegistrySTOCKTRADER's RegRead command read a specified registry value.T1027 · Obfuscated Files or InformationSTOCKSTAY used encrypted configurations, junk code, and K1MORPHER string obfuscation.T1036.005 · Match Legitimate Resource Name or LocationSTOCKSTAY impersonated stock-market utilities, PDF viewers, calculators, and Windows libraries; MARKETMAKER used the name MicrosoftUpdateOneDrive.T1041 · Exfiltration Over C2 ChannelCollected files, screen captures, and command results were returned through STOCKSTAY's C2 channel.T1057 · Process DiscoveryThe Sysinfo command collected the names of running processes.T1059.007 · JavaScriptHTA-embedded JScript renamed styles.dat to styles.dat.exe and launched it through WScript.Shell.T1071.001 · Web ProtocolsSTOCKSTAY exchanged C2 messages over secure WebSocket connections.T1082 · System Information DiscoveryThe Sysinfo command queried WMI for operating-system and hardware information.T1083 · File and Directory DiscoverySTOCKTRADER's Dir command enumerated files and subdirectories, optionally recursively.T1105 · Ingress Tool TransferMARKETMAKER downloaded additional STOCKSTAY payload archives; STOCKTRADER's Put command wrote supplied file content onto infected devices.T1112 · Modify RegistrySTOCKTRADER supported setting and deleting registry values through RegWrite and RegDelete.T1113 · Screen CaptureSTOCKTRADER's Image command captured the victim's screen and encoded the image for transmission.T1140 · Deobfuscate/Decode Files or InformationSTOCKMARKET decrypted configuration data embedded in decoy fields, and K1MORPHER deobfuscated strings and other datatypes at runtime.T1203 · Exploitation for Client ExecutionMalicious RAR archives exploited WinRAR CVE-2025-8088 to install STOCKSTAY components.T1204.002 · Malicious FileVictims were lured into opening malicious RDP files and executing a military-calculator HTA.T1218.005 · MshtaA malicious HTA military-calculator lure executed the bundled STOCKSTAY.MARKETMAKER downloader.T1480.001 · Environmental KeyingLater-stage STOCKSTAY deployments required particular host, user, or domain attributes to decrypt configuration data.T1484.001 · Group Policy ModificationTurla deployed malware through malicious GPO installation from a compromised Ukrainian domain controller.T1547.001 · Registry Run Keys / Startup FolderSTOCKSTAY installers created registry Run entries, and November archives attempted to place LNK shortcuts in the startup programs directory.T1560.001 · Archive via UtilityCollected files were placed in an in-memory ZIP archive before transmission.T1566.001 · Spearphishing AttachmentPhishing emails carried malicious RDP attachments that connected victims to actor-controlled infrastructure.T1566.002 · Spearphishing LinkNovember phishing emails contained file-sharing links leading to malicious RAR archives.T1573.002 · Asymmetric CryptographySTOCKMARKET generated a unique 4096-bit RSA key pair for encrypting outbound data and supplied its public key to the server.
CVE
People
Threat Actors
Secret BlizzardAlias of Turla, the actor linked to STOCKSTAY deployment and development.SUMMITAlias of Turla, the actor linked to STOCKSTAY deployment and development.TurlaRussia-linked actor attributed by GTIG with high confidence to STOCKSTAY-related activity; the article identifies SUMMIT, Secret Blizzard, VENOMOUS BEAR, and UAC-0194 as aliases.UAC-0194Alias of Turla, the actor linked to STOCKSTAY deployment and development.VENOMOUS BEARAlias of Turla, the actor linked to STOCKSTAY deployment and development.
Malware
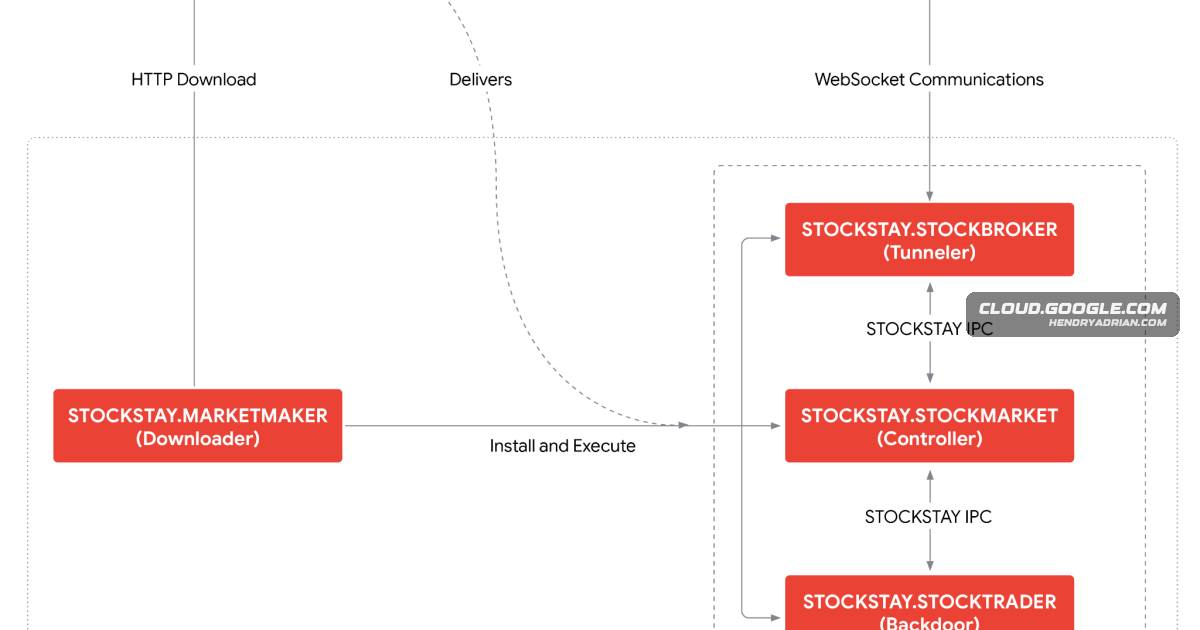
DIAMONDBACKDIAMONDBACK, a dropper often deployed prior to KAZUAR in the execution chain, has made use of a hash of the target’s hostname in decrypting its payload, to prevent divulgence of its intentions outside of the targetKazuarUsed for ongoing cyber espionage, this backdoor shares significant code and functional overlaps with KAZUAR, a successful toolkit previously attributed to Turla.SnakeTurla, and specifically their longstanding Snake implant, has been publicly attributed by the United States Cybersecurity and Infrastructure Security Agency (CISA) to Center 16 of Russia’s Federal Security Service (FSB).STOCKSTAYThreat Intelligence Group (GTIG) has conducted an in-depth analysis of a .NET backdoor, tracked as STOCKSTAY, that has been continually developed and deployed by the Russia-linked threat actor Turla (aka SUMMIT,STOCKSTAY.MARKETMAKERSTOCKSTAY.MARKETMAKERSTOCKSTAY.STOCKBROKERSTOCKSTAY.STOCKBROKERSTOCKSTAY.STOCKMARKETto a specified remote server, after which it acts as a relay between the server and the STOCKSTAY.STOCKMARKET orchestrator.STOCKSTAY.STOCKTRADERSTOCKSTAY.STOCKMARKET also communicates with the STOCKSTAY.STOCKTRADER component in order to issue commands to be executed on the infected host.WILDDAYin which we observed Turla deploying a wide range of tools into the victim’s network, including WILDDAY, DIAMONDBACK and KAZUAR, via malicious GPO installation from a compromised domain controller.
Vendors
GitHubGTIG identified a publicly accessible GitHub repository containing a Python implementation of the victim-facing STOCKSTAY WebSocket server controller.GoogleGoogle Threat Intelligence Group (GTIG) has conducted an in-depth analysis of a .NET backdoor, tracked as STOCKSTAY, that has been continually developed and deployed by the Russia-linked threat actor Turla (aka SUMMIT,Renderserver component appears to supplement the threat actor’s usage of third-party hosting platforms such as Render platform which provides a platform for hosting web services, including WebSockets.
Products
GitHubGTIG identified a publicly accessible GitHub repository containing a Python implementation of the victim-facing STOCKSTAY WebSocket server controller.Google Security OperationsGoogle Security Operations (SecOps)Renderserver component appears to supplement the threat actor’s usage of third-party hosting platforms such as Render platform which provides a platform for hosting web services, including WebSockets.Signal Messengeras demonstrated by its deployment of specialized scripts to intercept secure communications from Signal Messenger users, its hijacking of legacy criminal botnets to target Ukrainian organizations, and its recentWinRAREach link led to a malicious RAR archive which exploits a path traversal vulnerability in WinRAR (CVE-2025-8088) to install the core STOCKSTAY components.WordPressBoth ecosystems rely heavily on .NET development, and have been observed using compromised WordPress sites during various stages of their operations.
Tools
Countries
ItalyEarly development samples of STOCKSTAY were identified in various European nations, including Italy, the Netherlands, Poland, and Germany; however, we have been largely unable to confirm the intended victims for theRussiaof a .NET backdoor, tracked as STOCKSTAY, that has been continually developed and deployed by the Russia-linked threat actor Turla (aka SUMMIT, Secret Blizzard, VENOMOUS BEAR, UAC-0194) since at least DecemberUkraineTurla has deployed STOCKSTAY against government and military organizations in Ukraine, as well as entities with an interest in Italian foreign policy.
Industries
DefenseThe group has a long history of targeting a wide range of industries, with a particular focus on western Ministries of Foreign Affairs, and defense organizations within the context of heightened political tensions.Educationcompromising a diplomatic education platform for phishing and distribution of malicious RDP files;GovernmentTurla has deployed STOCKSTAY against government and military organizations in Ukraine, as well as entities with an interest in Italian foreign policy.ITcan be instructed to establish a secure WebSocket connection to a specified remote server, after which it acts as a relay between the server and the STOCKSTAY.STOCKMARKET orchestrator.MilitaryTurla has deployed STOCKSTAY against government and military organizations in Ukraine, as well as entities with an interest in Italian foreign policy.