
41 Fake Download Sites Redirect Users to Download Studio
Summary
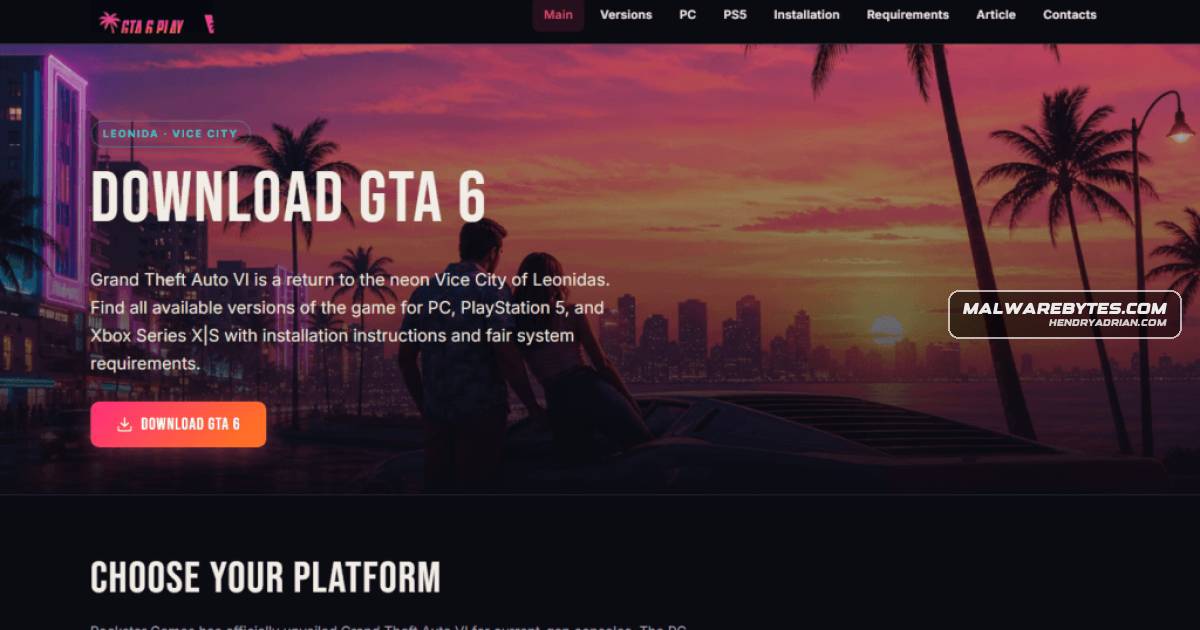
Malwarebytes found 41 fake game and software download sites using JavaScript click handlers and affiliate redirects to deliver a signed Download Studio installer. The installer was not shown to be malware, but its updater was abused in 2020.
Key points
- The 41 sites impersonated games and Windows applications, using accurate product information and genuine-looking links to appear legitimate.
- JavaScript made a download button display a genuine destination on hover, then redirected visitors elsewhere through affiliate tracking when clicked.
- The campaign delivered a roughly 73 MB Windows installer for Download Studio, signed by Grand Media, TOV; analysis found torrent components and an automatic updater.
- The valid signature did not mean users had downloaded the software they intended. The article says its analysis did not establish that the current installer was malware.
- Avast researchers reported that Download Studio's updater was used in 2020 to distribute FakeMBAM, a backdoor disguised as a Malwarebytes installer. The article found no evidence that the same activity is happening again.
- The article recommends downloading from developers or trusted stores, checking that the file identifies itself as the intended program, and removing Download Studio if it was installed unintentionally.
Article Details
- Attack Vectors
- Fake download pages impersonate games and Windows software, then use JavaScript click handlers to override the displayed legitimate destination and send visitors through affiliate redirects.
- The redirect funnel instructs visitors to install a roughly 73 MB Download Studio Windows installer instead of the advertised software.
- Historically, Avast observed Download Studio's automatic updater silently delivering FakeMBAM; the article says there is no evidence the current installer is malicious or that the earlier attack is recurring.
- Defensive Notes
- Download software directly from the developer or a trusted app store; do not rely on link hover previews because click handling can send visitors elsewhere.
- Check that the downloaded file's product name matches the intended software. A valid digital signature does not establish that the file is the program the user wanted.
- Close pages that require installing a separate download manager before providing the advertised software.
- If Download Studio is installed without the user's choice, remove it through Settings > Apps and run a full virus scan.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | acronisportal[.]ru | Fake Acronis download site listed among the campaign's lure sites. |
| DOMAIN | apis[.]downloadstud[.]io | Listed as Download Studio infrastructure or a redirect endpoint used in the campaign. |
| DOMAIN | crystaldisk24[.]ru | Fake CrystalDisk download site listed among the campaign's lure sites. |
| DOMAIN | csgodownload[.]ru | Fake Counter-Strike download site used to funnel visitors toward Download Studio. |
| DOMAIN | downloadstudio[.]net | Listed as Download Studio infrastructure or a redirect endpoint used in the campaign. |
| DOMAIN | dstudio[.]app | Listed as Download Studio infrastructure or a redirect endpoint used in the campaign. |
| DOMAIN | fallout24[.]ru | Fake Fallout download site listed among the campaign's lure sites. |
| DOMAIN | foxitpdf[.]ru | Fake Foxit PDF download site listed among the campaign's lure sites. |
| DOMAIN | get7zip[.]ru | Fake 7-Zip download site listed among the campaign's lure sites. |
| DOMAIN | getaimp[.]ru | Fake AIMP download site listed among the campaign's lure sites. |
| DOMAIN | getavast[.]ru | Fake Avast download site listed among the campaign's lure sites. |
| DOMAIN | getbandicam[.]ru | Fake Bandicam download site listed among the campaign's lure sites. |
| DOMAIN | getbluestacks[.]ru | Fake BlueStacks download site listed among the campaign's lure sites. |
| DOMAIN | getdownloadstudio[.]net | Listed as Download Studio infrastructure or a redirect endpoint used in the campaign. |
| DOMAIN | getmovavi[.]ru | Fake Movavi download site listed among the campaign's lure sites. |
| DOMAIN | getrecuva[.]ru | Fake Recuva download site listed among the campaign's lure sites. |
| DOMAIN | getultraiso[.]ru | Fake UltraISO download site listed among the campaign's lure sites. |
| DOMAIN | getvmware[.]ru | Fake VMware download site listed among the campaign's lure sites. |
| DOMAIN | getvuescan[.]ru | Fake VueScan download site listed among the campaign's lure sites. |
| DOMAIN | gta6-play[.]ru | Fake Grand Theft Auto VI download site used as a lure in the campaign. |
| DOMAIN | halflife-play[.]ru | Fake Half-Life download site listed among the campaign's lure sites. |
| DOMAIN | paintdotnet[.]ru | Fake Paint.NET download site listed among the campaign's lure sites. |
| DOMAIN | pubgplay[.]ru | Fake PUBG download site listed among the campaign's lure sites. |
| DOMAIN | r[.]byteengineering[.]net | Listed as Download Studio infrastructure or a redirect endpoint used in the campaign. |
| DOMAIN | roblox-play[.]ru | Fake Roblox download site listed among the campaign's lure sites. |
| DOMAIN | rust-play[.]ru | Fake Rust download site listed among the campaign's lure sites. |
| DOMAIN | tcommander[.]ru | Fake Total Commander download site listed among the campaign's lure sites. |
| DOMAIN | thewitcherplay[.]ru | Fake The Witcher download site listed among the campaign's lure sites. |
| DOMAIN | vlcmp[.]ru | Fake VLC download site used to direct visitors away from the genuine VideoLAN download. |
| SHA256 | 9a3f6e69c12cb814c45862219ecb17e9ab7744877c9da1c49f3ea046437f8fca | SHA-256 hash of the Download Studio installer sample examined in the article. |
MITRE ATT&CK
T1036 · MasqueradingThe campaign's websites impersonate popular games and Windows software to make fake download pages appear authentic.T1105 · Ingress Tool TransferThe deceptive download process delivers a Windows installer for Download Studio to visitors.T1204.001 · Malicious LinkVisitors are induced to click deceptive download buttons that appear to point to legitimate software or game destinations but redirect to Download Studio.
Malware
Vendors
AvastThe campaign included genuine-looking links, valid signatures, and prior abuse history tied to Download Studio’s updater, including FakeMBAM distribution by Avast-reported attackers.Grand Media, TOVThe delivered installer was a roughly 73 MB Windows package for Download Studio, signed by Grand Media, TOV, and it validated successfully.
Products
7-ZipTargets included Counter-Strike, Half-Life, Fallout, Roblox, PUBG, The Witcher, VLC, 7-Zip, Paint.NET, VMware, Total Commander, Foxit PDF, and others.AcronisOther lures target security, backup, and recovery products, including Avast, Acronis, and Recuva.AIMPVLC, 7-Zip, Paint.NET, and AIMP are legitimate applications people routinely download.Download StudioA network of 41 websites impersonated popular games and Windows software to funnel visitors toward installing Download Studio, using deceptive click handling, affiliate redirects, and convincing fake download pages.Grand Theft Auto VIOne site, GTA 6 PLAY, claims to offer a PC download of Grand Theft Auto VI.Malwarebytes Browser GuardMalwarebytes Browser Guard blocks pages like these before they load, which stops the problem before you’ve downloaded anything.Paint.NETTargets included Counter-Strike, Half-Life, Fallout, Roblox, PUBG, The Witcher, VLC, 7-Zip, Paint.NET, VMware, Total Commander, Foxit PDF, and others.RecuvaOther lures target security, backup, and recovery products, including Avast, Acronis, and Recuva.Steam#DownloadStudioVLCTargets included Counter-Strike, Half-Life, Fallout, Roblox, PUBG, The Witcher, VLC, 7-Zip, Paint.NET, VMware, Total Commander, Foxit PDF, and others.