Google Details Russian Espionage Clusters Abusing Authentication Flows to Target Individuals
Summary
Google tracks three suspected Russian espionage clusters targeting academics, diplomats, and defense-related individuals through app-password and OAuth phishing, device linking, and infostealer malware. It reports disrupting infrastructure and offers mitigation guidance
Key points
- GTIG assesses with high confidence that UNC6293, UNC7005, and UNC5976 have a Russian nexus; it links UNC6293 and UNC7005 to an ICE RELIC subcluster with moderate confidence.
- The clusters target individuals in academia, diplomacy, government, think tanks, aerospace, and defense, often using invitations and impersonation to build trust.
- Attackers abuse app passwords, OAuth authorization, and Microsoft or WhatsApp device linking to gain account access.
- UNC7005's WhatsApp pages can prompt victims to link an attacker-controlled device and, during a fake call, record audio and video for upload to attacker infrastructure.
- A UNC7005 phishing wave delivered VIDAR to Windows systems and ATOMIC infostealer to macOS systems; another operation distributed ENGINELIGHT malware.
- UNC5976 used fake file-sharing pages and cloud projects to collect authentication tokens, and also distributed the HEADRUSH Excel plugin that led to an HTA downloader.
- GTIG says it disabled known infrastructure and disrupted UNC5976 cloud projects. It advises verifying invitations, avoiding app-password sharing, and auditing linked messaging devices.
Article Details
- Attack Vectors
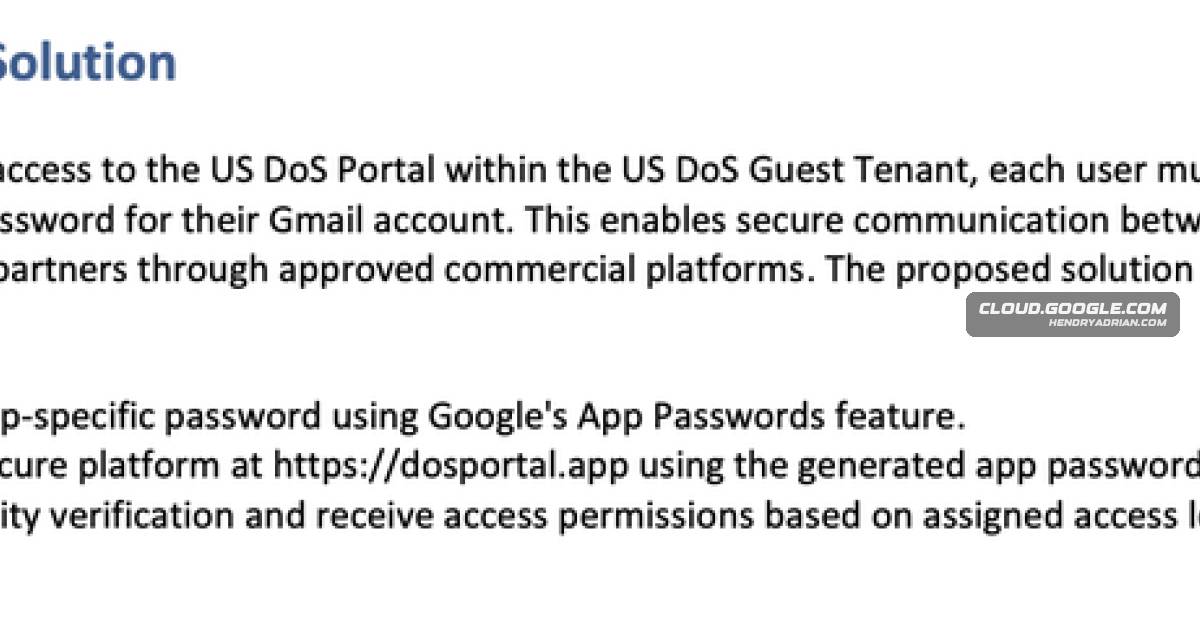
- UNC6293 used app-password phishing, impersonating U.S. State Department officials and asking targets to create and submit app passwords.
- UNC6293 used OAuth phishing that asked targets to provide a verification code or full URL after legitimate authentication.
- UNC7005 used email links to spoofed event and organization websites for Microsoft device-code phishing and other credential or account-compromise operations.
- UNC7005 tricked targets into linking WhatsApp accounts to an attacker-controlled device, then presented fake calls, chats, or file-transfer lures.
- UNC7005 distributed VIDAR and ATOMIC through a spoofed summit website, selecting the malware based on the target's operating system.
- UNC7005 used Google OAuth phishing and an attacker-controlled cloud project to obtain authentication tokens.
- UNC5976 used fake file-sharing pages and Google OAuth redirects to capture authentication tokens through cloud infrastructure.
- UNC5976 distributed the HEADRUSH Excel plugin, which led to an HTA downloader.
- UNC7005's WhatsApp lure could record target audio and video and upload the recordings to its C2 endpoint.
- UNC7005 used browser and system checks on phishing pages to detect or evade automated analysis.
- Defensive Notes
- Do not proceed past warnings for suspicious websites; check the browser URL before entering credentials or authenticating.
- Confirm invitations directly with official organizers using contact details obtained independently of the invitation.
- Do not share app passwords; revoke legacy or potentially compromised app passwords.
- Consider the Advanced Protection Program; Google Cloud enterprise customers can disable app-specific passwords by restricting 2-Step Verification to security keys or enrolling users in the program.
- For messaging applications, enforce registration locks and two-factor authentication where possible, regularly audit linked devices, and verify safety numbers or codes through an independent channel.
Indicators of compromise
| Type | Indicator | Context |
|---|---|---|
| DOMAIN | chamber-ua[.]org | Phishing domain and attacker account email domain associated with UNC7005. |
| DOMAIN | dosportal[.]app | Phishing domain listed as an indicator for the reported operations. |
| DOMAIN | fewfwfwfwfwf[.]info | C2 for the first ATOMIC/AtomicStealer payload. |
| DOMAIN | finishoperations[.]com | Attacker-controlled domain spoofing the Finnish Operations Center in OAuth phishing. |
| DOMAIN | finishoperations[.]org | Attacker-controlled domain spoofing the Finnish Operations Center in OAuth phishing. |
| DOMAIN | foc-share[.]com | Attacker-controlled domain associated with UNC7005's OAuth phishing infrastructure. |
| DOMAIN | foc-share[.]org | Attacker-controlled domain associated with UNC7005's OAuth phishing infrastructure. |
| DOMAIN | foreignrelations[.]us | Phishing site used by UNC6293 to request an OAuth verification code. |
| DOMAIN | globsec[.]net | Listed as an indicator associated with UNC7005's GLOBSEC-themed phishing operation. |
| DOMAIN | internal-share[.]com | Attacker-controlled domain associated with the reported OAuth phishing infrastructure. |
| DOMAIN | m365-owa[.]com | Attacker-registered Outlook Web Access-themed domain linked to the hospitality captive-portal campaign. |
| DOMAIN | mail[.]kiis[.]co[.]uk | Malware distribution domain. |
| DOMAIN | mioisiskwowiwjowuwjwolab[.]club | Listed as an indicator in the ATOMIC/AtomicStealer infrastructure set. |
| DOMAIN | miov2iaiaoubqosiqoiajwowiwjso[.]online | C2 for the second stage of ATOMIC/AtomicStealer. |
| DOMAIN | ms365-device[.]com | Attacker-registered Outlook Web Access-themed domain linked to the hospitality captive-portal campaign. |
| DOMAIN | ms365-live[.]com | Attacker-controlled domain masquerading as Microsoft and resolving to an IP associated with UNC7005 infrastructure. |
| DOMAIN | my-invite[.]org | Domain used in UNC7005's Microsoft device-code phishing operation. |
| DOMAIN | owa-ms365[.]com | Attacker-registered Outlook Web Access-themed domain linked to the hospitality captive-portal campaign. |
| DOMAIN | shopinvite[.]org | Listed as an indicator associated with the reported phishing operations. |
| DOMAIN | statistic-ms[.]live | Attacker-controlled domain spoofing Microsoft and used as C2 for ENGINELIGHT. |
| DOMAIN | wa-connect[.]eu | Attacker-controlled domain spoofing WhatsApp in a phishing operation. |
| DOMAIN | wa-connect[.]net | Listed as an indicator associated with UNC7005's WhatsApp-themed operations. |
| DOMAIN | wa-device[.]com | Listed as an indicator associated with UNC7005's WhatsApp-themed operations. |
| DOMAIN | wa-invite[.]com | Listed as an indicator associated with UNC7005's WhatsApp-themed operations. |
| DOMAIN | wa-meeting[.]com | Listed as an indicator associated with UNC7005's WhatsApp-themed operations. |
bounce@chamber-ua[.]org | Attacker-controlled account used to send an ENGINELIGHT phishing operation. | |
chikolimdrid@gmail[.]com | Attacker email used to register domains linked to UNC7005 operations. | |
keyereaonkendrick4@gmail[.]com | Attacker email used to register statistic-ms.live and associated with a later malware operation. | |
| HOSTNAME | drive[.]google[.]verify-drive[.]com | Attacker-controlled hostname hosting a fake file-sharing page used in UNC5976 OAuth phishing. |
| IPV4 | 104[.]194[.]159[.]150 | IP resolution shared by attacker-controlled domains used in UNC7005 operations. |
| IPV4 | 107[.]189[.]18[.]7 | VIDAR command-and-control address. |
| IPV4 | 196[.]251[.]107[.]171 | C2 for the second ATOMIC/AtomicStealer payload. |
| IPV4 | 31[.]57[.]243[.]154 | Related IP listed among the campaign's network indicators. |
| IPV4 | 38[.]146[.]28[.]75 | Related IP listed among the campaign's network indicators. |
| SHA256 | 125752ad7c20d715920a3b2fb0fdde660f07b3f2b053665cf38c2d6d9de86e1e | Hash listed for ENGINELIGHT in the campaign's file indicators. |
| SHA256 | 1d9299799a7b8da67c44ebec064d64542c27645f8e84de4a22ca3f6cbc843e3c | Hash of a VIDAR sample distributed by UNC7005. |
| SHA256 | 1e3ee845fde739fcd3ca9ce62c7f142a7c501d11db4c4fb294d4939f12d0f916 | File hash listed as an indicator for the reported operations; specific artifact not identified. |
| SHA256 | 20e20b074967ed6f6e04d609ccec5ff7492665ef25f894c90c2ddc92fa47ac38 | File hash listed as an indicator for the reported operations; specific artifact not identified. |
| SHA256 | 28f622028e690c943f7fa9aca426c07cab52b5aaba757ef8a3328609c0b3bec3 | File hash listed as an indicator for the reported operations; specific artifact not identified. |
| SHA256 | 2c7f4165967d6f7737b3fef87959846920b57a5368b531ad1427c7214d4c41a2 | Hash of a HEADRUSH sample observed in UNC5976 activity. |
| SHA256 | 403b624e35777cbc07dbe66398b21bba70396a20b859c880732338ce1dd1f41f | Hash listed for CHERRYPIE in the campaign's file indicators. |
| SHA256 | 5b8d50c2e8cc3038b7c6e6dbf1219f6e814930a1e3c0053143a1191ae67f8ffc | Hash of the GLOBSEC phishing page. |
| SHA256 | 6f7090895c1c3dee30de6b3f098ca3a788dc198646e5293a8b1210430b0add97 | File hash listed as an indicator for the reported operations; specific artifact not identified. |
| SHA256 | a06a8fd1b6fa1924199a4540cf16d089217ce8f78c617739946f145fd1fc88c1 | Hash of the Finnish Operations Center OAuth phishing landing page. |
| SHA256 | be99857449d2856dd5a84e21c8a3d5e0e01456adb44062ddec5a6b4970d8d42c | File hash listed as an indicator for the reported operations; specific artifact not identified. |
| SHA256 | c5826032207d623a7f6caec8465af7364eccc355f9a48897da2a54f3e4420265 | Hash of an ATOMIC sample distributed by UNC7005. |
| SHA256 | ca3be5885afb3eb3bb19341e2653212200c568f3f900e0b2f04de9ba209aed25 | File hash listed as an indicator for the reported operations; specific artifact not identified. |
MITRE ATT&CK
T1041 · Exfiltration Over C2 ChannelVIDAR sent collected browser information to its C2, and UNC7005's page uploaded recordings to a C2 endpoint.T1056.003 · Web Portal CapturePhishing pages prompted targets to enter app passwords, credentials, or other authentication information.T1082 · System Information DiscoveryUNC7005's page collected system and browser attributes including platform, screen dimensions, time zone, language, processor count, and memory.T1105 · Ingress Tool TransferUNC7005's spoofed summit page served infostealer malware, and UNC5976 distributed an Excel plugin leading to an HTA downloader.T1123 · Audio CaptureUNC7005's WhatsApp-themed page used browser media access to record target audio.T1125 · Video CaptureUNC7005's WhatsApp-themed page used browser media access to record target video.T1497.001 · System ChecksUNC7005's phishing page checked browser automation and headless-browser indicators to evade automated analysis.T1528 · Steal Application Access TokenUNC7005 and UNC5976 used OAuth flows and cloud-project scripts to obtain or capture authentication tokens.T1555.003 · Credentials from Web BrowsersVIDAR targeted credentials, cookies, payment information, and other data stored in browsers.T1566.002 · Spearphishing LinkThe clusters sent phishing emails containing links to attacker-controlled sites and lures.
People
Threat Actors
APT29Name given as the former name of ICE RELIC.ICE RELICCluster assessed with moderate confidence to be related to UNC6293 and UNC7005; the article says ICE RELIC was formerly APT29.Storm-2945Alternate name explicitly given for UNC7005.UNC5976Suspected Russian cyber espionage cluster focused on OAuth phishing and malware operations.UNC6293Suspected Russian cyber espionage cluster assessed with moderate confidence to be a subcluster of ICE RELIC and involved in initial-access phishing operations.UNC7005Suspected Russian cyber espionage cluster; the article identifies STORM-2945 as an alternate name for this cluster.
Malware
ATOMICIf the User Agent indicates that the target is browsing from a machine running macOS, the malicious webpage served a sample of ATOMIC to the target (c5826032207d623a7f6caec8465af7364eccc355f9a48897da2a54f3e4420265).AtomicStealerATOMIC (aka AtomicStealer) is a macOS infostealer operated as a MaaS and also targets sensitive browser information.CHERRYPIESamples of the CHERRYPIE PowerShell infostealer (also known as ChocoShell) contain numerous artifacts suggesting the malware is generated by a large language model (LLM).ChocoShellSamples of the CHERRYPIE PowerShell infostealer (also known as ChocoShell) contain numerous artifacts suggesting the malware is generated by a large language model (LLM).ENGINELIGHTAn earlier attacker-controlled domain spoofing Microsoft in late April 2026 (statistic-ms[.]live) was used by UNC7005 as C2 for Go malware we call ENGINELIGHT.HEADRUSHIn addition to these phishing pages, we have also observed UNC5976 leverage a malicious Excel plugin, which we named HEADRUSH.VidarIf the User Agent indicates that the target is browsing from a machine running Windows, the malicious webpage serves a sample of VIDAR to the target (1d9299799a7b8da67c44ebec064d64542c27645f8e84de4a22ca3f6cbc843e3c).
Vendors
GoogleGoogle Threat Intelligence Group (GTIG) is tracking three distinct suspected Russian cyber espionage threat clusters abusing legitimate authentication flows to target individuals working in academia, aerospace andMicrosoftUNC7005 in particular is tied to the hospitality captive portal redirects reported on by Reliaquest and Microsoft.
Products
Advanced Protection Program (APP)High-risk users should consider Google’s enhanced security resources such as the Advanced Protection Program (APP).Google CloudAfter authenticating, the target was redirected to a Google Cloud project URL.Google Security Operations (SecOps)Google Security Operations (SecOps)Microsoft Outlook Web Access (OWA)Between July 16 and July 23, 2026, UNC7005 registered three Microsoft Outlook Web Access (OWA) themed domains (owa-ms365[.]com, m365-owa[.]com, and ms365-device[.]com), which were later linked to the hospitality captiveWhatsAppUNC7005 also conducts device code phishing operations for both Microsoft and WhatsApp accounts.
Countries
ArmeniaMuch of the group’s geographic targeting has centered on Ukraine and Armenia.RussiaUNC6293 operations were initially reported in June 2025 (also by Citizen Lab) as an aggressive app password phishing campaign against prominent individuals that are critical of Russia.Ukraineidentified in February 2026 that primarily targets academia, diplomatic, and nonprofit personnel across Ukraine, Western Europe, and the US Although this group shares many high-level similarities with UNC6293,United Statesdefense, governments and think tanks across Europe, as well as academia and think tanks within the United States.
Industries
Academiacyber espionage threat clusters abusing legitimate authentication flows to target individuals working in academia, aerospace and defense, governments and think tanks across Europe, as well as academia and think tanksAerospacethreat clusters abusing legitimate authentication flows to target individuals working in academia, aerospace and defense, governments and think tanks across Europe, as well as academia and think tanks within theDefenseabusing legitimate authentication flows to target individuals working in academia, aerospace and defense, governments and think tanks across Europe, as well as academia and think tanks within the United States.Defense industrial baseIts operational focus is primarily centered on the military, aerospace, defense industrial base, and NGOs/think tanks.DiplomacyThere is significant overlap in target industries (academia, NGOs, diplomacy, and defense) and geographic regions between historical ICE RELIC phishing operations and current UNC6293 and UNC7005 campaigns.GovernmentMilitaryIts operational focus is primarily centered on the military, aerospace, defense industrial base, and NGOs/think tanks.Nonprofit organizationsThink tanksauthentication flows to target individuals working in academia, aerospace and defense, governments and think tanks across Europe, as well as academia and think tanks within the United States.